September 2026 On Tap: Cloud Bucket Redirection Surge & Regional DGA Subdomain Telemetry

September 2026 Threat Landscape Abstract
In September 2026, across 148 verified malicious messages, threat actors demonstrated a sharp escalation in public cloud bucket redirection—with Google Cloud Storage (storage.googleapis.com) links jumping to 901 instances-while distributing payloads through high-entropy regional subdomains (.web.id, .my.id, .biz.id, .com.de) and DGA .us domains.
MITRE ATT&CK Techniques Observed This Month
Top Risks & Findings This Month
Google Cloud Storage Link Surge (storage.googleapis.com)
Our link extraction identified 901 total hyperlink references pointing to storage.googleapis.com across 148 messages (averaging ~6 redirector links per email across buttons, images, and footer anchors).
Health & Medical Supplement Spam Dominance (43.2%)
Over 43% of September spam payloads promoted erectile dysfunction remedies, weight loss hacks, and cognitive supplement claims.
Focus: content filtering, domain reputation reputation rulesRegional Subdomain & DGA Infrastructure Exploitation
Heavy reliance on free or low-cost regional subdomains (.web.id, .my.id, .biz.id, .com.de) combined with random string .us domains.
Cloud Storage Account Deletion Threat Influx (32.4%)
High volume of alerts alleging imminent cloud storage capacity limits or photo/video deletion unless billing details are updated.
Focus: security awareness training, external sender bannersInfrastructure & Malicious Link Analysis
The September dataset demonstrated a dramatic surge in links pointing to static Google Cloud Storage buckets (storage.googleapis.com), which threat actors use to host intermediate static HTML redirectors. Additionally, attackers routinely hotlink remote images from legitimate public hosts like Imgur (i.imgur.com) to bypass inline attachment filters:
Observed In-Message Link Infrastructure (September 2026)
| Hostname / Service | Extracted Links | Role in Telemetry | Infrastructure Type |
|---|---|---|---|
storage.googleapis.com | 901 | Static HTML bucket redirectors | Threat-Controlled Staging |
i.imgur.com | 109 | Remote logo & banner image hotlinking | Abused Legitimate Service |
d3k81ch9hvuctc.cloudfront.net | 10 | Content Delivery Network (CDN) assets | Abused Legitimate Service |
Primary Sender Registrar TLDs & Full URL Structure
Threat actors heavily utilized dynamic subdomains and hash-appended bucket URLs to deliver payloads:
- Indonesian & Regional Subdomains (
.web.id,.my.id,.biz.id):xhtwlhmd.markif.lightworksa.web.idxpysjlaa.teleso.barviko.my.idpfgvdpzh.soibm.pravento.biz.idvwwdtqtw.allied.metanova.biz.idolyamzcr.samsung.kalqima.my.id
- Random String DGA
.usDomains:aax.lbxrvtstbtbdw.ussaq.hcdwqozyylqgc.usmhz.kmvhompywgibm.us628mqiak.us
Unique Google Cloud Storage Bucket Paths (8 Paths / 901 Links)
Every extracted storage.googleapis.com URL in the September telemetry mapped to one of eight distinct bucket/object paths:
| Bucket & Object Path | Link Count | Target Redirector Role |
|---|---|---|
worklinks/evrtinggood.html | 500 | Primary intermediate static HTML redirector |
smalbus/salaminka.html | 383 | Secondary intermediate static HTML redirector |
hmdbox/hmd-v1-cl3.html | 9 | Campaign variant redirector |
yassales/hreflyass.html | 2 | Campaign variant redirector |
strow/strw_v3.html | 2 | Staging variant redirector |
strow/strw-v1-cl2.html | 2 | Staging variant redirector |
bowly/bowly.html | 2 | Campaign variant redirector |
sndrr/nobotgogomailbali_v2.html | 1 | Anti-bot detection staging script |
Intercepted Phishing Case Studies & Evidence
Below are key case studies highlighting major true phishing campaigns observed during the September collection window. Use the provided Gmail search terms to locate these exact lures in your spam folder.
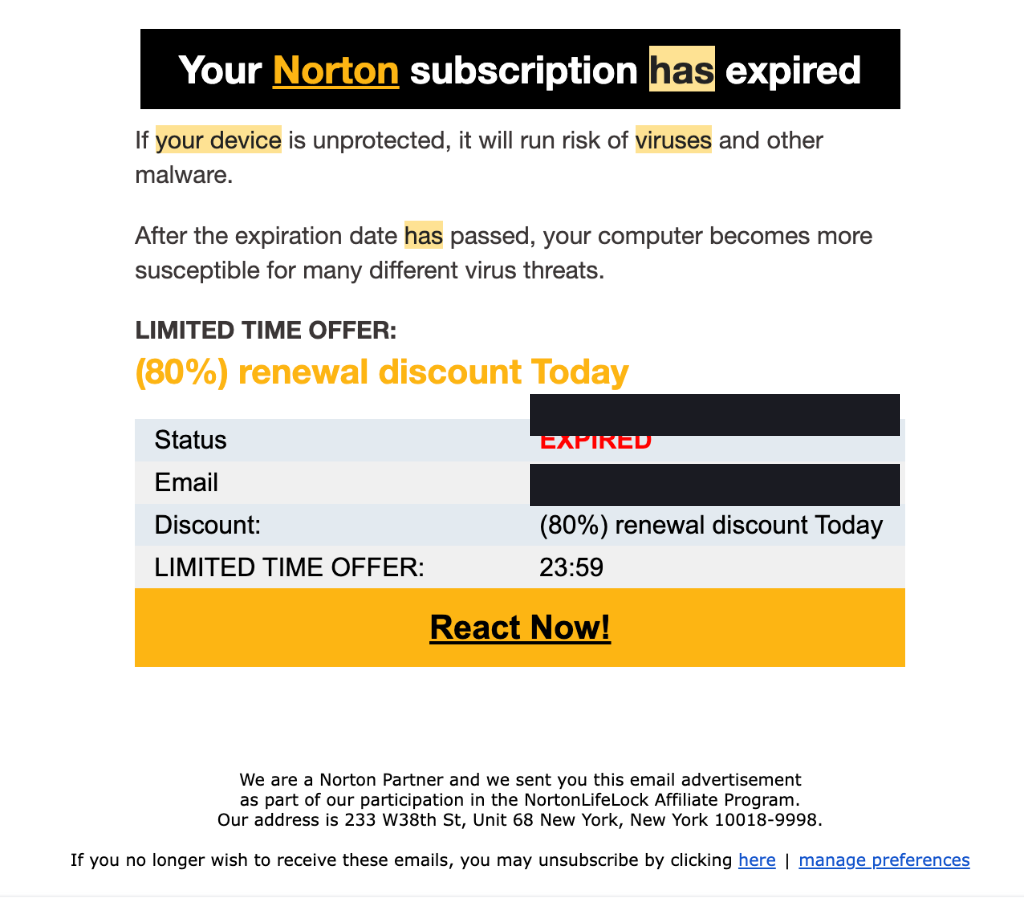
Case Study A: Norton Anti-Virus Expiration & Infection Lure
- Gmail Search Query:
Your NORTON Subscription HasorYour device has been infected with (22) viruses - Sender Domain:
ukb.zhukxkxqvbeey.us - Subject:
Your NORTON Subscription Has Expired — Your device has been infected with (22) viruses - Technique: Displays a fake urgent virus infection alert and subscriber ID, embedding static Google Cloud Storage redirector links (
storage.googleapis.com/smalbus/salaminka.html).
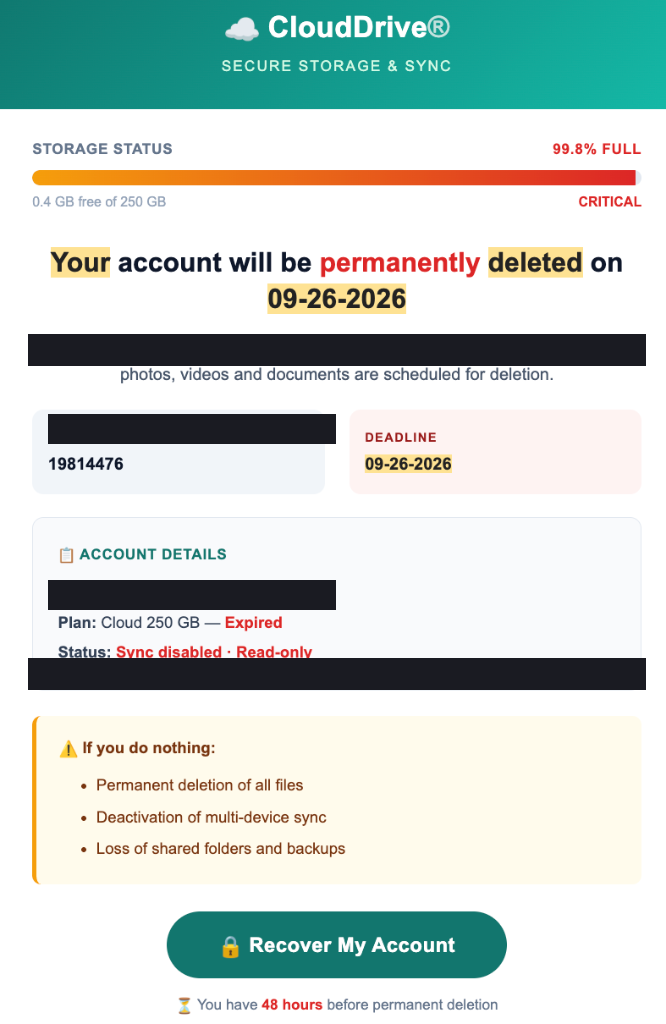
Case Study B: Cloud Storage Deletion Extortion Threat
- Gmail Search Query:
ACCOUNT SUSPENDED YOUR ACCOUNT AND ALL DATA WILL BE DELETEDorClaim your free renewal today - Sender Domain:
dawrnjdv.whatsapp.norquell.my.id - Subject:
Your account has been suspended! All your files and memories will be erased on 09-26-2026 - Technique: Leverages high-urgency loss-aversion threats claiming cloud storage backup files will be permanently erased, routing to static HTML buckets.
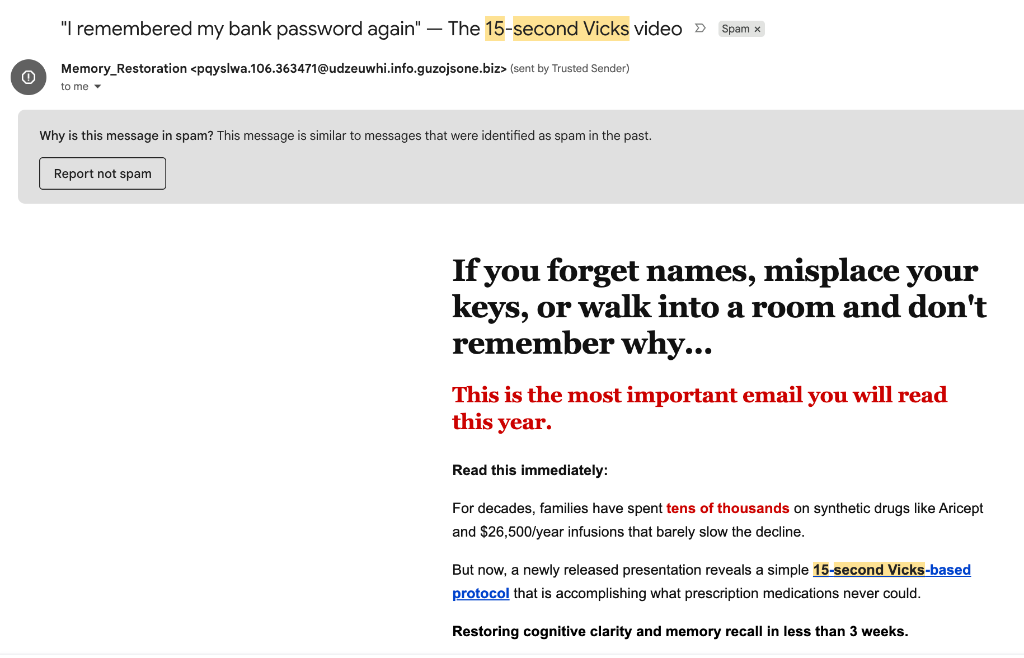
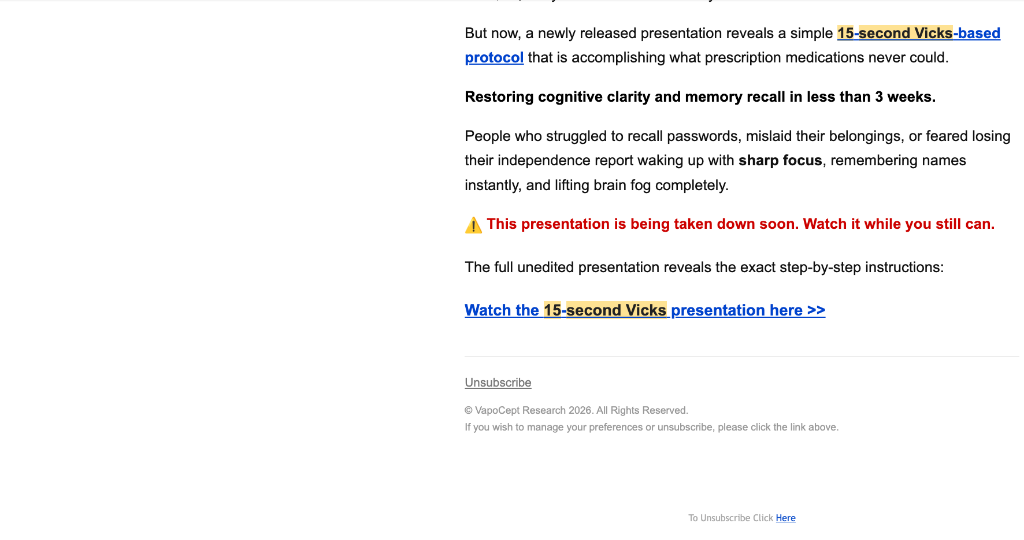
Case Study C: "VapoCept" 15-Second Vicks Memory Restoration Lure
- Gmail Search Query:
"I remembered my bank password again" — The 15-second Vicks video - Sender Domain:
udzeuwhi.info.guzojsone.biz - Subject:
"I remembered my bank password again" — The 15-second Vicks video - Technique: Promotes an absurd pseudoscience "Vicks-based protocol" by "VapoCept Research" claiming to cure memory loss and restore bank passwords in 15 seconds.
Threat Community & Sandbox Correlation
Our telemetry findings correlate directly with external threat intelligence repositories, automated sandbox submissions, and active phishing feeds tracking these exact Google Cloud Storage bucket redirectors:
Classification & Role: Primary intermediate HTML redirector actively observed dynamically routing targets via client-side URL hash parameters (#...).
Classification & Role: High-volume static HTML redirector landing page flagged across multiple credential harvesting and tech support submissions.
Classification & Role: Anti-bot evasion script and kit identifier (nobot-gogo-mail-bali) designed to detect and filter automated security crawlers before routing human victims.
Classification & Role: Tech support, browser locker, and urgency alert redirector variants (also observed alongside strow/strw_v3.html).
🍻 The Defensive Playbook
Apply these four security controls to protect organizational inboxes against cloud bucket redirection and DGA subdomain lures:
Inspect Public Cloud Bucket Links
Enforce gateway URL inspection for links pointing to storage.googleapis.com and s3.amazonaws.com to resolve final payload destinations before delivery.
Restrict Dynamic Regional Subdomains
Flag or score inbound email containing URLs or sender domains hosted on high-entropy .web.id, .my.id, .biz.id, and random .us subdomains.
Enforce FIDO2 / Passkey Authentication
Deploy phishing-resistant MFA (FIDO2 / WebAuthn / Passkeys) to neutralize credential harvesting portals accessed via email links.
Maintain Safe Sender Allowlists
Review spam gateway rules to ensure legitimate vendor communications (rewards updates, event bulletins) avoid automated spam folder placement.