5 posts tagged with "spam"

View All Tags

Spam Tales: DocuSign Homoglyph Attack

· 5 min read

Overview

A sneaky brand impersonation attack hit my inbox disguised as an urgent DocuSign notification (Your DОϹU91826661542441 is ready).

This campaign used a combination of:

  • homoglyph character substitution,
  • email service provider (ESP) abuse,
  • and open redirectors on compromised WordPress sites
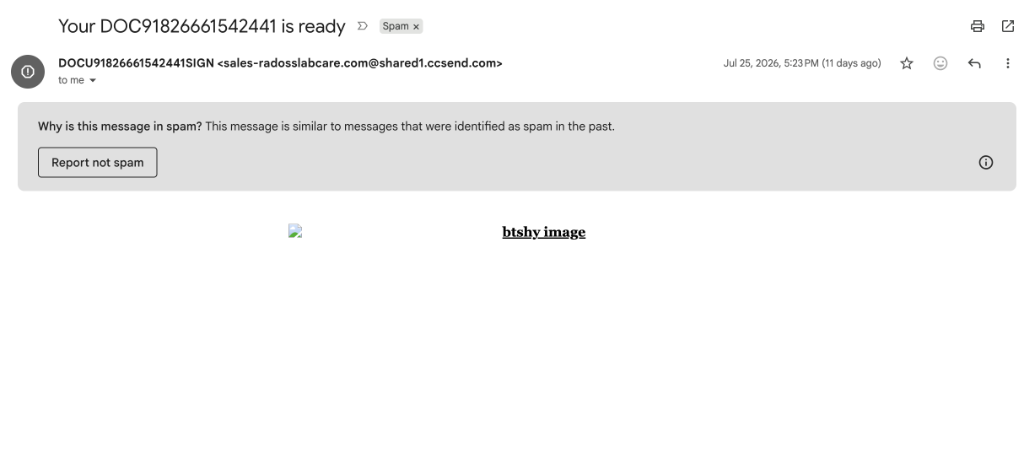
Gmail inbox header showing spam warning and subject line

Methodology

For this type of email lure, I like to preserve a few layers separately:

  1. Capture the rendered email and inbox spam warnings before interacting with links.
  2. Review the sender, recipient, timestamps, homoglyphs, and ESP authentication results.
  3. Inspect the raw HTML for hidden text, tracking, encoding tricks, and benign filler templates.
  4. Trace link redirects using sandbox analysis and isolated browser tools.
  5. Inspect the jump host environment, TLS certificate issuance history, and final landing page behavior.
  6. Extract reusable IOCs and construct detection logic.

Tools used

  • Email source view for MIME structure, DKIM signatures, and homoglyph decoding
  • Message authentication summary for SPF, DKIM, and DMARC results
  • urlscan.io, urlquery, etc. sandbox for link expansion, TLS cert analysis, and HTTP redirect tracing
  • Isolated browser inspection for domain, cPanel 404, and certificate details

Investigation

Email authentication

Raw Email Headers
Delivered-To: [email protected]
Received: by 2002:a05:6000:2981:20b0:470:1989:2b with SMTP id gl1-n2csp382087wrb; Sat, 25 Jul 2026 13:23:13 -0700 (PDT)
X-Received: by 2002:a05:622a:5b8b:b0:51c:11b4:6b24 with SMTP id d75a77b69052e-529a839eaf9mr30388281cf.3.1785010993037; Sat, 25 Jul 2026 13:23:13 -0700 (PDT)
ARC-Seal: i=1; a=rsa-sha256; t=1785010993; cv=none; d=google.com; s=arc-20260327; b=jc2U3u3oriGdaW3zKhRYbGj1CEYlYmguRS38AGYWbm8gveX7B86yYUiO0s0M7iBbF2 oVDANLiIYuaaZQGLDR0reqgBwZ8FaapypyN+eIFQQz13zOY69Kl91hlnt6APsmrCAEHz sq0bNJ+peR+l8qiavAjPF2K5scMRiVfpMmbRRmfX2oPTgZ1dZulB3VJCPiIRG3SE0UgA IdHcvE/1RTizvnx90LUIZreYH0JuUkw7/NWyH12XmRUgpHlddjT1Q62SLZC40bC1RbVo IxK/+z1OEzVDa0Zb3lExn0fV0gWFDHAWSa0tW8rLXR8b/7vr46YzjAEp8StEqQvWTrVG IM1g==
ARC-Message-Signature: i=1; a=rsa-sha256; c=relaxed/relaxed; d=google.com; s=arc-20260327; h=list-unsubscribe-post:list-unsubscribe:mime-version:subject:to :reply-to:from:date:message-id:dkim-signature:dkim-signature; bh=rEOILjV78ogHqX9MMMMGWZeCQ79y6ZHG/KxudsG5+H0=; fh=XM/DofkuIl8YxShyFh70zFRSv5HB1tzZL88CBxycvV0=; b=LQlyyeXe/82+ggZ+ecguRc8Bje5rKaICVaN8WfK5VGyNFWTtyCOZzIU+CSm26mtsoX aNt9hp0qgqo9fn3Rw+eL0dko0WoNQqiczHBcZSMvSG3csckaZQm6u4JF80aP0lH6AIBD 6FDNtr6KqPcT6INOkyjqb4SxVfDqrw1qPf90MqqP/2n1br3LQvOUx8bXrgZAAXu2lpVJ 34jLj4tWdHVd/IC/kNSaNad4jEb7qOgTZ8woyPaOq1Q7xZ6WZoM6LhkbzP/jM/9f9d/D 5ON5Vdpt+1LGYflnucMF849tTvHOtj4S45LwJ8gELIH1LEUJ1eiudFDXF+aS6/+cXbeF S8KQ==; dara=google.com
ARC-Authentication-Results: i=1; mx.google.com; dkim=pass [email protected] header.s=12042023 header.b=GhADEAp8; dkim=pass [email protected] header.s=1000073432 header.b=BQKKmA2h; spf=pass (google.com: domain of avmjokt7ttosjvgioqix2pq==_1142334191866_tcsumohmefg6vqjccjiaaw==@in.constantcontact.com designates 208.75.123.235 as permitted sender) smtp.mailfrom="AvMjokt7tTOSJVgiOqIX2PQ==_1142334191866_TCSUMohmEfG6vQJCCjIAAw==@in.constantcontact.com"; dmarc=pass (p=REJECT sp=REJECT dis=NONE) header.from=ccsend.com
Return-Path: <AvMjokt7tTOSJVgiOqIX2PQ==_1142334191866_TCSUMohmEfG6vQJCCjIAAw==@in.constantcontact.com>
Received: from ccm235.constantcontact.com (ccm235.constantcontact.com. [208.75.123.235]) by mx.google.com with ESMTPS id d75a77b69052e-529a2b0c0f6si37975291cf.265.2026.07.25.13.23.12 for <[email protected]> (version=TLS1_3 cipher=TLS_AES_256_GCM_SHA384 bits=256/256); Sat, 25 Jul 2026 13:23:13 -0700 (PDT)
Received-SPF: pass (google.com: domain of avmjokt7ttosjvgioqix2pq==_1142334191866_tcsumohmefg6vqjccjiaaw==@in.constantcontact.com designates 208.75.123.235 as permitted sender) client-ip=208.75.123.235;
Authentication-Results: mx.google.com; dkim=pass [email protected] header.s=12042023 header.b=GhADEAp8; dkim=pass [email protected] header.s=1000073432 header.b=BQKKmA2h; spf=pass (google.com: domain of avmjokt7ttosjvgioqix2pq==_1142334191866_tcsumohmefg6vqjccjiaaw==@in.constantcontact.com designates 208.75.123.235 as permitted sender) smtp.mailfrom="AvMjokt7tTOSJVgiOqIX2PQ==_1142334191866_TCSUMohmEfG6vQJCCjIAAw==@in.constantcontact.com"; dmarc=pass (p=REJECT sp=REJECT dis=NONE) header.from=ccsend.com
DKIM-Signature: v=1; q=dns/txt; a=rsa-sha256; c=relaxed/relaxed; s=12042023; d=shared1.ccsend.com; h=date:mime-version:subject:X-Feedback-ID:X-250ok-CID:message-id:from:reply-to:list-unsubscribe:list-unsubscribe-post:to; bh=rEOILjV78ogHqX9MMMMGWZeCQ79y6ZHG/KxudsG5+H0=; b=GhADEAp8Hl9mtinYMtmO7cWOCCfkJyHS3LNc2GWRAtNuJWkNoGaHi/9Mn5AC0R2x9gCnUJFU7NBOSCUkOpKM4jh7X9HwBKw/oJVofst4COXz82o/q9PG0ttDxYEjJnZRNnGjO4llhMuHa83FUIopPb9YhHcdS2ylLTsTmApBftJNwQpSi4vBJArC827YX/CW9PMDYCegUeRKUtiZJDhuMYVLLHF2LJxnYzqGoXW5Xoh89J8txf05xq9DXOiZtF//rulJJX5JvVb9cBjSPEGgm1n01mXrLLzGjX5y4f3yfpIpHT8yEFl6cERimZTUiR13jrd/q3TNqfA2fJr7RQ4IWw==
DKIM-Signature: v=1; q=dns/txt; a=rsa-sha256; c=relaxed/relaxed; s=1000073432; d=auth.ccsend.com; h=date:mime-version:subject:X-Feedback-ID:X-250ok-CID:message-id:from:reply-to:list-unsubscribe:list-unsubscribe-post:to; bh=rEOILjV78ogHqX9MMMMGWZeCQ79y6ZHG/KxudsG5+H0=; b=BQKKmA2hm8ll5kaH7Ta9cQdLtzW8O7KwoNkUV8ZpGduqEjcTTy2kyV3dyXK3iNE97k60jRjTTxISdFivzZh51sT8dzwirbvnsZiy6kcjRJemEYQWj6Eu05Ao4xROp38tMCeUnoDVyG2E+nGKpsPIztEjqgrOBgcDnL9H7gA7wsg=
Message-ID: <1142334703227.1142334191866.1072553232.0.291622JL.2002@synd.ccsend.com>
Date: Sat, 25 Jul 2026 16:23:12 -0400 (EDT)
From: =?utf-8?Q?D=D0=9E=CF=B9U91826661542441=D0=85=D0=86G=CE=9D?= <[email protected]>
Reply-To: [email protected]
To: [email protected]
Subject: =?utf-8?Q?Your_D=D0=9E=CF=B991826661542441_is_ready?=
MIME-Version: 1.0
Content-Type: multipart/alternative; boundary="----=_Part_275054477_708520069.1785010992844"
List-Unsubscribe: <https://visitor.constantcontact.com/do?p=un&m=001st0JLJ3BRgXpr0CayrEO5A%3D%3D&se=001cBN8W11zlBDfFajHrVJgTw%3D%3D&t=001EkZLEx15CcE%3D&llr=9h5yg7hbb>
List-Unsubscribe-Post: List-Unsubscribe=One-Click
X-Campaign-Activity-ID: bcc8e892-deed-4ce4-8956-088ea885f63d
X-250ok-CID: bcc8e892-deed-4ce4-8956-088ea885f63d
X-Channel-ID: 4c249432-8866-11f1-babd-02420a320003
X-Return-Path-Hint: AvMjokt7tTOSJVgiOqIX2PQ==_1142334191866_TCSUMohmEfG6vQJCCjIAAw==@in.constantcontact.com
X-Roving-Campaignid: 1142334703227
X-Roving-Id: 1142334191866.1072553232
X-Feedback-ID: 4c249432-8866-11f1-babd-02420a320003:bcc8e892-deed-4ce4-8956-088ea885f63d:1142334191866:CTCT
X-CTCT-ID: 4c14f3f6-8866-11f1-babd-02420a320003

The message presented itself as:

From: DОϹU91826661542441ЅЅGΝ <[email protected]>
Subject: Your DОϹU91826661542441 is ready
Date: Sat, 25 Jul 2026 16:23:12 -0400

Observed authentication results:

SPF: PASS (google.com: domain of constantcontact.com designates 208.75.123.235 as permitted sender)
DKIM: PASS (shared1.ccsend.com and auth.ccsend.com)
DMARC: PASS (p=REJECT header.from=ccsend.com)

Because Constant Contact (ccm235.constantcontact.com / 208.75.123.235) is a legitimate bulk email marketing platform, the message passed all standard email authentication checks.

To evade automated Natural Language Processing (NLP) anti-phishing rules that flag words like DocuSign, the attacker replaced standard Latin characters with visually identical Cyrillic and Greek Unicode characters:

  • Subject String: DОϹU91826661542441
    • О → Cyrillic Capital Letter O (U+041E)
    • Ϲ → Greek Lunate Sigma Symbol (U+03F2)
  • Sender Display Name: DОϹU91826661542441ЅЅGΝ
    • Ѕ → Cyrillic Capital Letter Dze (U+0405)
    • Ν → Greek Capital Letter Nu (U+039N)

HTML filler

The HTML and plain text bodies contained a complete template for a business (radosslabcare) with a discount code (SAVE20).
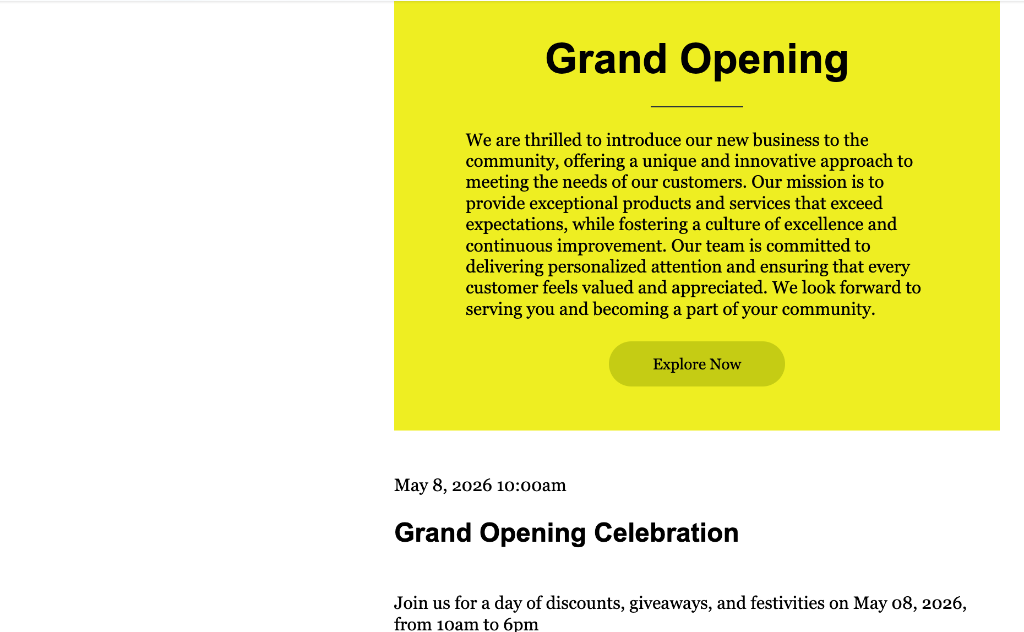
Rendered email body showing Grand Opening celebration copy

Inserting benign commercial text serves a dual purpose:

  1. Classifier Confusion: Spam filters scoring content intent classify the body as a standard commercial promotional message.
  2. Hidden Links: The actual visual link is tied to a large transparent overlay image pointing to the attacker's infrastructure.
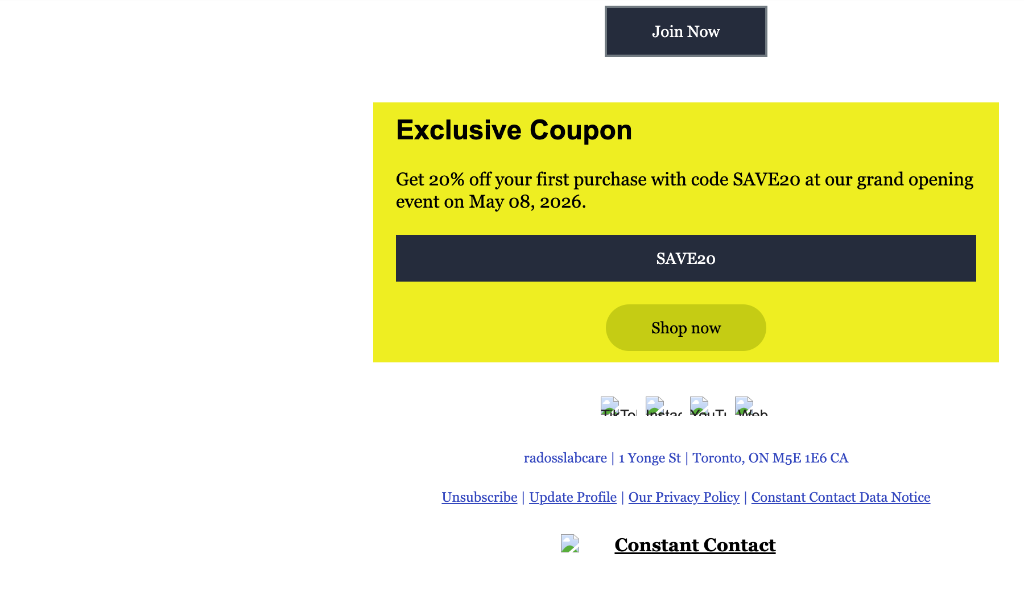
Rendered email footer showing coupon SAVE20 and Constant Contact branding

The primary link embedded in the message was wrapped via Constant Contact's tracking service:

https://9h5yg7hbb.cc.rs6.net/tn.jsp?f=001_jBSTymjOra5YfUT2qw9hXuChXdeMd26MdFnOw_DbLc1sErBjhURTLTMTGY1qUhLe-CFnbKIXq--vZW5n-j2kJY3Ppl89Kbs5dsCembTC1ceSa8NM80a0Sj8U1OOYU5GfqnHWCBbUfIr8gOQSqNt3YSq9_e4B0uJ

Which resolved to the first-stage jump host:

https://mcguiganflooring.com/mcguiganflooring/

Unsubscribe behavior

The message included standard Constant Contact unsubscribe headers and footer links:

List-Unsubscribe: <https://visitor.constantcontact.com/do?p=un&m=001st0JLJ3BRgXpr0CayrEO5A%3D%3D...>
List-Unsubscribe-Post: List-Unsubscribe=One-Click

Because legitimate ESP headers were used, mail clients recognized one-click unsubscribe functionality, further helping the message bypass initial email filters.

Redirect script

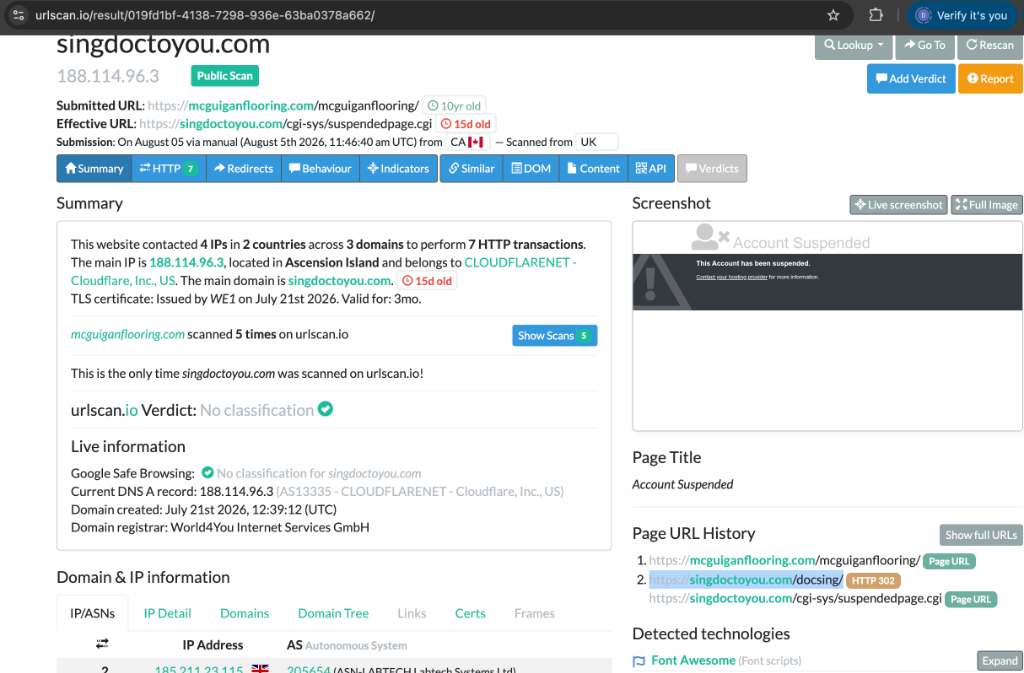
The jump host (mcguiganflooring.com/mcguiganflooring/) performed an HTTP 302 redirect directly to the second-stage domain:

HTTP/1.1 302 Found
Location: https://singdoctoyou.com/docsing/

Resulting redirect

The destination of the redirect chain was:

https://singdoctoyou.com/docsing/
  • Target Domain: singdoctoyou.com (possible typosquatting/anagram spoofing DocuSign).
  • Path: /docsing/ (doc-sing).
  • Domain Registration Date: July 21, 2026 (Registered just 4 days before the email was sent).
  • Hosted On: Cloudflare (188.114.96.3).

urlscan.io scan results for singdoctoyou.com showing suspended account and Cloudflare WAF block

By the time of inspection, the host and domain were suspended (/cgi-sys/suspendedpage.cgi), and Cloudflare WAF was blocking incoming connections.

I was too late, bummer!

Redirect host cover page and certificate

Examining the jump host (mcguiganflooring.com):

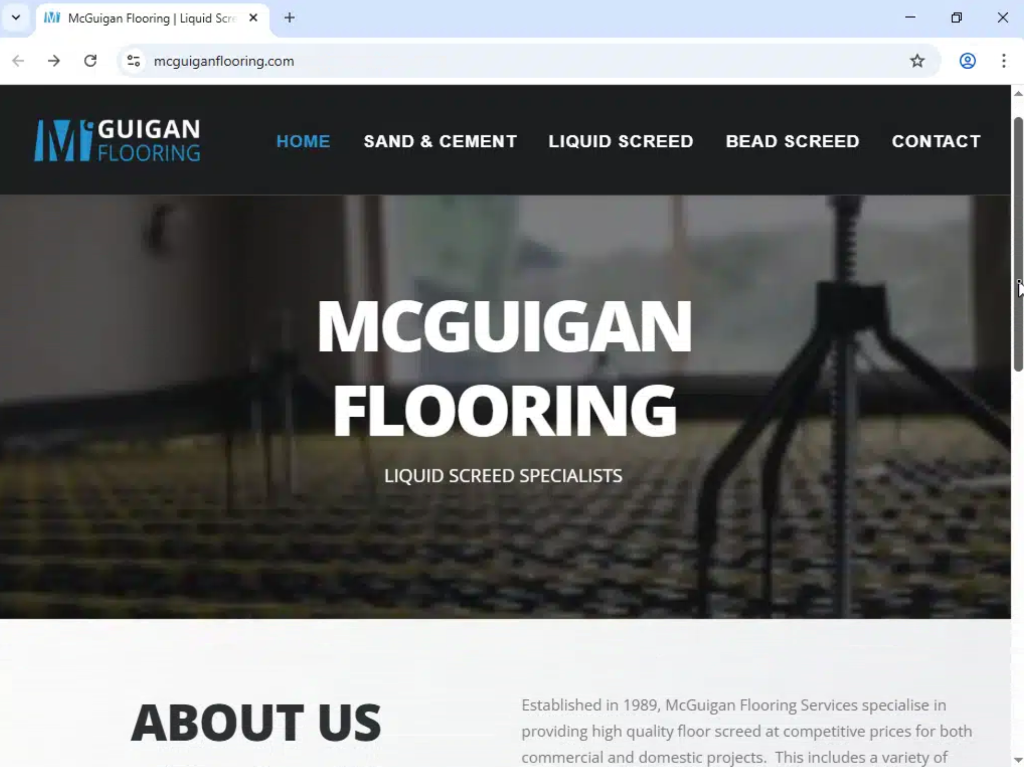
  • The initial link points to a UK flooring business website (mcguiganflooring.com).

McGuigan Flooring business homepage

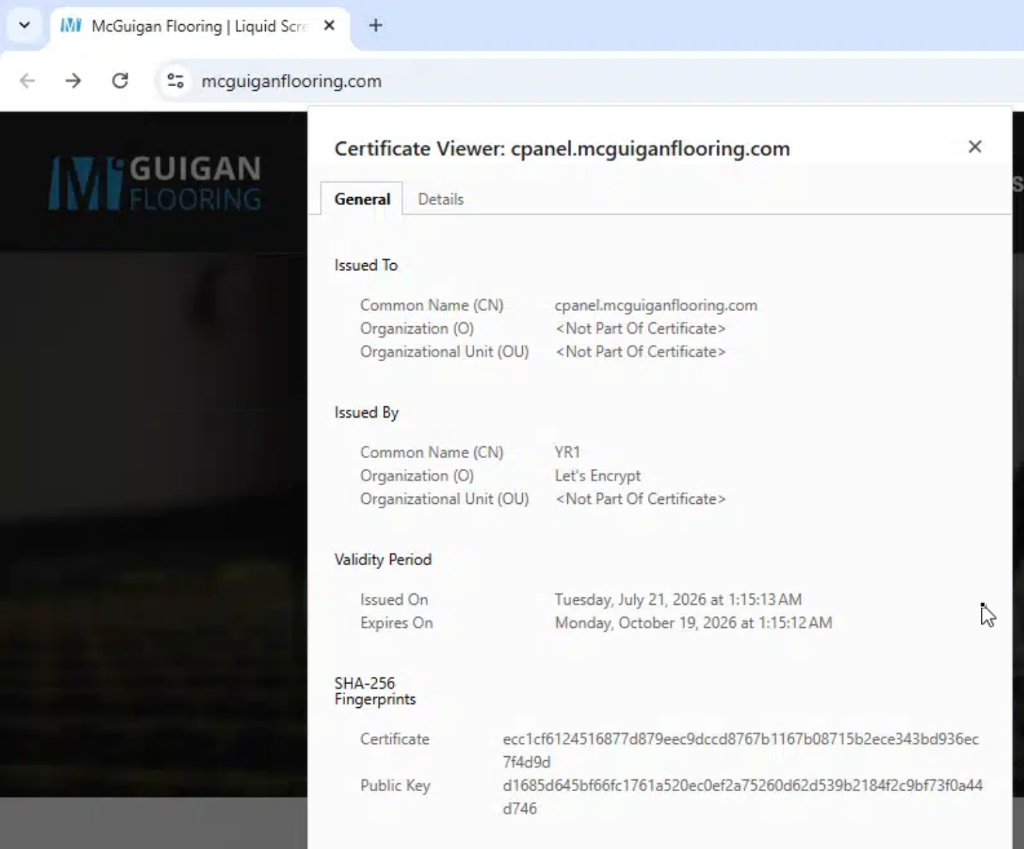
  • cPanel Compromise Timeline Correlation: Inspecting the SSL certificate for cpanel.mcguiganflooring.com reveals a Let's Encrypt TLS certificate issued on July 21, 2026 at 01:15 AM UTC — just 11 hours before the attacker registered the phishing target singdoctoyou.com (July 21 at 12:39 PM UTC)!

Certificate viewer showing Let&#39;s Encrypt cert issued for cpanel.mcguiganflooring.com on July 21, 2026

  • Server Environment: Visiting missing subpaths (e.g. /liquid-screed/) returns a standard cPanel / Apache 404 error (The requested URL was not found on this server. Additionally, a 404 Not Found error...), indicating an underlying cPanel hosting account.
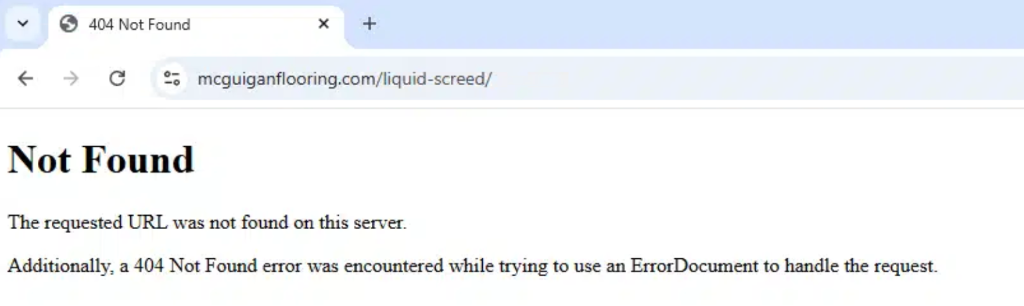
Apache 404 error page on mcguiganflooring.com

  • Historical scans reveal this host was previously compromised to host probable credential theft scripts (e.g., /zz/enterpassword.php).
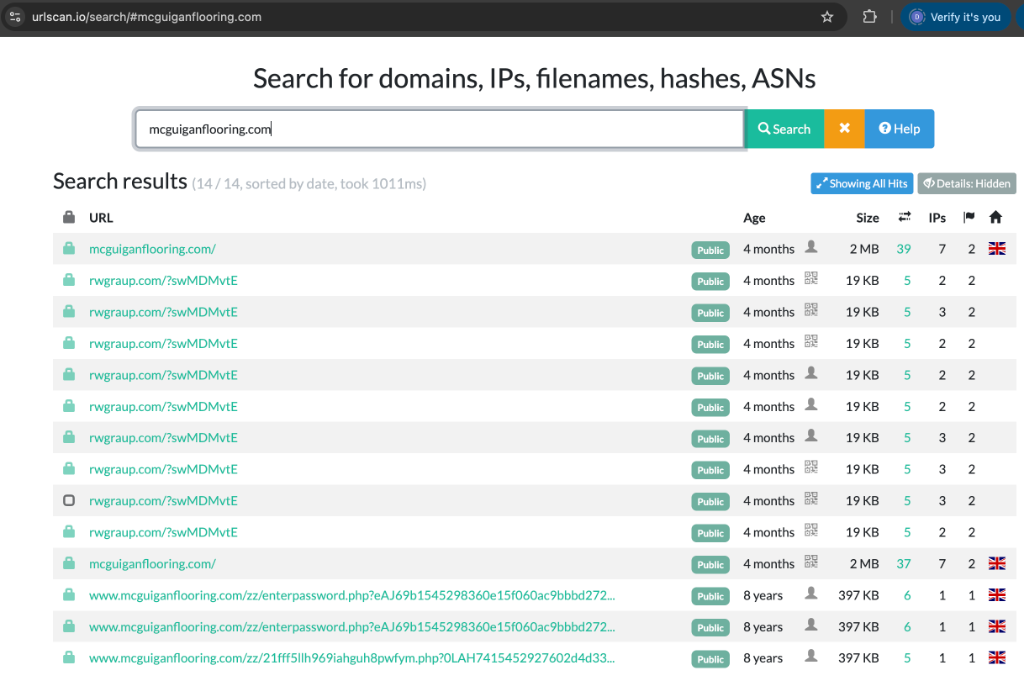
urlscan.io search results for mcguiganflooring.com

IOCs

Indicator TypeValueDescription
Phishing Domainsingdoctoyou.comTyposquatted DocuSign Phishing Host
Phishing Path/docsing/Phishing credential harvester endpoint
Compromised Hostmcguiganflooring.comOpen Redirector / Compromised CMS

Detection Logic

IF
Subject or Display Name contains non-ASCII homoglyphs resembling brand names (DocuSign)
AND Email originates from legitimate ESP infrastructure (Constant Contact / ccsend.com)
THEN
Homoglyph ESP abuse phishing attempt likely

Observations & Conclusions

  1. The attacker abused a legitimate Email Service Provider (Constant Contact) to obtain clean SPF, DKIM, and DMARC pass results.
  2. Homoglyph character substitution (Cyrillic and Greek Unicode characters) was used in both the Subject and Display Name to bypass string-matching security rules.
  3. The email body was stuffed with benign commercial promotional text to confuse content-based classification engines.
  4. The initial link leveraged a compromised UK flooring company (mcguiganflooring.com), whose cPanel SSL certificate was re-issued just 11 hours before the phishing target domain was registered on July 21, 2026.
  5. The final target (singdoctoyou.com/docsing/) was suspended shortly after the campaign launched.
Indicators of Compromise (IOCs)
IOCs (domains, IP addresses, files, hashes, etc.) from this analysis are available on GitHub.
View on GitHub →

Spam Tales: Prime Subscription Expired

· 5 min read

Overview

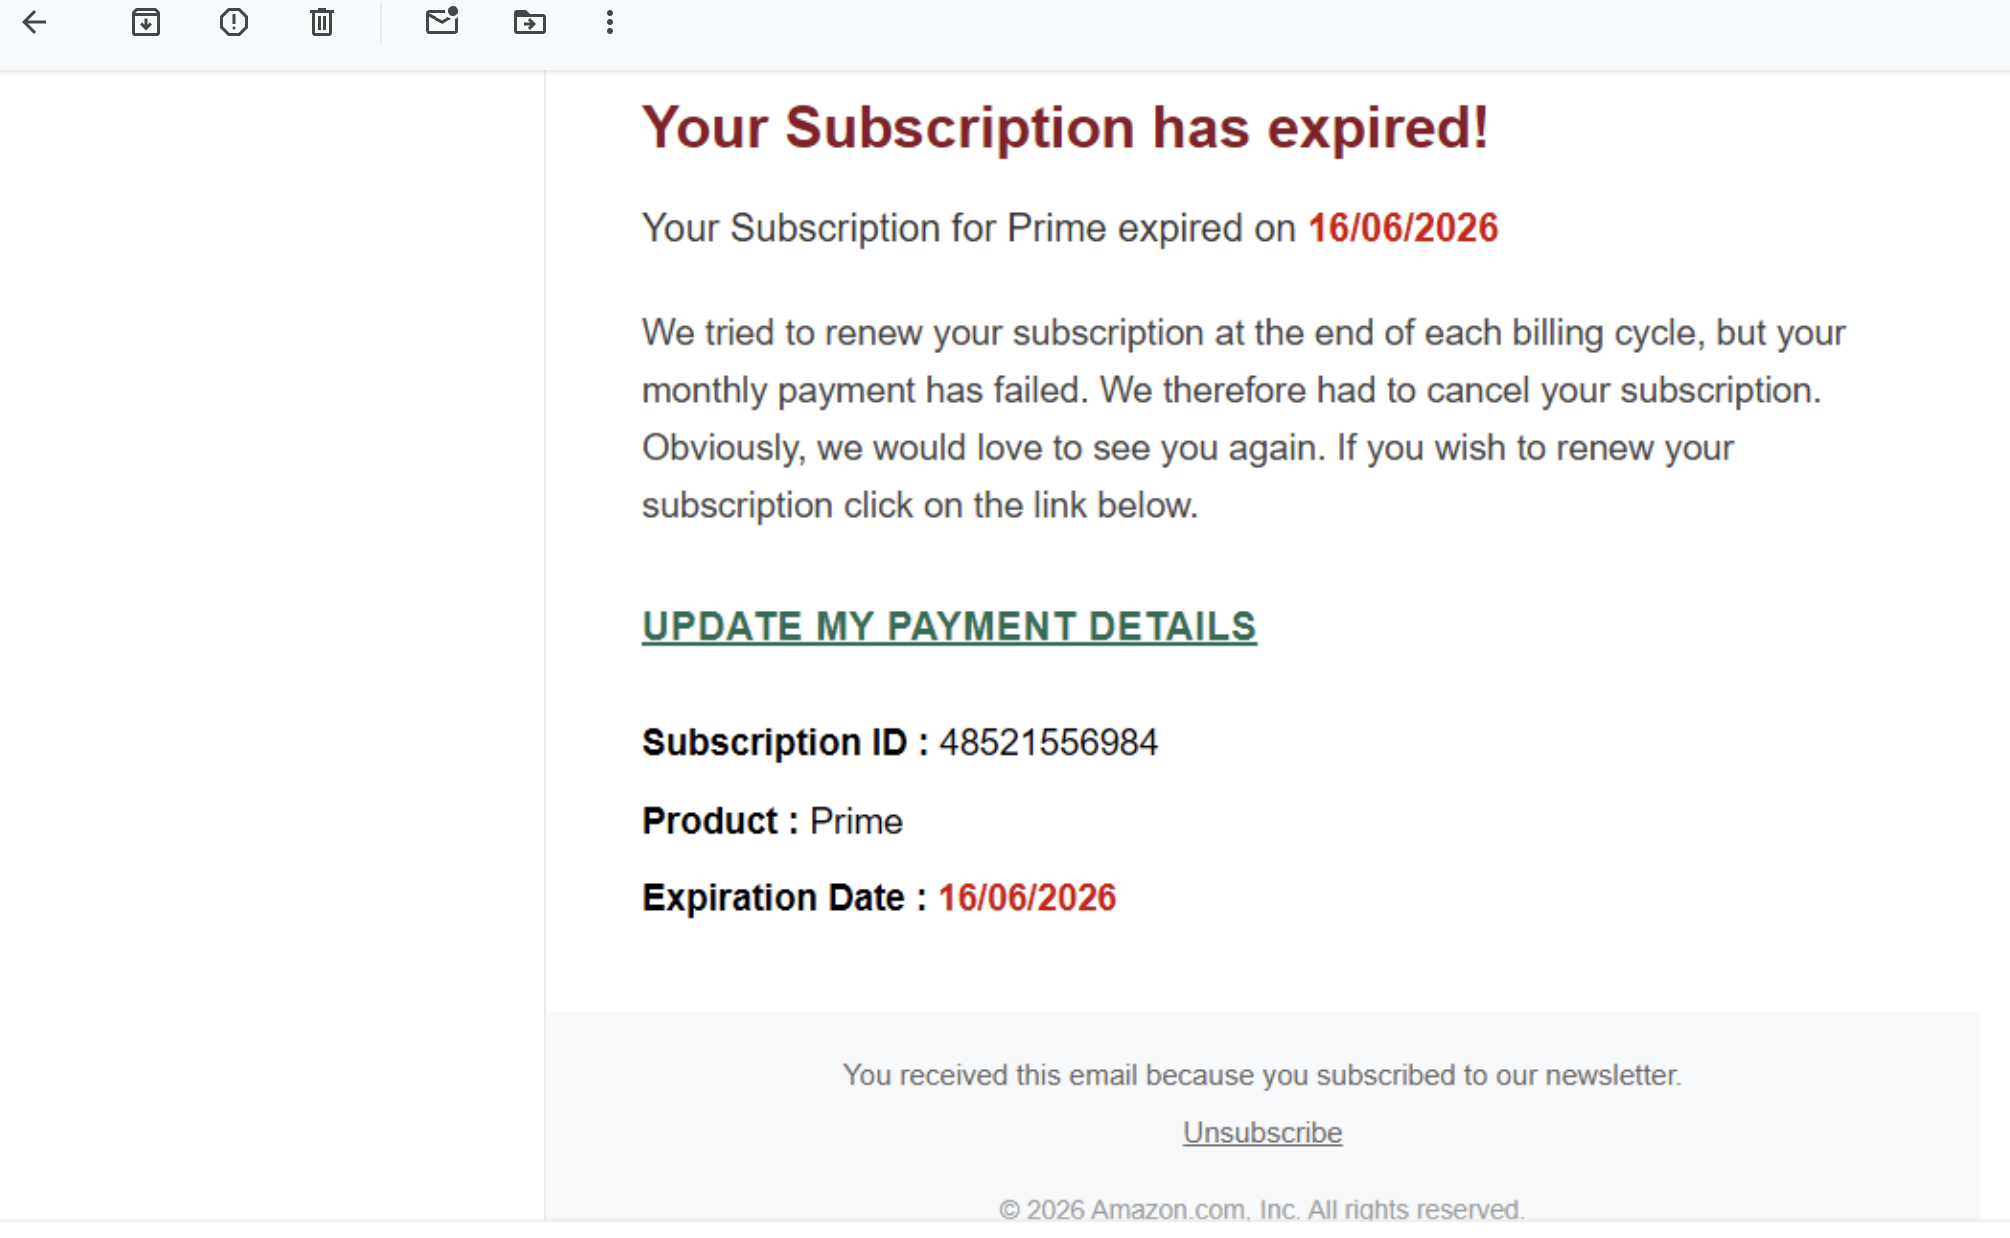
Oh no, my Prime subscription expired!

Rendered Gmail message showing a fake Prime Video terms and conditions lure

Your Subscription has expired!
Your Subscription for Prime expired on 16/06/2026
UPDATE MY PAYMENT DETAILS

The message appears like this in the inbox:

From: comoe ber <[email protected]>
Subject: Re: Reaching Out
Date: Sun, 14 Jun 2026 17:36:16 -0700

The body impersonates Prime Video, but the subject says nothing about Prime. It uses Re: Reaching Out, which is wonderfully vague.

Rendered Gmail message showing fake Prime subscription expiration details

The invoice-ish bit claims:

Subscription ID: 48521556984
Product: Prime
Expiration Date: 16/06/2026

The footer says:

You received this email because you subscribed to our newsletter.
© 2026 Amazon.com, Inc. All rights reserved.
Classic payment-recovery bait. Nothing about the sender path, unsubscribe metadata, or link hosting belongs to Amazon.

Methodology

For this sample, I preserved a few layers separately:

  1. Capture the rendered email before interacting with any links.
  2. Review the sender path, authentication results, and SMTP submission trail.
  3. Pull out the action URLs, image URLs, and unsubscribe URLs.
  4. Check whether the first-hop infrastructure is still alive.
  5. Separate reusable campaign-looking artifacts from one-off junk and copied residue.

Tools used

  • Gmail original message view for headers and raw source
  • Local IOC extraction from the HTML and MIME body
  • Browser screenshots for the rendered lure and dead hosted object(s)

Email Headers

Raw Email Headers
Delivered-To: [email protected]
Received: by 2002:a5d:4388:0:b0:45e:c606:5a52 with SMTP id i8csp801548wrq; Sun, 14 Jun 2026 17:36:18 -0700 (PDT)
X-Received: by 2002:a05:6a00:1255:b0:82c:20ec:6589 with SMTP id d2e1a72fcca58-8434d08fb02mr6040631b3a.3.1781483777888; Sun, 14 Jun 2026 17:36:17 -0700 (PDT)
ARC-Seal: i=1; a=rsa-sha256; t=1781483777; cv=none; d=google.com; s=arc-20240605; b=WXdSVVEbcWalqUt+DtNLzYELJ8MIlL5r/zW+zYUN4uJlzXJMwNRjiOfw1jDGLFtg3K MSipq63Y//xPdHr0xPRl6YT9raexezQw0ZL+cYGcgy2IJTjImUVEiXfNhbte6MsOi4FF zka/HHoLgRw+hawZlUtfMoI/4G3Zw0+kYc+L3VdAa6t04aa76J9yXBev+NacbX6VCFBr TozAuNMDroQEAfQy6mt7JurdNsWRBMoJ6PuWcJZvyKEWFsQO3HzSKFLonjTXXIG6Qd6b E1SxU38WmsE+uJvpwFGCcUV9ykK3WAXXqUy/Ik9q/ckSUd6UJzhd2T8uZKhk4Nwu5d2A 08mA==
ARC-Message-Signature: i=1; a=rsa-sha256; c=relaxed/relaxed; d=google.com; s=arc-20240605; h=feedback-id:list-unsubscribe-post:feedback-id:content-id:cf-2025-91 :message-id:list-unsubscribe:content-transfer-enfcoding:references :feedback-id:mime-version:campaign_id:rcpt_domain:subject:errors-to :in-reply-to:cc:to:from:date:dkim-signature; bh=mTrkK2dTQwWekvdaUHi04OhpuIfdToDLenjNp7IBUG0=; fh=uCpEWAVPefAsuxydQrQ6jFza+PFTZWbqjgkrsdbsK38=; b=Ptv/3vp6JACgAQAq5uLmmTWv33sqyb051RWBIIEg4vjrEjw5DLCDthmXAoYI2xSqPE pWDaaEbquE85ryVjvCUD95Qydbycbsf5V5BQywNnvGBggERu9QfGxYq/ZNDVf/5/S1RJ O1avKjDFwDHj7DNW3SXhBZFg3nkRlZbAtJ23P+YCu12KGagp/HvtiJH3Fw13g/wKdjlx TlXIo8S/XiEDObNDD7OA4/OB5/V9KvxslryllgRR+ss3sA71PYlvpVKAGILrDGGZhtPu pDBqK78f3FtJvWXmc5QLxYVdLMGSfp1ifMd1mMda89wnDBoEZHwskdTLAJlxTPG+WEc2 uFxA==; dara=google.com
ARC-Authentication-Results: i=1; mx.google.com; dkim=pass [email protected] header.s=20251104 header.b=mWvC9KDg; spf=pass (google.com: domain of [email protected] designates 209.85.220.65 as permitted sender) [email protected]; dmarc=pass (p=NONE sp=QUARANTINE dis=NONE) header.from=gmail.com; dara=pass [email protected]
Return-Path: <[email protected]>
Received: from mail-sor-f65.google.com (mail-sor-f65.google.com. [209.85.220.65]) by mx.google.com with SMTPS id d2e1a72fcca58-8434acd1953sor1901458b3a.1.2026.06.14.17.36.17 for <[email protected]> (Google Transport Security); Sun, 14 Jun 2026 17:36:17 -0700 (PDT)
Received-SPF: pass (google.com: domain of [email protected] designates 209.85.220.65 as permitted sender) client-ip=209.85.220.65;
Authentication-Results: mx.google.com; dkim=pass [email protected] header.s=20251104 header.b=mWvC9KDg; spf=pass (google.com: domain of [email protected] designates 209.85.220.65 as permitted sender) [email protected]; dmarc=pass (p=NONE sp=QUARANTINE dis=NONE) header.from=gmail.com; dara=pass [email protected]
DKIM-Signature: v=1; a=rsa-sha256; c=relaxed/relaxed; d=gmail.com; s=20251104; t=1781483777; x=1782088577; dara=google.com; h=feedback-id:list-unsubscribe-post:feedback-id:content-id:cf-2025-91 :message-id:list-unsubscribe:content-transfer-enfcoding:references :feedback-id:mime-version:campaign_id:rcpt_domain:subject:errors-to :in-reply-to:cc:to:from:date:from:to:cc:subject:date:message-id :reply-to; bh=mTrkK2dTQwWekvdaUHi04OhpuIfdToDLenjNp7IBUG0=; b=mWvC9KDgsWQ1bTXsaOMw9pJSriAZptfpYubgIVY8BJbAevcmKU1ZA40FiwzXpcV7VL hNwQ7BnsyLvVwBw7mQg+aoN8EfsU45QwyzB/ATi95bGYxDQB+k2EOd674c/A8+ir5wTE Kf5MaScg3BrBn5VnohoiYaO1jVQW7WQjQAHAQMfx3S3s8Ad5DhXWlPZH4sBDxtScaa+e bUBthn+1QUOfhFoKWtuwOWK4wvu999pkXHLuG/klLvNUYe7kDhz2RUAcpDDJ0jbYTwOW vDEco4l4v9jW349XUE9YoPSyRZs28fNPmSw3WgvA3+tp5+LKeXKQUBbYg+iDbv3jiASV rlXw==
X-Google-DKIM-Signature: v=1; a=rsa-sha256; c=relaxed/relaxed; d=1e100.net; s=20251104; t=1781483777; x=1782088577; h=feedback-id:list-unsubscribe-post:feedback-id:content-id:cf-2025-91 :message-id:list-unsubscribe:content-transfer-enfcoding:references :feedback-id:mime-version:campaign_id:rcpt_domain:subject:errors-to :in-reply-to:cc:to:from:date:x-gm-gg:x-gm-message-state:from:to:cc :subject:date:message-id:reply-to; bh=mTrkK2dTQwWekvdaUHi04OhpuIfdToDLenjNp7IBUG0=; b=MwwPg8NnEI7b8AWcFbfmRq3sp9JlySSjqiLflSrUKDE/ub9uzBS8WsnscCtu5N6F30 iAKuBtJUJ0kHtmXncN0S92YLfYje4udTdHAInQMff3qDYIJFyvfGwIs3mF8pHUHgITuG 86OKRBK8Y6eL/7B+e38ZhQGn48XIh1x9d6QqjRI4bS2Bym9QDPK17MxwA4XESYmnOGQt lLUryGZe1yiMb/FVqAf19hp9qUXQ5zP0uP/Qw+LI0moElsEFGLwmvLhO8D7eJdS/Z6bX aXi0UCUVCRVql0t6HUKT+nDKOFJG8dZBuzCUgWzNV9bTlxOmsSJbdQ1K7is5/izoSjqm 6rJA==
X-Gm-Message-State: AOJu0YxI8GYLJ96NfL0w+RBy/hF5rM48gQ0r3P6XKAA16EIcFfYmohng UTOWh+cOr3xN/TSnICZCHm/0670fN/Ddg3BdHgTcwE3jEkXG3TH8gL7QL7UYLiKS5agl7Js0
X-Gm-Gg: Acq92OFX8Z1YDCVzvedDSyrbpTJBJUyfOfwqoBGvESQmJnULj4OtZbaBHfpjWw87kKq MTEgf6o1Y0le/u04HhAXqUCxSa2CcawXYRR9N3pBdaBblGjWvV9NjRHOon/s4EB27iY0kIc3gSr 9C8DNroBpyUzViXz7mNjc7Ws75iHv8n9ePNOL1fKLD9VvfZM8dmQ5in/hLqqOPxP5eI7k54MCZ+ ak7vvVASBe8JS4U+8flYg/qjUUVlj8ElyqLtCgwiTTc6Ty/itabvK/hsKR1tqXMI4vtu/ll3RTM sfg5tbZWl8+Atpztk/ZmCrUWNh9T6fsO3TZSOm7ZwoH/74TD5EvIseOdjMLJuwMnc4/LEp1j3bv 7anDYgaaLcncu4AIMuGM5OPwDtkc/wDSh8pey3GA2n5m9MJ7VH8e8iKKxzHwahCtliCGbUIOS83 kUGfIkqFR/eqrUdjMvJNIafYu/zWB+juftrw+Uvmws0ZMaSSa/hvuDB8JNP8okla2R6nCSxQ+6d SIQMg2kgQRlQkMAuBkvfcHKeytSnIVK4BKfU4BJ71XVdhb5Oh/a3TpMqhY1y/dKfuDzFrSW/qvh SY2gQa2T3XpnsYQ=
X-Received: by 2002:a05:6a00:340d:b0:842:2cda:7aa2 with SMTP id d2e1a72fcca58-8434d0abff6mr13127653b3a.30.1781483777235; Sun, 14 Jun 2026 17:36:17 -0700 (PDT)
Return-Path: <[email protected]>
Received: from mail.Calixo.me (ec2-13-204-180-155.ap-south-1.compute.amazonaws.com. [13.204.180.155]) by smtp.gmail.com with ESMTPSA id d2e1a72fcca58-8434accbc89sm8443948b3a.15.2026.06.14.17.36.16 for <[email protected]> (version=TLS1 cipher=ECDHE-ECDSA-AES128-SHA bits=128/128); Sun, 14 Jun 2026 17:36:16 -0700 (PDT)
Date: Sun, 14 Jun 2026 17:36:16 -0700 (PDT)
X-Google-Original-Date: [smtp_date]
From: comoe ber <[email protected]>
X-Google-Original-From: comoe ber <[email protected]>
To: "[email protected]" <[email protected]>
X-rpcampaign: stcsp99709194
X-SG-EID: [aa_7]/[aa_49]+/bXwD3nnE226p/imTTAl/87k5Ymm84hMsEQPntlZ3Kma7BgkFnHVg1BYF+87k5Ymm84hMsEQPntlZ3Kma7BgkFnHVg1BYF/vVAHG/ZliEmOU9KeL1zjpkig2seBqoM8PVwWvIpjcfWw7k2sj0RwsR+DZTbItn27lXc1NE/rUhaq7ywc0i9RCoXhZTpxyZJfZ2mqHAPlv==?
X-campaignid: rUhaq7ywc0i9RCoXhZTpxyZJfZ2mqHAPlv.lBMErXjNLv
CC: "[to]" <[to]>
X-Feedback-ID: 1781223:SG
In-Reply-To: <[email protected]><Zb1JlTI9ZVDf7PhkzRRdcGmtzJ3VbJBwpX3PrlZ52TcU@vVAHG-GOe47.sog.unc.edu>
Errors-To: [email protected]
X-Report-Abuse: <[email protected]>
Subject: Re: Reaching Out
X-Mailer: PHPMailer 6.9.2 (https://github.com/PHPMailer/PHPMailer)
X-SFMC-Stack: 7
rcpt_domain: gmail.com
X-SG-EID: [aa_7]/[aa_49]+/bXwD3nnE226p/imTTAl/87k5Ymm84hMsEQPntlZ3Kma7BgkFnHVg1BYF+87k5Ymm84hMsEQPntlZ3Kma7BgkFnHVg1BYF/vVAHG/ZliEmOU9KeL1zjpkig2seBqoM8PVwWvIpjcfWw7k2sj0RwsR+DZTbItn27lXc1NE/rUhaq7ywc0i9RCoXhZTpxyZJfZ2mqHAPlv==?
X-JMailer: ip-10-55-95-109.ec2.internal
X-Kmail-Account: f0cVbI
campaign_id: 511517
MIME-Version: 1.0
Feedback-ID: f0cVbI:4OYyS5k0Ot9:forms::container:CK
X-Report-Spam: <[email protected]>
X-TM-ID: 8698350323148187.99709194.27060
X-Entity-ID: 23agIQTx4WWT24fC67Lvzn==?=
References: <[email protected]> <[email protected]>
Content-Transfer-Enfcoding: 7bit
List-Unsubscribe: <https://www.sog.unc.edu/unsubscribe/?aZ9hLS37Zd91hzoEfxXskzOuF6tK2qoHOjqyBJ8LXAPAdw49cpQcH57p7niszKuQmwiHdTyMadmLsZ8zqpABkd2yJvmKTlhwCKQ9Ho3Nr0ihGN0LEHN1NTz47==>
Message-ID: <AC500000000pYOJKYIyXXKPWBjLmscom_mkt_prod8@[placeholde1]>
X-Auto-Response-Suppress: OOF, AutoReply
X-Feedback-ID: 1835:99709194:campaign:sailthru
X-Campaign: rUhaq7ywc0i9RCoXhZTpxyZJfZ2mqHAPlv.lBMErXjNLv
X-SFMC-Stack: 7
cf-2025-91: 
X-Google-Original-From: "GoogleAlerts" <[email protected]>
Content-Id: <[email protected]>
X-Mailer: AWeber Composer 2.72.4
X-Unsubscribe-Web: https://sog.unc.edu/oc/Mn0nfocytOPSbvR5uBz8TB3HvVuAyL.9dzs/7b80de18
Feedback-ID: f0cVbI:4OYyS5k0Ot9:04
List-Unsubscribe-Post: List-Unsubscribe=One-Click
Content-Type: multipart/signed; boundary="-------3dAw2PEf--==--9dzs-==--3dAw2PEf--==--"; type="multipart/alternative"
Feedback-ID: ::1.ap-southeast-1.pYOJKYIyXXKPWBjL+cezwlDkKAyWMxqc3po7Y=:AmazonSES
X-SES-Outgoing: 2026.03.16-172.31.15.162

---------3dAw2PEf--==--9dzs-==--3dAw2PEf--==--
Content-Type: multipart/report; boundary="_-------nhrZSyTQIA3kZSwurm8O.DZTbItn27lXc1NE-959873471455850nhrZSyTQIA3kZSwurm8O.DZTbItn27lXc1NE=:"

--_-------nhrZSyTQIA3kZSwurm8O.DZTbItn27lXc1NE-959873471455850nhrZSyTQIA3kZSwurm8O.DZTbItn27lXc1NE=:
Content-Type: text/html;charset="UTF-8"

<!DOCTYPE html>
<html lang="en">
<head>
  <meta charset="UTF-8">
  <title>bXwD3nnE226p</title>

  <style>
    body.app-root {
      margin: 0;
      padding: 50px 0;
      background-color: #ffffff;
      font-family: Arial, Helvetica, sans-serif;
      text-align: center;
    }

    table.layout-grid {
      width: 100%;
      border-collapse: collapse;
    }

    template-container {
      display: block;
    }

    .module-wrapper {
      width: 95%;
      max-width: 720px;
      background-color: #1f0b09;
      border-radius: 16px;
      box-shadow: 0 0 36px rgba(255, 99, 71, 0.45);
      overflow: hidden;
      border: 1px solid white;
    }

    .banner-block {
      background: linear-gradient(135deg, #020617, #1e40af, #3b82f6);
      padding: 38px;
      text-align: center;
      position: relative;
    }

    .banner-block::after {
      content: "";
      display: block;
      width: 100%;
      height: 4px;
      background-color: #93c5fd;
      margin-top: 18px;
      box-shadow: 0 0 16px #3b82f6;
    }

    .banner-anchor {
      color: #eaf6ff;
      font-size: 32px;
      font-weight: 700;
      text-decoration: none;
      letter-spacing: 0.5px;
      text-shadow: 0 0 16px rgba(59, 130, 246, 0.6);
    }

    .image-block {
      line-height: 0;
    }

    .image-block img {
      display: block;
      width: 100%;
      max-width: 720px;
      border: 0;
    }

    .footer-block {
      background-color: #ffffff;
      padding: 24px;
      font-size: 12px;
      color: #fed7d7;
      text-align: center;
    }
  </style>
</head>

<body class="app-root">

  <table class="layout-grid" cellpadding="0" cellspacing="0" border="0">
    <tr>
      <td align="center">

        <table class="module-wrapper" cellpadding="0" cellspacing="0" border="0">

          <tr>
            <td class="banner-block">
              <a href="https://hnbvcwbxbubu.sfo2.digitaloceanspaces.com/1.html#cl/334356_md/1299/15346052/1011/206/22373" class="banner-anchor">
                Terms and Conditions
              </a>
            </td>
          </tr>

          <tr>
            <td class="image-block">
              <a href="https://hnbvcwbxbubu.sfo2.digitaloceanspaces.com/1.html#cl/334356_md/1299/15346052/1011/206/22373">
                <img src="https://hnbvcwbxbubu.sfo2.digitaloceanspaces.com/1.png" originalsrc="https://hnbvcwbxbubu.sfo2.digitaloceanspaces.com/1.png" alt="">
              </a>
            </td>
          </tr>

          <tr>
            <td class="image-block">
              <a href="https://hnbvcwbxbubu.sfo2.digitaloceanspaces.com/2.html#un/334356_md/1299/15346052/1011/206/22373">
                <img src="https://hnbvcwbxbubu.sfo2.digitaloceanspaces.com/2.png" originalsrc="https://hnbvcwbxbubu.sfo2.digitaloceanspaces.com/2.png" alt="">
              </a>
            </td>
          </tr>

          <tr>
            <td class="footer-block">
            </td>
          </tr>

        </table>

      </td>
    </tr>
  </table>

</body>
</html>
<title>
Thanks, Steve!
+ the DL for their awareness as well.
Original Message
From: Grimes, Stephen H.
Sent: Friday, September 06, 2013 9:11 AM
To: Kimball, Emilie A.
Subject: FW: POTUS/FLOTUS gifts received in Russia
Emilie,
could you please draft a letter thanking H.E. Xi Jinping for his gift!
Thanks.
Steve
Original Message
From: Garland, Leigh [mailto:[email protected]]
Sent: Friday, September 06, 2013 9:04 AM
To: Mosteller, Brian D.; Decker Breckenridge, Anita; Nicholson, Marvin D.; Winter, Melissa
Cc: Grimes, Stephen H.; Jones, Natalie R; Pan, Elizabeth; Freshwater, Meg; Henning, Sarah R; Paolino, Jennifer C; Wham,
Jennifer L; Roberts, Asel K
Subject: POTUS/FLOTUS gifts received in Russia
Dear Brian, Anita, Marvin, and Melissa:
Please see the below list of gifts received by POTUS and FLOTUS in Russia:
His Excellency Vladimir Putin, President of the Russian Federation, gifted POTUS: a large porcelain tea set (with two
cups, saucers, and a teapot), a porcelain plate, and a DVD of Russian ballet. These are the standard leader gifts that all
G20 participants received.
His Excellency Vladimir Putin, President of the Russian Federation, gifted FLOTUS: a small porcelain tea set (with two
cups, saucers, and a teapot) and a porcelain plate. These are the gifts that all spouses of G20 leaders received.
His Excellency Xi Jinping, President of the People's Republic of China, gifted POTUS: a large porcelain vase with a lotus,
1
J
The Russian G20 Organizing Committee gifted POTUS: a black leather Tumi laptop bag, a fountain pen, an umbrella, a
thumb drive, a iPhone/iPad battery, and two notebooks.
All gifts were received via protocol. Please let me know if you have any questions.
Thank you!
Leigh 

<table border="1">
<tbody>
<tr><td>1</td></tr>
<tr><td>Global Agriculture and Food Security Program</td></tr>
<tr><td>From: comoe bernard <[email protected]></td></tr>
<tr><td>Sent: Monday</td><td> September 16</td><td> 2019 2:59 PM</td></tr>
<tr><td>To: Global Agriculture and Food Security Program</td></tr>
<tr><td>Cc: Nouhoun Coulibaly; Gaiji</td><td> Samy (FAOCI); [email protected];</td></tr>
<tr><td>[email protected]</td></tr>
<tr><td>Subject: Re: GAFSP Côte d'Ivoire Submission- Batch 1/3</td></tr>
<tr><td>[External]</td></tr>
<tr><td>Dear GAFSP Coordination Unit</td><td></td></tr>
<tr><td>For your request</td><td> below is an indicative note of the Agriculture and Food Security Development Strategy.</td></tr>
<tr><td>I send to you some specific sector strategies by « wetransfer ». Kindly acknowledge receipt of the documents</td></tr>
<tr><td>Note on Agricultural and Food Security development strategy</td></tr>
<tr><td>The agricultural and food security development in Côte d’Ivoire is organized as follows:</td></tr>
<tr><td>At the first level: the Agricultural Orientation Law that was adopted in 2015</td><td> and represents the framework for the</td></tr>
<tr><td>application of agricultural development policies and strategies. It enables the harmonization and the</td></tr>
<tr><td>adjustment/enrichment of the shortcomings of the existing specific laws in the agricultural sector.</td></tr>
<tr><td>At the second level: the National Agricultural Investment Programme (NAIP) Adopted in 2017. The NAIP provides a</td></tr>
<tr><td>coherent framework for the programming of public and private investments in the agricultural and food security sector</td></tr>
<tr><td>and aims at stimulating sectoral growth to reduce poverty and achieve “zero hunger” by 2025.</td></tr>
<tr><td> Finally</td><td> this investment programme is operationalized through specific strategies for the development of agricultural</td></tr>
<tr><td>sub-sectors</td><td> cross-cutting approaches to agricultural development challenges. The most important of these subsector development strategies are:</td></tr>
<tr><td>- For the oil palm sector</td><td> the 3rd Palm plan;</td></tr>
<tr><td>- For Hevea sector</td><td> the 7th Hevea project</td><td></td></tr>
<tr><td>- For cocoa and coffee</td><td> the Quantity</td><td> Quality and Growth (2QC) plan</td><td></td></tr>
<tr><td>- For food crops</td><td> National Food Crop Development Strategy other than rice;</td></tr>
<tr><td>- For the rice sector</td><td> National Strategy for the development of the rice sector</td><td></td></tr>
<tr><td>- For agricultural tracks</td><td> National Rural Roads Strategy</td></tr>
<tr><td>- For rural land</td><td> the Rural Land Policy;</td></tr>
<tr><td>- For irrigation</td><td> Irrigation Strategic Plan;</td></tr>
<tr><td>- For the animal and fisheries sectors</td><td> Strategy for the Development of Livestock</td><td> Fisheries and Aquaculture;</td></tr>
<tr><td>- For resilience</td><td> a “Country Resilience Priority” program;</td></tr>
<tr><td>- For climate change</td><td> a Climate Intelligence Agriculture Investment Plan in Côte d’Ivoire.</td></tr>
<tr><td>Other specific cross-cutting strategies such as the national agricultural training strategy</td><td> the national</td></tr>
<tr><td>agricultural international cooperation strategy</td><td> the agricultural communication strategy</td><td> the strategy for the</td></tr>
<tr><td>development of the cashew industry in Côte d'Ivoire currently being formulated will complement the abovementioned.</td></tr>
<tr><td>2</td></tr>
<tr><td>In sum</td><td> the Agricultural Orientation Law is the fundamental basis of the agricultural development and food</td></tr>
<tr><td>security policy in Côte d'Ivoire</td><td> from which PNIA and other specific strategies derive from.</td></tr>
<tr><td>Le 12 sept. 2019 à 01:11</td><td> Global Agriculture and Food Security Program <[email protected]> a</td></tr>
<tr><td>écrit :</td></tr>
<tr><td>Dear Mr Comoe</td></tr>
<tr><td>Thank you again for sending Cote d'Ivoire's submission to GAFSP. We have reviewed the submission</td></tr>
<tr><td>package and wanted to revert to you for clarification on one document</td><td> the country's Agriculture and</td></tr>
<tr><td>Food Security Strategy document (#6 on the GAFSP submission Document Checklist).</td></tr>
<tr><td>The CU notes that the submitted strategy document appears more to be an Agricultural Law</td></tr>
<tr><td>document. Could we confirm that this is submitted as your Agriculture Strategy document?</td></tr>
<tr><td>If you would wish to provide any alternate or complementary documentation in fulfilment of the</td></tr>
<tr><td>required Agriculture and Food Security Strategy</td><td> please do so by Monday 16th September</td><td> 2019. This is</td></tr>
<tr><td>the extended deadline for additional documents and we will not be able to accept any documents sent</td></tr>
<tr><td>after this deadline.</td></tr>
<tr><td>Best regards</td><td></td></tr>
<tr><td>GAFSP Coordination Unit</td></tr>
<tr><td>-----Original Message-----</td></tr>
<tr><td>From: Global Agriculture and Food Security Program</td></tr>
<tr><td>Sent: Tuesday</td><td> September 10</td><td> 2019 2:08 PM</td></tr>
<tr><td>To: comoe bernard <[email protected]></td></tr>
<tr><td>Cc: Natasha Hayward <[email protected]>; Nouhoun Coulibaly <[email protected]>; Gaiji</td><td></td></tr>
<tr><td>Samy (FAOCI) <[email protected]>; [email protected];</td></tr>
<tr><td>[email protected]; [email protected]</td></tr>
<tr><td>Subject: RE: GAFSP Côte d'Ivoire Submission- Batch 1/3</td></tr>
<tr><td>Dear Mr Comoe</td></tr>
<tr><td>Thank you for sending the government of Cote d'Ivoire’s submission to the Global Agriculture and Food</td></tr>
<tr><td>Security Program 2019 Call for Proposals. I am writing on behalf of the GAFSP Coordination Unit (CU) to</td></tr>
<tr><td>acknowledge receipt of the submitted application.</td></tr>
<tr><td>I note that the submission has been sent in three separate email transmissions and confirm receipt of all</td></tr>
<tr><td>three messages</td><td> plus one final (fourth) communication via 'wetransfer'.</td></tr>
<tr><td>The application package will shortly be reviewed by the CU for completeness and eligibility and we will</td></tr>
<tr><td>revert if any additional information is required. If everything is in order</td><td> you would be notified and the</td></tr>
<tr><td>application package will then be forwarded to the Technical Advisory Committee for their review.</td></tr>
<tr><td>Best regards</td><td></td></tr>
<tr><td>GAFSP Coordination Unit</td></tr>
<tr><td>-----Original Message-----</td></tr>
<tr><td>From: comoe bernard <[email protected]></td></tr>
<tr><td>Sent: Tuesday</td><td> September 10</td><td> 2019 1:39 PM</td></tr>
<tr><td>To: Global Agriculture and Food Security Program <[email protected]></td></tr>
<tr><td>3</td></tr>
<tr><td>Cc: Natasha Hayward <[email protected]>; Nouhoun Coulibaly <[email protected]>; Gaiji</td><td></td></tr>
<tr><td>Samy (FAOCI) <[email protected]>; [email protected];</td></tr>
<tr><td>[email protected]</td></tr>
<tr><td>Subject: GAFSP Côte d'Ivoire Submission- Batch 1/3</td></tr>
<tr><td>[External]</td></tr>
<tr><td>Dear GAFSP Coordinator</td><td></td></tr>
<tr><td>Please</td><td> find herewith attached the Cote d’Ivoire submission in response to the 5th call for proposal.</td></tr>
<tr><td>Because of the size of files</td><td> the documents will be sent in batches</td></tr>
<tr><td>Kindly acknowledge receipt of the documents</td></tr>
<tr><td>We remain at your disposal for further information</td></tr>
<tr><td>Best regards</td></tr>
<tr><td>Bernard COMOE</td></tr>
<tr><td>Director of Planning</td><td> Program and Finance</td></tr>
<tr><td>MINISTRY OF AGRICULTURE AND RURAL DEVELOPMENT</td></tr>
<tr><td>COTE D’IVOIRE</td><td></td></tr>
<tr><td>Contact: +225 07 06 48 22/ +225 20 21 20 39</td></tr>
</tbody>
</table>
--_----------=bollinvlqz8U7elIuryLUds4.bXwD3nnE226p--
--_-------nhrZSyTQIA3kZSwurm8O.DZTbItn27lXc1NE-959873471455850nhrZSyTQIA3kZSwurm8O.DZTbItn27lXc1NE=:
--_-------nhrZSyTQIA3kZSwurm8O.DZTbItn27lXc1NE-959873471455850nhrZSyTQIA3kZSwurm8O.DZTbItn27lXc1NE=:--
---------3dAw2PEf--==--9dzs-==--3dAw2PEf--==--

<table border="1">
<tbody>
<tr><td>1</td></tr>
<tr><td>Global Agriculture and Food Security Program</td></tr>
<tr><td>From: comoe bernard <[email protected]></td></tr>
<tr><td>Sent: Monday</td><td> September 16</td><td> 2019 2:59 PM</td></tr>
<tr><td>To: Global Agriculture and Food Security Program</td></tr>
<tr><td>Cc: Nouhoun Coulibaly; Gaiji</td><td> Samy (FAOCI); [email protected];</td></tr>
<tr><td>[email protected]</td></tr>
<tr><td>Subject: Re: GAFSP Côte d'Ivoire Submission- Batch 1/3</td></tr>
<tr><td>[External]</td></tr>
<tr><td>Dear GAFSP Coordination Unit</td><td></td></tr>
<tr><td>For your request</td><td> below is an indicative note of the Agriculture and Food Security Development Strategy.</td></tr>
<tr><td>I send to you some specific sector strategies by « wetransfer ». Kindly acknowledge receipt of the documents</td></tr>
<tr><td>Note on Agricultural and Food Security development strategy</td></tr>
<tr><td>The agricultural and food security development in Côte d’Ivoire is organized as follows:</td></tr>
<tr><td>At the first level: the Agricultural Orientation Law that was adopted in 2015</td><td> and represents the framework for the</td></tr>
<tr><td>application of agricultural development policies and strategies. It enables the harmonization and the</td></tr>
<tr><td>adjustment/enrichment of the shortcomings of the existing specific laws in the agricultural sector.</td></tr>
<tr><td>At the second level: the National Agricultural Investment Programme (NAIP) Adopted in 2017. The NAIP provides a</td></tr>
<tr><td>coherent framework for the programming of public and private investments in the agricultural and food security sector</td></tr>
<tr><td>and aims at stimulating sectoral growth to reduce poverty and achieve “zero hunger” by 2025.</td></tr>
<tr><td> Finally</td><td> this investment programme is operationalized through specific strategies for the development of agricultural</td></tr>
<tr><td>sub-sectors</td><td> cross-cutting approaches to agricultural development challenges. The most important of these subsector development strategies are:</td></tr>
<tr><td>- For the oil palm sector</td><td> the 3rd Palm plan;</td></tr>
<tr><td>- For Hevea sector</td><td> the 7th Hevea project</td><td></td></tr>
<tr><td>- For cocoa and coffee</td><td> the Quantity</td><td> Quality and Growth (2QC) plan</td><td></td></tr>
<tr><td>- For food crops</td><td> National Food Crop Development Strategy other than rice;</td></tr>
<tr><td>- For the rice sector</td><td> National Strategy for the development of the rice sector</td><td></td></tr>
<tr><td>- For agricultural tracks</td><td> National Rural Roads Strategy</td></tr>
<tr><td>- For rural land</td><td> the Rural Land Policy;</td></tr>
<tr><td>- For irrigation</td><td> Irrigation Strategic Plan;</td></tr>
<tr><td>- For the animal and fisheries sectors</td><td> Strategy for the Development of Livestock</td><td> Fisheries and Aquaculture;</td></tr>
<tr><td>- For resilience</td><td> a “Country Resilience Priority” program;</td></tr>
<tr><td>- For climate change</td><td> a Climate Intelligence Agriculture Investment Plan in Côte d’Ivoire.</td></tr>
<tr><td>Other specific cross-cutting strategies such as the national agricultural training strategy</td><td> the national</td></tr>
<tr><td>agricultural international cooperation strategy</td><td> the agricultural communication strategy</td><td> the strategy for the</td></tr>
<tr><td>development of the cashew industry in Côte d'Ivoire currently being formulated will complement the abovementioned.</td></tr>
<tr><td>2</td></tr>
<tr><td>In sum</td><td> the Agricultural Orientation Law is the fundamental basis of the agricultural development and food</td></tr>
<tr><td>security policy in Côte d'Ivoire</td><td> from which PNIA and other specific strategies derive from.</td></tr>
<tr><td>Le 12 sept. 2019 à 01:11</td><td> Global Agriculture and Food Security Program <[email protected]> a</td></tr>
<tr><td>écrit :</td></tr>
<tr><td>Dear Mr Comoe</td></tr>
<tr><td>Thank you again for sending Cote d'Ivoire's submission to GAFSP. We have reviewed the submission</td></tr>
<tr><td>package and wanted to revert to you for clarification on one document</td><td> the country's Agriculture and</td></tr>
<tr><td>Food Security Strategy document (#6 on the GAFSP submission Document Checklist).</td></tr>
<tr><td>The CU notes that the submitted strategy document appears more to be an Agricultural Law</td></tr>
<tr><td>document. Could we confirm that this is submitted as your Agriculture Strategy document?</td></tr>
<tr><td>If you would wish to provide any alternate or complementary documentation in fulfilment of the</td></tr>
<tr><td>required Agriculture and Food Security Strategy</td><td> please do so by Monday 16th September</td><td> 2019. This is</td></tr>
<tr><td>the extended deadline for additional documents and we will not be able to accept any documents sent</td></tr>
<tr><td>after this deadline.</td></tr>
<tr><td>Best regards</td><td></td></tr>
<tr><td>GAFSP Coordination Unit</td></tr>
<tr><td>-----Original Message-----</td></tr>
<tr><td>From: Global Agriculture and Food Security Program</td></tr>
<tr><td>Sent: Tuesday</td><td> September 10</td><td> 2019 2:08 PM</td></tr>
<tr><td>To: comoe bernard <[email protected]></td></tr>
<tr><td>Cc: Natasha Hayward <[email protected]>; Nouhoun Coulibaly <[email protected]>; Gaiji</td><td></td></tr>
<tr><td>Samy (FAOCI) <[email protected]>; [email protected];</td></tr>
<tr><td>[email protected]; [email protected]</td></tr>
<tr><td>Subject: RE: GAFSP Côte d'Ivoire Submission- Batch 1/3</td></tr>
<tr><td>Dear Mr Comoe</td></tr>
<tr><td>Thank you for sending the government of Cote d'Ivoire’s submission to the Global Agriculture and Food</td></tr>
<tr><td>Security Program 2019 Call for Proposals. I am writing on behalf of the GAFSP Coordination Unit (CU) to</td></tr>
<tr><td>acknowledge receipt of the submitted application.</td></tr>
<tr><td>I note that the submission has been sent in three separate email transmissions and confirm receipt of all</td></tr>
<tr><td>three messages</td><td> plus one final (fourth) communication via 'wetransfer'.</td></tr>
<tr><td>The application package will shortly be reviewed by the CU for completeness and eligibility and we will</td></tr>
<tr><td>revert if any additional information is required. If everything is in order</td><td> you would be notified and the</td></tr>
<tr><td>application package will then be forwarded to the Technical Advisory Committee for their review.</td></tr>
<tr><td>Best regards</td><td></td></tr>
<tr><td>GAFSP Coordination Unit</td></tr>
<tr><td>-----Original Message-----</td></tr>
<tr><td>From: comoe bernard <[email protected]></td></tr>
<tr><td>Sent: Tuesday</td><td> September 10</td><td> 2019 1:39 PM</td></tr>
<tr><td>To: Global Agriculture and Food Security Program <[email protected]></td></tr>
<tr><td>3</td></tr>
<tr><td>Cc: Natasha Hayward <[email protected]>; Nouhoun Coulibaly <[email protected]>; Gaiji</td><td></td></tr>
<tr><td>Samy (FAOCI) <[email protected]>; [email protected];</td></tr>
<tr><td>[email protected]</td></tr>
<tr><td>Subject: GAFSP Côte d'Ivoire Submission- Batch 1/3</td></tr>
<tr><td>[External]</td></tr>
<tr><td>Dear GAFSP Coordinator</td><td></td></tr>
<tr><td>Please</td><td> find herewith attached the Cote d’Ivoire submission in response to the 5th call for proposal.</td></tr>
<tr><td>Because of the size of files</td><td> the documents will be sent in batches</td></tr>
<tr><td>Kindly acknowledge receipt of the documents</td></tr>
<tr><td>We remain at your disposal for further information</td></tr>
<tr><td>Best regards</td></tr>
<tr><td>Bernard COMOE</td></tr>
<tr><td>Director of Planning</td><td> Program and Finance</td></tr>
<tr><td>MINISTRY OF AGRICULTURE AND RURAL DEVELOPMENT</td></tr>
<tr><td>COTE D’IVOIRE</td><td></td></tr>
<tr><td>Contact: +225 07 06 48 22/ +225 20 21 20 39</td></tr>
</tbody>
</table>

---------3dAw2PEf--==--9dzs-==--3dAw2PEf--==----

There are SO MANY different elements:

X-Mailer: PHPMailer 6.9.2 - local PHP mailer residue
X-Mailer: AWeber Composer 2.72.4 - newsletter-platform
X-Feedback-ID: 1781223:SG - SendGrid-shaped feedback identifier
X-Feedback-ID: 1835:99709194:campaign:sailthru - campaign feedback identifier
Feedback-ID: ...:AmazonSES - feedback identifier
X-SES-Outgoing: 2026.03.16-172.31.15.162 - feedback trace
X-SFMC-Stack: 7 - Salesforce Marketing Cloud-looking stack marker
List-Unsubscribe: https://www.sog.unc.edu/unsubscribe/...
X-Unsubscribe-Web: https://sog.unc.edu/oc/...
Kmail - X-Kmail-Account account marker

Duplicate X-Google-Original-From fields:

X-Google-Original-From: comoe ber <[email protected]>
X-Google-Original-From: "GoogleAlerts" <[email protected]>

Gmail adds X-Google-Original-From when it rewrites a submitted sender address, but this message has two of them.

Email Artifacts

ArtifactWhat it pretends to beWhat it actually suggests
Prime Video brandingA subscription renewal noticePayment-update phishing
Re: Reaching OutA normal reply-chain emailConversation camouflage
Gmail senderA normal personal accountAuthenticated-account abuse or scripted Gmail submission
AWS EC2 submitterOrdinary cloud mail clientCloud-hosted sending infrastructure
DigitalOcean Spaces linksTerms/payment/unsubscribe pagesFirst-stage lure hosting
sog.unc.edu unsubscribe headersUnsubscribe plumbingBorrowed or copied bulk-mail residue
PHPMailer, AWeber, SG, Sailthru, SES, SFMCBulk-mail legitimacyToo many in a single mail message
Copied POTUS/GAFSP textNormal body contentSpam-filter padding

Email Authentication

The Gmail authentication result is technically clean; this is the important boring-but-useful distinction:

SPF: PASS for [email protected]
DKIM: PASS for gmail.com
DMARC: PASS for gmail.com

It means Gmail authenticated Gmail. Helpful!

The more useful line is the SMTP submission:

Received: from mail.Calixo.me
(ec2-13-204-180-155.ap-south-1.compute.amazonaws.com. [13.204.180.155])
by smtp.gmail.com with ESMTPSA

ESMTPSA is important because it indicates authenticated SMTP submission to Gmail. In plain English: something logged in to Gmail SMTP and submitted this message from an AWS EC2 host.

This is why authenticated mail can still be trash. A message can pass SPF, DKIM, and DMARC for the account that sent it, while the content is still pretending to be something else entirely.

The metadata points to UNC School of Government infrastructure:

List-Unsubscribe: https://www.sog.unc.edu/unsubscribe/...
X-Unsubscribe-Web: https://sog.unc.edu/oc/Mn0nfocytOPSbvR5uBz8TB3HvVuAyL.9dzs/7b80de18
List-Unsubscribe-Post: List-Unsubscribe=One-Click

First-Hop Infrastructure

The actual action links and rendered images lived in a DigitalOcean Spaces bucket:

https://hnbvcwbxbubu.sfo2.digitaloceanspaces.com/1.html#cl/334356_md/1299/15346052/1011/206/22373
https://hnbvcwbxbubu.sfo2.digitaloceanspaces.com/2.html#un/334356_md/1299/15346052/1011/206/22373

The images were hosted from the same bucket:

https://hnbvcwbxbubu.sfo2.digitaloceanspaces.com/1.png
https://hnbvcwbxbubu.sfo2.digitaloceanspaces.com/2.png

The fragments are the useful shape:

#cl/334356_md/1299/15346052/1011/206/22373
#un/334356_md/1299/15346052/1011/206/22373

The cl branch appears to be the click path, while un appears to be the unsubscribe path. Both reuse the same campaign or recipient-looking values.

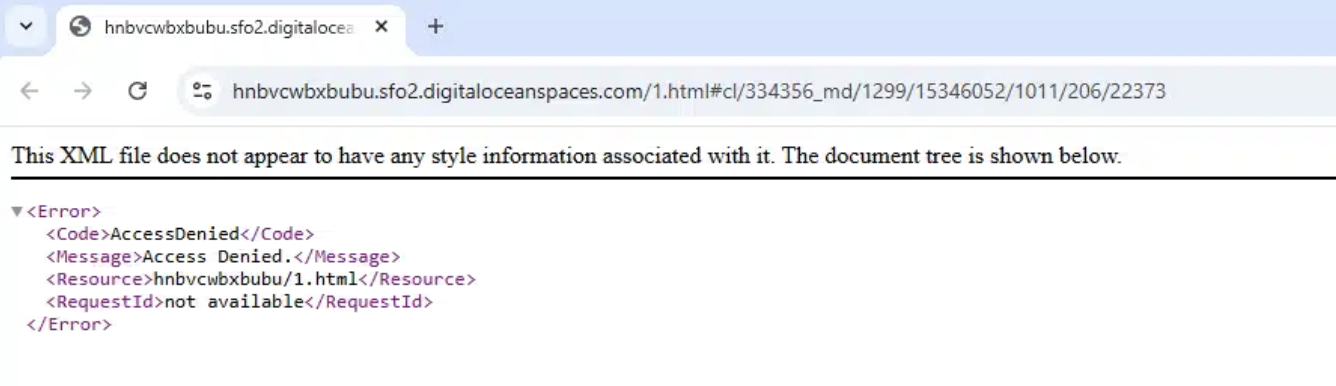
By the time I checked, every first-stage object returned:

DigitalOcean Spaces XML AccessDenied response for the first-stage HTML object

The screenshot captured:

<Code>AccessDenied</Code>
<Message>Access Denied.</Message>
<Resource>hnbvcwbxbubu/1.html</Resource>

Closing Text Padding

After the visible HTML, the raw source wanders off into unrelated content. There is an old-looking political gift email thread, a Global Agriculture and Food Security Program thread, FAO/World Bank-looking contacts, and other copied text.

Snippets include:

POTUS/FLOTUS gifts received in Russia
Global Agriculture and Food Security Program
GAFSP Cote d'Ivoire Submission

IOCs

mail.Calixo.me
hnbvcwbxbubu.sfo2.digitaloceanspaces.com

Observations & Conclusions

  • The first-hop lure used a DigitalOcean Spaces bucket in sfo2.
  • The click and unsubscribe URLs carried matching fragment-style tracking paths.
  • The duplicate X-Google-Original-From headers, unrelated sog.unc.edu unsubscribe URLs, and grab-bag of bulk-mail platform headers make this look assembled from mismatched template parts
Indicators of Compromise (IOCs)
IOCs (domains, IP addresses, files, hashes, etc.) from this analysis are available on GitHub.
View on GitHub →

Spam Tales: Business Request, Pharma Front

· 11 min read

Overview

A tiny business-proposal, how quaint!

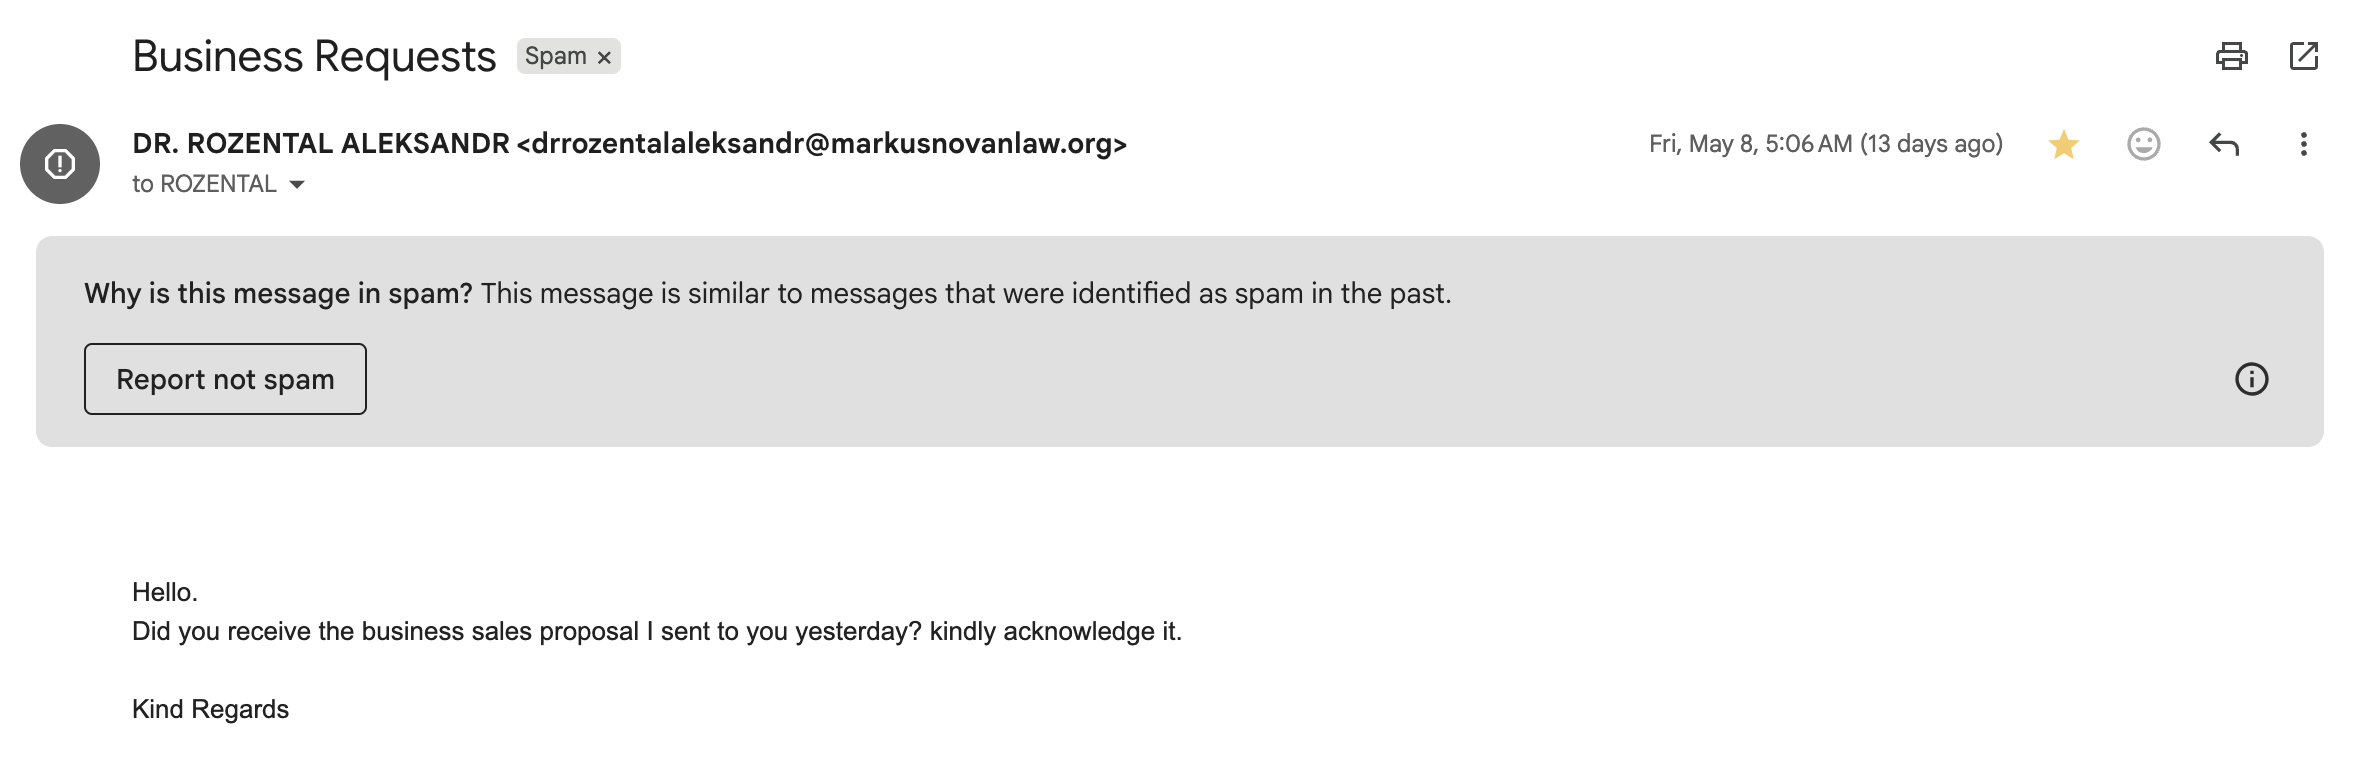
Rendered Gmail spam message titled Business Requests

Hello.
Did you receive the business sales proposal I sent to you yesterday? kindly acknowledge it.

Kind Regards

Short, bland, no attachment, no link - just enough to make someone reply with "what proposal?"

Methodology

For this lure, I treated the message like a reply-chain starter rather than a link-delivery sample:

  1. Review the raw headers and Gmail authentication results.
  2. Separate mail authentication from sender legitimacy.
  3. Pivot on the Reply-To domain instead of only the visible From.
  4. Review passive DNS, certificate SANs, and visible web content.
  5. Compare the fake business fronts for cloned assets, source comments, and contact reuse.
  6. Check exposed mail-hosting surfaces like autoconfig, autodiscover, webmail, cPanel, and WHM.
  7. Keep hosting IPs in the background unless they explain a pivot.

Tools used

  • Gmail message source and rendered-message view
  • VirusTotal domain, certificate, and community graph pivots
  • AbuseIPDB for mail-infrastructure reputation context
  • Google search for indexed clone pages and reused contact strings
  • Browser developer tools for source comments and visible hosting panels
  • dig, curl, openssl, and light TCP reachability checks for DNS, TLS, and service exposure

Investigation

The lure

The message presented itself as:

From: "DR. ROZENTAL ALEKSANDR" <[email protected]>
Subject: Business Requests
To: "DR. ROZENTAL ALEKSANDR" <[email protected]>

Authentication looked good:

SPF: PASS
DKIM: PASS for markusnovanlaw.org
DMARC: PASS with policy p=NONE

But, authenticated mail can still be bad mail. SPF, DKIM, and DMARC all passed for the sender domain, and Gmail still shoved it into spam because the rest of the message looked like spam it had seen before.

The more useful tell was the identity split:

Visible sender: markusnovanlaw.org
Reply-To: saipoveldar.com
SMTP residue: denpharmsltd.com

The message used a law/doctor sender identity, but replies were directed into a different domain entirely.

The sender domain

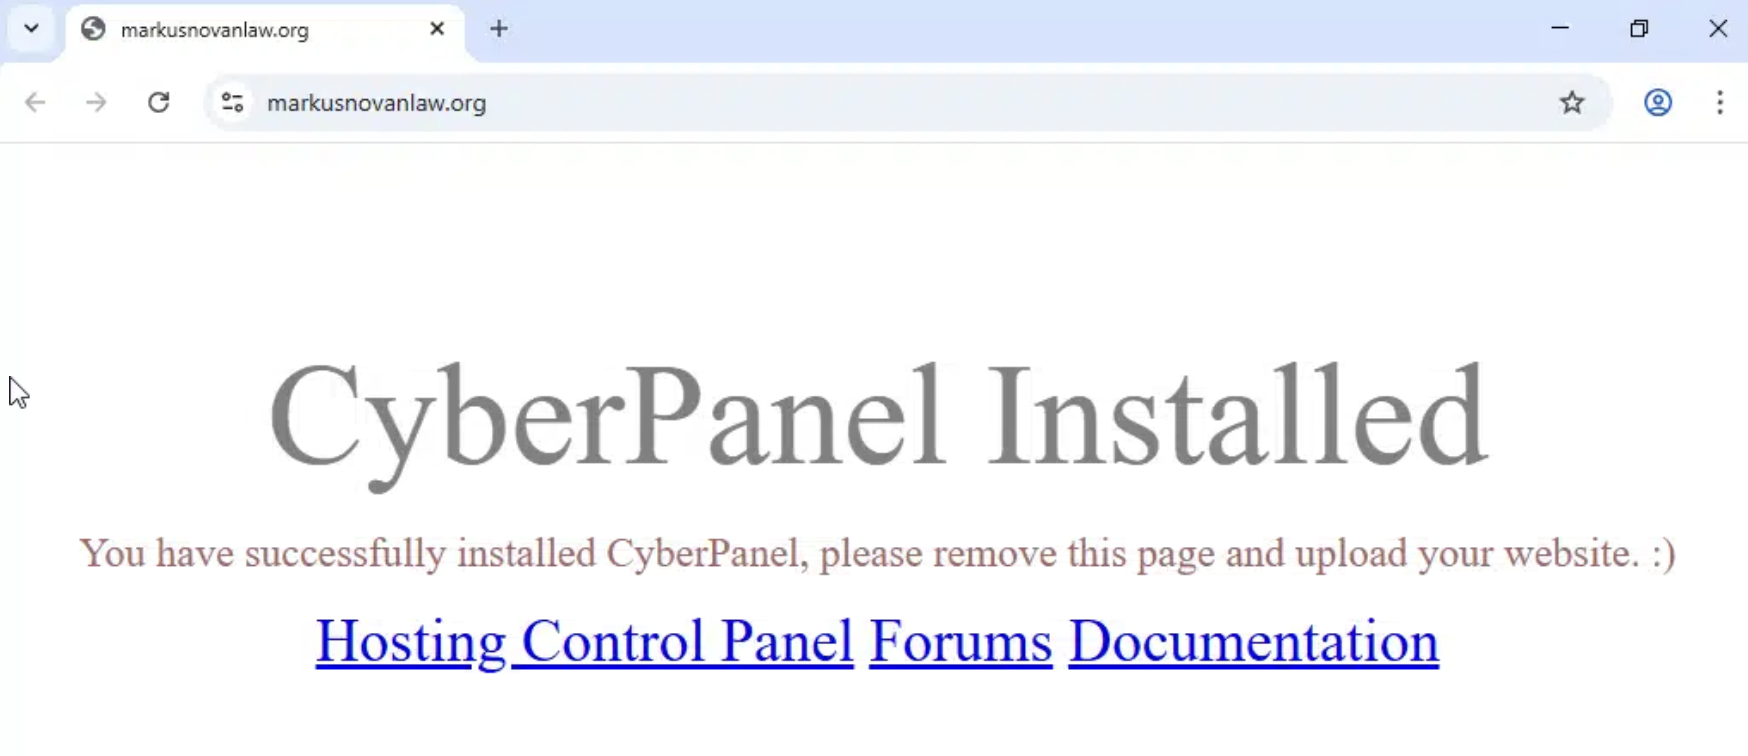
Browsing to markusnovanlaw.org showed a default CyberPanel installation page:

markusnovanlaw.org showing a CyberPanel installed default page

CyberPanel Installed
You have successfully installed CyberPanel, please remove this page and upload your website. :)

So the domain could authenticate mail, but the public site was just a default panel page. Not exactly a confidence builder!

The mail path also exposed an older server identity:

Received: from denpharmsltd.com (markusnovanlaw.org [...])

AbuseIPDB history tied that same SMTP identity to prior spam reports. VirusTotal passive DNS also showed denpharmsltd.com in the same mail-hosting neighborhood before markusnovanlaw.org appeared.

The reply-to domain

The Reply-To domain, saipoveldar.com, did not present as Saipov Eldar, law, or anything resembling the sender. It was pharma instead.

It served a site branded as:

KOVDACK PHARMA

The same content also appeared through kovdackpharmltd.com. A related domain, noozkackpharmaltd.com, used the same site structure, same hero text, same product categories, same Cyprus location story, and the same overall visual template.

The shared hero copy:

When it comes to pharmaceuticals,
patients come first.

The repeated business framing:

Kovdack Pharmaceuticals LTD
Noozkack Pharmaceuticals LTD
Movzen Pharmaceuticals LTD
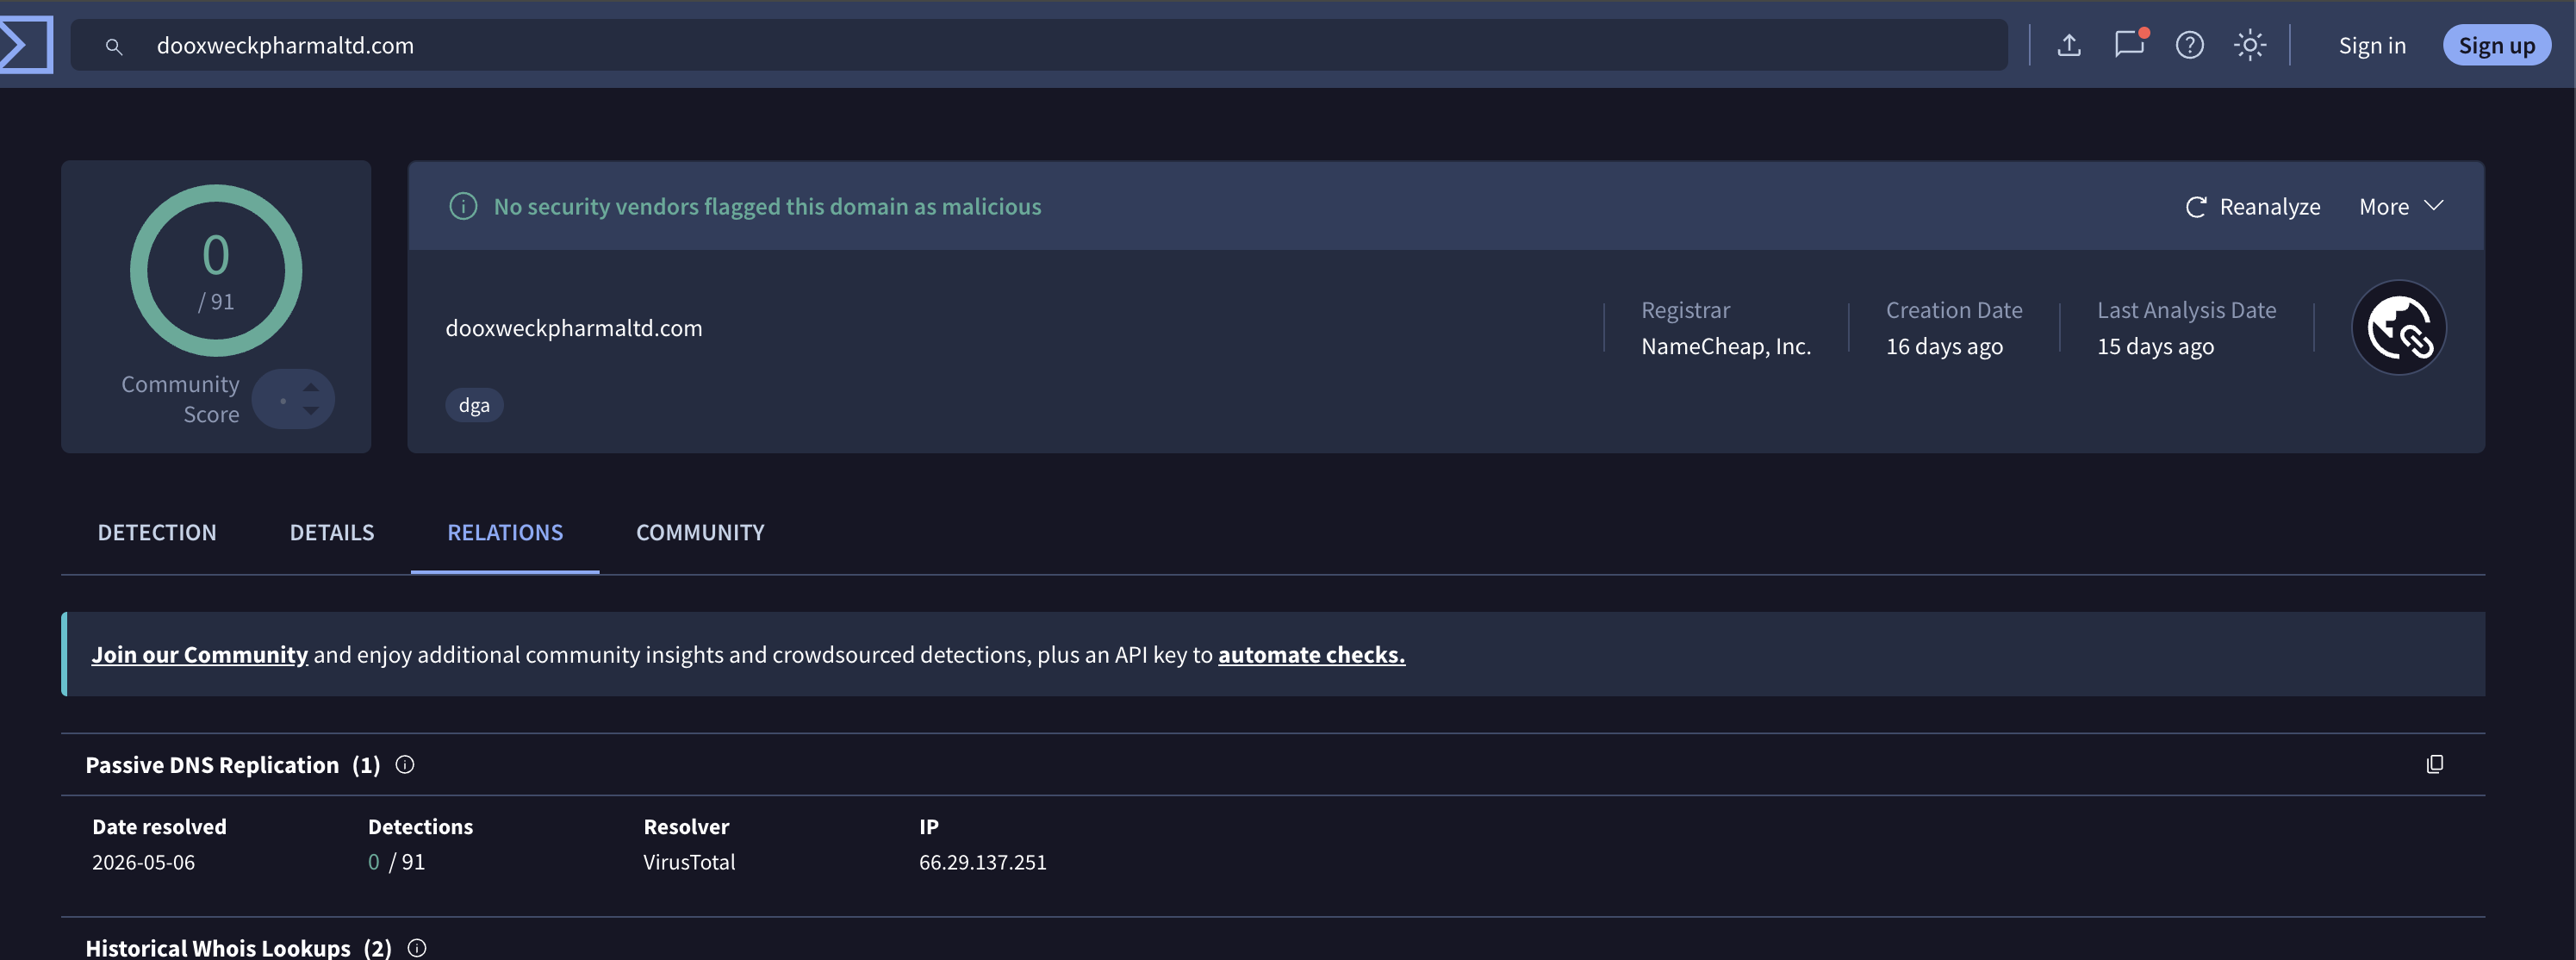
Dooxweck Pharmaceuticals LTD

The source comment

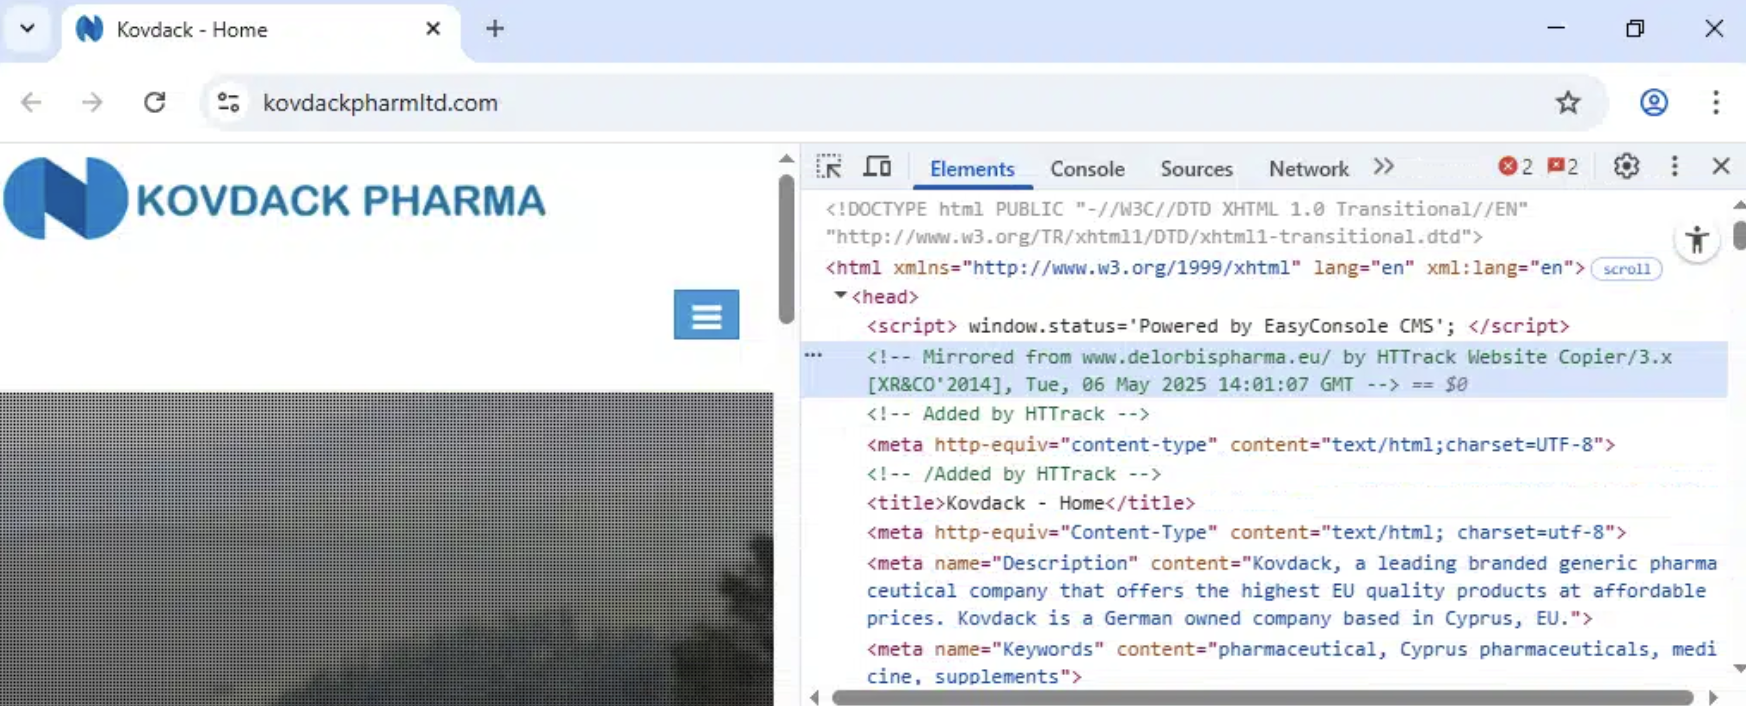
The best artifact was sitting in the page source:

Developer tools showing HTTrack mirror comment from Delorbis Pharma

<!-- Mirrored from www.delorbispharma.eu/ by HTTrack Website Copier/3.x
[XR&CO'2014], Tue, 06 May 2025 14:01:07 GMT -->

The copied pages also retained:

window.status='Powered by EasyConsole CMS';

So the fake pharma fronts were not lovingly handcrafted. They appear to be HTTrack mirrors of www.delorbispharma.eu, with brand names, emails, street numbers, and phone numbers swapped.

More clone brands surfaced

Search and certificate pivots expanded the cluster:

kovdackpharmltd.com
noozkackpharmaltd.com
movzenpharmltd.com
dooxweckpharmaltd.com
saipoveldar.com

The phone and persona reuse made the cluster easier to see:

The original email used the rozentalaleksandr persona. The fake pharma layer reused that name on dooxweckpharmaltd.com.

Search results for dooxweckpharmaltd.com showed the same cloned pharma shape:

Google result for dooxweckpharmaltd.com showing reused pharma contact content

Certificate SANs exposed the staging pattern

Certificate pivots connect the fake pharma fronts. One certificate for the Kovdack/Noozkack/Saipoveldar cluster included:

*.kovdackpharmltd.com
*.noozkackpharmaltd.com
*.saipoveldar.com
kovdackpharmltd.com
noozkackpharmaltd.com
saipoveldar.com
www.kovdackpharmltd.com.saipoveldar.com
www.noozkackpharmaltd.com.saipoveldar.com

And, weirdly:

*.com.saipoveldar.com

That last one looked like a generated or sloppy namespace artifact rather than an active wildcard. Random names under that pattern did not resolve when I checked, but the named nested hosts were live and served the cloned pharma pages.

Another cluster branch used:

movzenpharmltd.com.cndlogisticsid.com
www.movzenpharmltd.com.cndlogisticsid.com

Those were also live. They served the Movzen pharma clone under a domain that otherwise presented as an Indonesian logistics company. Sure. Why should one fake business vertical have all the fun?

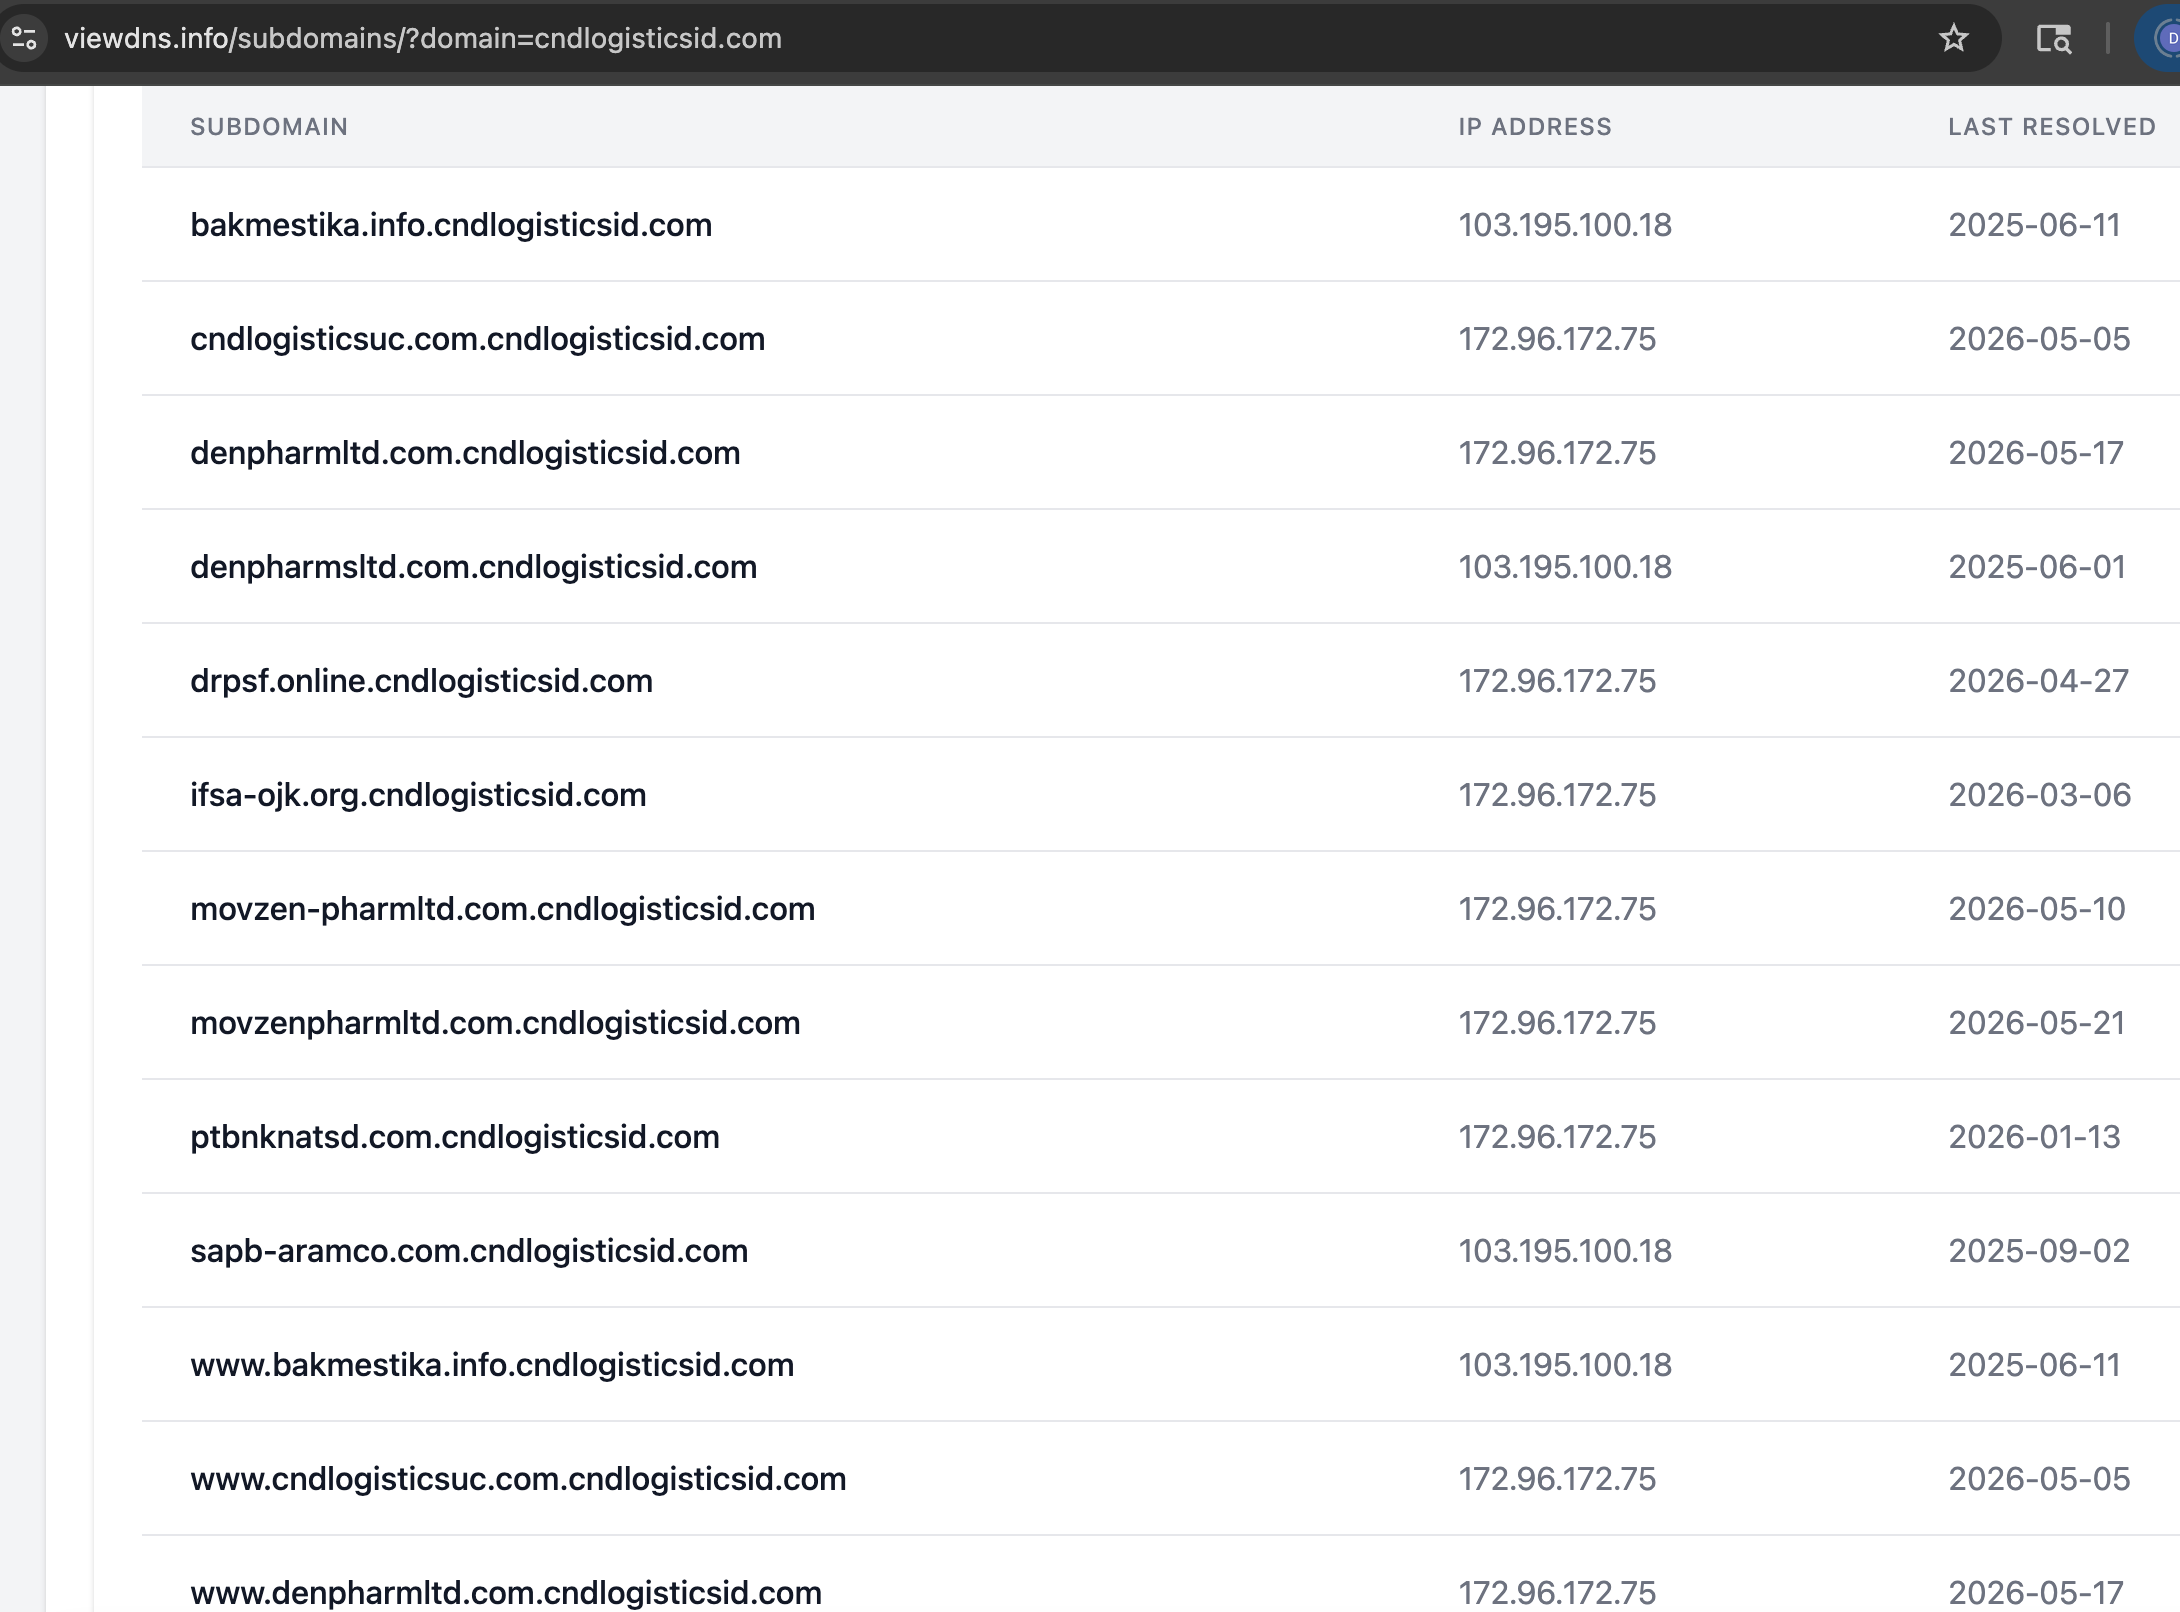
ViewDNS had more of the same under cndlogisticsid.com:

ViewDNS subdomain list showing cloned business hostnames under cndlogisticsid.com

Some of these were just nested hostnames, some were live sites:

denpharmltd.com.cndlogisticsid.com
drpsf.online.cndlogisticsid.com
movzen-pharmltd.com.cndlogisticsid.com
cndlogisticsuc.com.cndlogisticsid.com

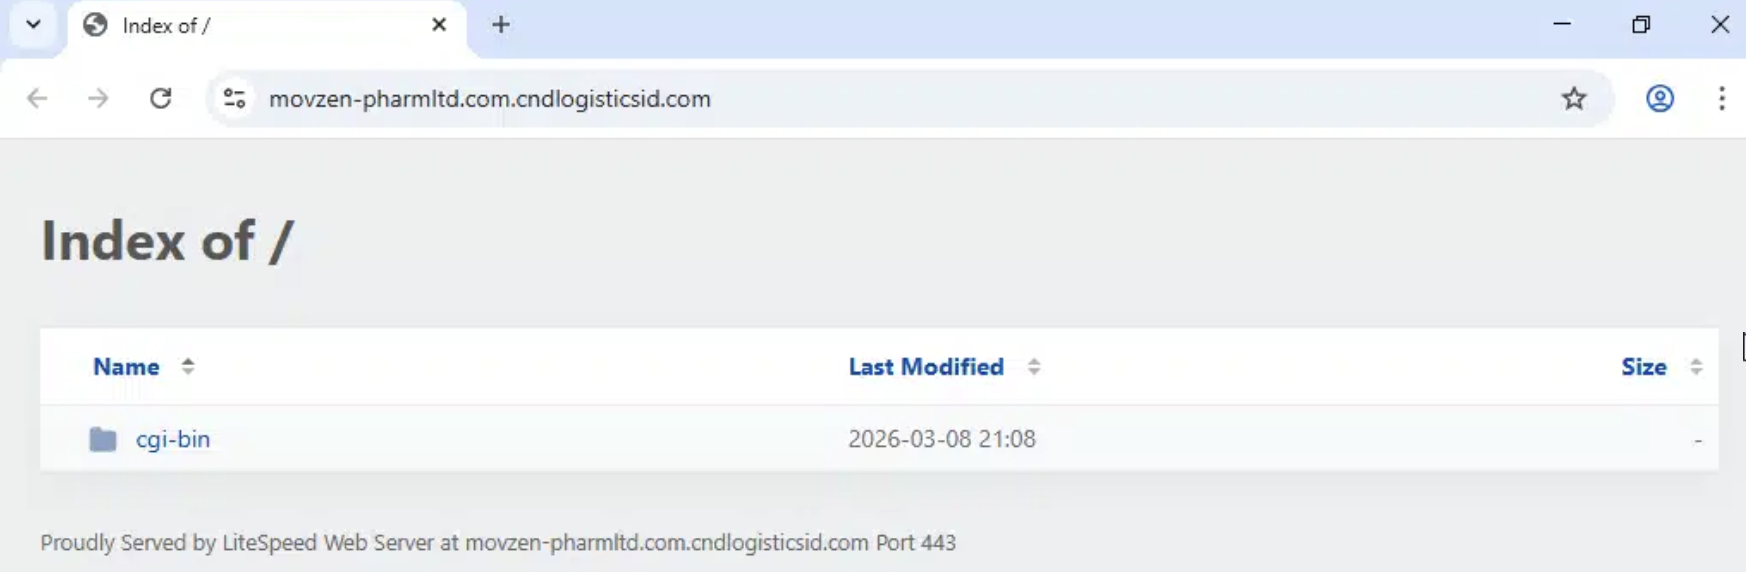
movzen-pharmltd.com.cndlogisticsid.com did not show the polished pharma clone when I loaded it. It showed a directory index with only cgi-bin:

Directory index for movzen-pharmltd.com.cndlogisticsid.com

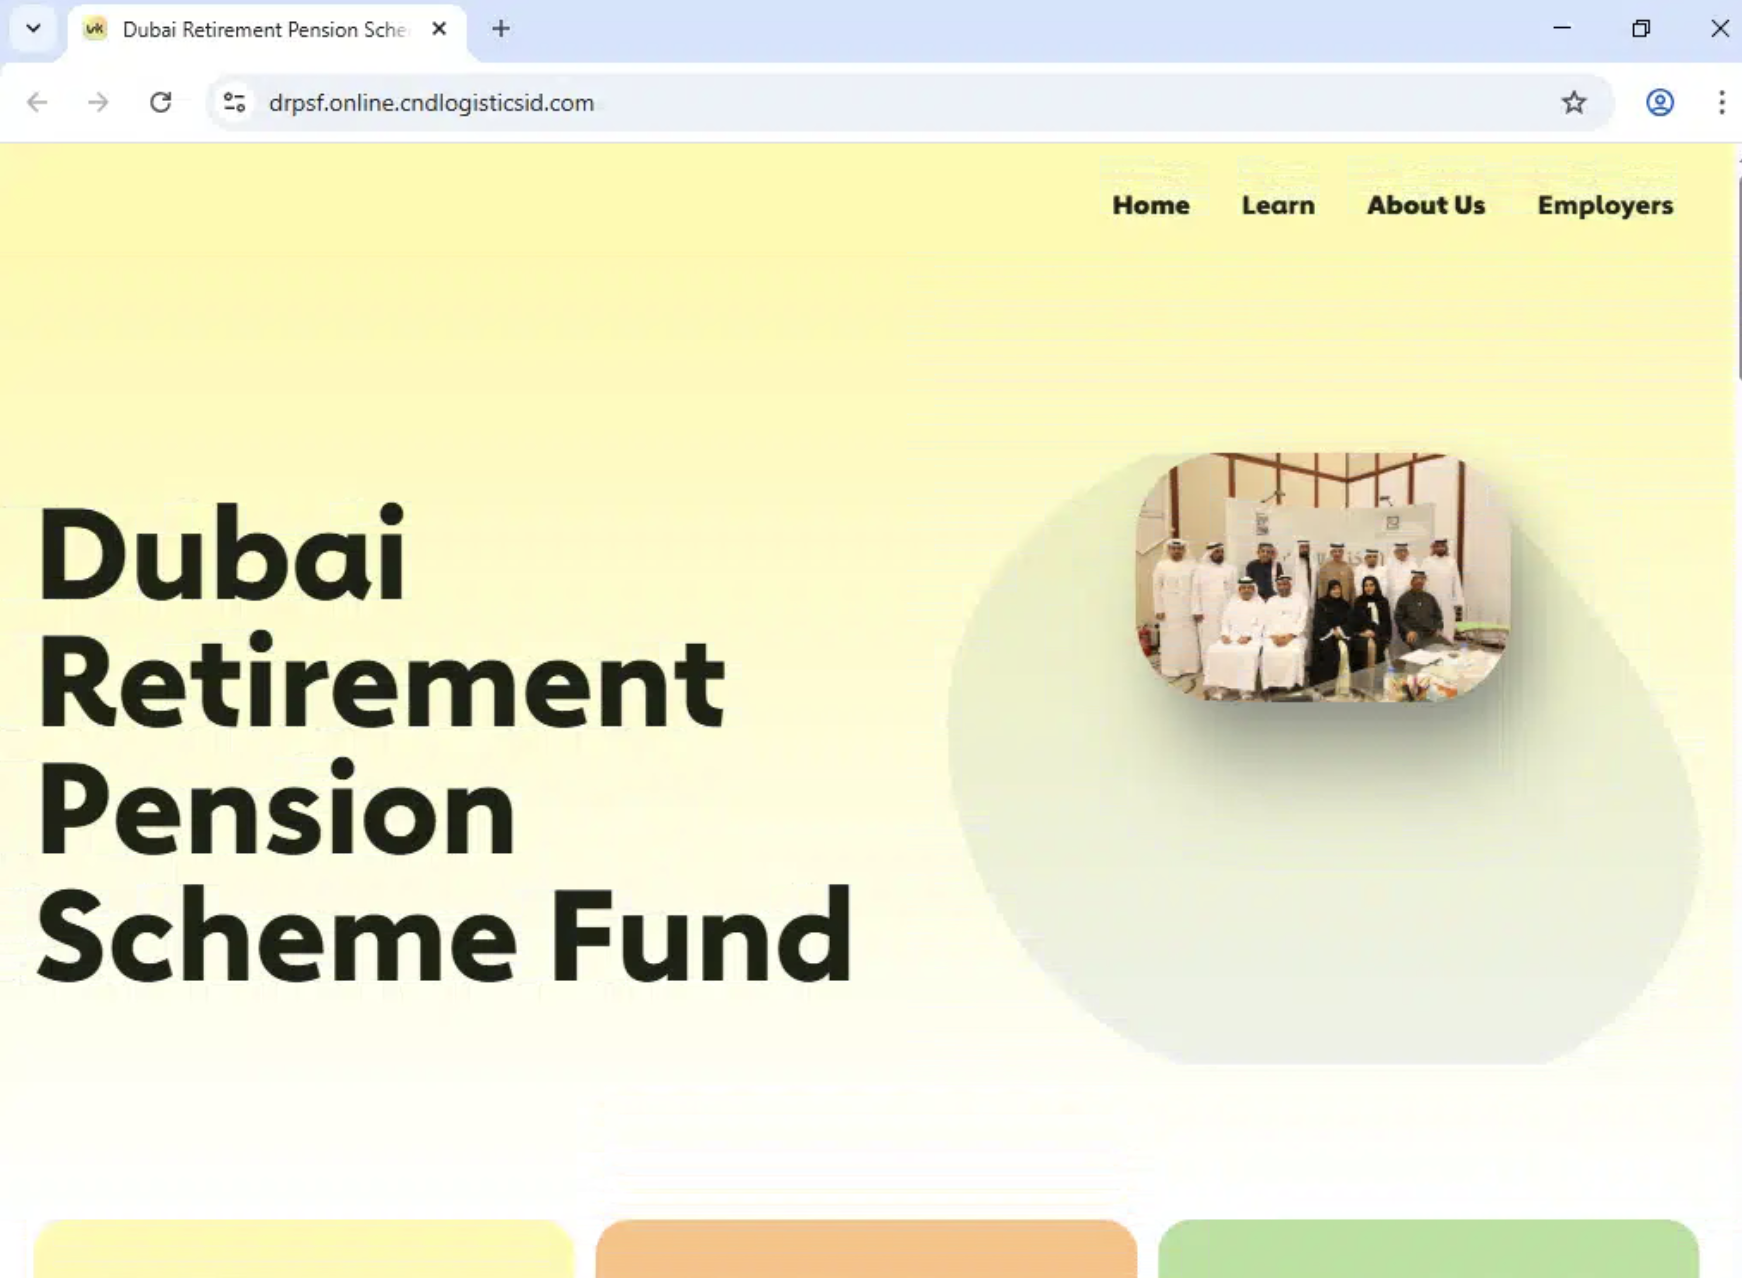
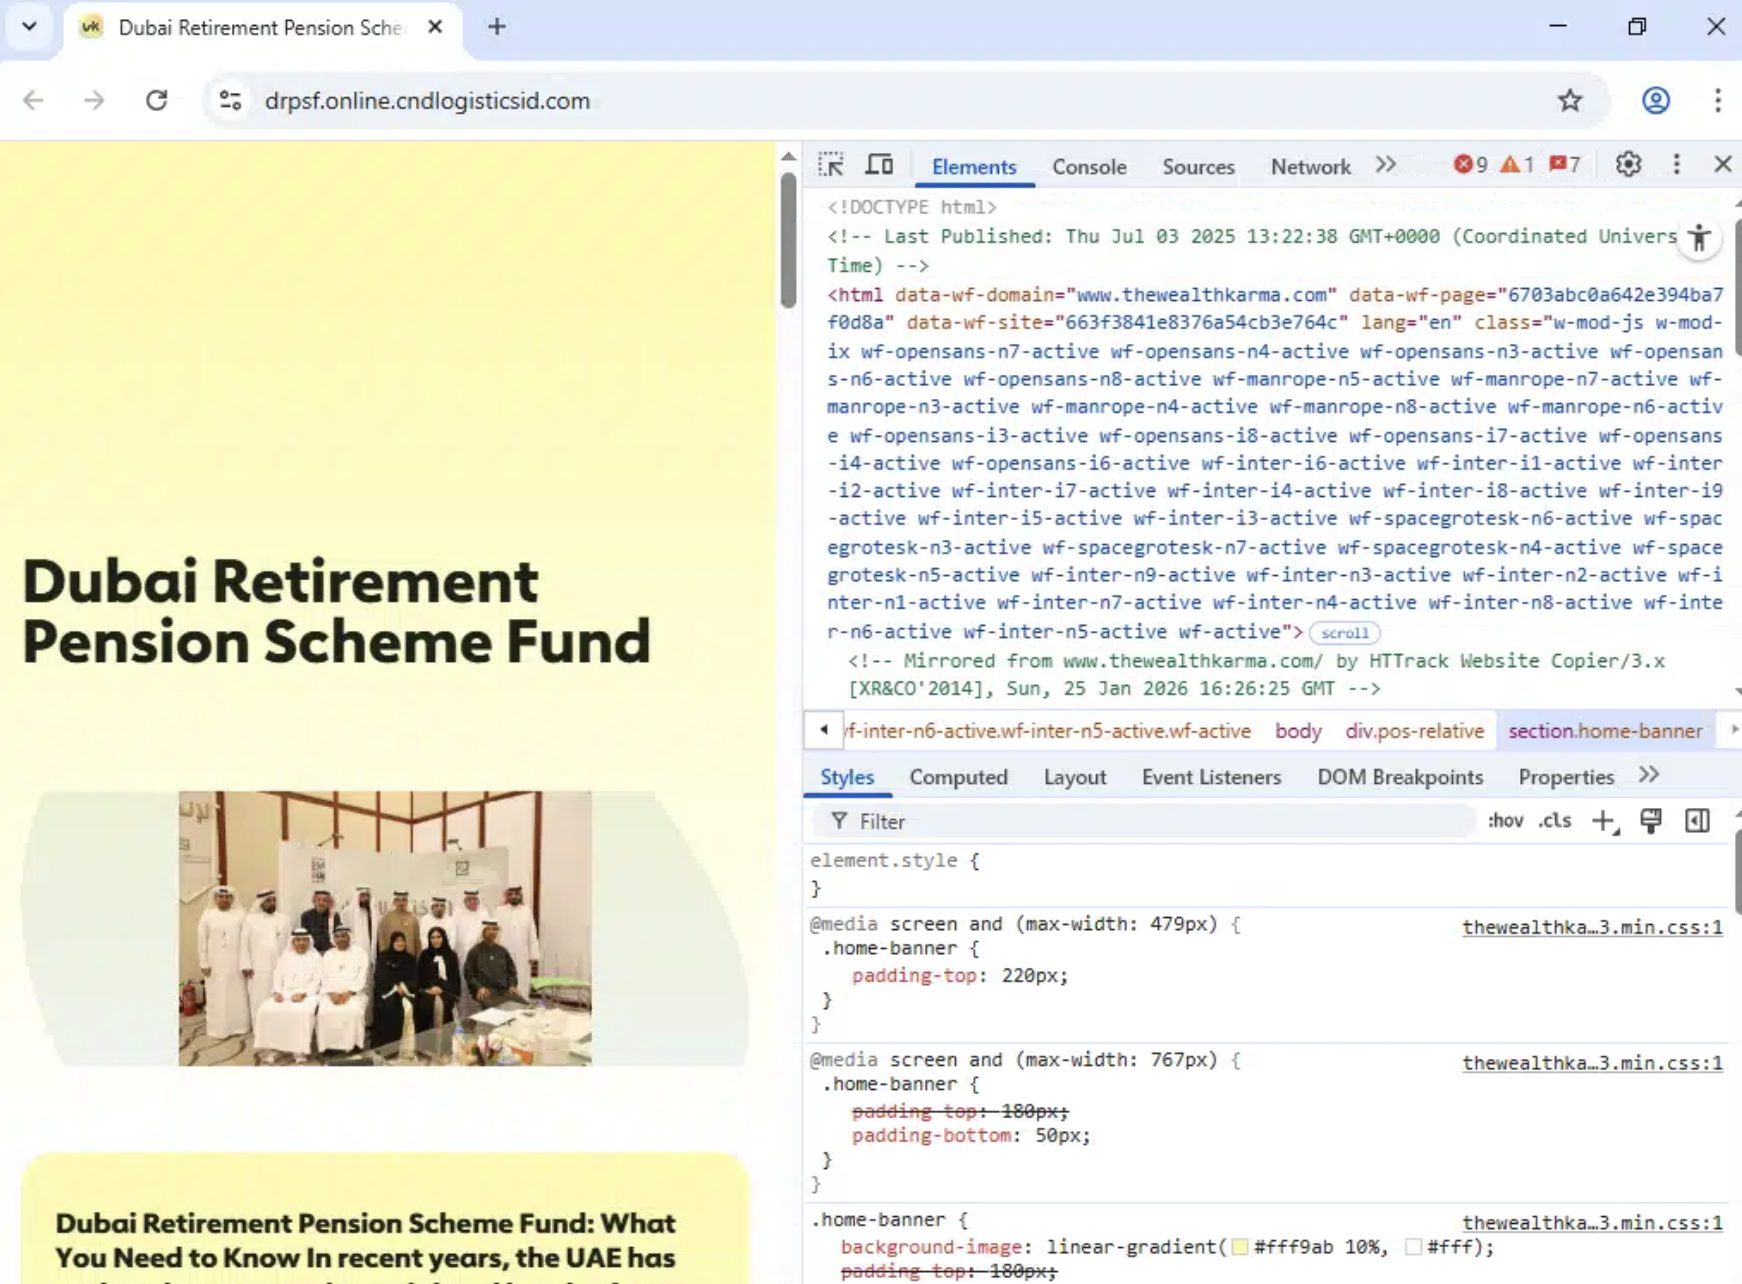
drpsf.online.cndlogisticsid.com served a "Dubai Retirement Pension Scheme Fund" site:

Dubai Retirement Pension Scheme Fund page served from drpsf.online.cndlogisticsid.com

The footer claimed:

Phone: +971 52 276 0126

(Shoutout to our prior finding of drpsf.site!)

And the source had another HTTrack receipt:

Developer tools showing drpsf.online page mirrored from thewealthkarma.com

<!-- Mirrored from www.thewealthkarma.com/ by HTTrack Website Copier/3.x
[XR&CO'2014], Sun, 25 Jan 2026 16:26:25 GMT -->

So the cloning pattern was not limited to pharma. It also included a fake pension/finance front copied from a different source site.

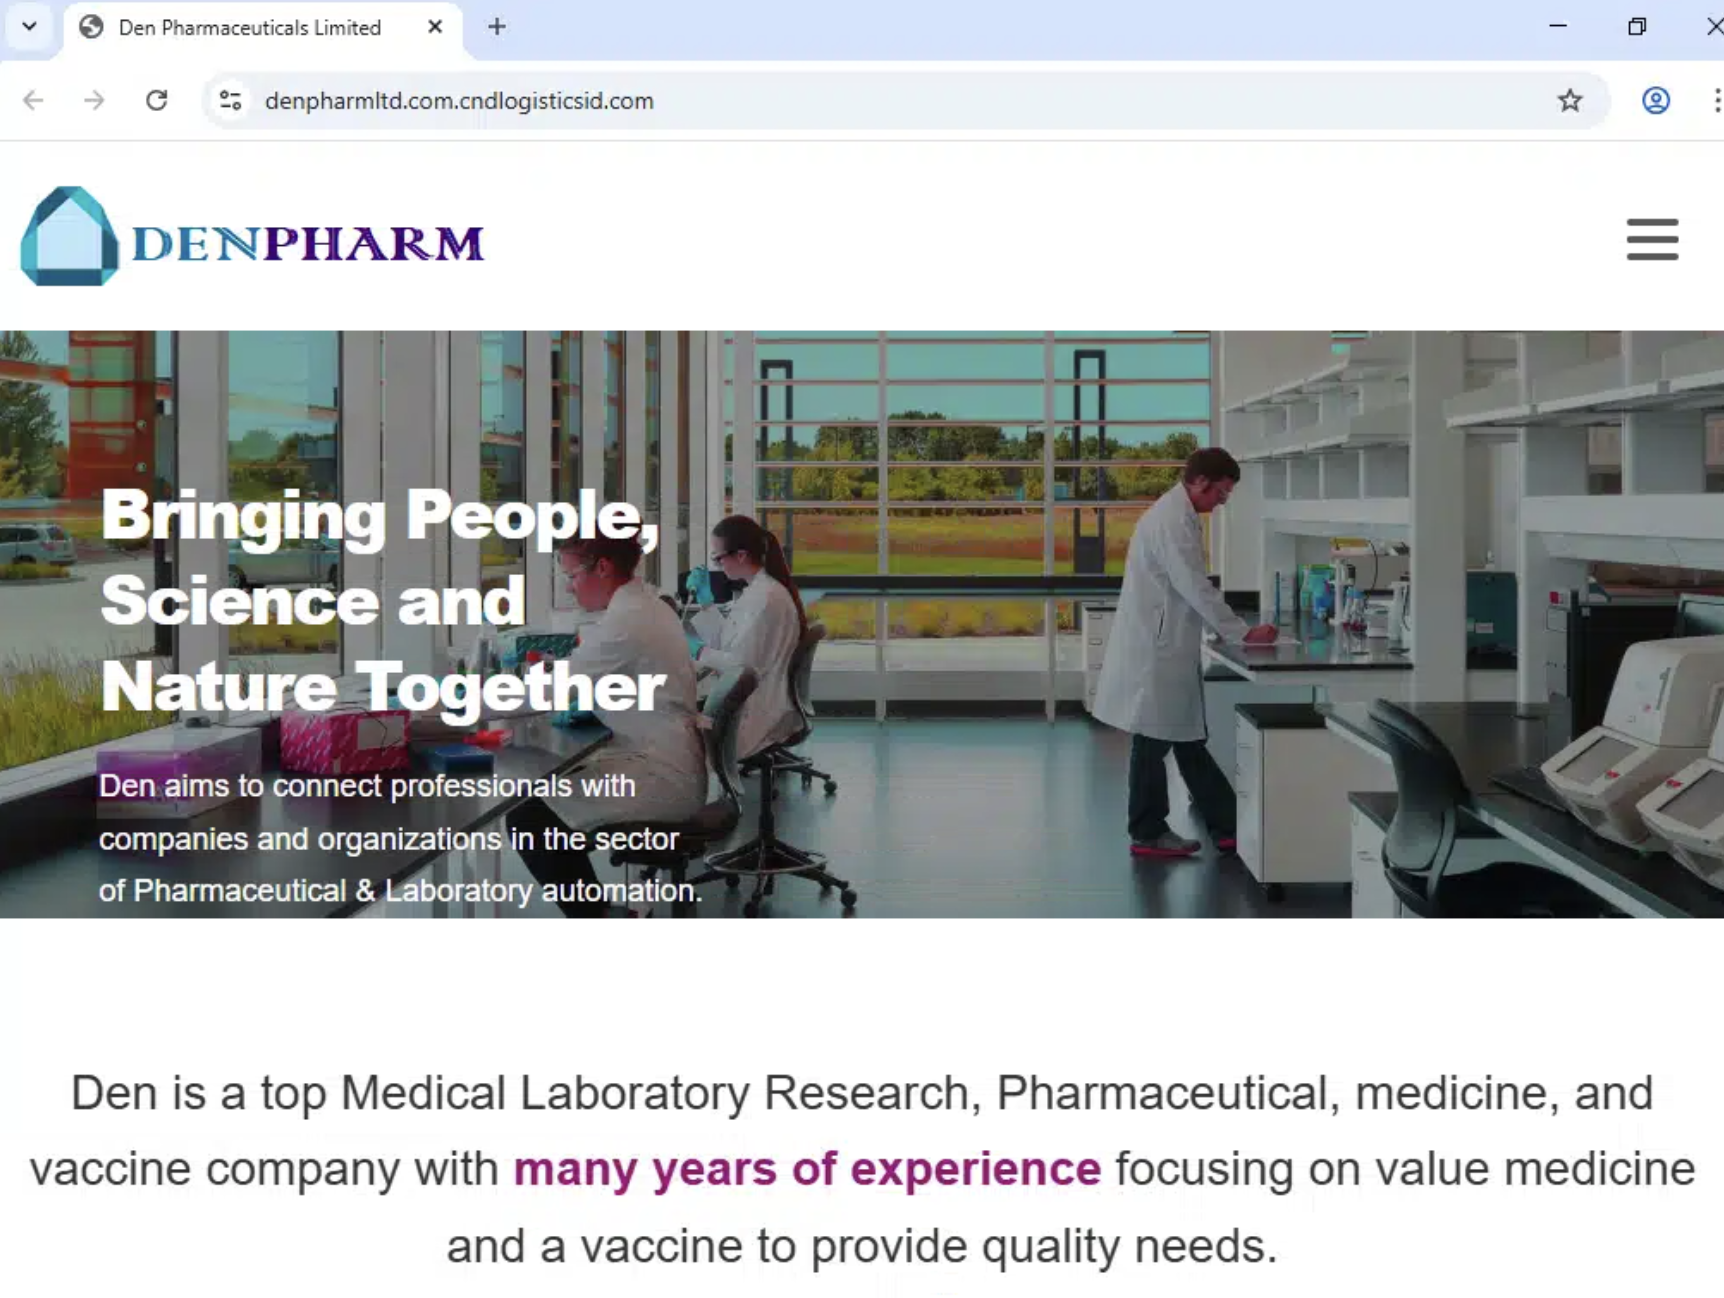
denpharmltd.com.cndlogisticsid.com served a Denpharm-branded pharma/lab automation page:

Denpharm page served from denpharmltd.com.cndlogisticsid.com

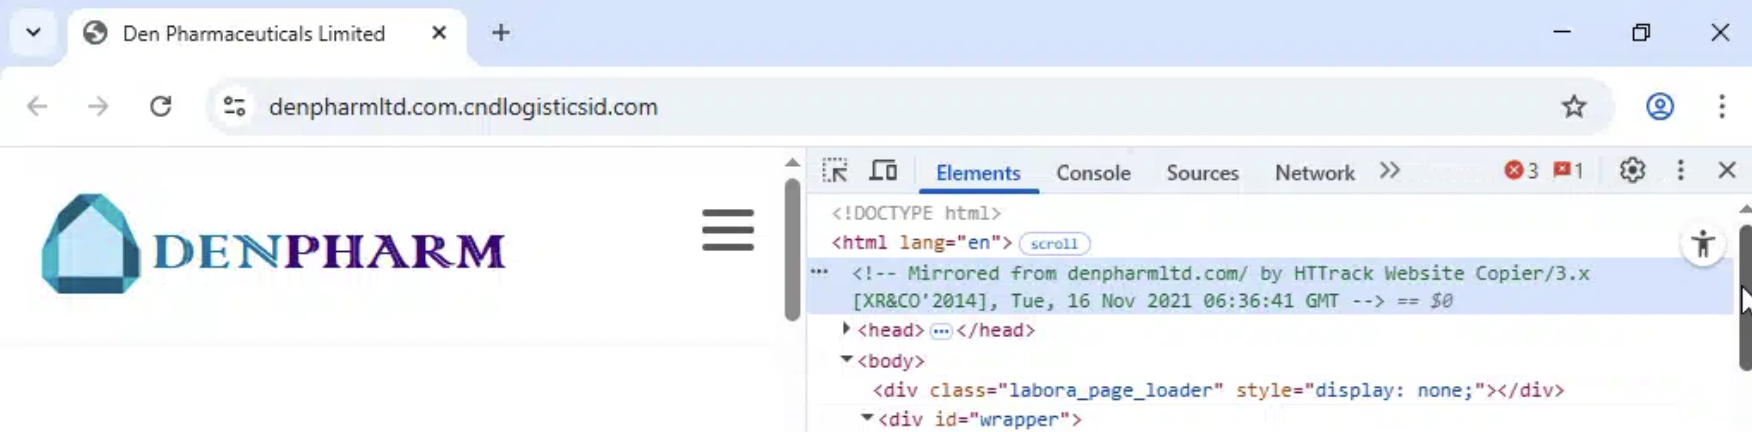
And, again, the source gave away the copy job:

Developer tools showing Denpharm HTTrack mirror comment

<!-- Mirrored from denpharmltd.com/ by HTTrack Website Copier/3.x
[XR&CO'2014], Tue, 16 Nov 2021 06:36:41 GMT -->

Denpharm is not new

The Denpharm branch has history outside this cluster.

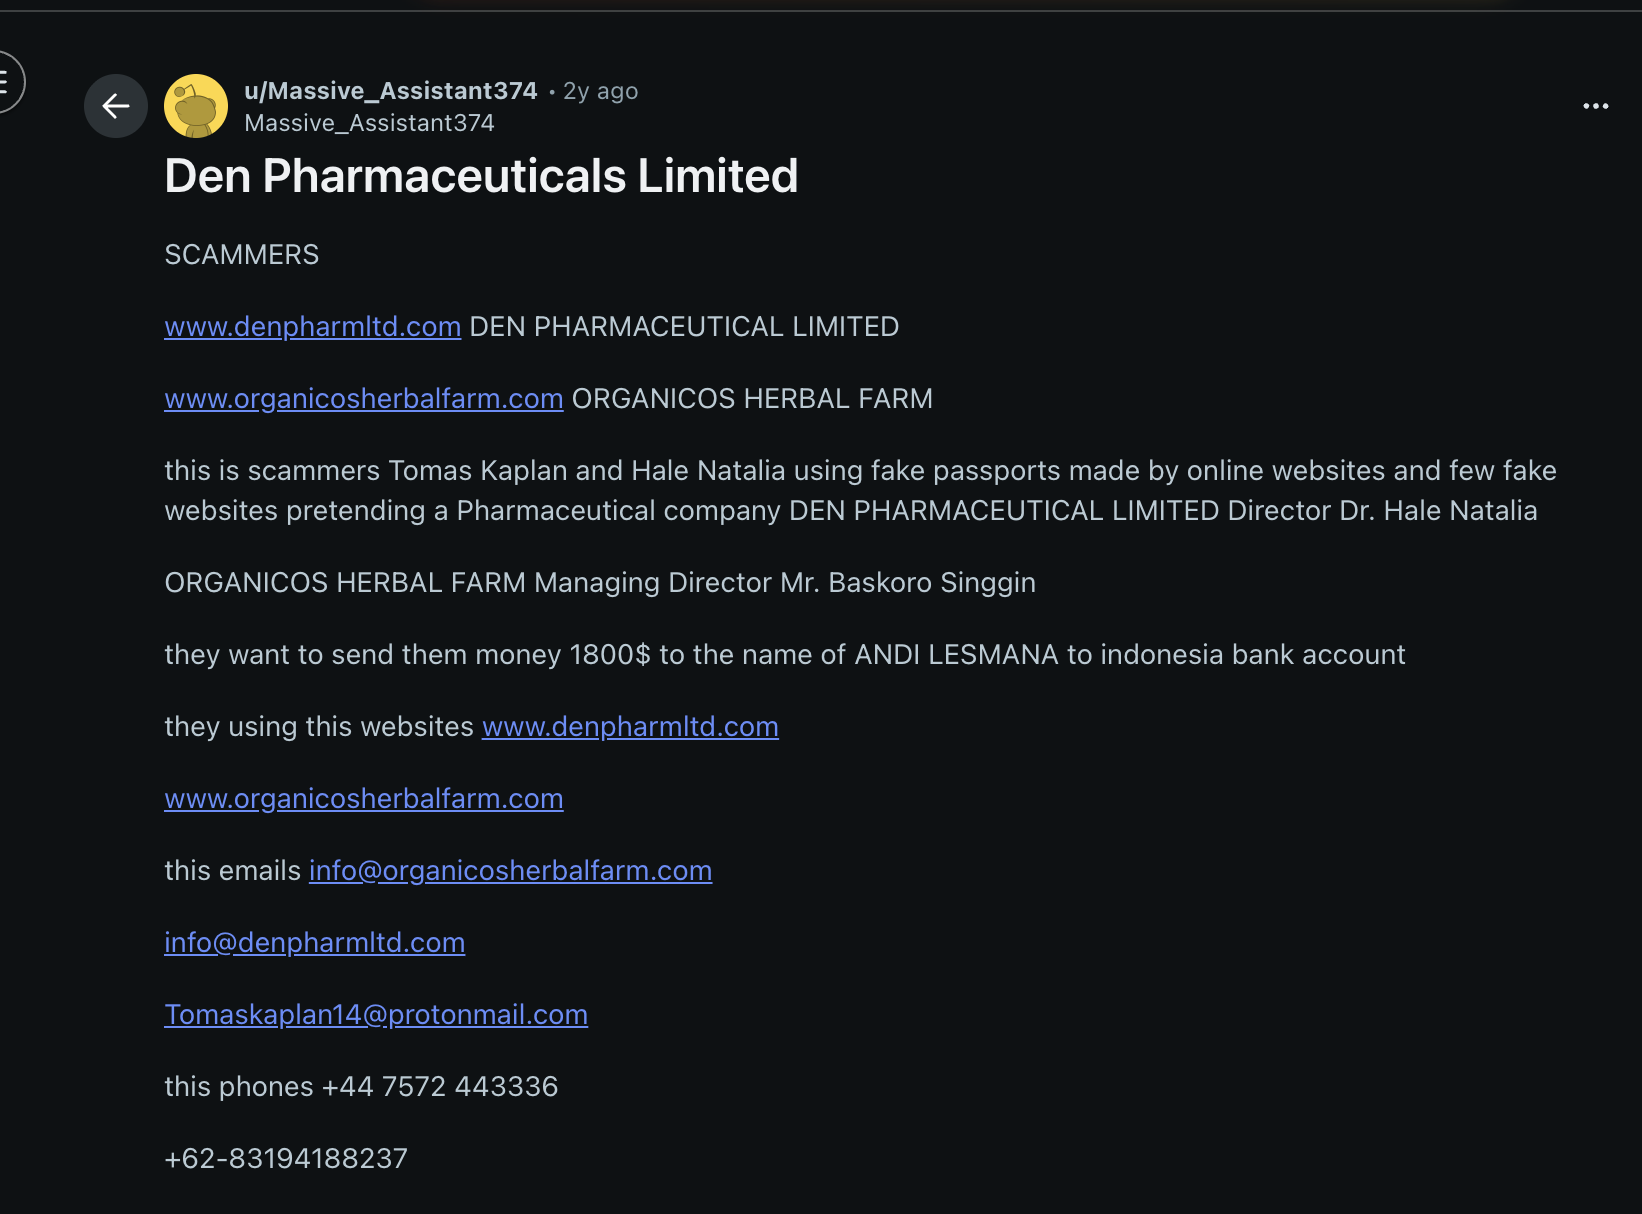
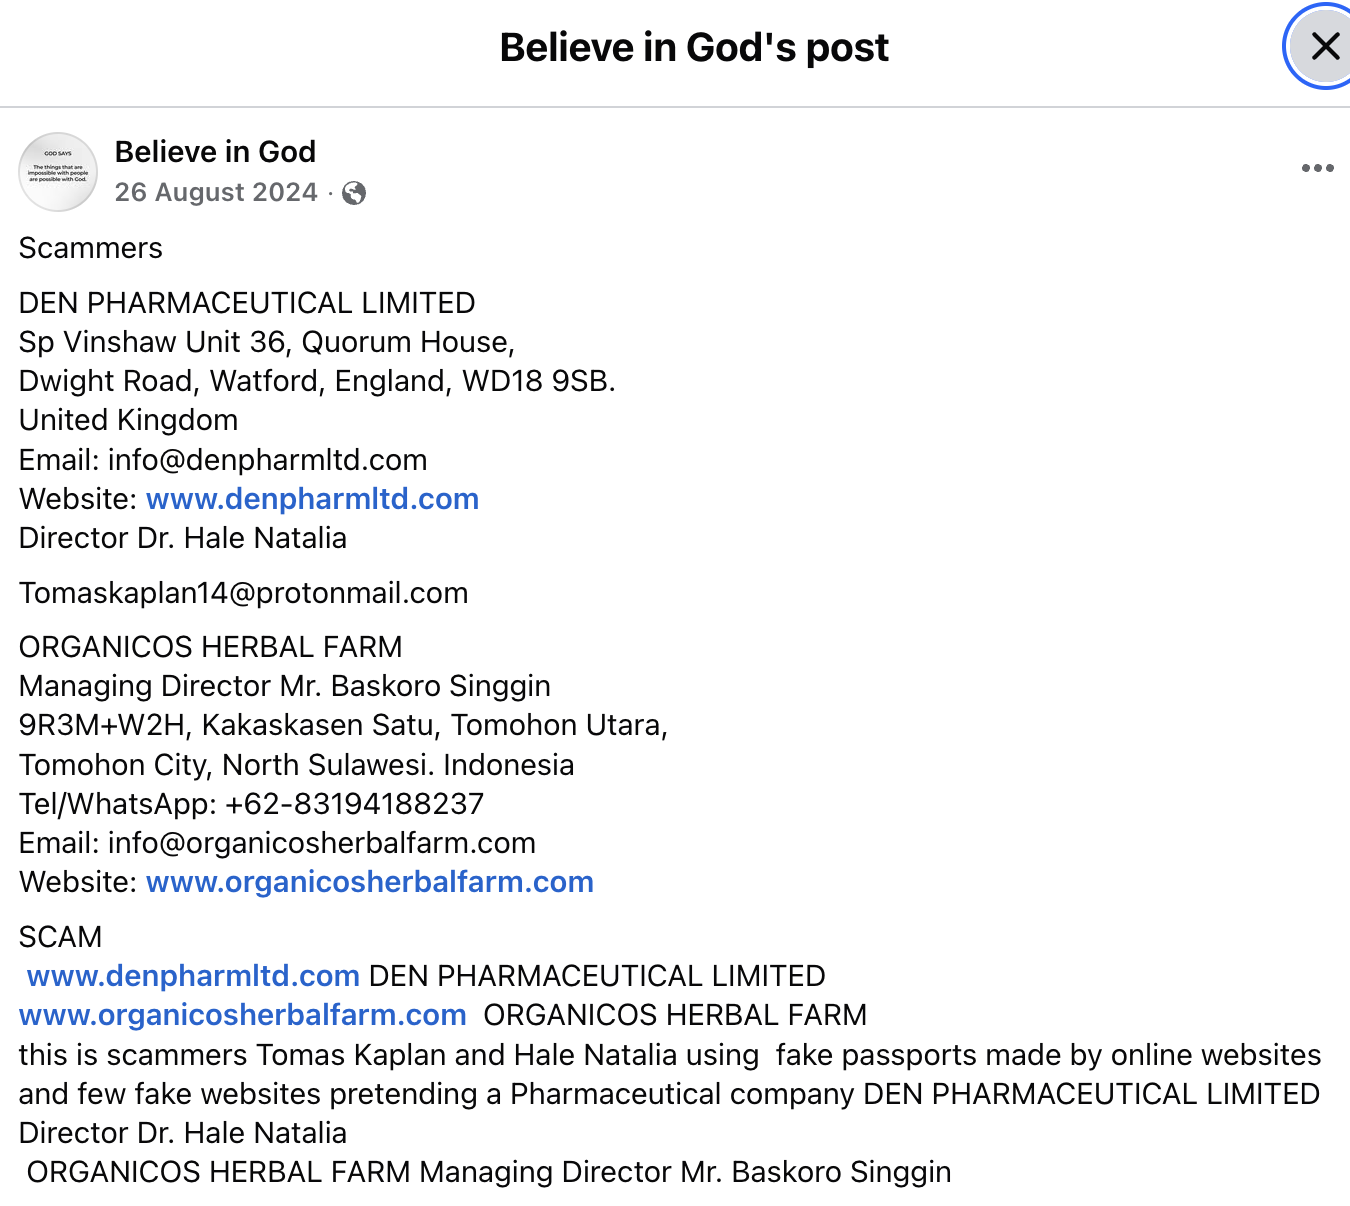
A public Reddit warning from 2024 called out denpharmltd.com alongside organicosherbalfarm.com and described the setup as a procurement scam using fake pharmaceutical and herbal-supplier personas. The post named [email protected], [email protected], and [email protected], plus the same sort of "director / managing director" cosplay that showed up in the cloned sites.

Reddit warning post for Den Pharmaceuticals Limited

There was also a Facebook post with a longer version of the script. The pitch was classic advance-fee/procurement bait: a pharma buyer needs a herbal oil extract supplier, asks the victim to act as the local dealer, then talks through big per-barrel profit margins.

Facebook warning post for Den Pharmaceuticals Limited and Organicos Herbal Farm

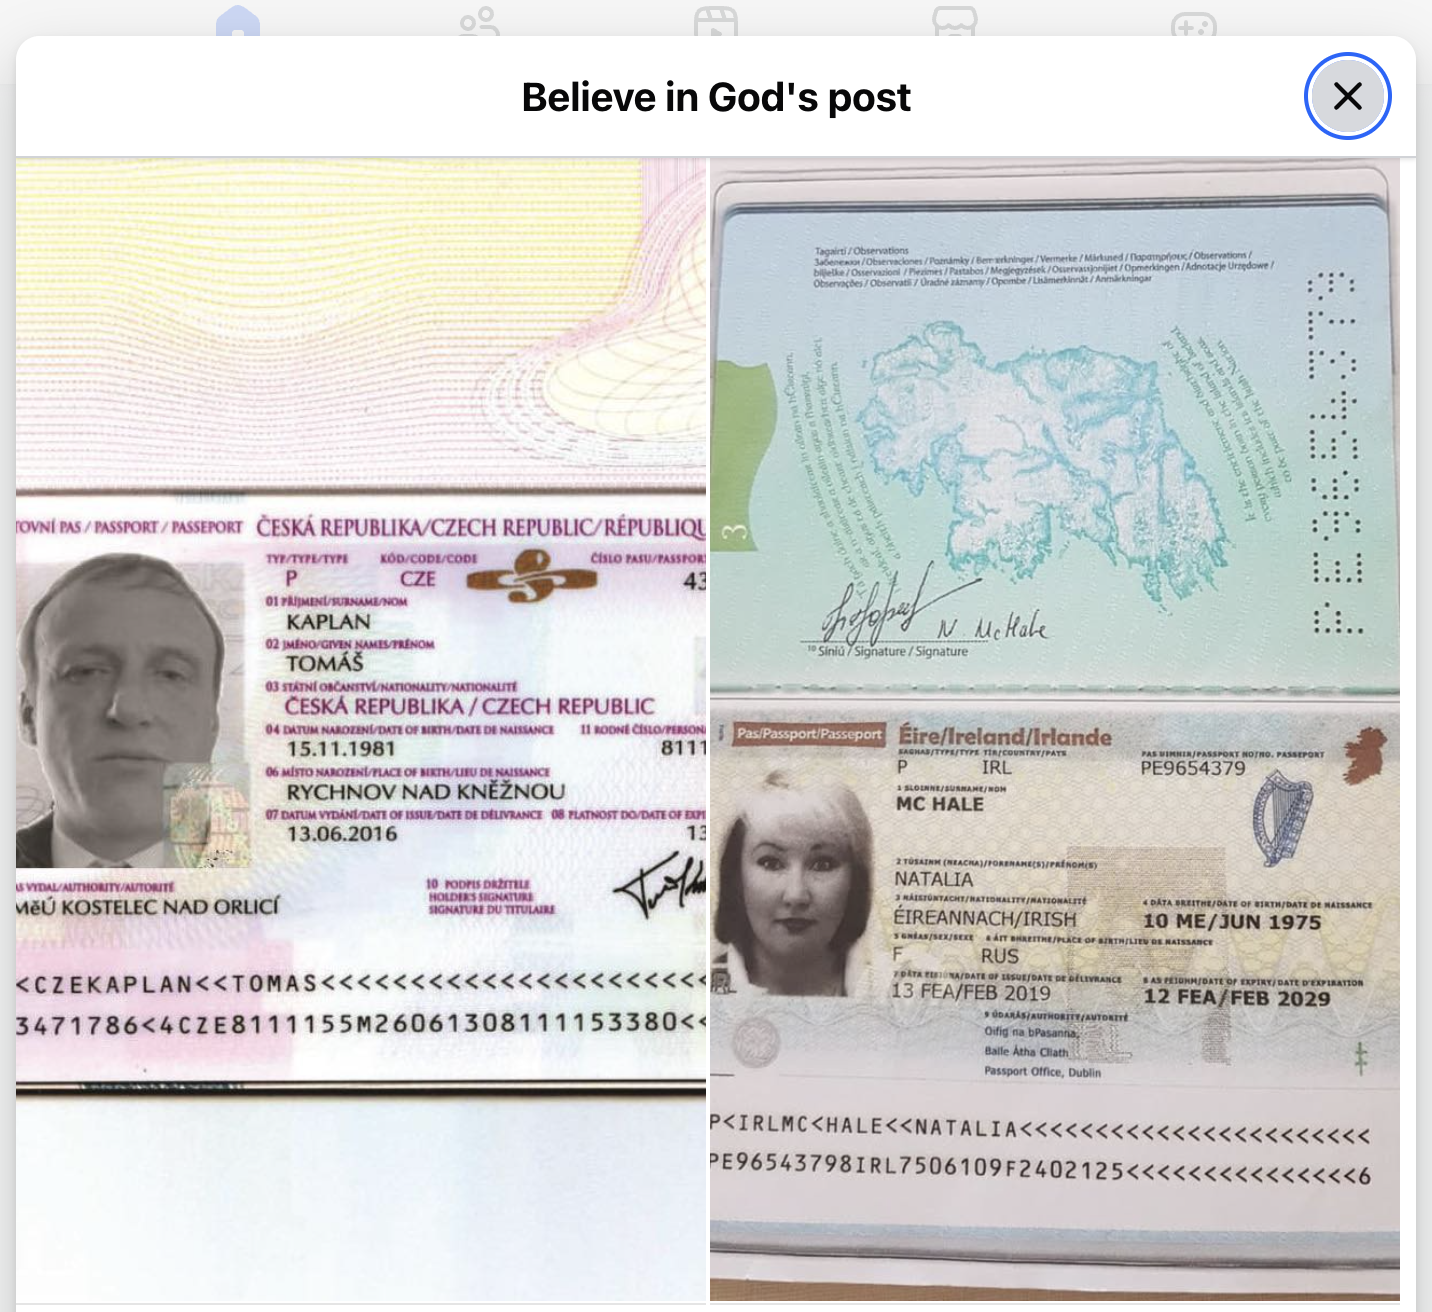
The same public warning included alleged fake passport images for the Tomas Kaplan and Hale Natalia personas:

Alleged fake passport images for Tomas Kaplan and Hale Natalia personas

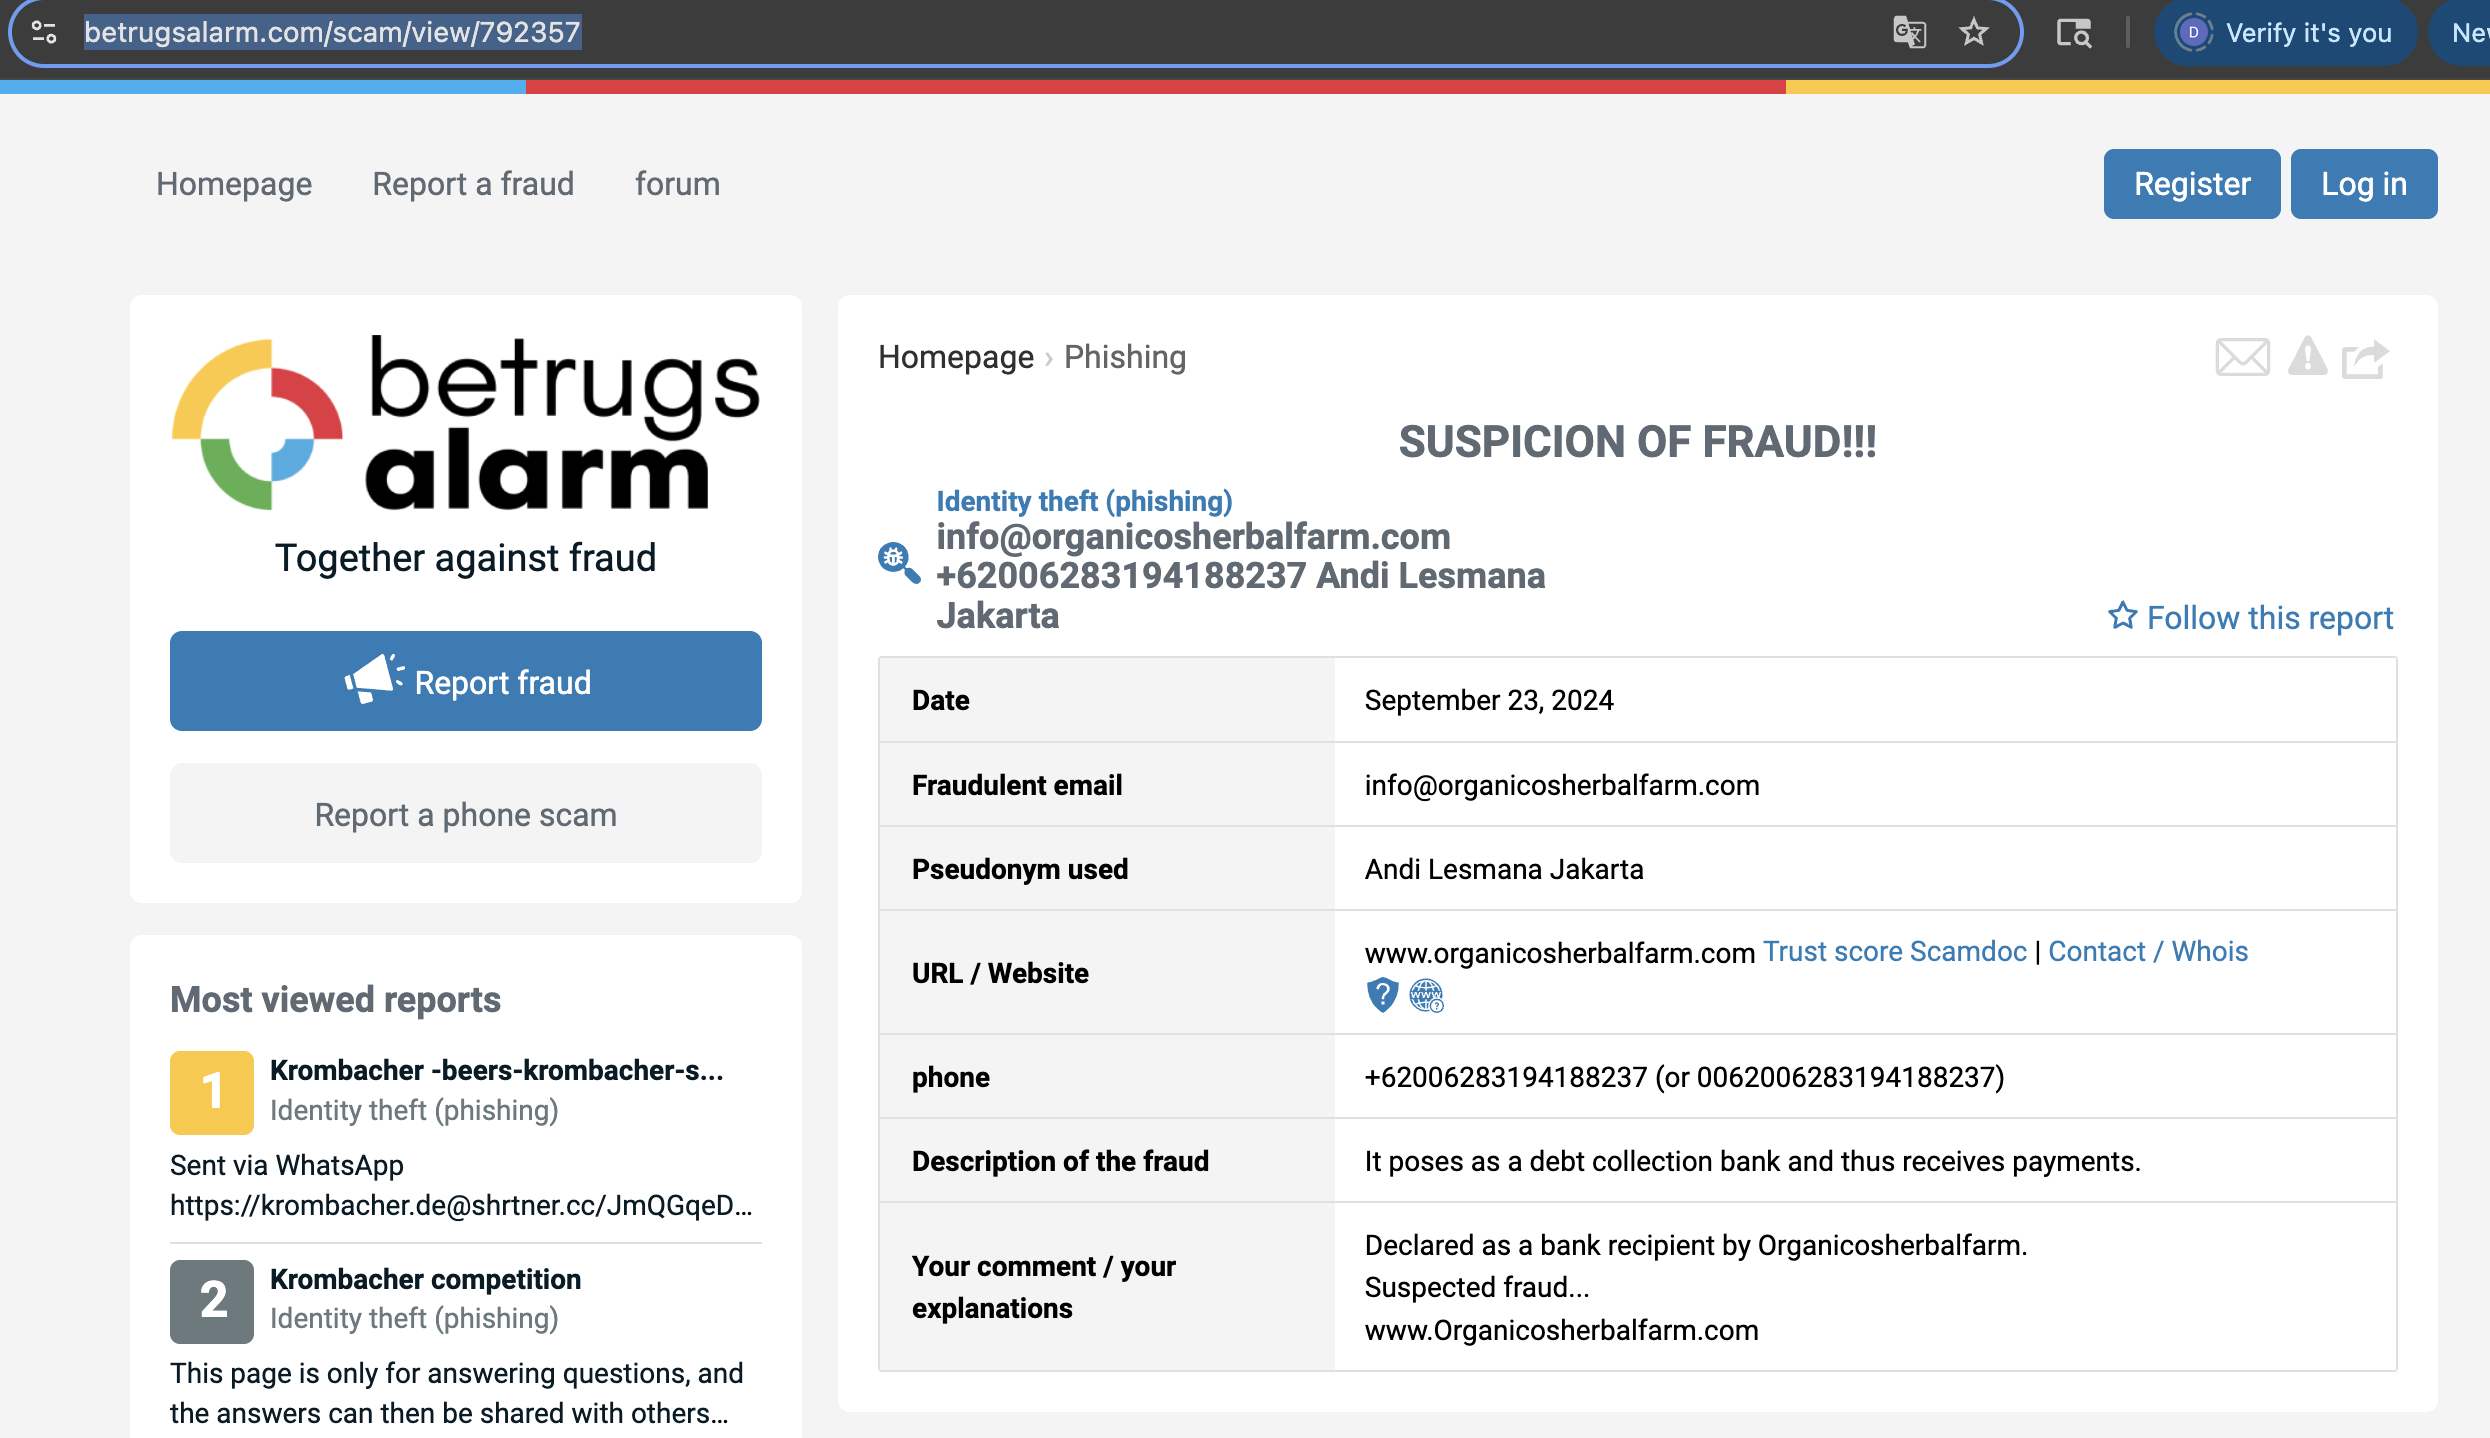
A separate Betrugsalarm report from September 2024 pointed at organicosherbalfarm.com, [email protected], the Andi Lesmana Jakarta name, and the same Indonesian phone number family:

Betrugsalarm report for Organicos Herbal Farm

Fraudulent email: [email protected]
Pseudonym used: Andi Lesmana Jakarta
Website: www.organicosherbalfarm.com
Phone: +62006283194188237

That makes denpharmltd.com more than a random clone found under cndlogisticsid.com. It appears to be an older front that had already been reported in public scam warnings, then later showed up again in the same nested-hostname style as the current cluster.

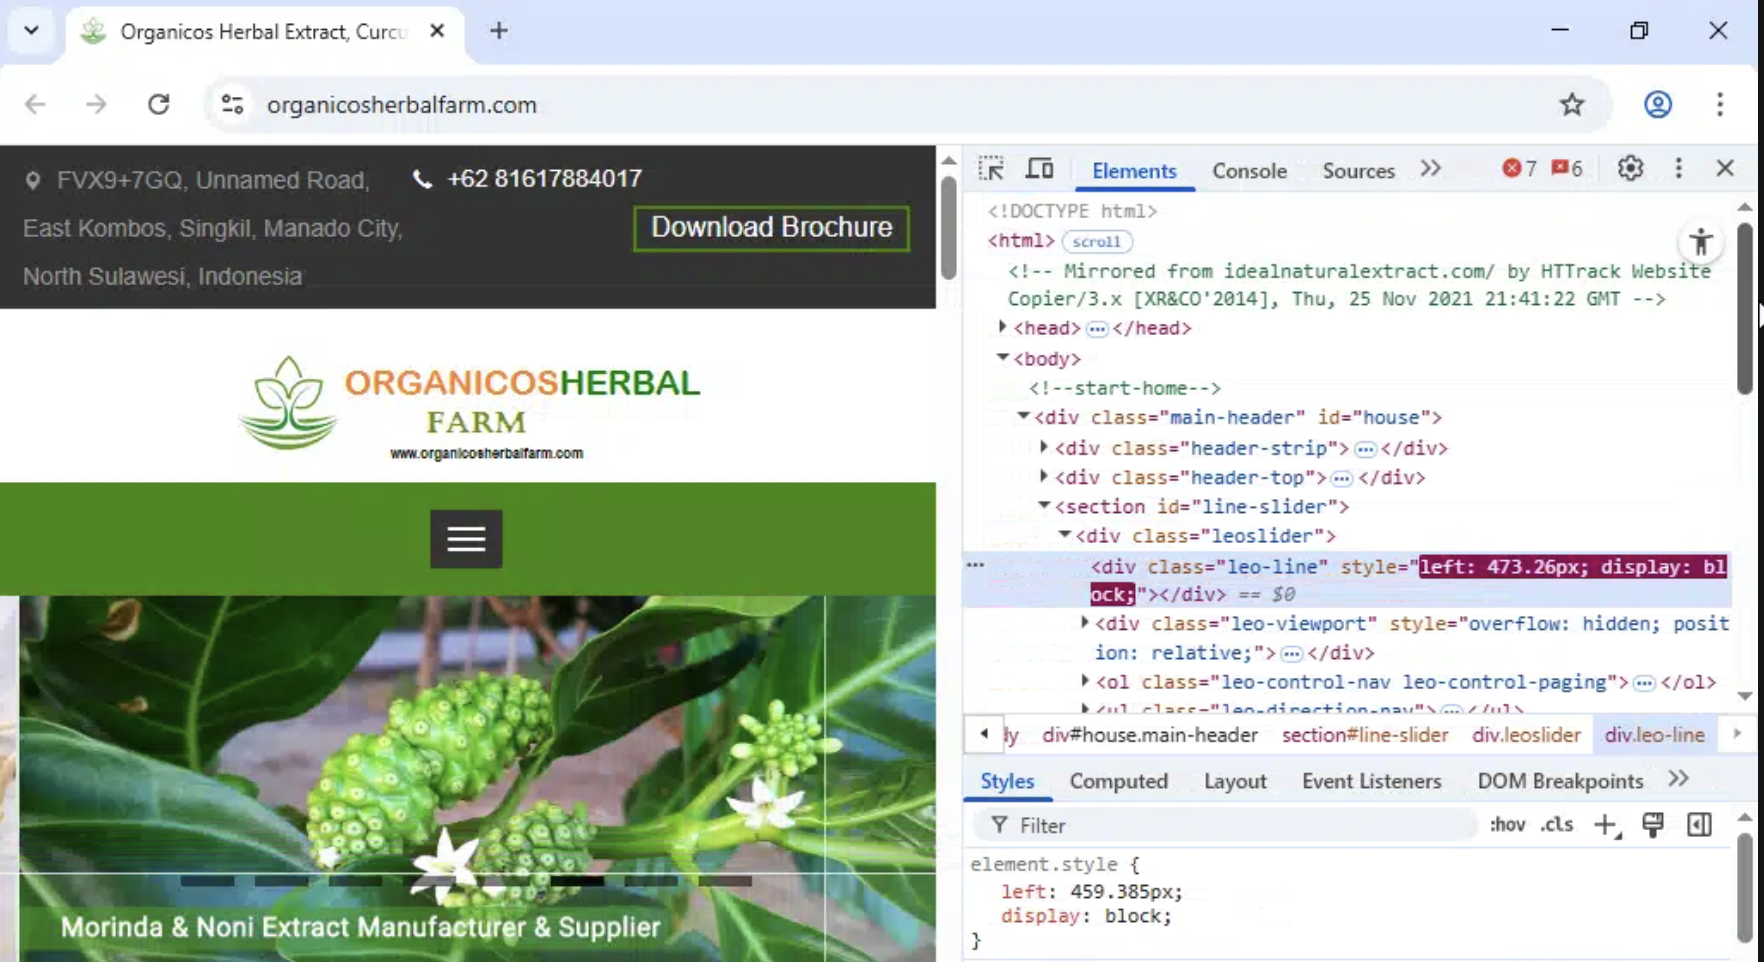
The Organicos side had its own clone residue:

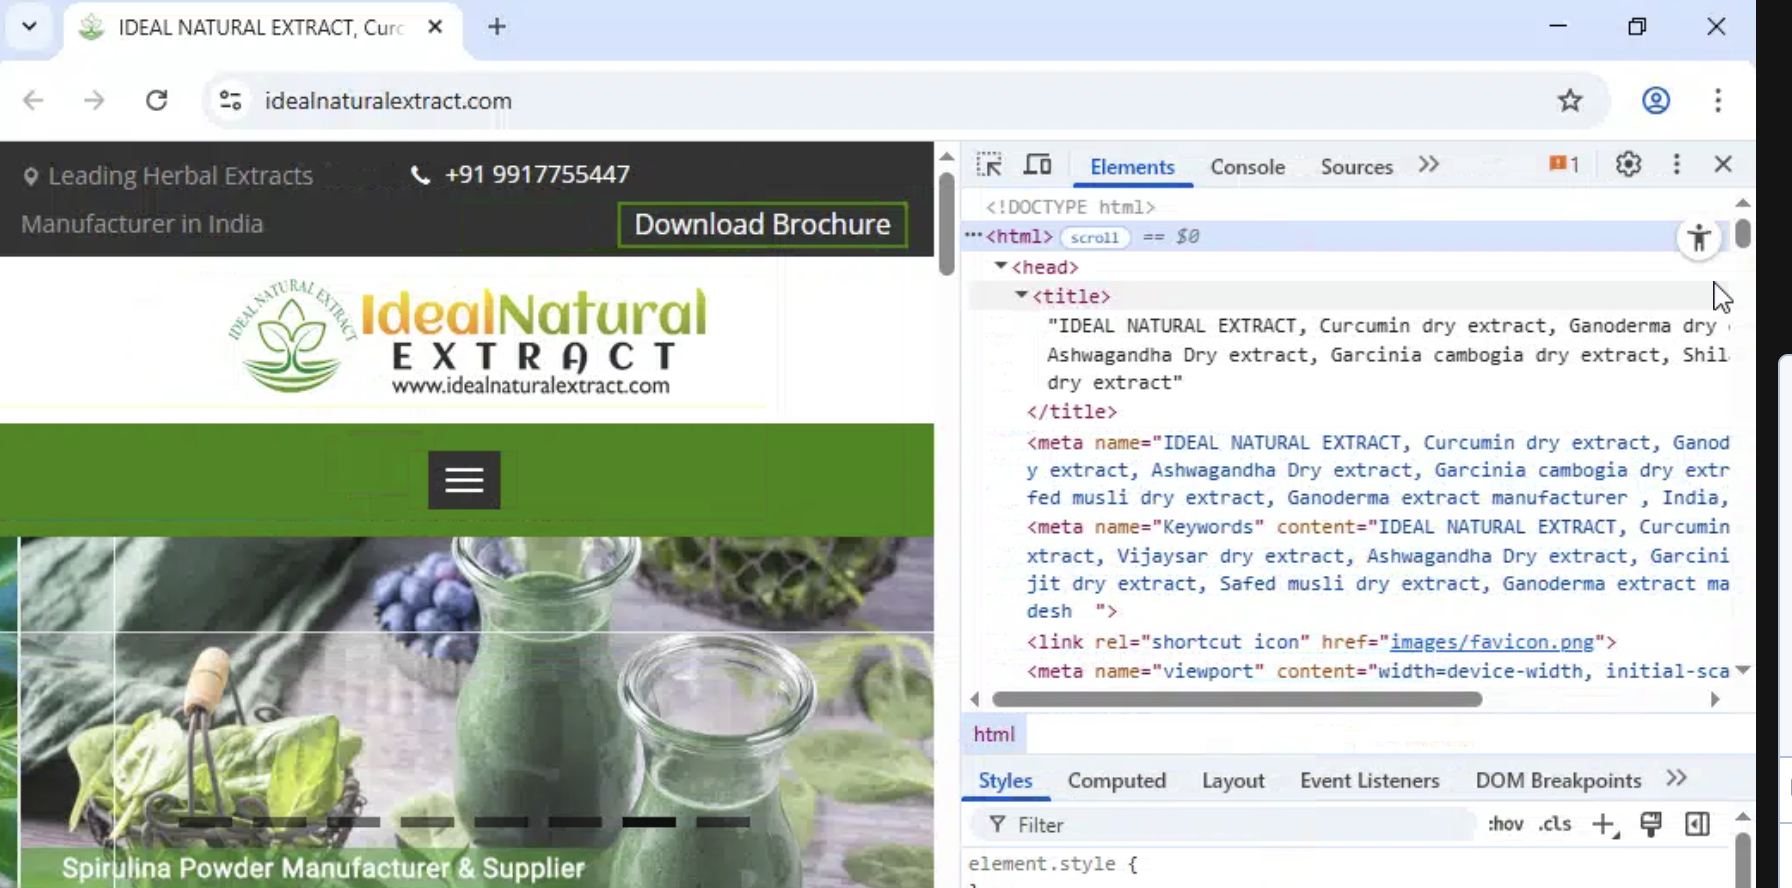
Organicos Herbal Farm page showing HTTrack mirror comment from Ideal Natural Extract

<!-- Mirrored from idealnaturalextract.com/ by HTTrack Website Copier/3.x
[XR&CO'2014], Thu, 25 Nov 2021 21:41:22 GMT -->

The live-looking source site, idealnaturalextract.com, still showed the same herbal-extract theme and product language:

Ideal Natural Extract source site used as clone source

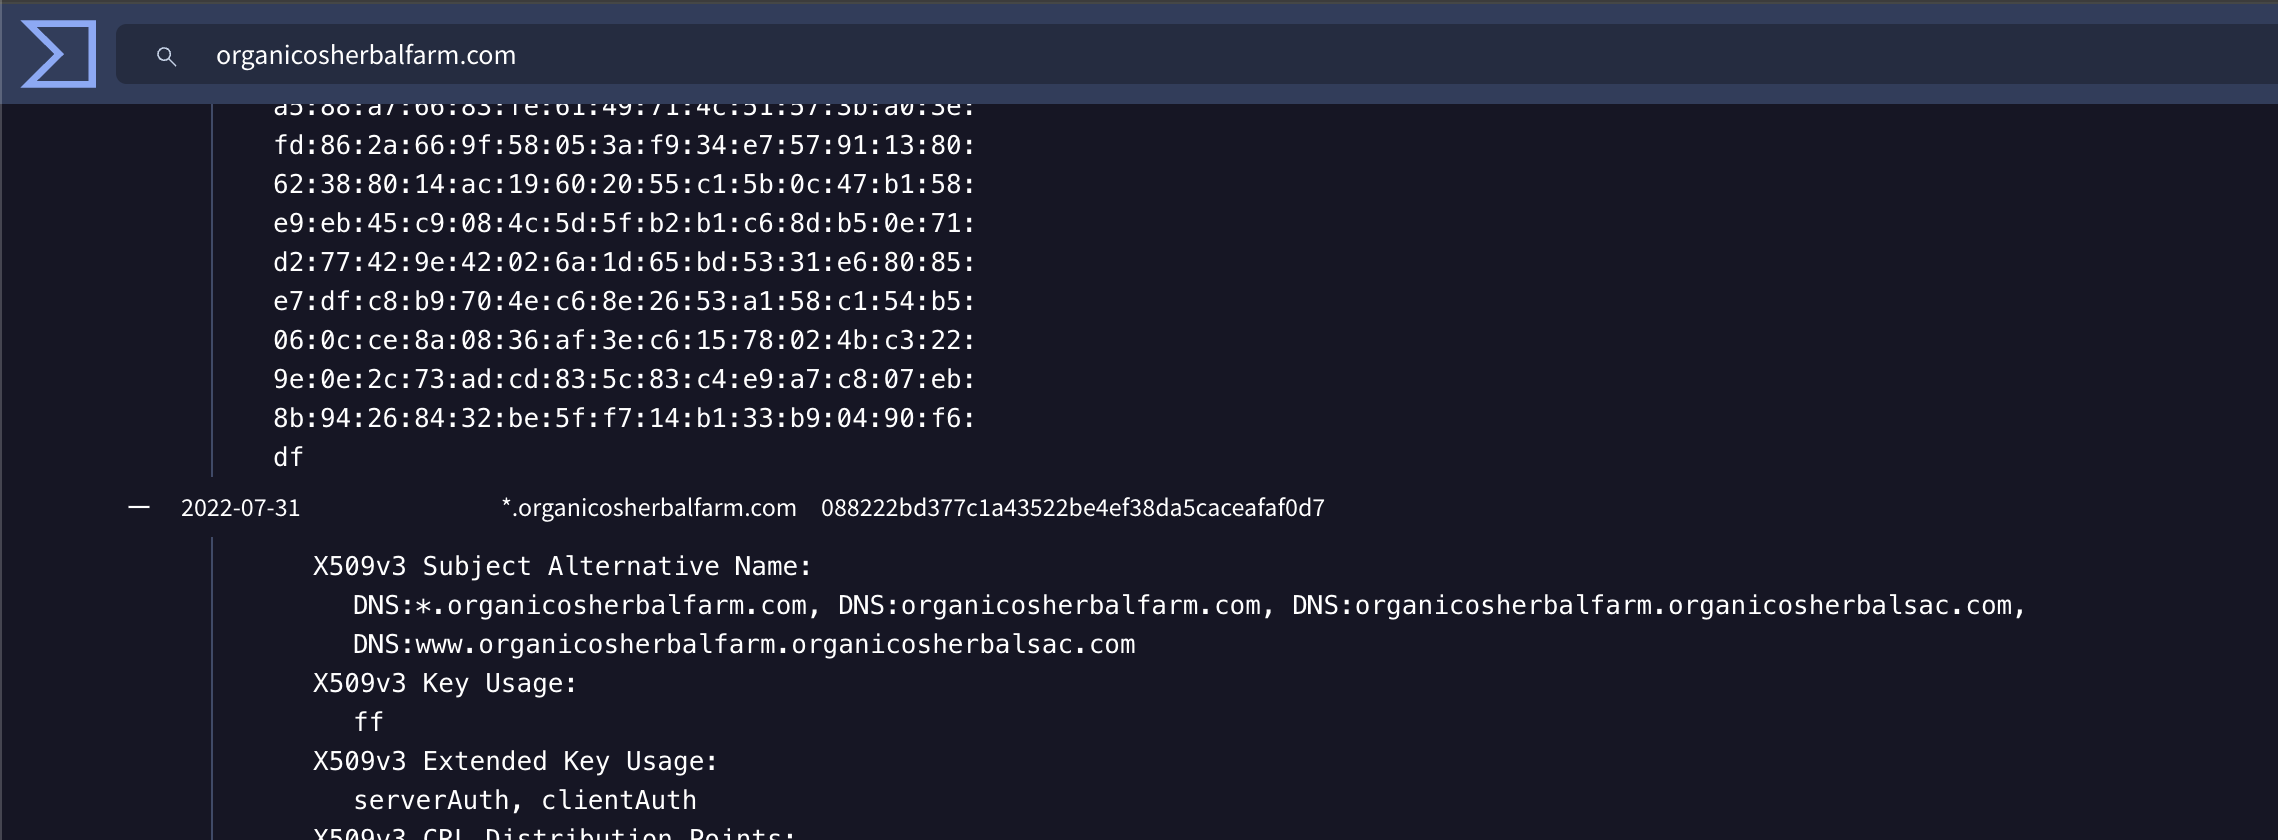
The certificate history for organicosherbalfarm.com also had a familiar little nested-domain tell:

VirusTotal certificate SANs for organicosherbalfarm.com showing organicosherbalsac.com nesting

*.organicosherbalfarm.com
organicosherbalfarm.com
organicosherbalfarm.organicosherbalsac.com
www.organicosherbalfarm.organicosherbalsac.com

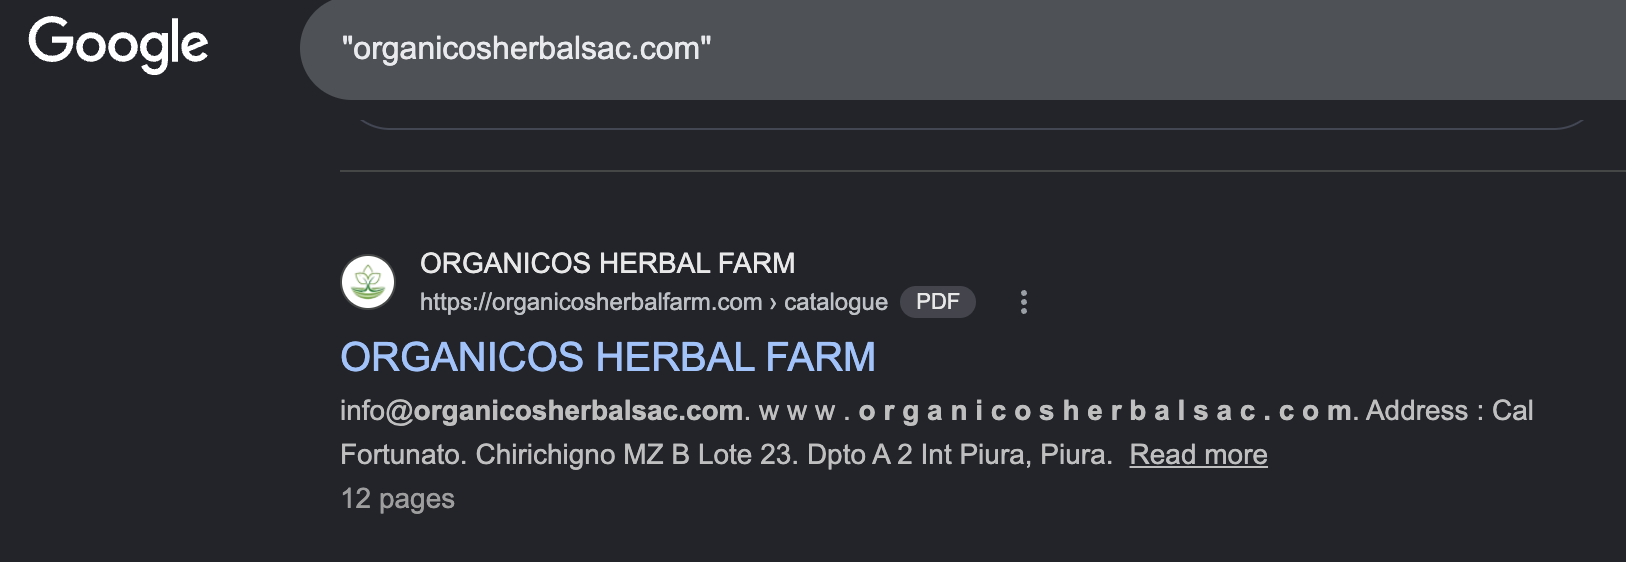
And Google still had organicosherbalsac.com indexed from the catalogue:

Google search result for organicosherbalsac.com residue

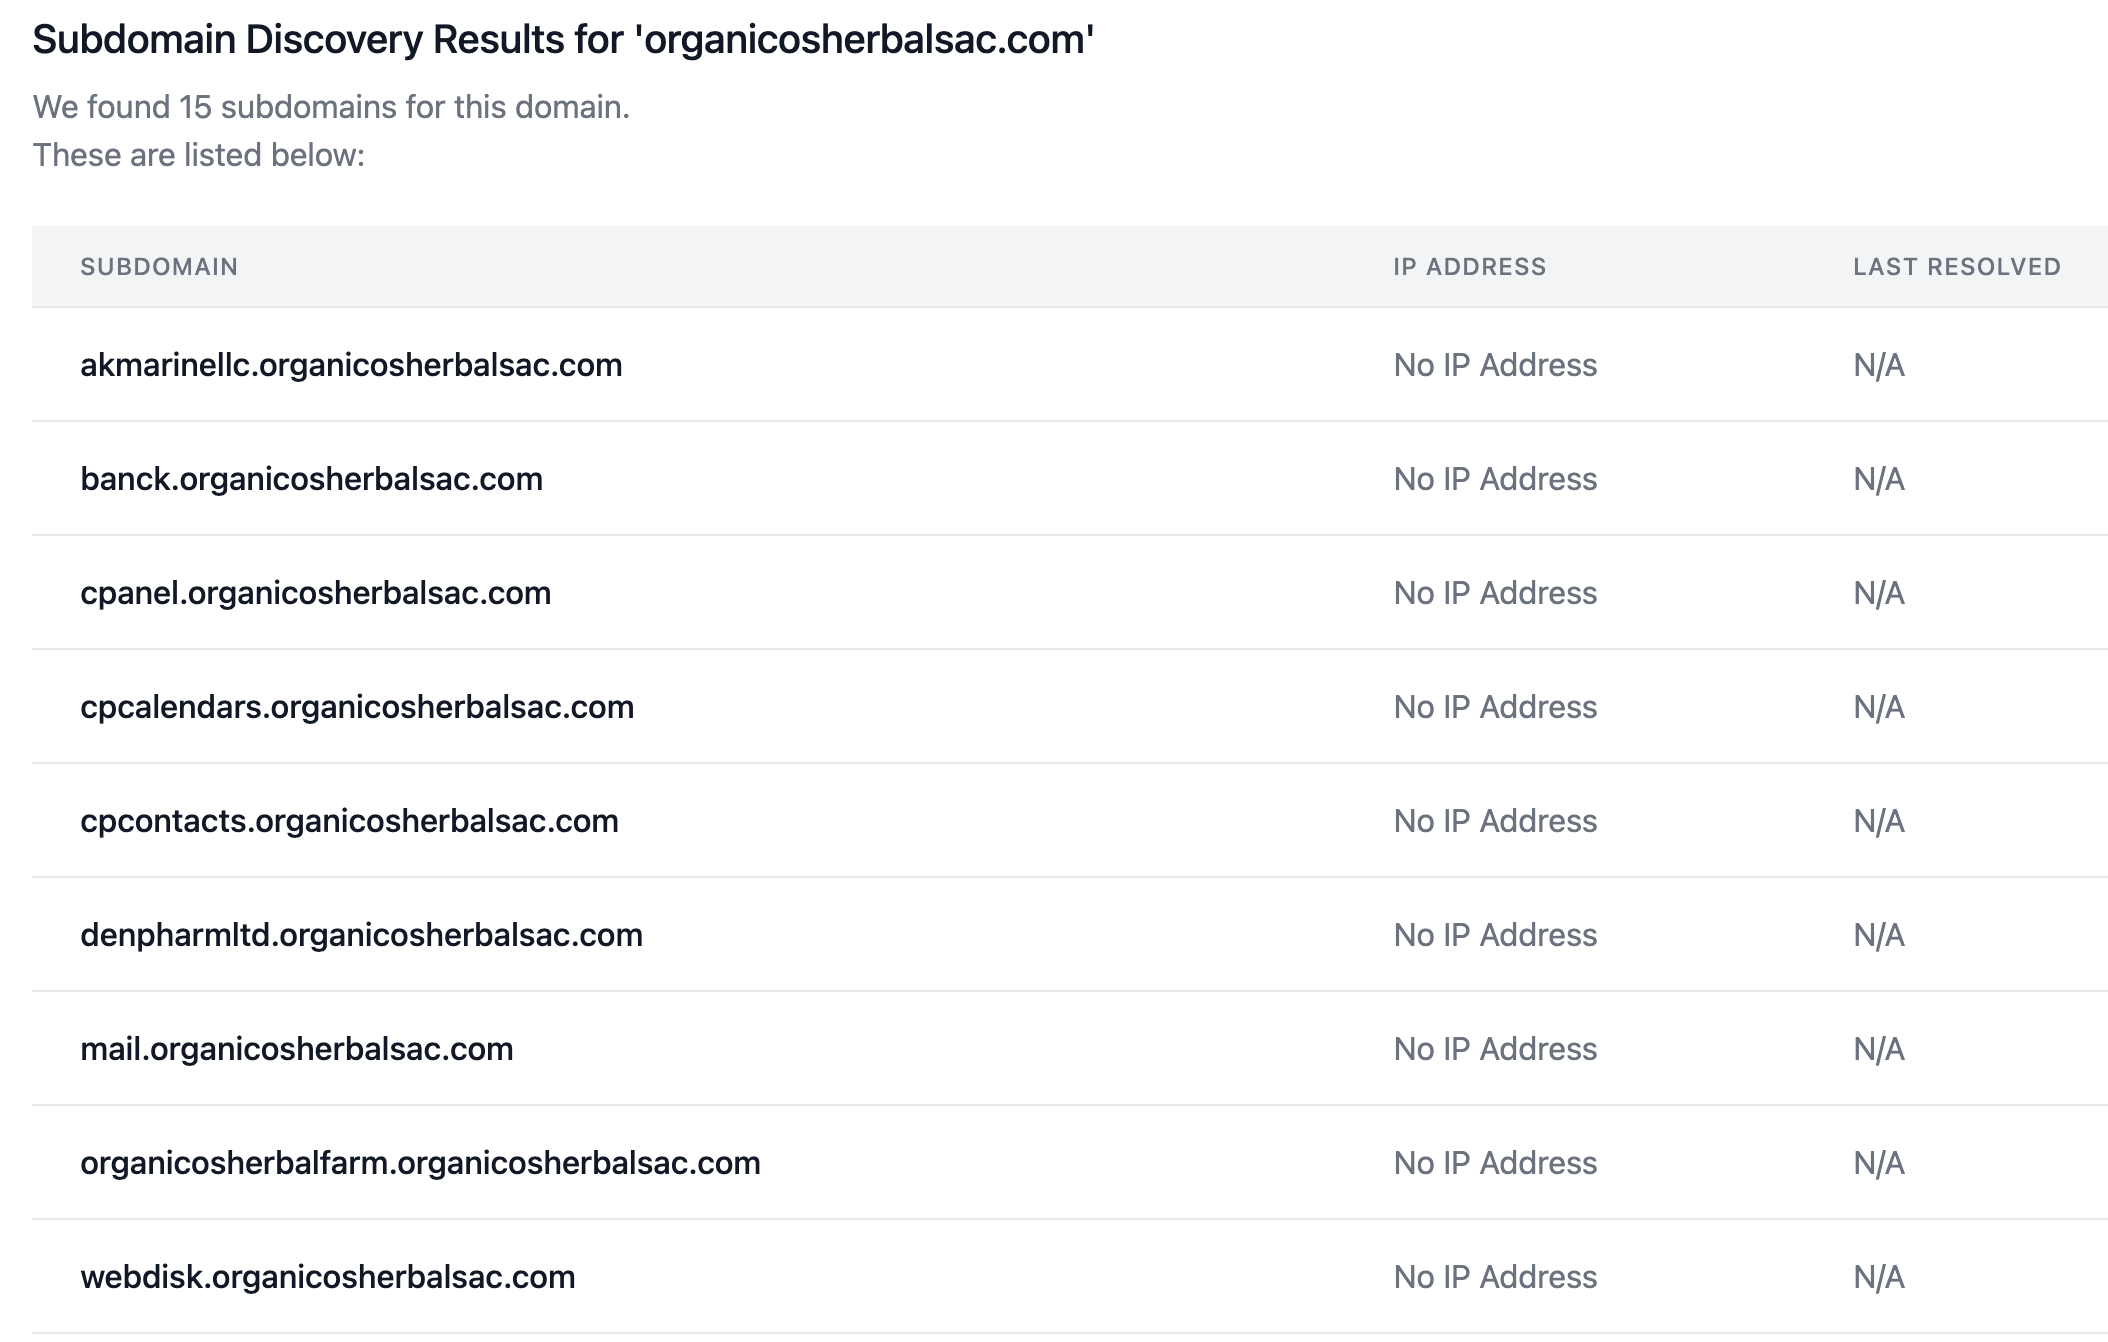
Subdomain discovery for organicosherbalsac.com added one more Denpharm bridge and a couple of names worth later checking:

Subdomain discovery results for organicosherbalsac.com

denpharmltd.organicosherbalsac.com
organicosherbalfarm.organicosherbalsac.com
akmarinellc.organicosherbalsac.com
banck.organicosherbalsac.com

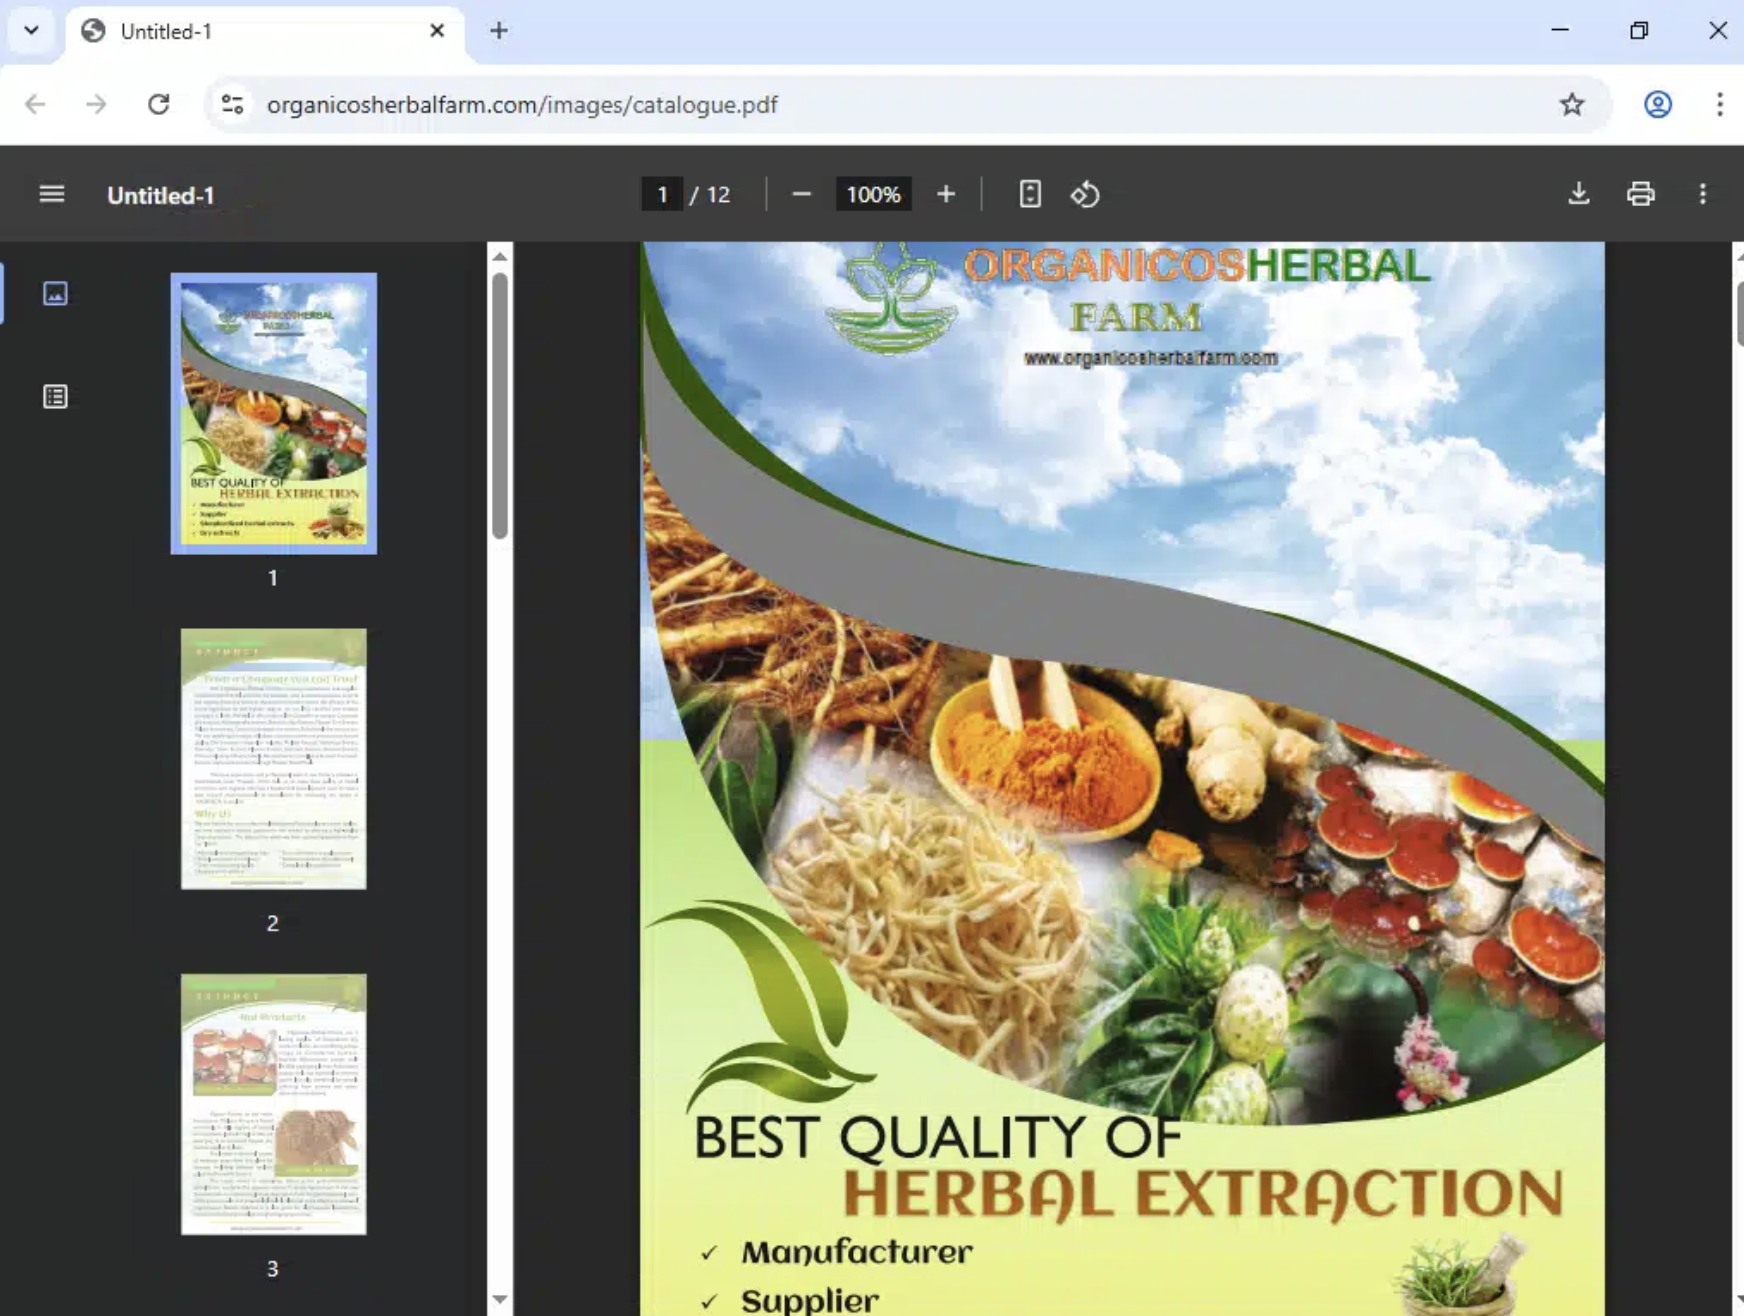
Organicos Herbal Farm catalogue PDF cover

The last page carried the contact details:

Organicos Herbal Farm catalogue contact page

+62-83872929468

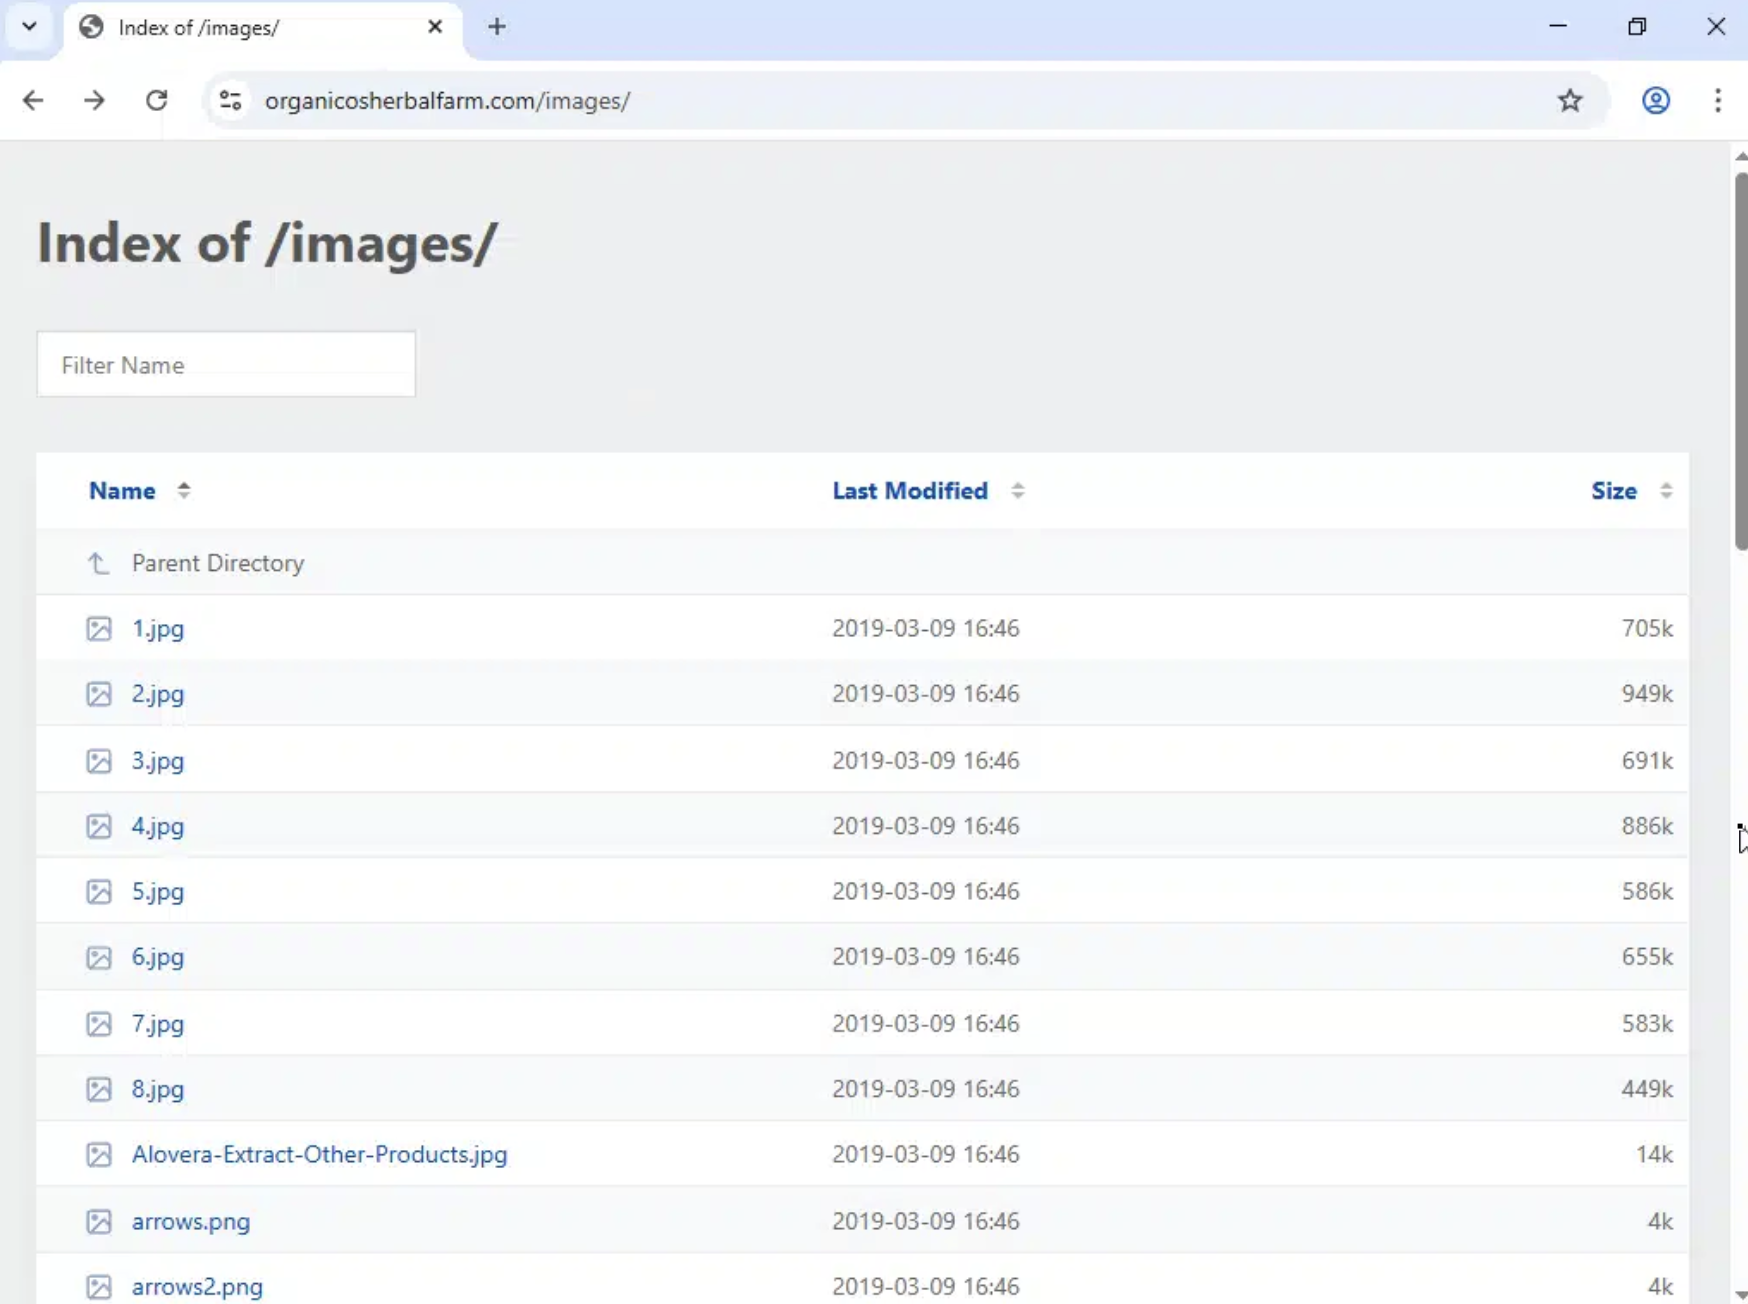
And because this cluster is sloppy, /images/ listed the site assets directly:

Open directory listing for organicosherbalfarm.com images

So the Denpharm/Organicos piece looks like an older procurement-scam branch: public warnings, cloned company sites, fake identity material, a product catalogue, and another nested-domain/certificate breadcrumb.

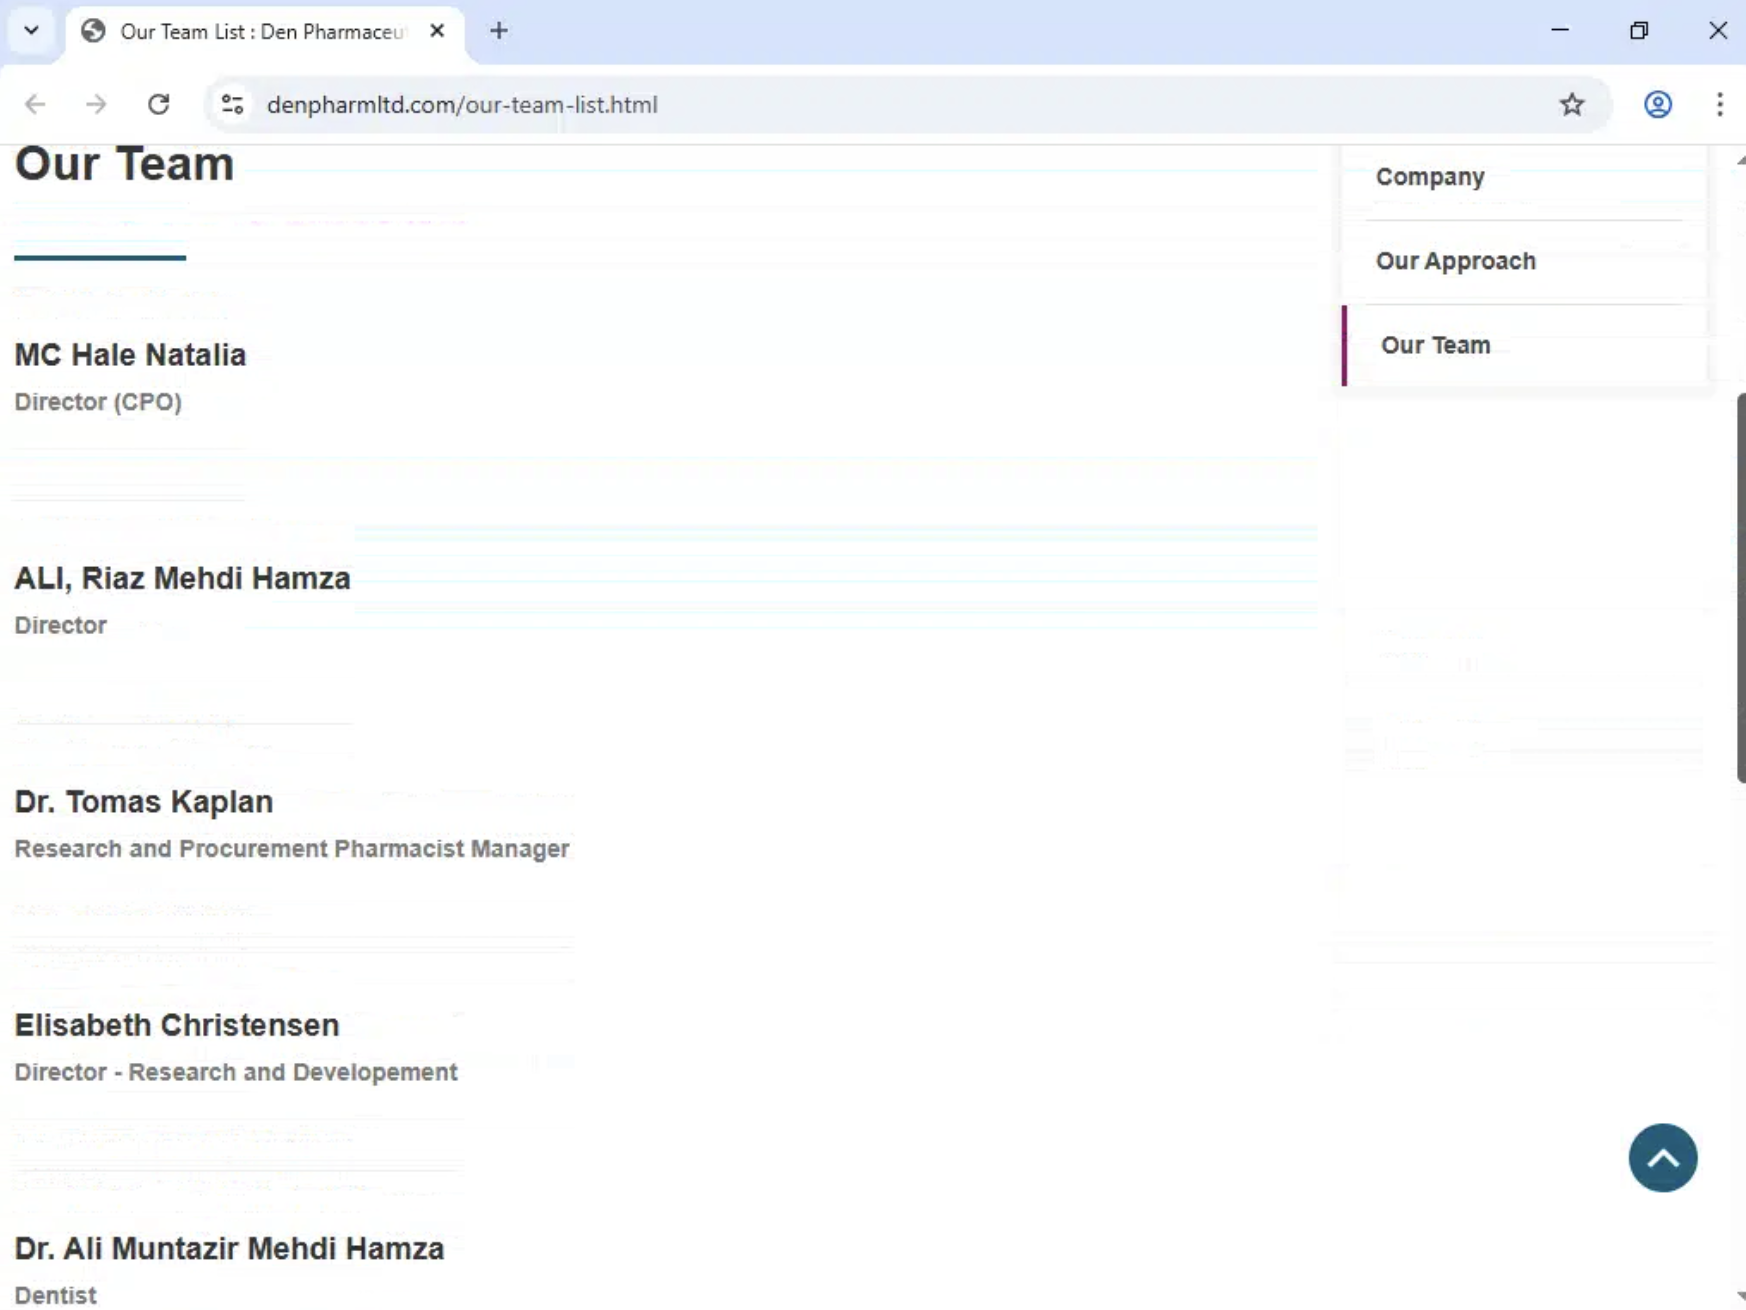
The Denpharm site itself still had a few helpful pages exposed. The team page included MC Hale Natalia and Dr. Tomas Kaplan, matching the names from the public warnings:

Denpharm team page showing Hale Natalia and Tomas Kaplan personas

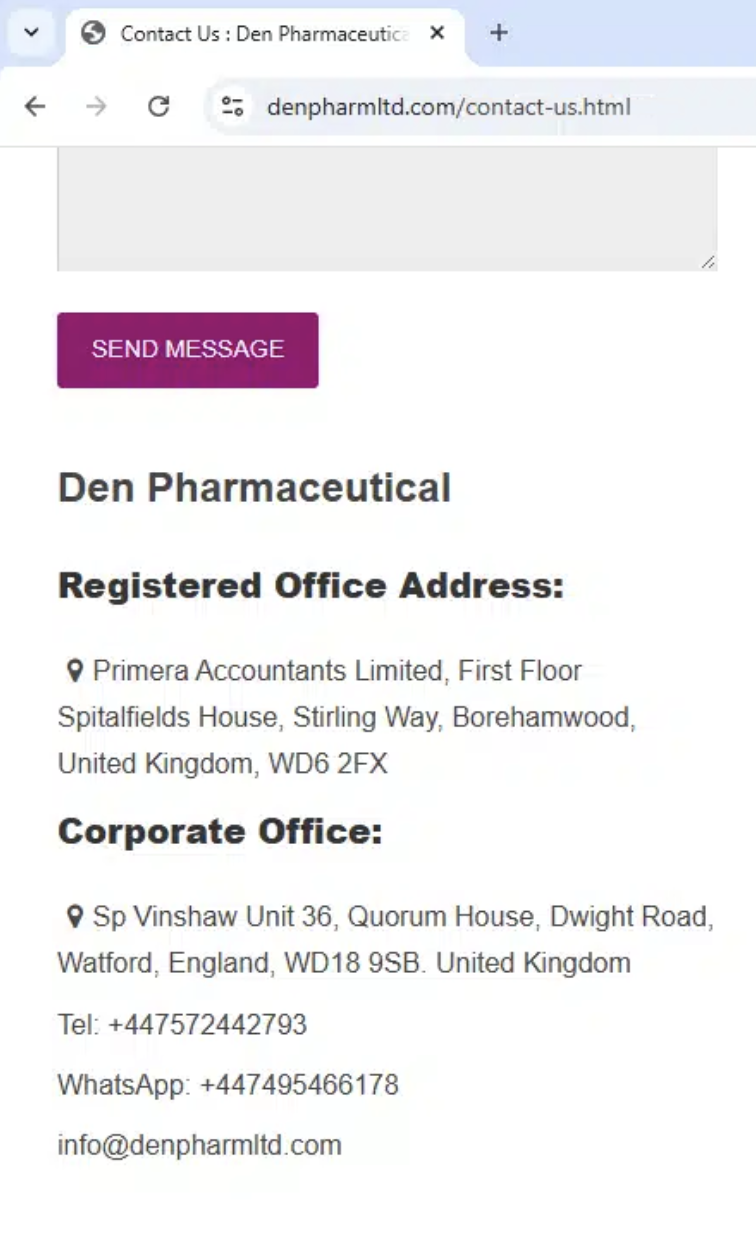
The contact page added more UK phone numbers:

Denpharm contact page showing address and phone numbers

Tel: +447572442793
WhatsApp: +447495466178

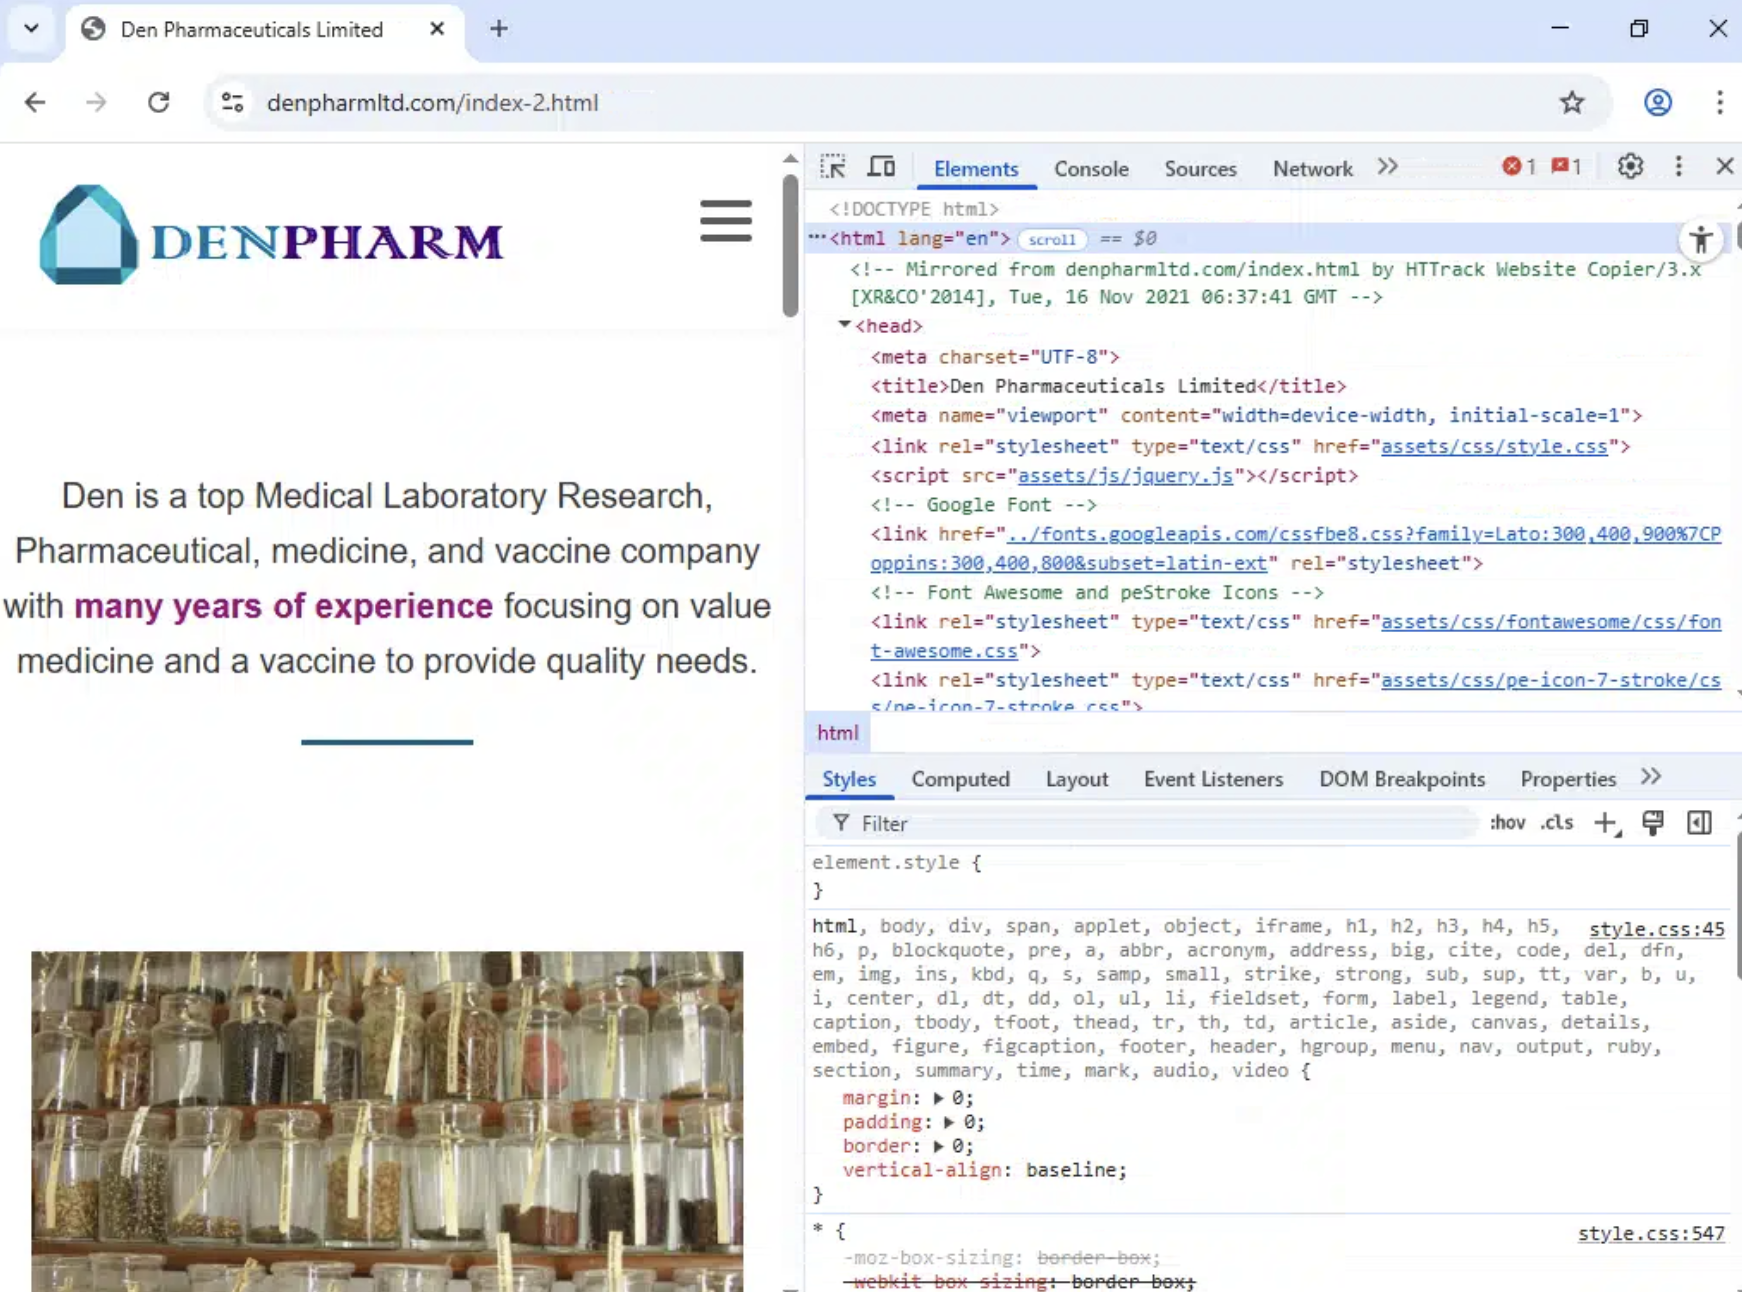
And index-2.html still carried the HTTrack timestamp:

Denpharm index-2 page showing HTTrack mirror comment

<!-- Mirrored from denpharmltd.com/index.html by HTTrack Website Copier/3.x
[XR&CO'2014], Tue, 16 Nov 2021 06:37:41 GMT -->

The "CND Logistics" theme also had a sibling-looking site:

CND Logistics US site

cndlogisticsuc.com
cndlogisticsuc.com.cndlogisticsid.com

Mail hosting surfaces

The fake pharma domains exposed the usual hosted-mail and control-panel elements:

autoconfig.kovdackpharmltd.com
autodiscover.kovdackpharmltd.com
cpanel.kovdackpharmltd.com
webmail.kovdackpharmltd.com
whm.kovdackpharmltd.com
mail.kovdackpharmltd.com

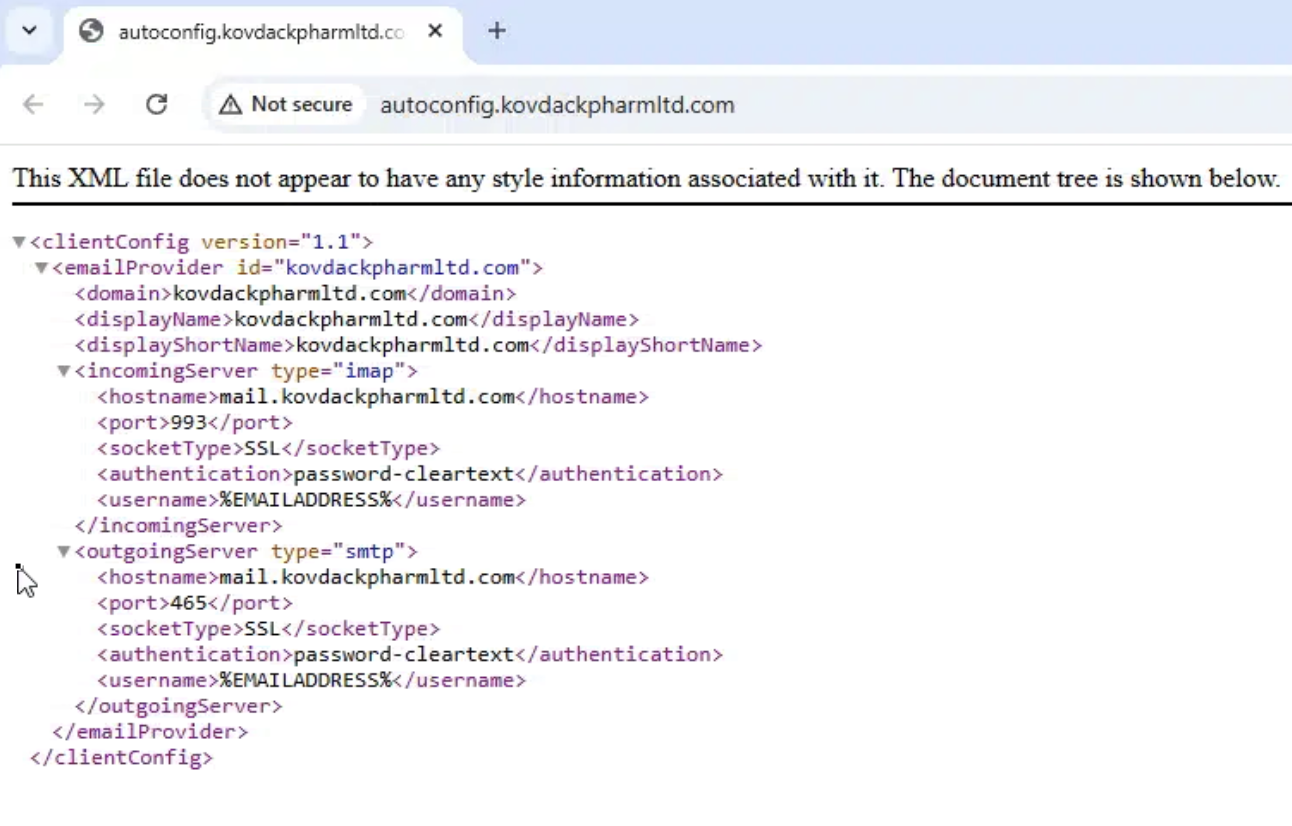
The autoconfig endpoint returned a Thunderbird-style XML profile:

autoconfig XML for kovdackpharmltd.com showing mail host settings

<emailProvider id="kovdackpharmltd.com">
<domain>kovdackpharmltd.com</domain>
<incomingServer type="imap">
<hostname>mail.kovdackpharmltd.com</hostname>
<port>993</port>
<socketType>SSL</socketType>
<authentication>password-cleartext</authentication>
</incomingServer>
<outgoingServer type="smtp">
<hostname>mail.kovdackpharmltd.com</hostname>
<port>465</port>
<socketType>SSL</socketType>
<authentication>password-cleartext</authentication>
</outgoingServer>
</emailProvider>

noozkackpharmaltd.com (and others) exposed the same kind of autoconfig profile for its own mail host.

The mail-service pivot

movzenpharmltd.com used a shared mail exchanger at one point in the investigation. VirusTotal confirms the mail service touched by this cluster has suspicious community context:

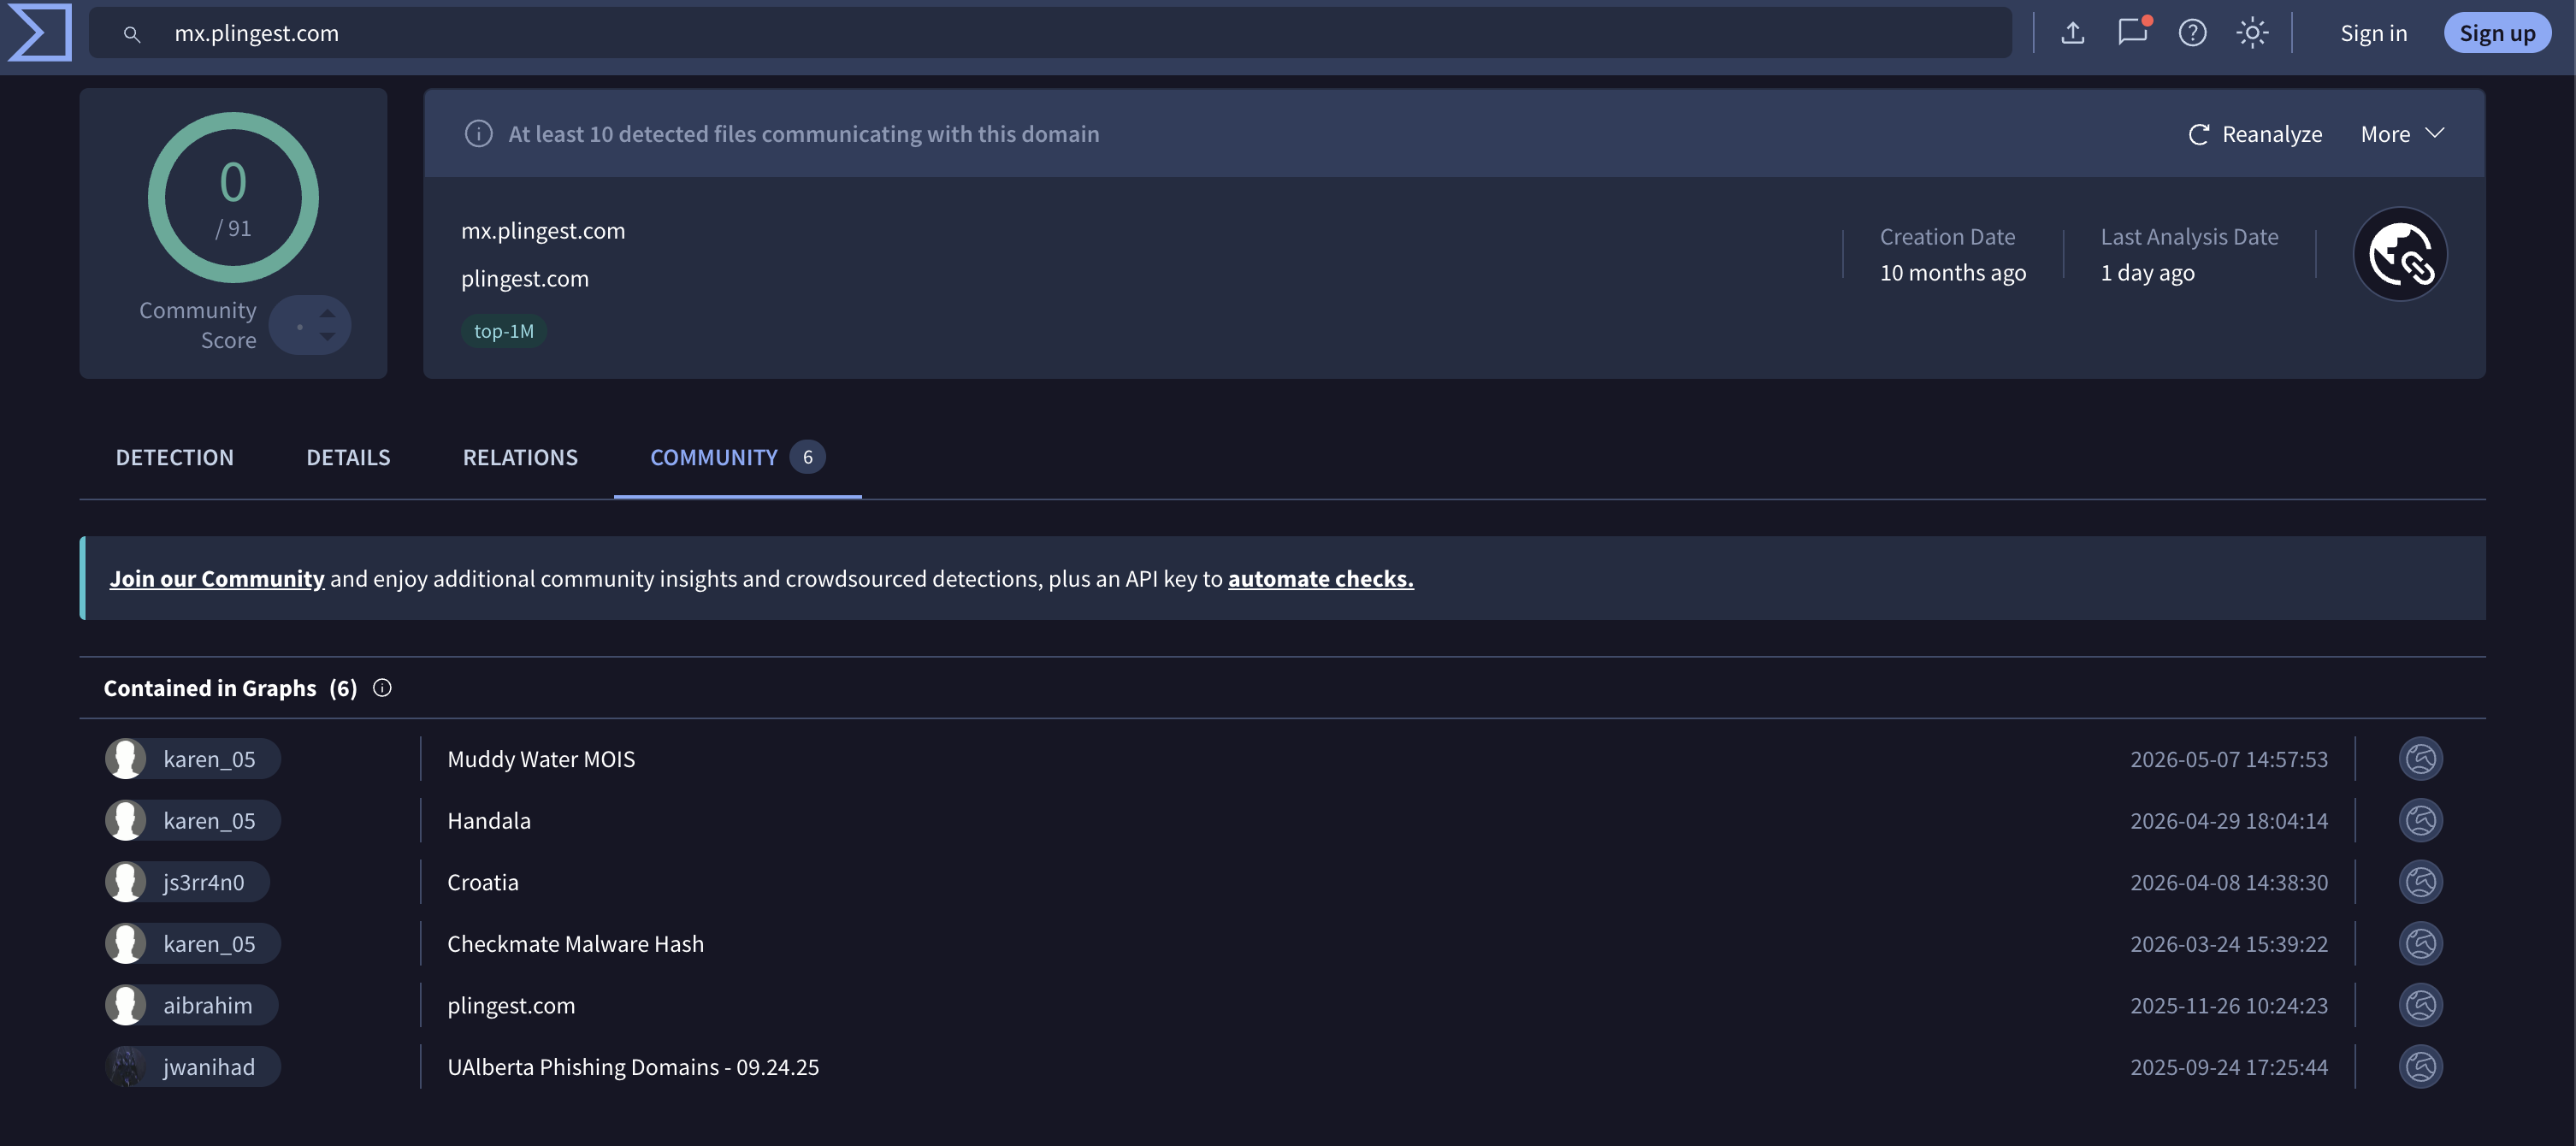
VirusTotal community graph view for mx.plingest.com

At least 10 detected files communicating with this domain

Contained in graphs:
- Muddy Water MOIS
- Handala
- Croatia
- Checkmate Malware Hash
- plingest.com
- UAlberta Phishing Domains - 09.24.25

Also, reverse-MX data showed a huge number of domains using that mail server. So, for IOC purposes, I am treating it as shared hosting/mail context rather than campaign-specific infrastructure.

IOCs

Email identities

Names and pseudonyms

DR. ROZENTAL ALEKSANDR
Tomas Kaplan
MC Hale Natalia
Andi Lesmana Jakarta
Baskoro Singgin

Domains and hostnames

markusnovanlaw.org
denpharmsltd.com
saipoveldar.com
kovdackpharmltd.com
noozkackpharmaltd.com
movzenpharmltd.com
dooxweckpharmaltd.com
cndlogisticsid.com
cndlogisticsuc.com
drpsf.site
drpsf.online
denpharmltd.com
organicosherbalfarm.com
organicosherbalsac.com

Nested hostnames

movzenpharmltd.com.cndlogisticsid.com
www.movzenpharmltd.com.cndlogisticsid.com
movzen-pharmltd.com.cndlogisticsid.com
www.movzen-pharmltd.com.cndlogisticsid.com
denpharmltd.com.cndlogisticsid.com
www.denpharmltd.com.cndlogisticsid.com
drpsf.online.cndlogisticsid.com
www.drpsf.online.cndlogisticsid.com
cndlogisticsuc.com.cndlogisticsid.com
www.cndlogisticsuc.com.cndlogisticsid.com
kovdackpharmltd.com.saipoveldar.com
www.kovdackpharmltd.com.saipoveldar.com
noozkackpharmaltd.com.saipoveldar.com
www.noozkackpharmaltd.com.saipoveldar.com
organicosherbalfarm.organicosherbalsac.com
www.organicosherbalfarm.organicosherbalsac.com
denpharmltd.organicosherbalsac.com

Exposed service hostnames

autoconfig.kovdackpharmltd.com
autodiscover.kovdackpharmltd.com
cpanel.kovdackpharmltd.com
webmail.kovdackpharmltd.com
whm.kovdackpharmltd.com
mail.kovdackpharmltd.com

autoconfig.noozkackpharmaltd.com
autodiscover.noozkackpharmaltd.com
ftp.noozkackpharmaltd.com
mail.noozkackpharmaltd.com

Reused visible contact values

+357 96 692 221
+357 95 550 432
+357 95 550 454
+357 96 910 893
+971 52 276 0126
+44 7572 443336
+62 83194188237
+62 83872929468
+62006283194188237
+44 7572 442793
+44 7495 466178

Detection Logic

IF
email authentication passes
AND the visible sender domain differs from the Reply-To domain
THEN
reply-chain fraud or BEC-style conversation starter likely

Observations & Conclusions

  1. SPF, DKIM, and DMARC passed, but authentication only proved control of the sending domain.
  2. The sender domain had a default CyberPanel page, not a credible law or doctor-related public site. (or even fake website prose).
  3. The Reply-To domain led into the fake pharma cluster.
  4. The pharma sites retained HTTrack comments naming www.delorbispharma.eu as the mirrored source.
  5. Kovdack, Noozkack, Movzen, and Dooxweck reused the same copied site structure with lightly edited names and contact details.
  6. Certificate and subdomain pivots exposed nested hostnames under saipoveldar.com and cndlogisticsid.com, several of which were live and serving cloned business pages.
  7. Mail autoconfig, webmail, cPanel, and WHM endpoints showed these domains were set up for operational mail.
  8. Public scam warnings tied denpharmltd.com to an older procurement-scam script and paired it with organicosherbalfarm.com.
  9. The Organicos branch had the same clone residue: HTTrack comments, a copied herbal-extract source site, indexed catalogue material, and nested certificate names.

Very normal. Very business. Please acknowledge the proposal I allegedly sent yesterday.

Indicators of Compromise (IOCs)
IOCs (domains, IP addresses, files, hashes, etc.) from this analysis are available on GitHub.
View on GitHub →

Spam Tales: Million-Dollar Jackpot Chance

· 6 min read

Overview

Yes, a million-dollar jackpot!

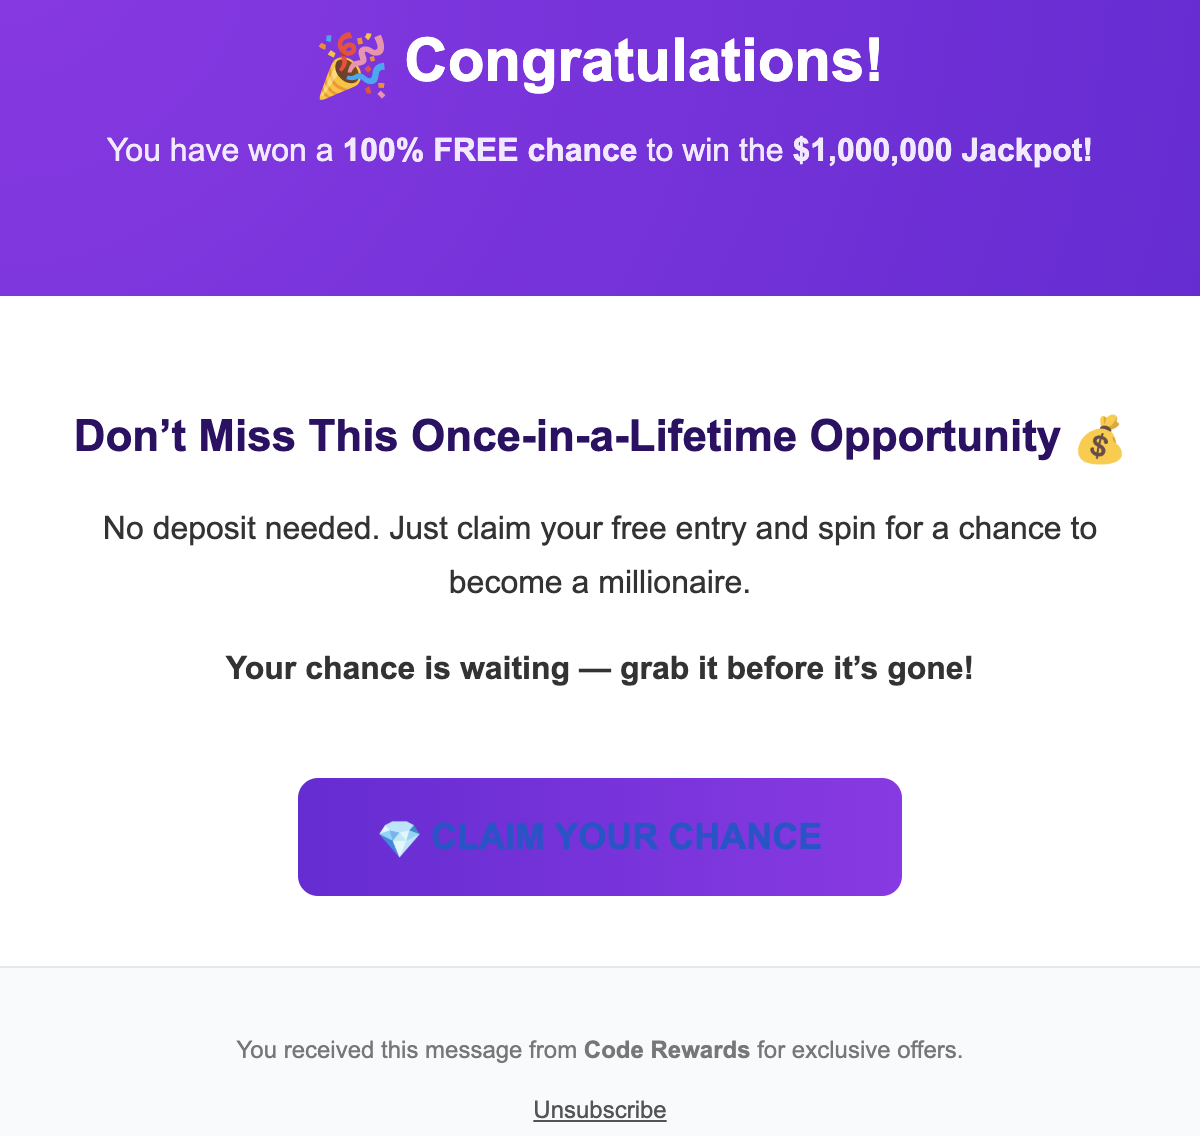
Rendered jackpot lure claiming a free chance to win a million-dollar jackpot

Congratulations!
You have won a 100% FREE chance to win the $1,000,000 Jackpot!
Claim your chance

The footer claims the message came from Code Rewards, which is generic enough to feel promotion-adjacent without requiring much brand impersonation effort.

Methodology

For this lure, I preserved the visible page, reviewed the message headers, and inspected the first hosted object without interacting with the final destination:

  1. Capture the rendered lure.
  2. Review the sender, recipient, timestamps, SPF, and DMARC result.
  3. Inspect the HTML for hidden filler content and action links.
  4. Decode the fragment payloads supplied in the CTA and unsubscribe URLs.
  5. Fetch the Google Cloud Storage HTML object directly.
  6. Review the client-side redirect script.
  7. Separate reusable campaign infrastructure from likely recipient or campaign-specific values.

Tools used

  • Browser developer tools in an isolated browser
  • Manual Base64 decoding of the URL fragment
  • curl for retrieving the first-stage HTML object
  • Message source view for headers, authentication, and hidden HTML content
  • Manual IOC extraction from the redirect script, message headers, and lure URL

Investigation

Email authentication

The message presented itself as:

From: CᴀsɪɴᴏRᴇᴡᴀʀᴅs <[email protected]>
Subject: user, No Deposit. No Risk. Just Real Casino Rewards!
Message-ID: <[email protected]>

Observed authentication and delivery details:

SPF: PASS with IP 91.99.29.100
DMARC: FAIL
Return-Path: return23203@lzmhneiktu7oayw784.pc8yosm64vt5bg7784.y4jfbahri016w87784.16niztwhjrk0cu9.hotnewscam.com
Received from: hotnewscam.com (static.100.29.99.91.clients.your-server.de [91.99.29.100])

SPF passed for the long hotnewscam.com return-path subdomain, not for the visible porqxyxml.com address shown to the recipient. DMARC failed because the authenticated sending domain did not align with the visible From domain.

The raw message also contained a malformed date placeholder:

Date: _smtpDate . _EMAILID

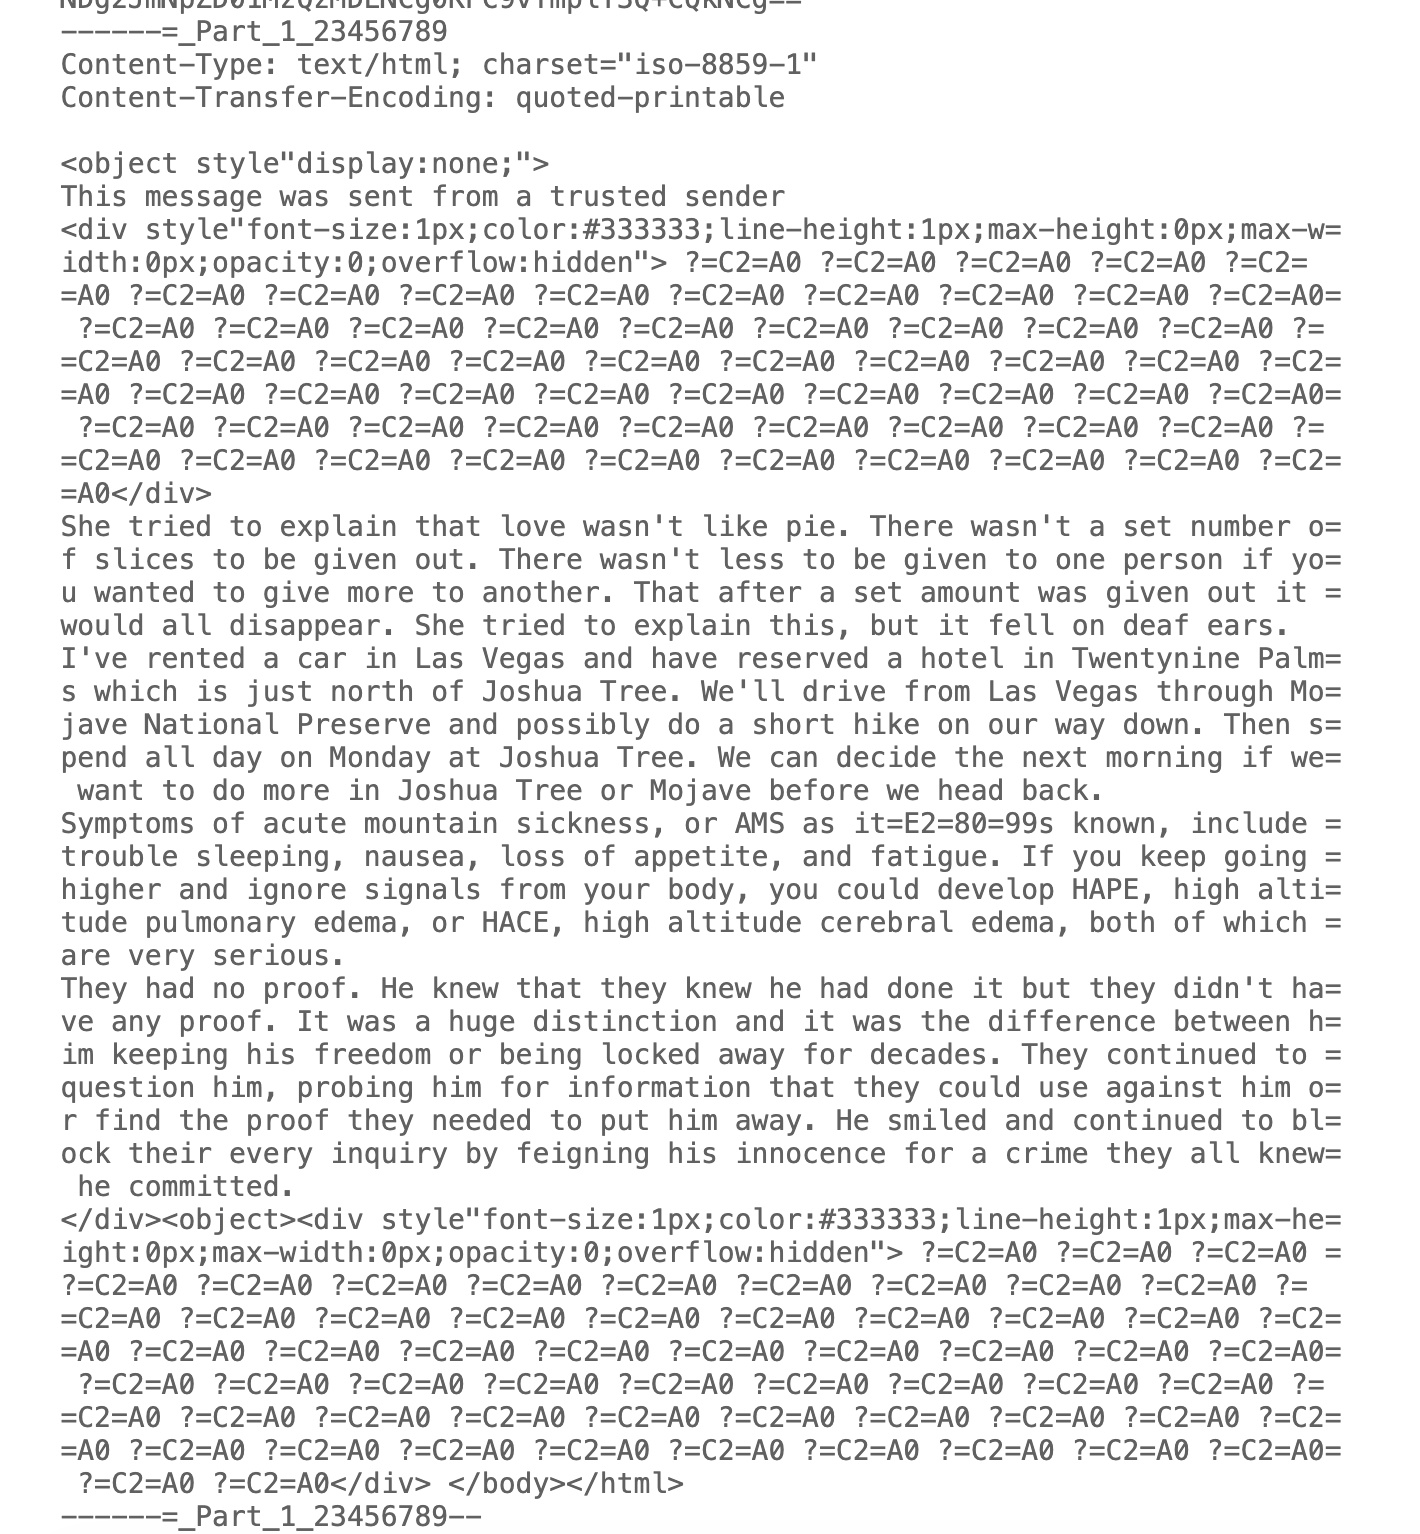
HTML filler

After the visible lure, the message includes a hidden block beginning with:

<ObJECT>
<tiTlE>
<div style="display:none;">
<!------------ START NEGATIVE ------------>

The hidden section mixes citrus-growing prose, random strings, copied-looking newsletter fragments, and unrelated transactional email snippets. That is classic content padding to make the message body look larger, more varied, and less obviously casino-spam-shaped to simple content filters.

The lure CTA used a Google Cloud Storage object with the tracking payload placed after the fragment marker:

https://storage.googleapis.com/25kdhsale/NWBH25.html#?Z289MSZzMT0yMjc1NTE2JnMyPTQzMDAwNzA1MyZzMz1HTEI=

The fragment content is Base64-encoded campaign data. Decoded, it becomes:

go=1&s1=2275516&s2=430007053&s3=GLB

That gives us three likely campaign or recipient tracking fields:

s1=2275516
s2=430007053
s3=GLB

The unsubscribe link points to the same hosted object with a slightly different Base64 fragment:

https://storage.googleapis.com/25kdhsale/NWBH25.html#?Z289MiZzMT0yMjc1NTE2JnMyPTQzMDAwNzA1MyZzMz1HTEI=

Decoded, that becomes:

go=2&s1=2275516&s2=430007053&s3=GLB

So go=1 appears to mark the main claim action, while go=2 appears to mark the unsubscribe action. Both preserve the same s1, s2, and s3 values (since they refer to 'me'!)

Unsubscribe behavior

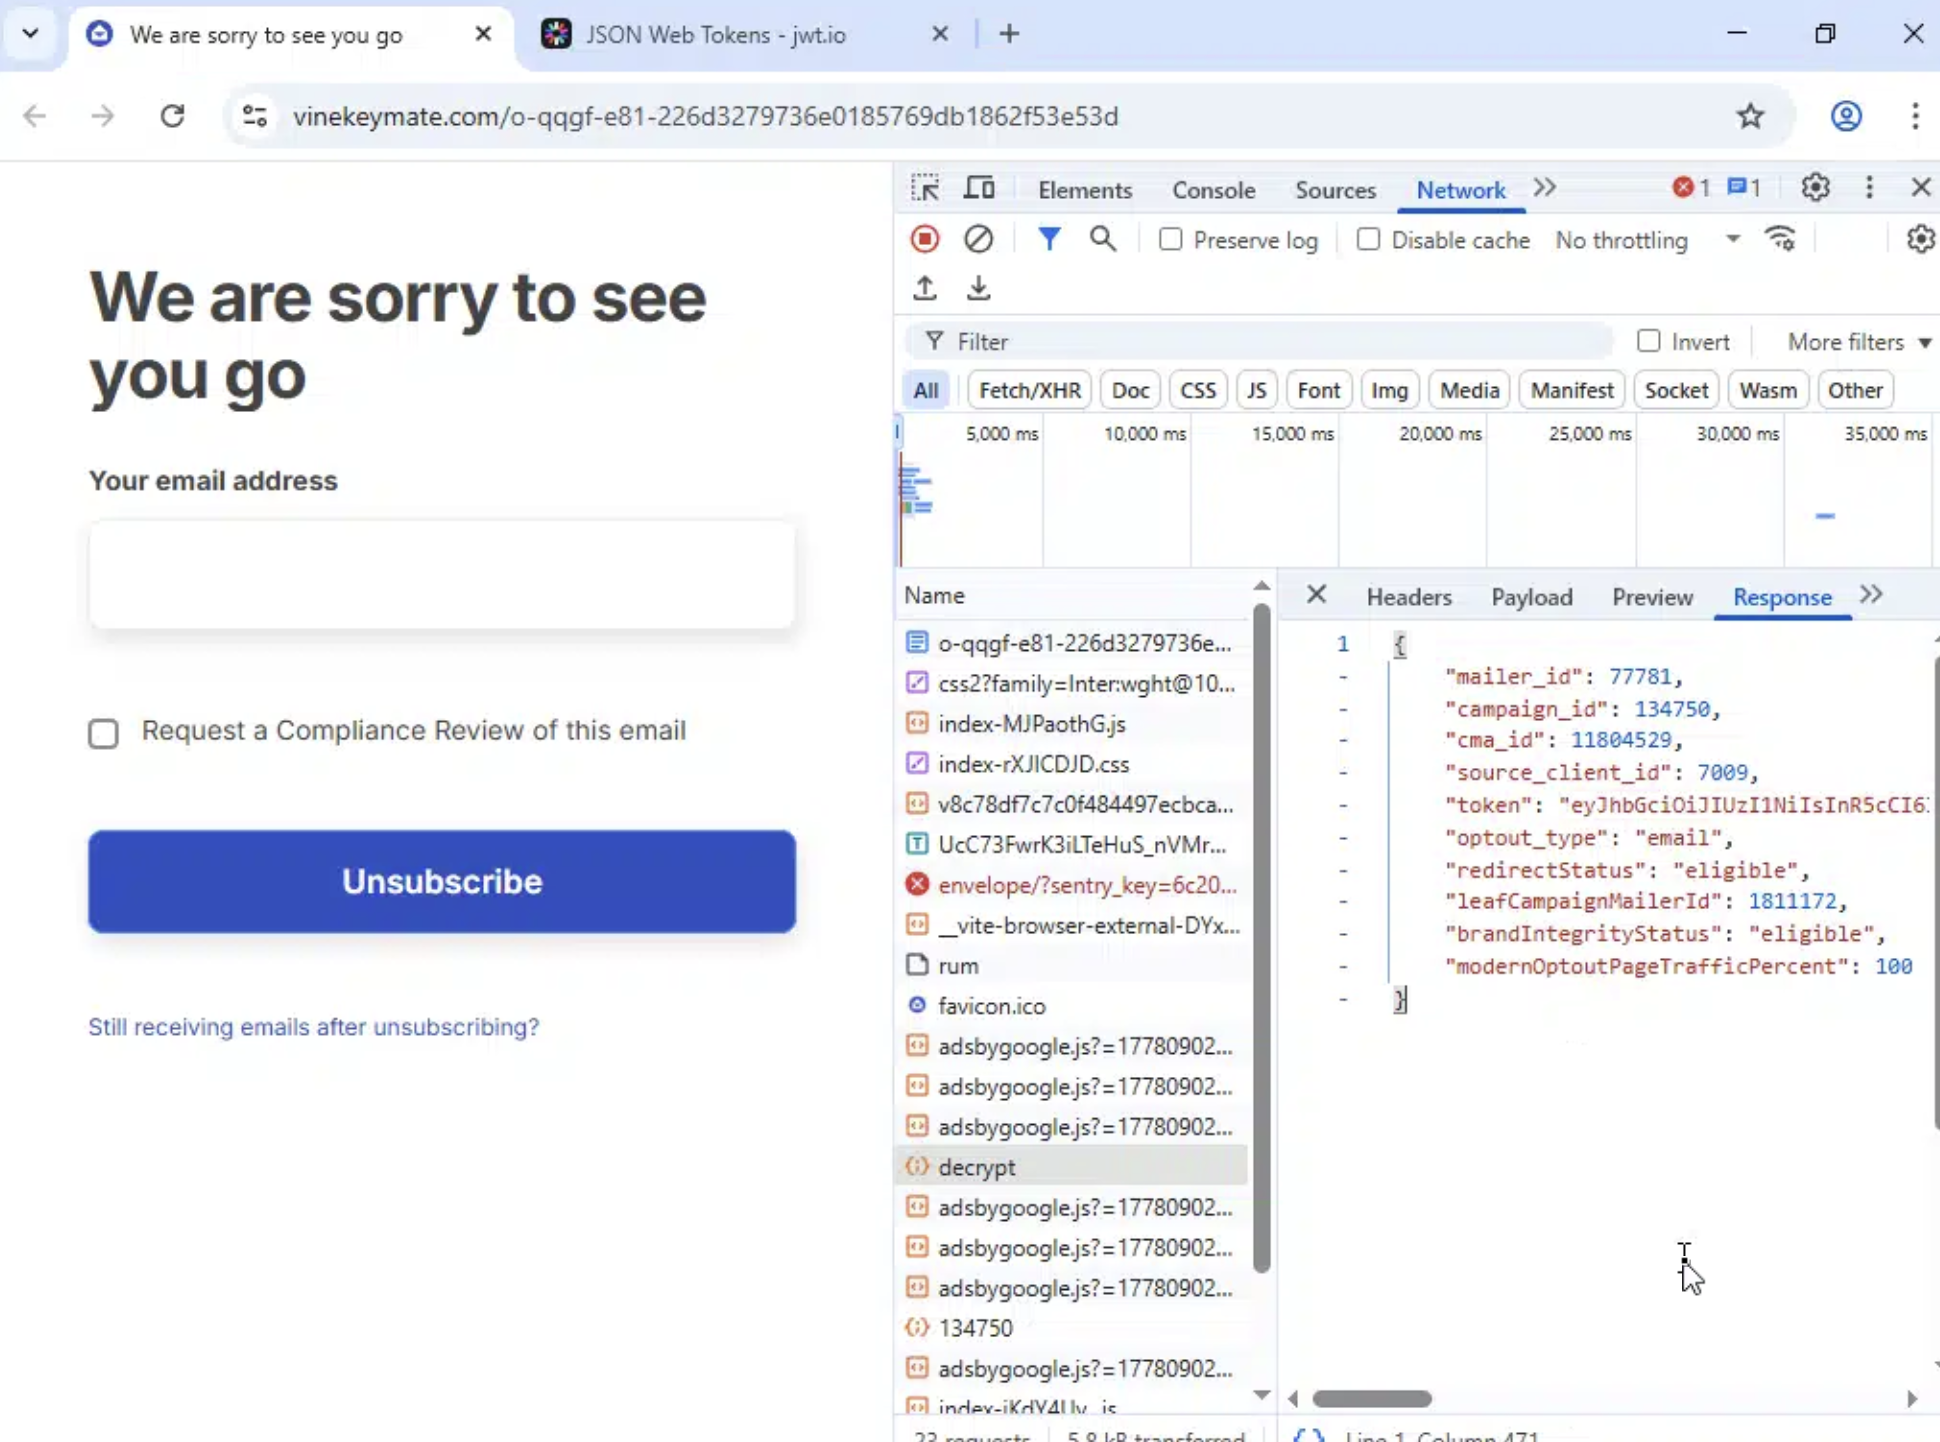
The go=2 sandbox run did not simply fail or return a static page. It redirected into an opt-out flow at:

vinekeymate.com/o-qqgf-e81-226d3279736e0185769db1862f53e53d

Sandboxed unsubscribe page and network response showing campaign metadata

The page title was:

We are sorry to see you go

The visible form requested an email address and included a checkbox labeled:

Request a Compliance Review of this email

In the network panel, a JSON response exposed campaign and opt-out metadata:

{
"mailer_id": 77781,
"campaign_id": 134750,
"cma_id": 11804529,
"source_client_id": 7009,
"optout_type": "email",
"redirectStatus": "eligible",
"leafCampaignMailerId": 1811172,
"brandIntegrityStatus": "eligible",
"modernOptOutPageTrafficPercent": 100
}

Redirect script

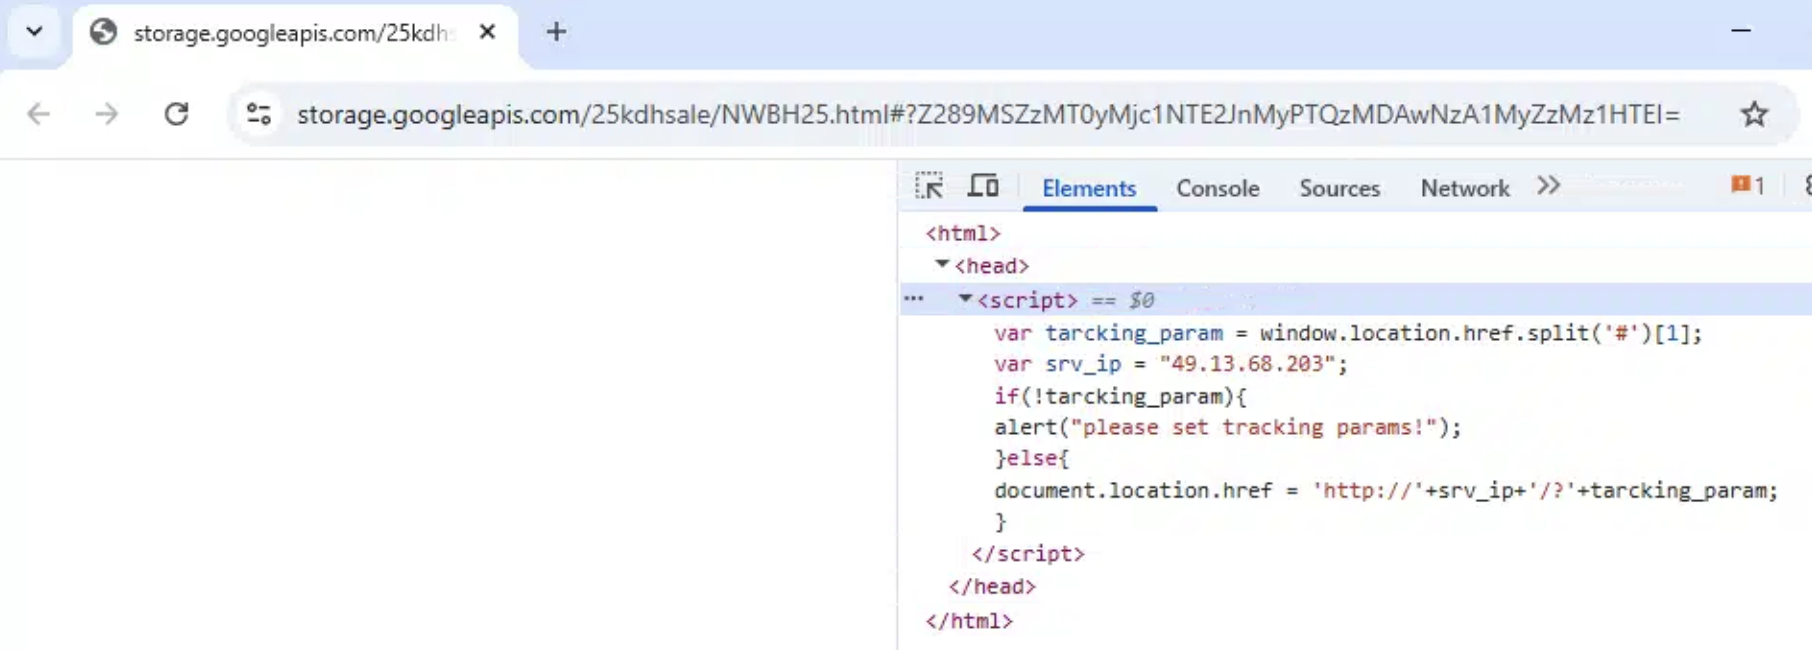
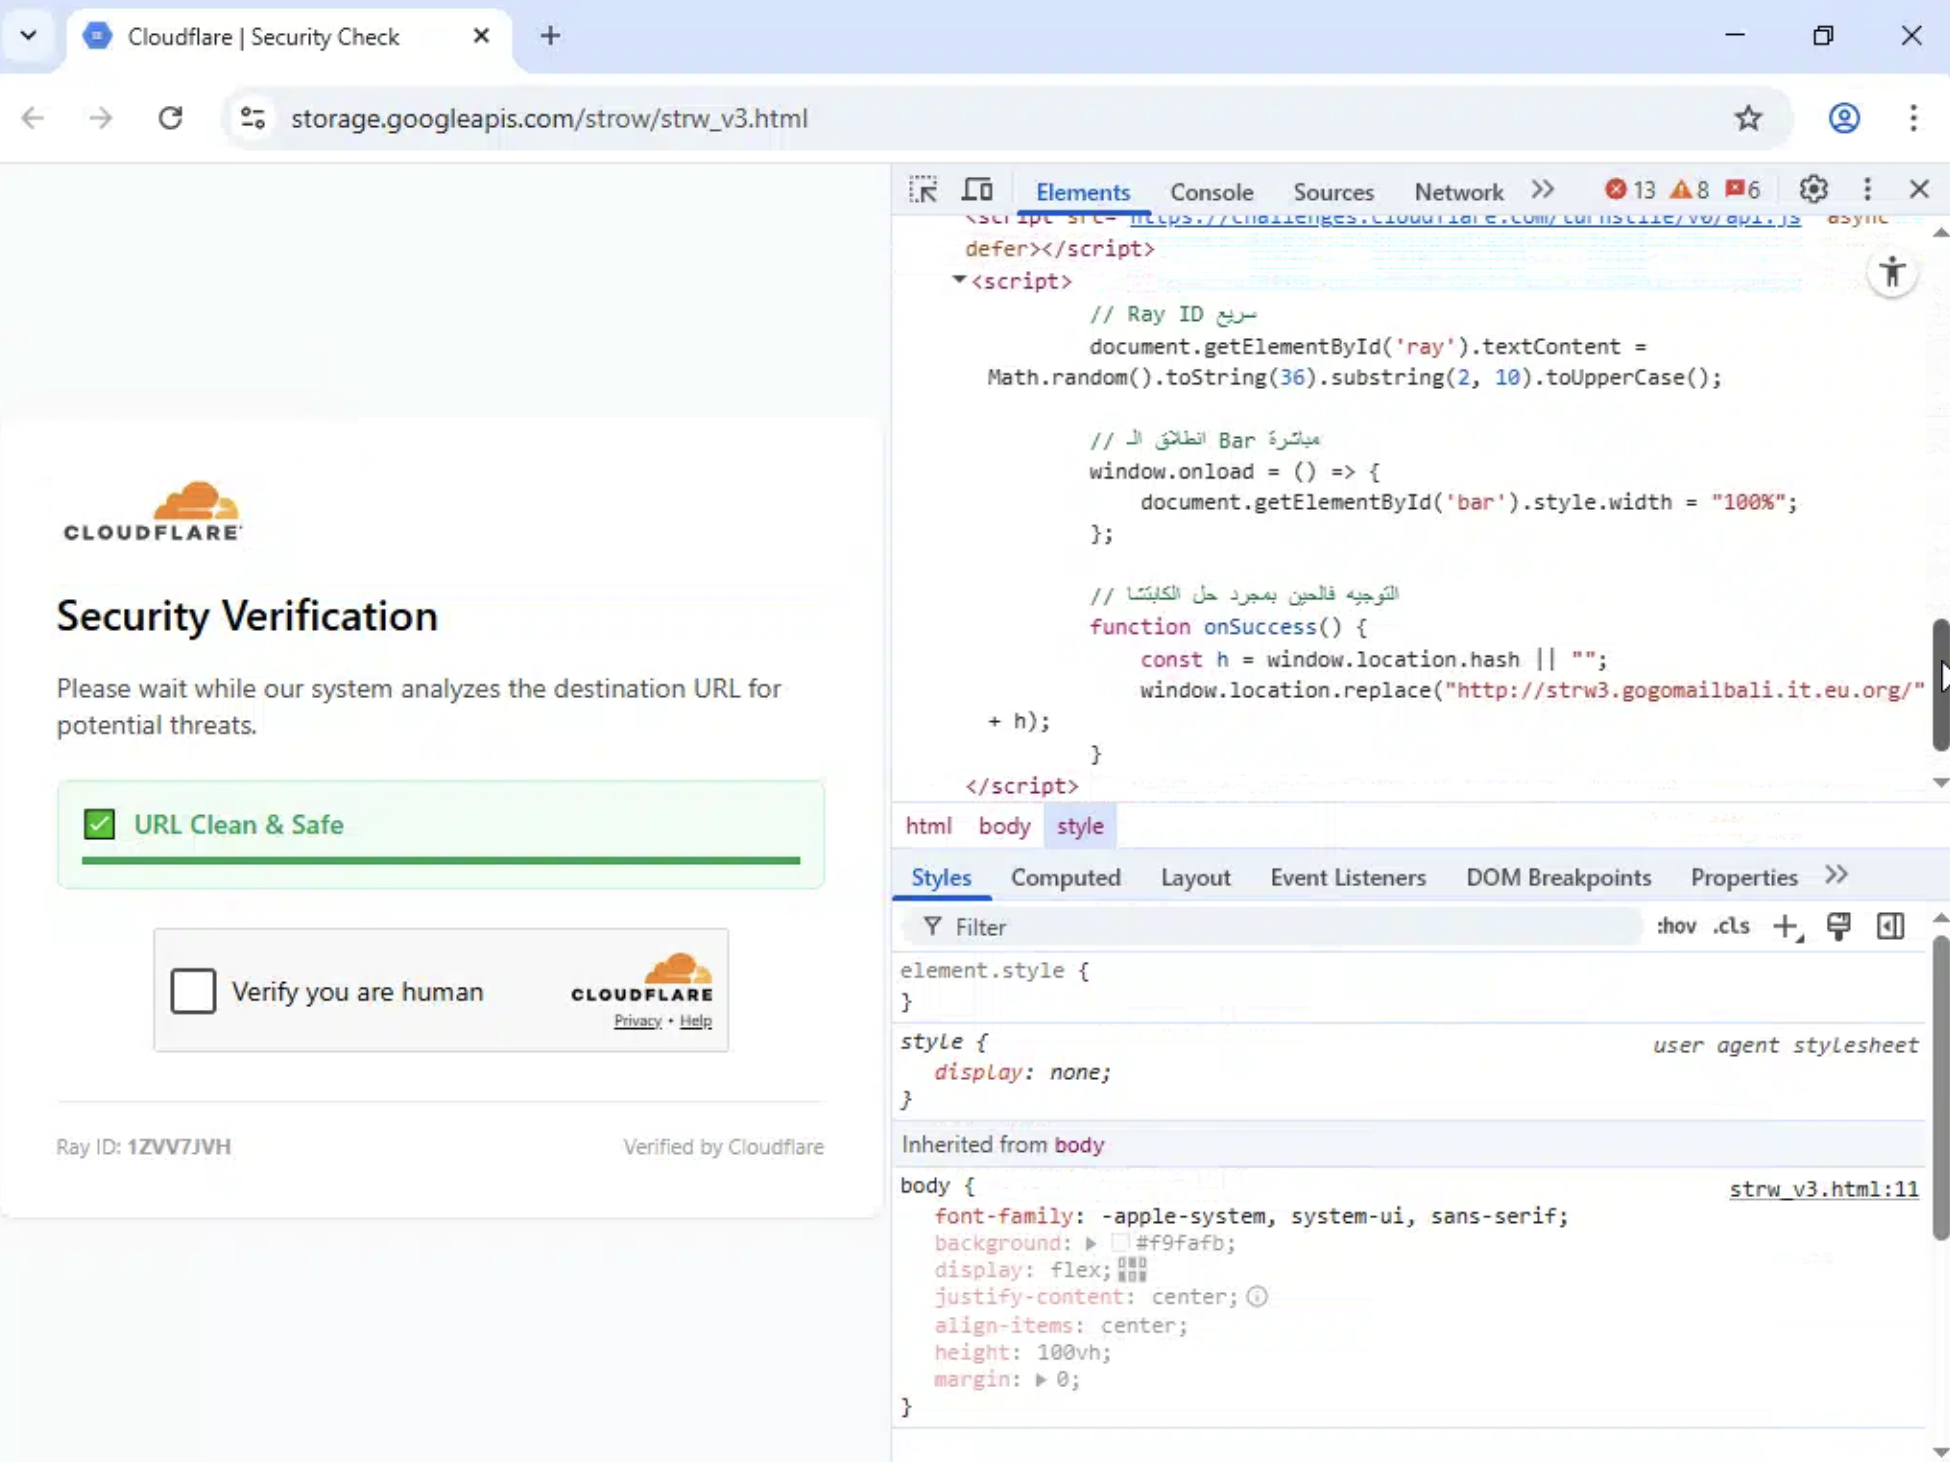
The Cloud Storage page is almost empty. Its job is to read whatever appears after #, preserve it, and forward the browser to a hard-coded IP over plain HTTP.

Browser developer tools showing the Cloud Storage redirect script

The fetched object served this script:

var tarcking_param = window.location.href.split('#')[1];
var srv_ip = "49.13.68.203";
if(!tarcking_param){
alert("please set tracking params!");
}else{
document.location.href = 'http://'+srv_ip+'/?'+tarcking_param;
}

The typo in tarcking_param is interesting, as AI rarely mispells!

Resulting redirect

Because the script appends the fragment value after /?, the original URL produces:

http://49.13.68.203/?Z289MSZzMT0yMjc1NTE2JnMyPTQzMDAwNzA1MyZzMz1HTEI=

After decoding the Base64 payload, the effective tracking values are:

go=1&s1=2275516&s2=430007053&s3=GLB

The first URL can carry tracking data after #, which is not sent to the server in the original HTTP request. Once JavaScript runs in the browser, the page reads that client-side fragment and turns it into a normal query-like value for the next hop.

Redirect host cover page and certificate

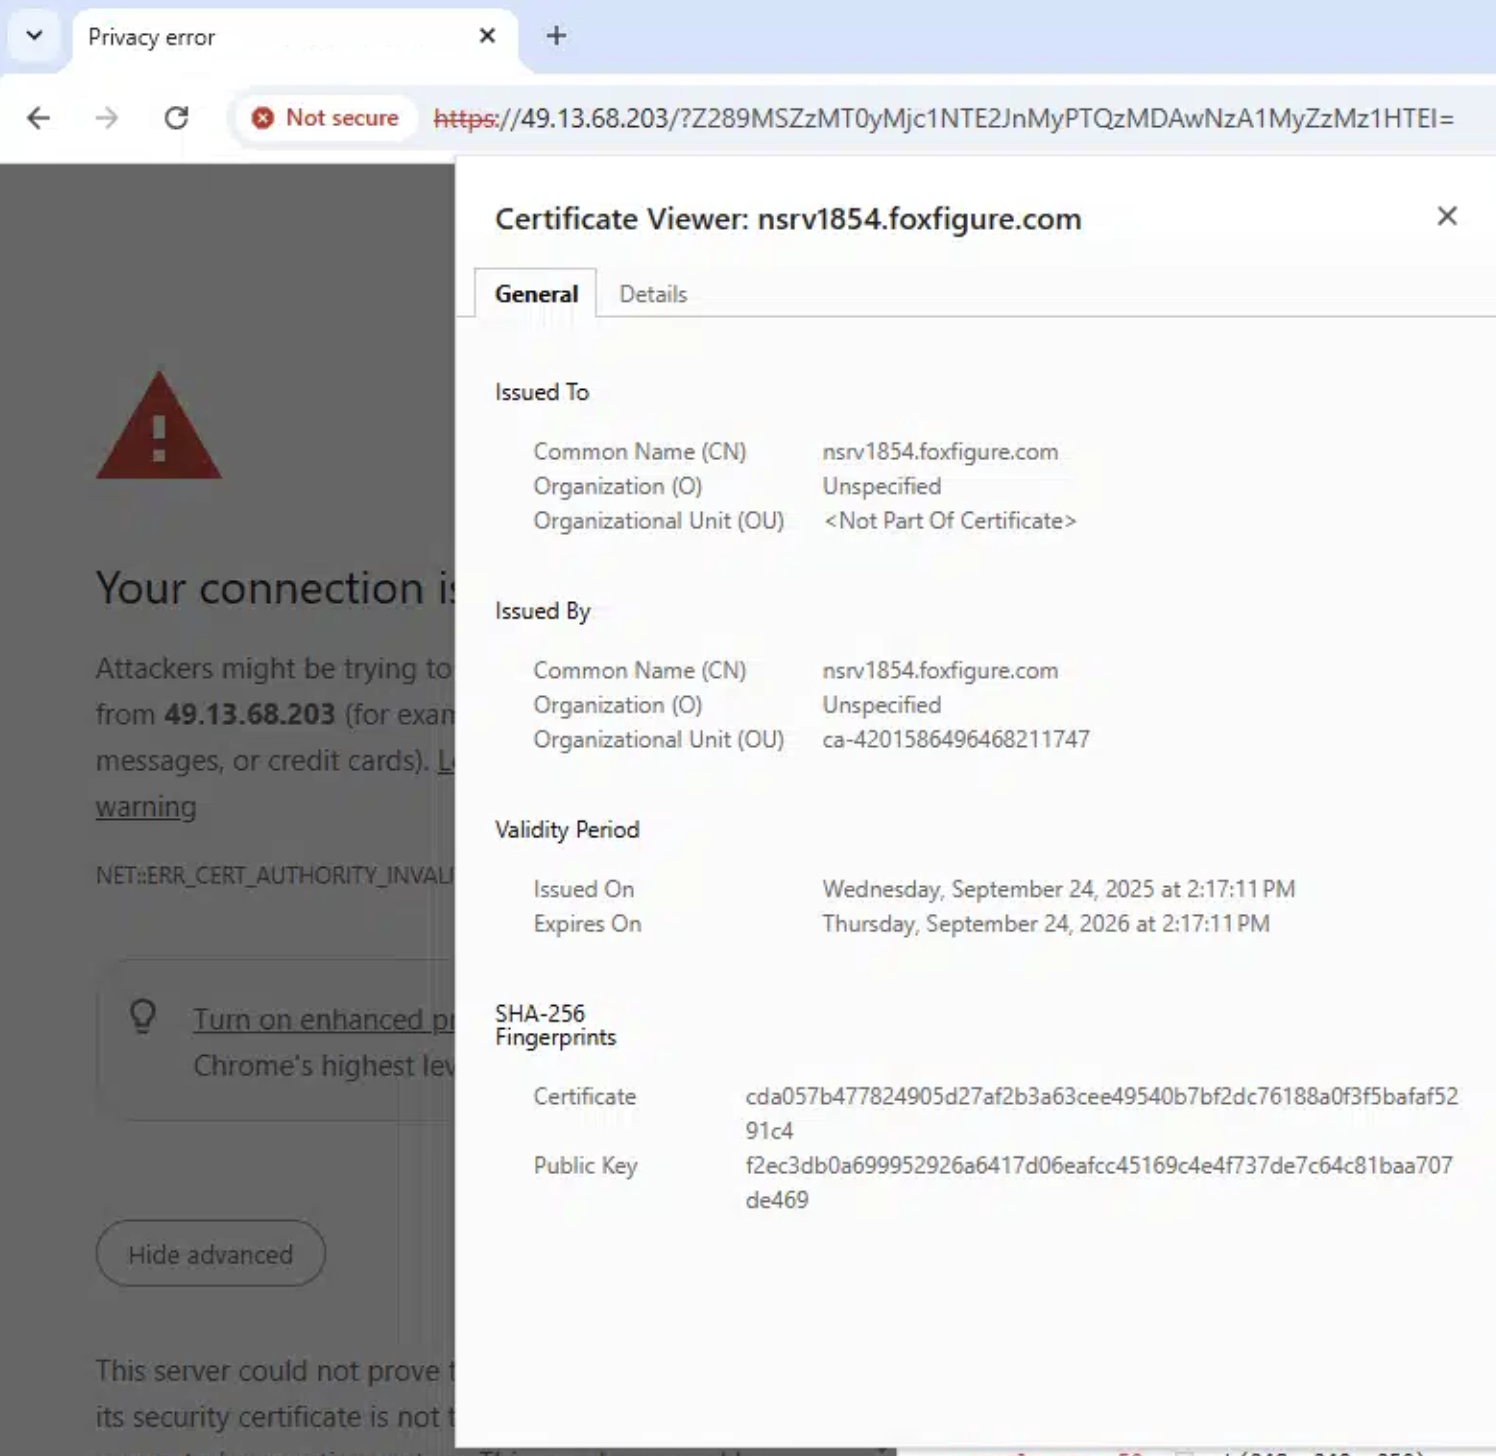
Browsing directly to the redirect IP over HTTPS produced a certificate warning. The certificate presented by 49.13.68.203 was not issued to the IP address; it identified:

Common Name: nsrv1854.foxfigure.com
Issued by: nsrv1854.foxfigure.com
Validity: September 24, 2025 to September 24, 2026
Chrome error: NET::ERR_CERT_AUTHORITY_INVALID

Certificate viewer showing nsrv1854.foxfigure.com certificate on 49.13.68.203

The observed SHA-256 certificate fingerprint was:

cda057b477824905d27af2b3a63cee49540b7bf2dc76188a0f3f5bafaf5291c4

The public key fingerprint shown in the browser was:

f2ec3db0a69952926a6417d06eafcc45169c4e4f737de7c64c81baa707de469

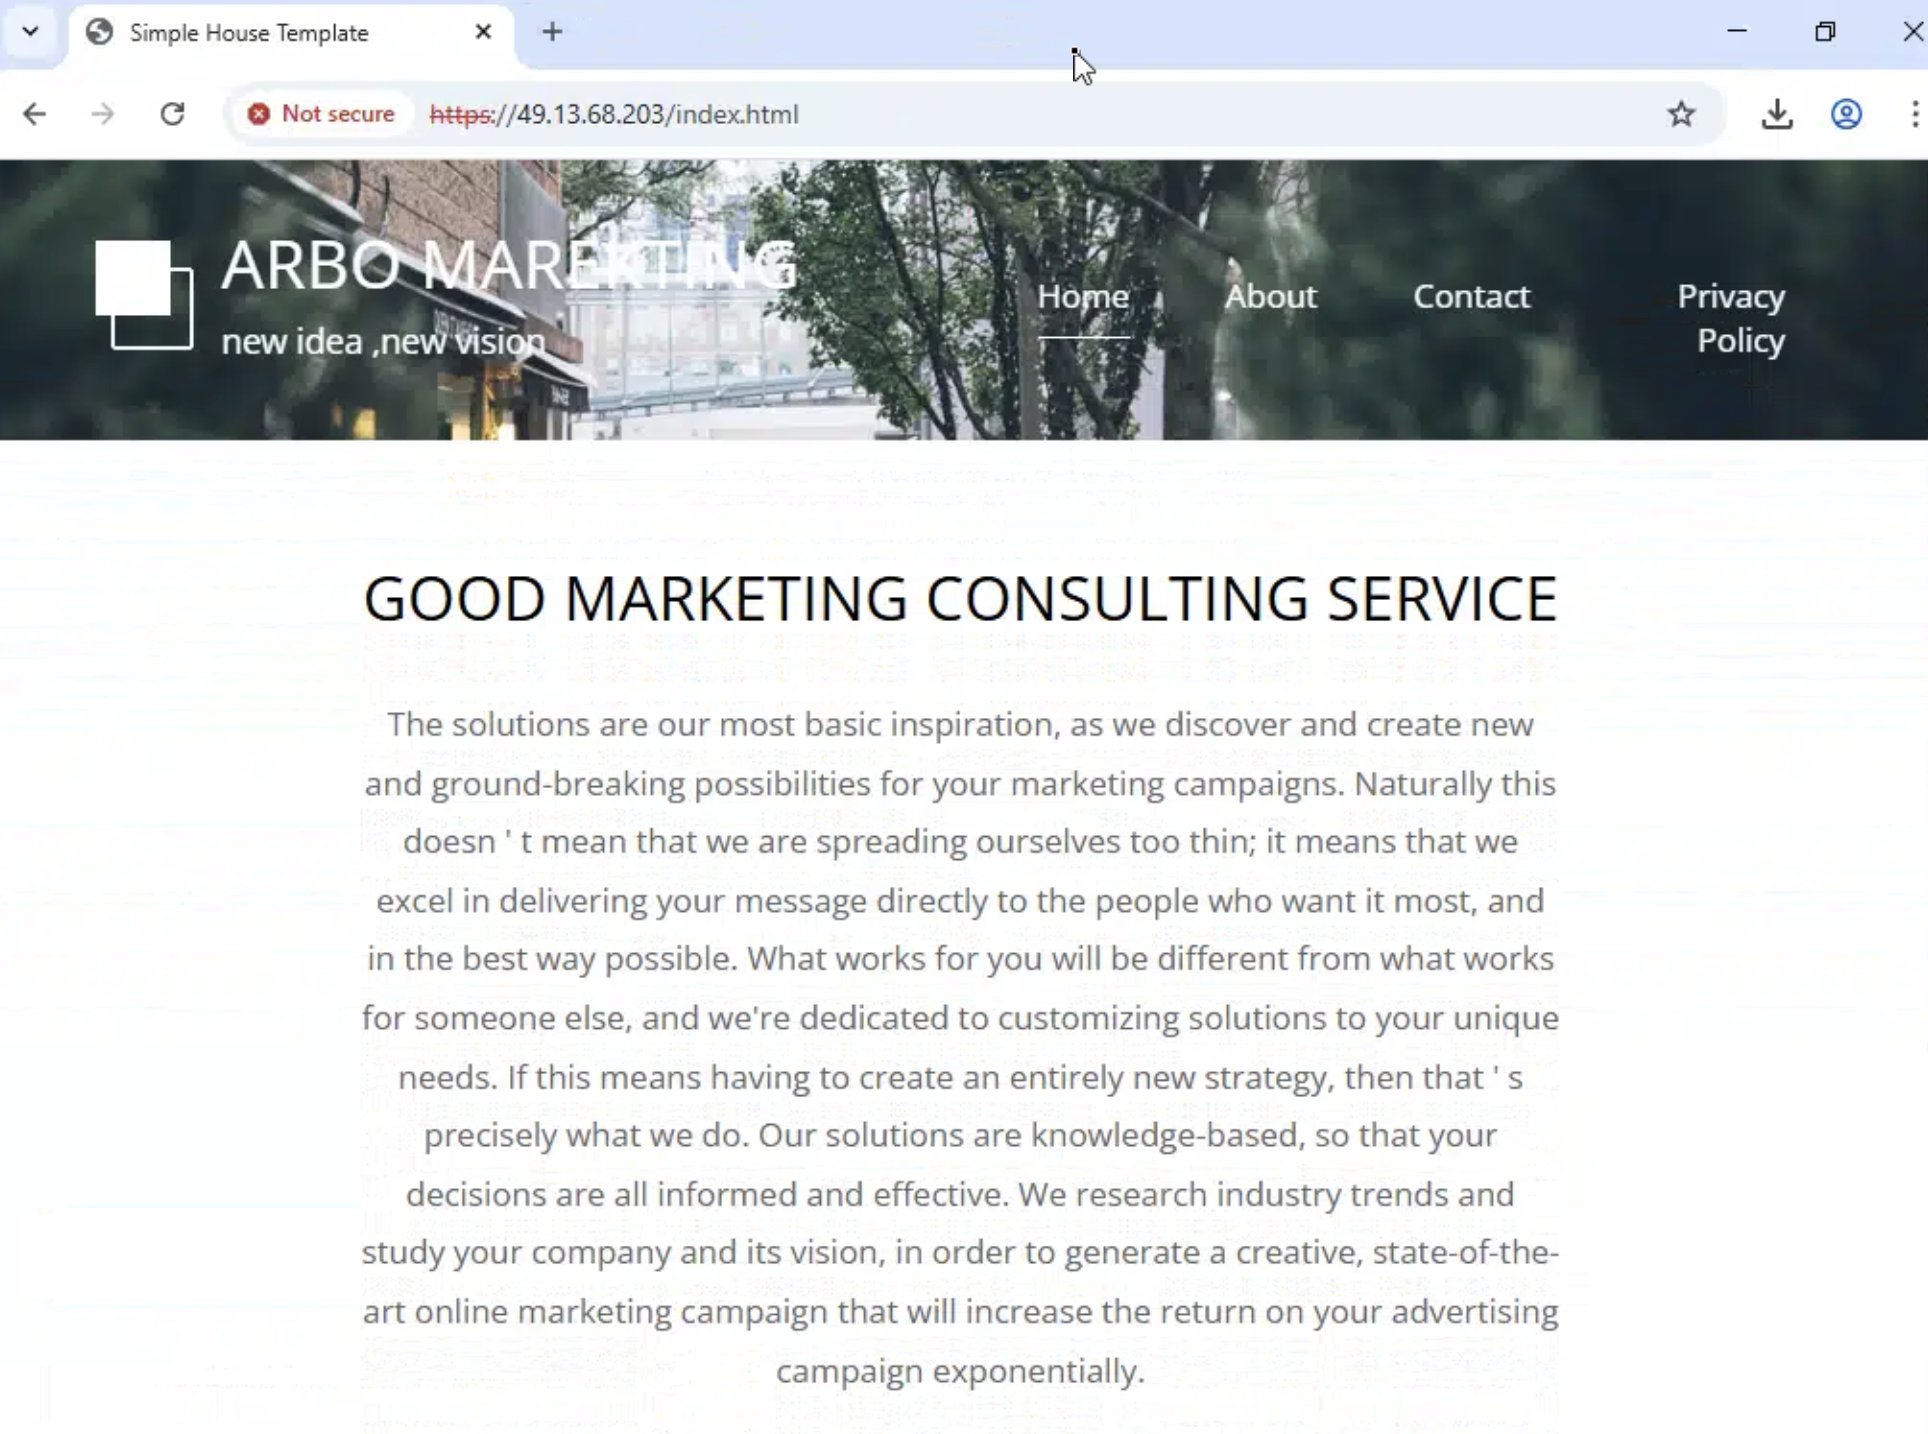
The same host also served a plain cover page at:

https://49.13.68.203/index.html

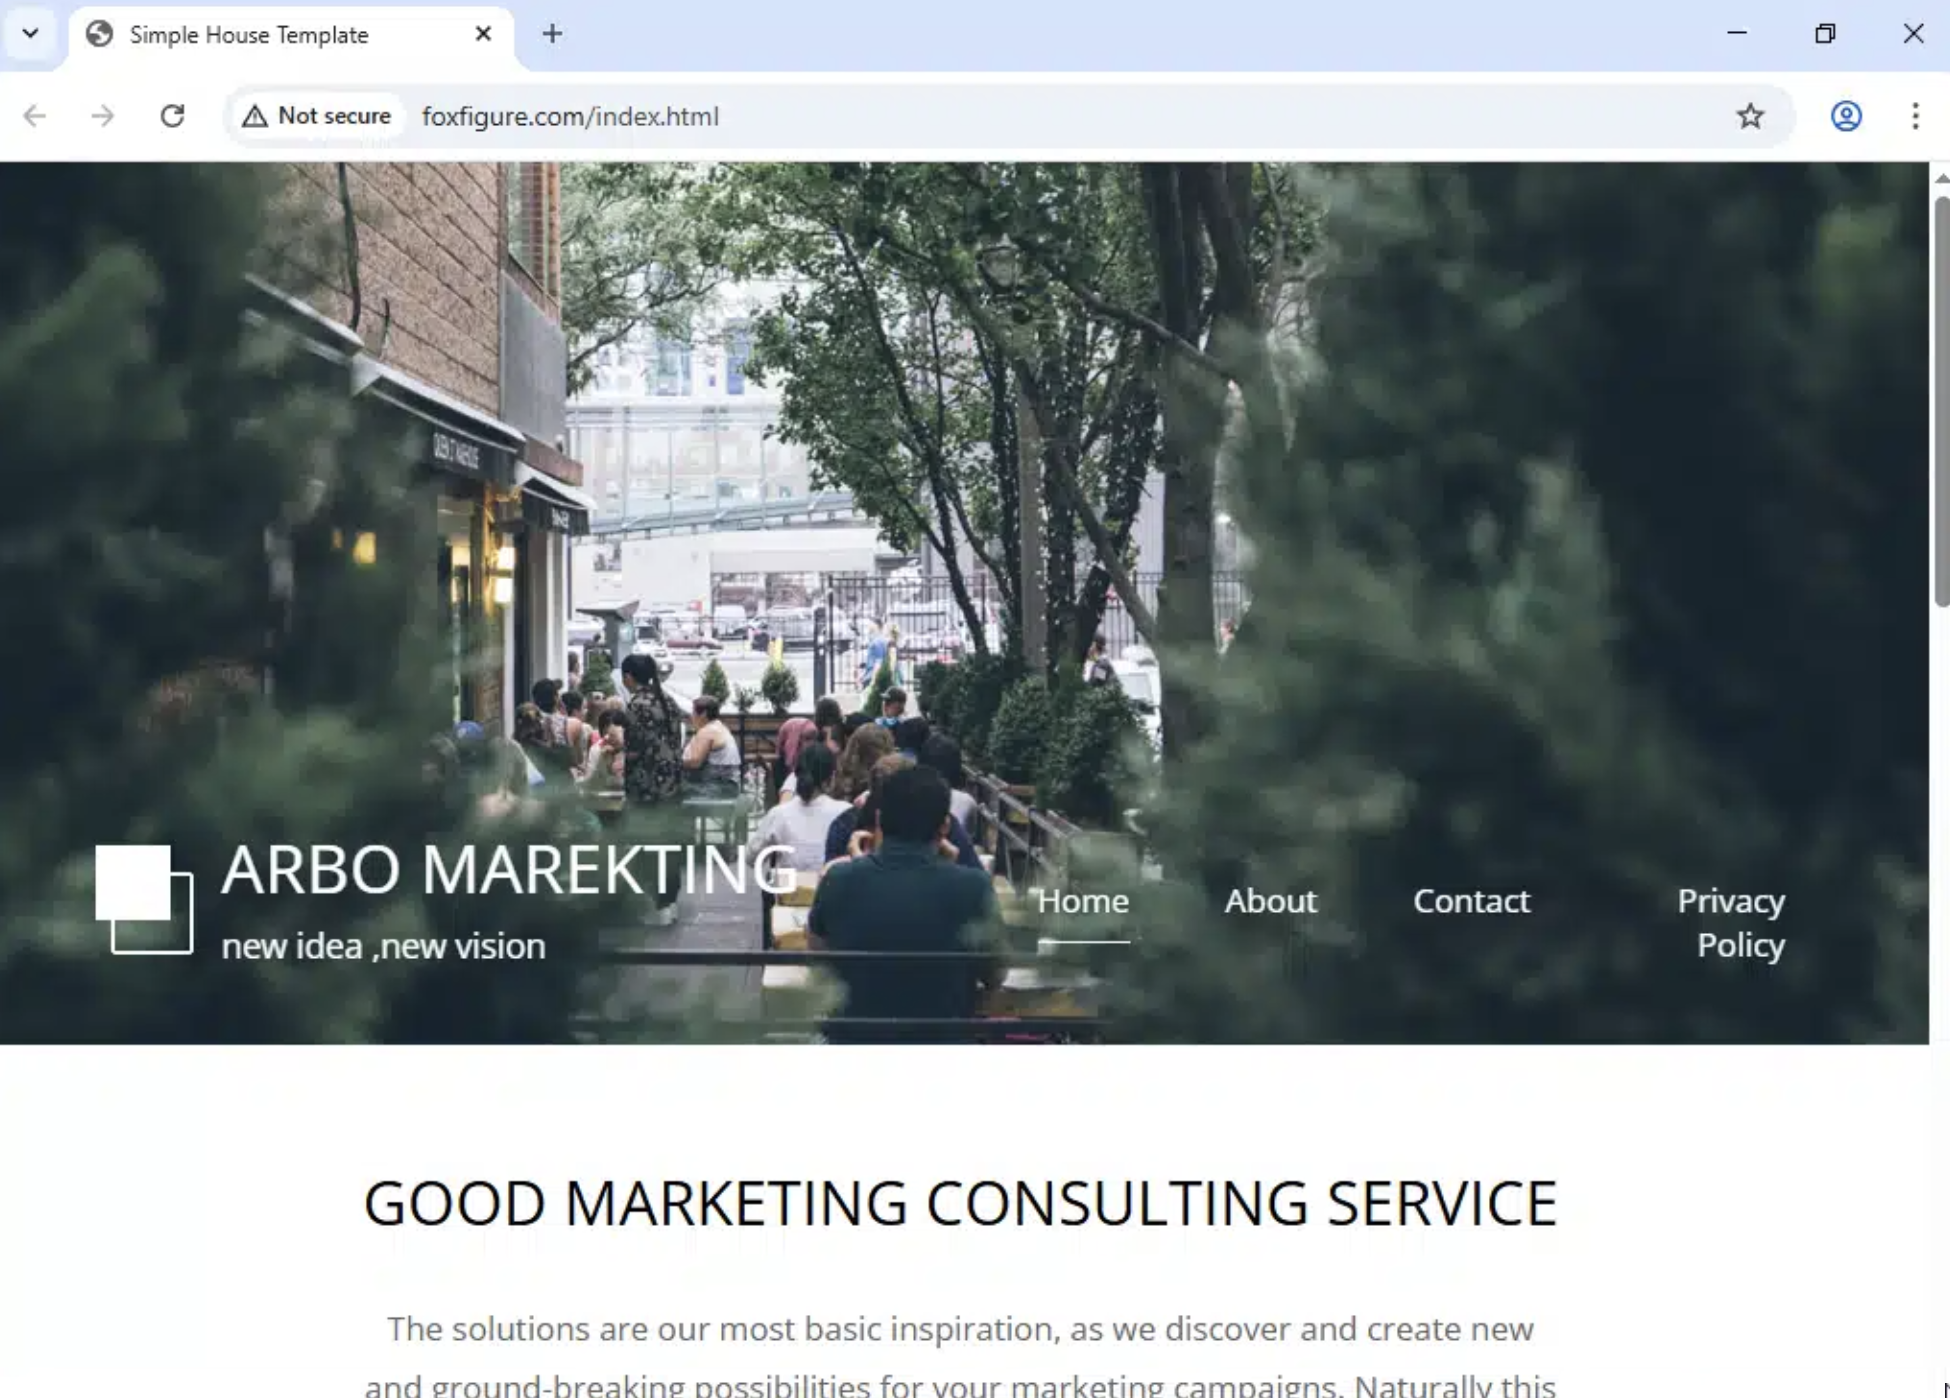
That page branded itself as:

ARBO MARKETING
new idea ,new vision
GOOD MARKETING CONSULTING SERVICE

ARBO MARKETING cover page served from the redirect IP

The certificate pivot also resolved back to the same marketing template. Visiting:

foxfigure.com/index.html

served another ARBO MARKETING page with the same title and visual layout:

ARBO MARKETING cover page served from foxfigure.com

IOCs

storage.googleapis.com/25kdhsale/NWBH25.html
49.13.68.203
nsrv1854.foxfigure.com
foxfigure.com
foxfigure.com/index.html
cda057b477824905d27af2b3a63cee49540b7bf2dc76188a0f3f5bafaf5291c4
f2ec3db0a69952926a6417d06eafcc45169c4e4f737de7c64c81baa707de469
ARBO MARKETING
vinekeymate.com
vinekeymate.com/o-qqgf-e81-226d3279736e0185769db1862f53e53d
91.99.29.100
hotnewscam.com
porqxyxml.com
POrqXyXml.com
lzmhneiktu7oayw784.pc8yosm64vt5bg7784.y4jfbahri016w87784.16niztwhjrk0cu9.hotnewscam.com
static.100.29.99.91.clients.your-server.de
return23203@lzmhneiktu7oayw784.pc8yosm64vt5bg7784.y4jfbahri016w87784.16niztwhjrk0cu9.hotnewscam.com

Detection Logic

IF
HTML contains hidden display-none blocks
AND hidden content mixes unrelated article prose, random strings, and copied email snippets
THEN
spam-filter evasion padding likely
IF
HTML object reads window.location.href.split('#')[1]
AND redirects to a hard-coded IP address over HTTP
THEN
fragment-handoff redirect behavior likely

Observations & Conclusions

  • SPF passed for the return-path infrastructure, but DMARC failed against the visible sender.
  • The message date appears to contain an unexpanded spam-kit template value.
  • The HTML includes a large hidden filler block for content-padding evasion.
  • The first-stage page is hosted on Google Cloud Storage.
  • CTA and unsubscribe tracking are carried in Base64-encoded fragments.
  • The unsubscribe branch redirects to vinekeymate.com and exposes campaign metadata in JSON.
  • The redirect IP presents an invalid certificate for nsrv1854.foxfigure.com.
  • The redirect IP also serves an ARBO MARKETING cover page at /index.html.
  • Client-side JavaScript converts the fragment into a redirect toward 49.13.68.203 (foxfigure).
  • The hard-coded IP redirect uses plain HTTP.
  • The misspelled tarcking_param variable is a small but useful clue.
Indicators of Compromise (IOCs)
IOCs (domains, IP addresses, files, hashes, etc.) from this analysis are available on GitHub.
View on GitHub →

Spam Tales: Claim Your Free Stanley Tool Set

· 6 min read

Overview

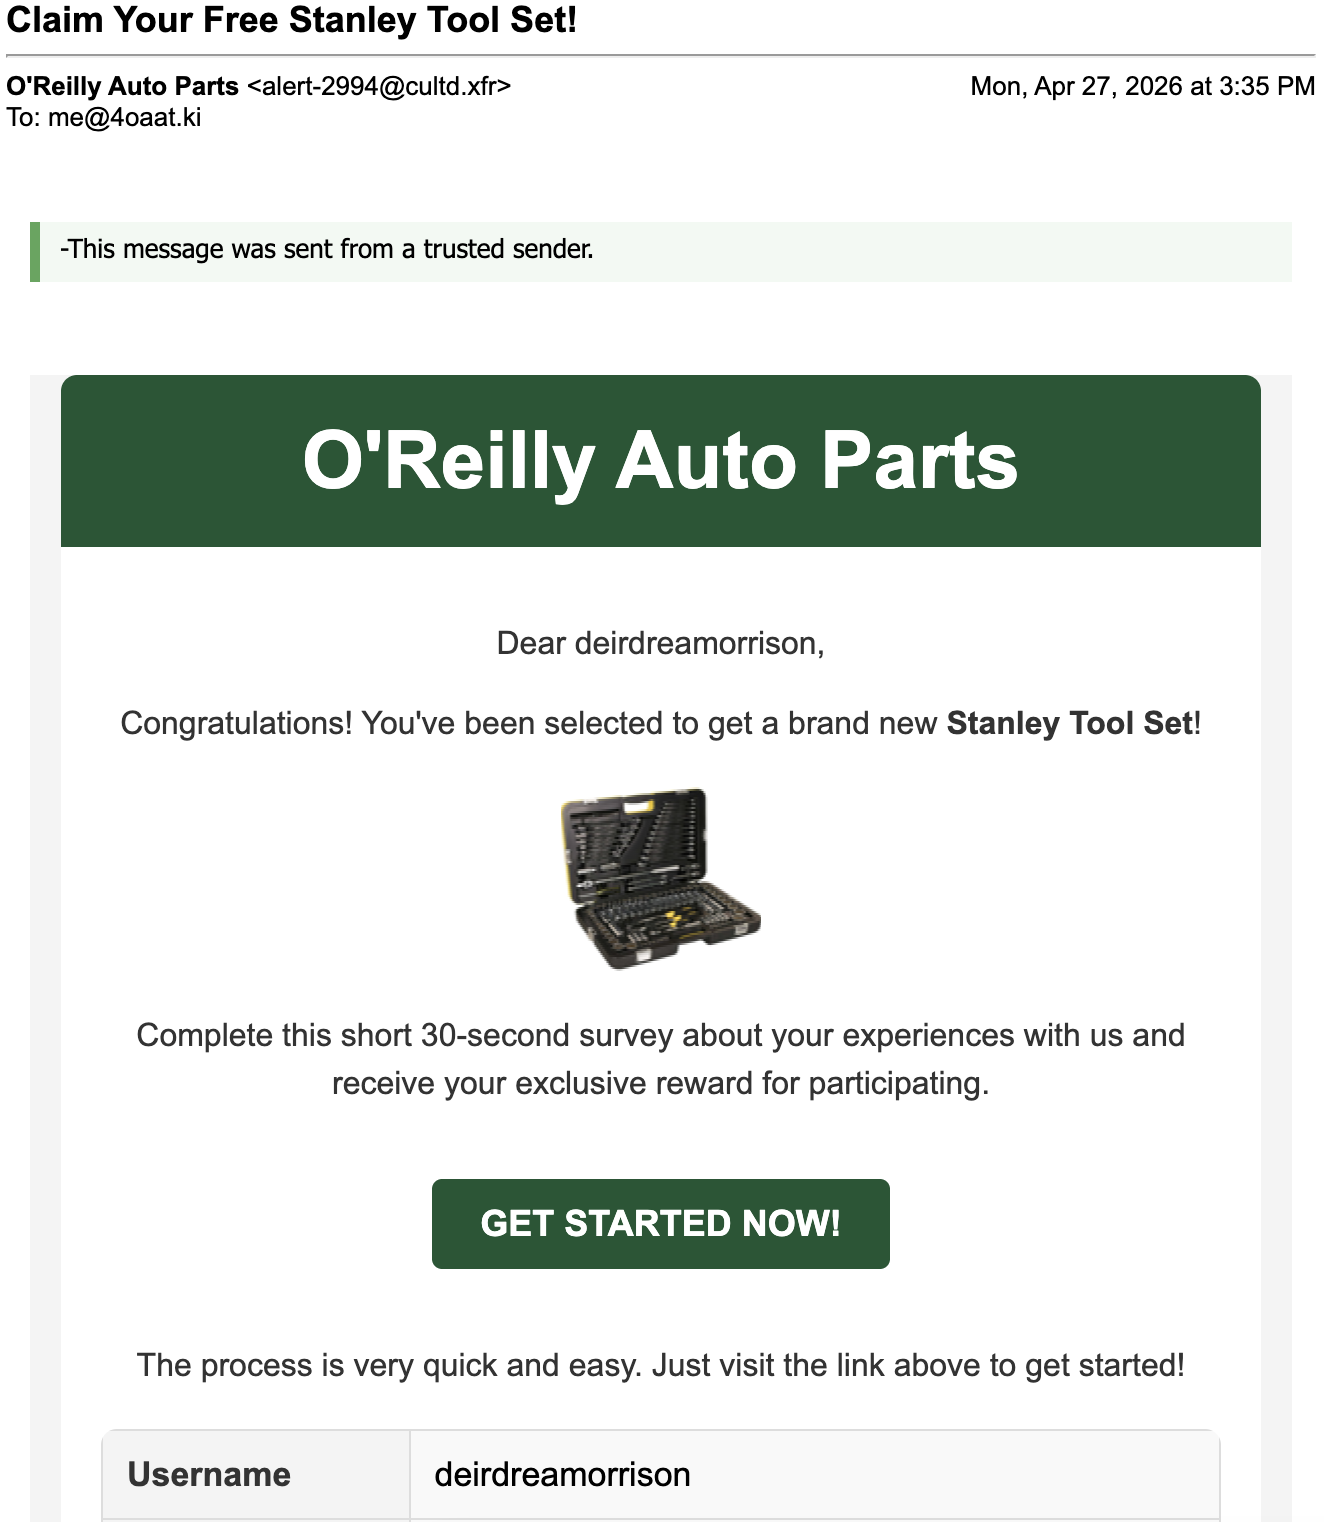
Sweet, a tool set!

image of a phishy tool set email

Methodology

For this type of email lure, I like to preserve a few layers separately:

  1. Capture the rendered email before interacting with any links.
  2. Review the sender, recipient, timestamps, and authentication results.
  3. Inspect the raw HTML for hidden text, tracking, encoding tricks, and unusual objects.
  4. Open the link in an isolated browser or sandbox.
  5. Record the first-hop domain, JavaScript redirects, and any visible URL parameters.
  6. Separate victim-specific fields from reusable campaign indicators.

Tools used

  • Email source view for MIME structure and hidden HTML content
  • Message authentication summary for SPF, DKIM, and DMARC results
  • Browser developer tools in an isolated environment (Browserling)
  • Manual IOC extraction from the lure, auth panel, and first-hop landing page

Email Authentication

The message presented itself as:

From: O'Reilly Auto Parts <[email protected]>
Subject: Claim Your Free Stanley Tool Set!
Created: Mon, Apr 27, 2026 at 3:35 PM

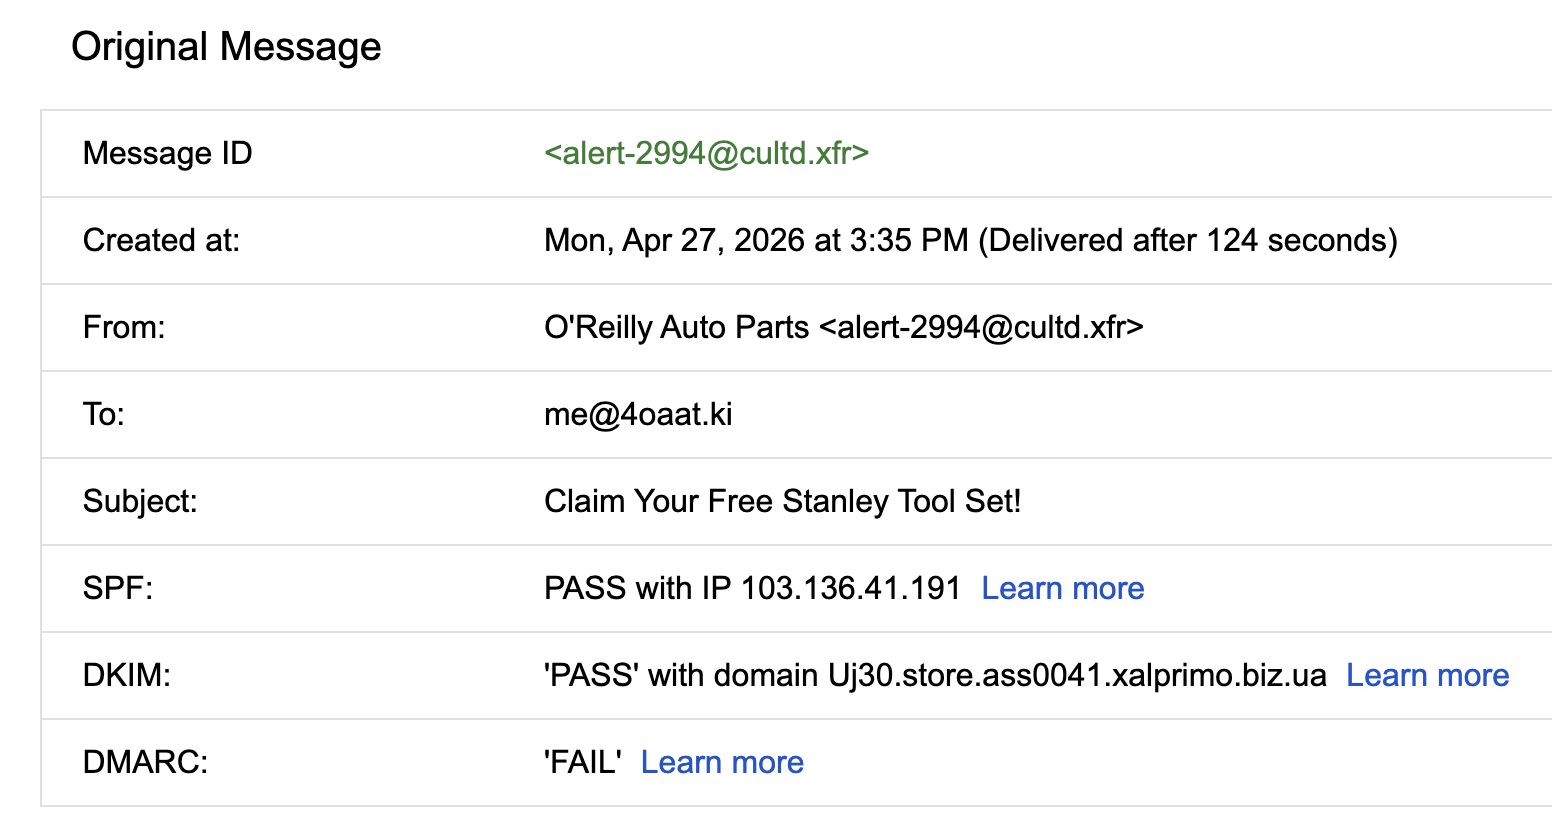
The authentication panel:

Original message authentication panel showing SPF pass, DKIM pass on an unrelated domain, and DMARC fail

Observed results:

SPF: PASS with IP 103.136.41.191
DKIM: PASS with domain Uj30.store.ass0041.xalprimo.biz.ua
DMARC: FAIL
tip

SPF and DKIM can pass individually while DMARC fails because DMARC also cares about alignment with the visible From domain. Here, the visible From domain was cultd.xfr, while DKIM aligned to an unrelated xalprimo.biz.ua subdomain.

Investigation

Lure structure

The lure uses a familiar reward-survey flow:

Claim your free Stanley Tool Set
Complete this short 30-second survey
Get started now
Reward status: Pending

The rendered body also claims that the message was sent from a trusted sender. That line is part of the lure's credibility play, not an authentication result to trust.

Hidden filler text

The HTML source included hidden content inside zero-height, zero-width, opacity-zero objects. The visible snippet begins with the trusted-sender language, then buries unrelated prose in the body.

Raw HTML showing hidden filler text inside zero-size objects

Redirect chain

The original link used a Google Cloud Storage object with campaign parameters placed after the fragment marker:

https://storage.googleapis.com/strow/strw_v3.html#?act=cl&pid=19298_md&uid=4&vid=849710&ofid=118&lid=486&cid=534301

That page presented a fake Cloudflare-style security check and used a Turnstile callback to preserve the fragment while moving the browser to the next host:

function onSuccess() {
const h = window.location.hash || "";
window.location.replace("http://strw3.gogomailbali.it.eu.org/" + h);
}

That produces:

http://strw3.gogomailbali.it.eu.org/#?act=cl&pid=19298_md&uid=4&vid=849710&ofid=118&lid=486&cid=534301

Fake Cloudflare gate

The Cloud Storage page visually imitates a Cloudflare security check:

fake captcha and redirect

Under the hood, it loads Cloudflare's Turnstile API and embeds a Turnstile widget with a reusable-looking site key:

<script src="https://challenges.cloudflare.com/turnstile/v0/api.js" async defer></script>
<div class="cf-turnstile" data-sitekey="0x4AAAAAAAWyD8kIgIxaOYq5" data-callback="onSuccess"></div>

The page also generates a fake-looking Ray ID client-side:

document.getElementById('ray').textContent =
Math.random().toString(36).substring(2, 10).toUpperCase();

That combination is a nice social-engineering layer: it borrows the look of a known security brand, presents the URL as already "clean," then requires interaction before forwarding the victim to the next campaign host.

info

One funny-but-benign artifact here: Cloudflare's Turnstile API script at:

https://challenges.cloudflare.com/turnstile/v0/api.js

contains logic that sends a watchdog-style message like:

{ event: "meow", source: "cloudflare-challenge", widgetId: ... }

cloudflare meow

and then handles a response event:

case "food":
...

So meow / food appears to be Cloudflare's internal parent-frame to challenge-iframe heartbeat/ack messaging. Delightfully silly, but not suspicious by itself.

Landing page behavior

The second-stage URL observed in the sandbox used:

strw3.gogomailbali.it.eu.org

The page itself was nearly empty except for a script that rewrites fragment-marked URLs into normal path separators:

Browser developer tools showing a redirect-normalizing script on the first-hop page

The visible script logic checks whether the current URL contains #, then replaces escaped and unescaped hash markers with /.

In practical terms, this lets the actor place routing data after a URL fragment and then normalize it client-side after the page loads. It also makes the original link a little less straightforward for static URL parsers that do not execute JavaScript.

For this lure, the normalized next URL is:

http://strw3.gogomailbali.it.eu.org/?act=cl&pid=19298_md&uid=4&vid=849710&ofid=118&lid=486&cid=534301

And then I lost the redirect trail, drat!

Earlier-month pivot

A related Hybrid Analysis submission from April 11, 2026 shows the same storage.googleapis.com/strow/strw_v3.html object, fake CAPTCHA/security verification behavior, and redirect to strw3.gogomailbali.it.eu.org:

That earlier sample used an encoded fragment:

https://storage.googleapis.com/strow/strw_v3.html?#%3Fact%3Dcl%26pid%3D18125_md%26uid%3D4%26vid%3D650852%26ofid%3D414%26lid%3D348%26cid%3D989216

After the Cloud Storage page redirected to strw3, the strw3 fragment-rewrite logic produced a path beginning with %3F instead of a normal query string:

http://strw3.gogomailbali.it.eu.org/%3Fact%3Dcl%26pid%3D18125_md%26uid%3D4%26vid%3D650852%26ofid%3D414%26lid%3D348%26cid%3D989216

Hybrid Analysis observed that encoded-path request returning 404 Not Found. That makes the newer literal #?act=... version worth noting: it normalizes into a clean query string instead of an encoded path.

Hybrid Analysis also matched the HTML against fake CAPTCHA social-engineering behavior. The relevant pattern was the combination of Cloudflare-branded verification text, Turnstile challenge markup, and the redirect callback:

Detected social engineering methods via fake CAPTCHA site in HTML
window.location.replace("http://strw3.gogomailbali.it.eu.org/" + h)
Security Verification
Cloudflare | Security Check

The embedded challenge script includes normal Cloudflare challenge terms such as cloudflare-challenge, turnstile_timeout, turnstile_expired, invalid_sitekey, and unsupported_browser. Those strings are not malicious on their own, but in this case they appear inside an attacker-controlled gate whose success callback redirects to unrelated HTTP infrastructure.

IOCs

cultd.xfr
103.136.41.191
ass0041.xalprimo.biz.ua
gogomailbali.it.eu.org
56be8f22434065af1080d922e24ea95d8beb1f967d86b346f01651ca28eb638a

Detection Logic

IF
message display name impersonates a known brand
AND DMARC fails
AND DKIM passes with a domain unrelated to the visible From domain
THEN
brand impersonation or spoofed reward lure likely
IF
HTML contains hidden zero-size or opacity-zero text blocks
THEN
spam-filter evasion likely
IF
page imitates Cloudflare security verification
AND callback redirects to an unrelated HTTP domain using window.location.hash
THEN
fake CAPTCHA gate for phishing redirect likely

Observations & Conclusions

  1. The social engineering is a simple survey-for-reward offer.
  2. The sender identity imitates a recognizable retail brand.
  3. The authentication results show partial pass signals but failed domain alignment.
  4. The HTML includes hidden filler text to muddy content-based filtering.
  5. The first stage uses a fake Cloudflare verification page hosted from Google Cloud Storage.
  6. The second stage uses JavaScript to normalize a fragment-heavy tracking URL.
  7. An April 11 sandbox sample shows the same hosted HTML object and redirect host - I'm not special, boo hoo!
Indicators of Compromise (IOCs)
IOCs (domains, IP addresses, files, hashes, etc.) from this analysis are available on GitHub.
View on GitHub →