Spam Tales: Business Request, Pharma Front

Overview
A tiny business-proposal, how quaint!
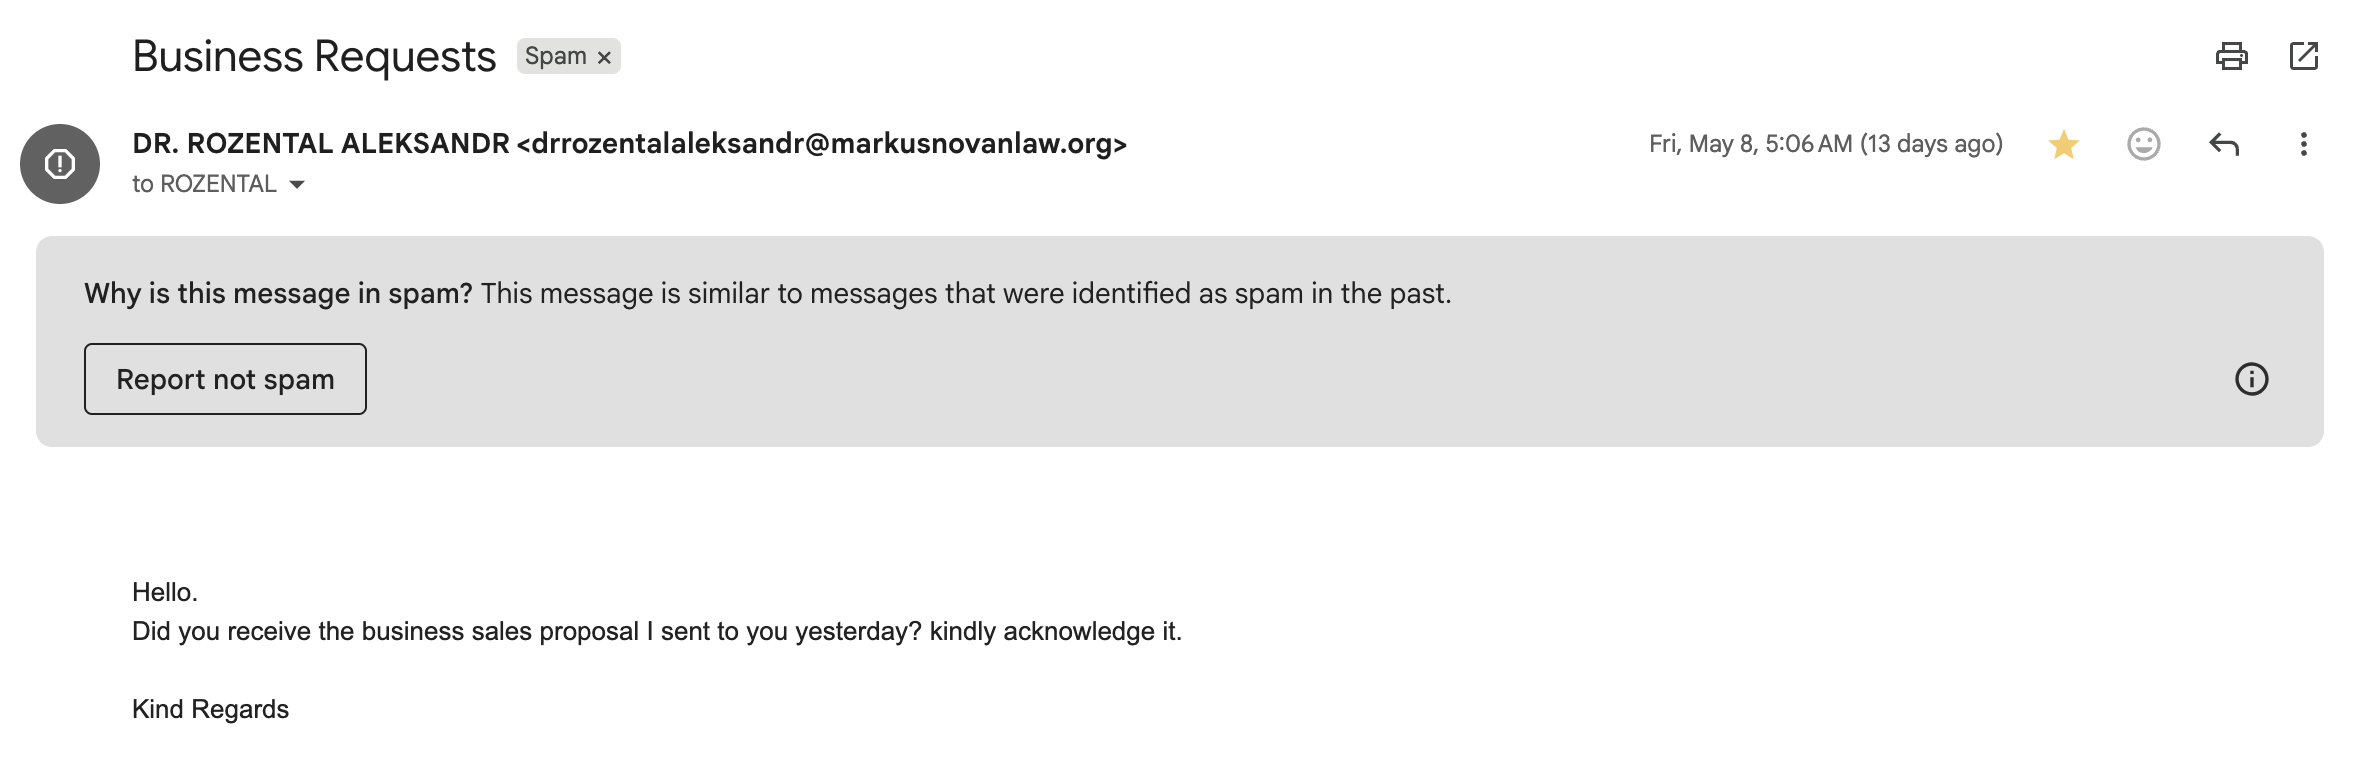
Hello.
Did you receive the business sales proposal I sent to you yesterday? kindly acknowledge it.

Kind Regards
Short, bland, no attachment, no link - just enough to make someone reply with "what proposal?"
Methodology
For this lure, I treated the message like a reply-chain starter rather than a link-delivery sample:
- Review the raw headers and Gmail authentication results.
- Separate mail authentication from sender legitimacy.
- Pivot on the
Reply-Todomain instead of only the visibleFrom. - Review passive DNS, certificate SANs, and visible web content.
- Compare the fake business fronts for cloned assets, source comments, and contact reuse.
- Check exposed mail-hosting surfaces like autoconfig, autodiscover, webmail, cPanel, and WHM.
- Keep hosting IPs in the background unless they explain a pivot.
Tools used
- Gmail message source and rendered-message view
- VirusTotal domain, certificate, and community graph pivots
- AbuseIPDB for mail-infrastructure reputation context
- Google search for indexed clone pages and reused contact strings
- Browser developer tools for source comments and visible hosting panels
dig,curl,openssl, and light TCP reachability checks for DNS, TLS, and service exposure
Investigation
The lure
The message presented itself as:
From: "DR. ROZENTAL ALEKSANDR" <[email protected]>
Subject: Business Requests
Reply-To: [email protected]
To: "DR. ROZENTAL ALEKSANDR" <[email protected]>
Authentication looked good:
SPF:   PASS
DKIM:  PASS for markusnovanlaw.org
DMARC: PASS with policy p=NONE
But, authenticated mail can still be bad mail. SPF, DKIM, and DMARC all passed for the sender domain, and Gmail still shoved it into spam because the rest of the message looked like spam it had seen before.
The more useful tell was the identity split:
Visible sender: markusnovanlaw.org
Reply-To:       saipoveldar.com
SMTP residue:   denpharmsltd.com
The message used a law/doctor sender identity, but replies were directed into a different domain entirely.
The sender domain
Browsing to markusnovanlaw.org showed a default CyberPanel installation page:
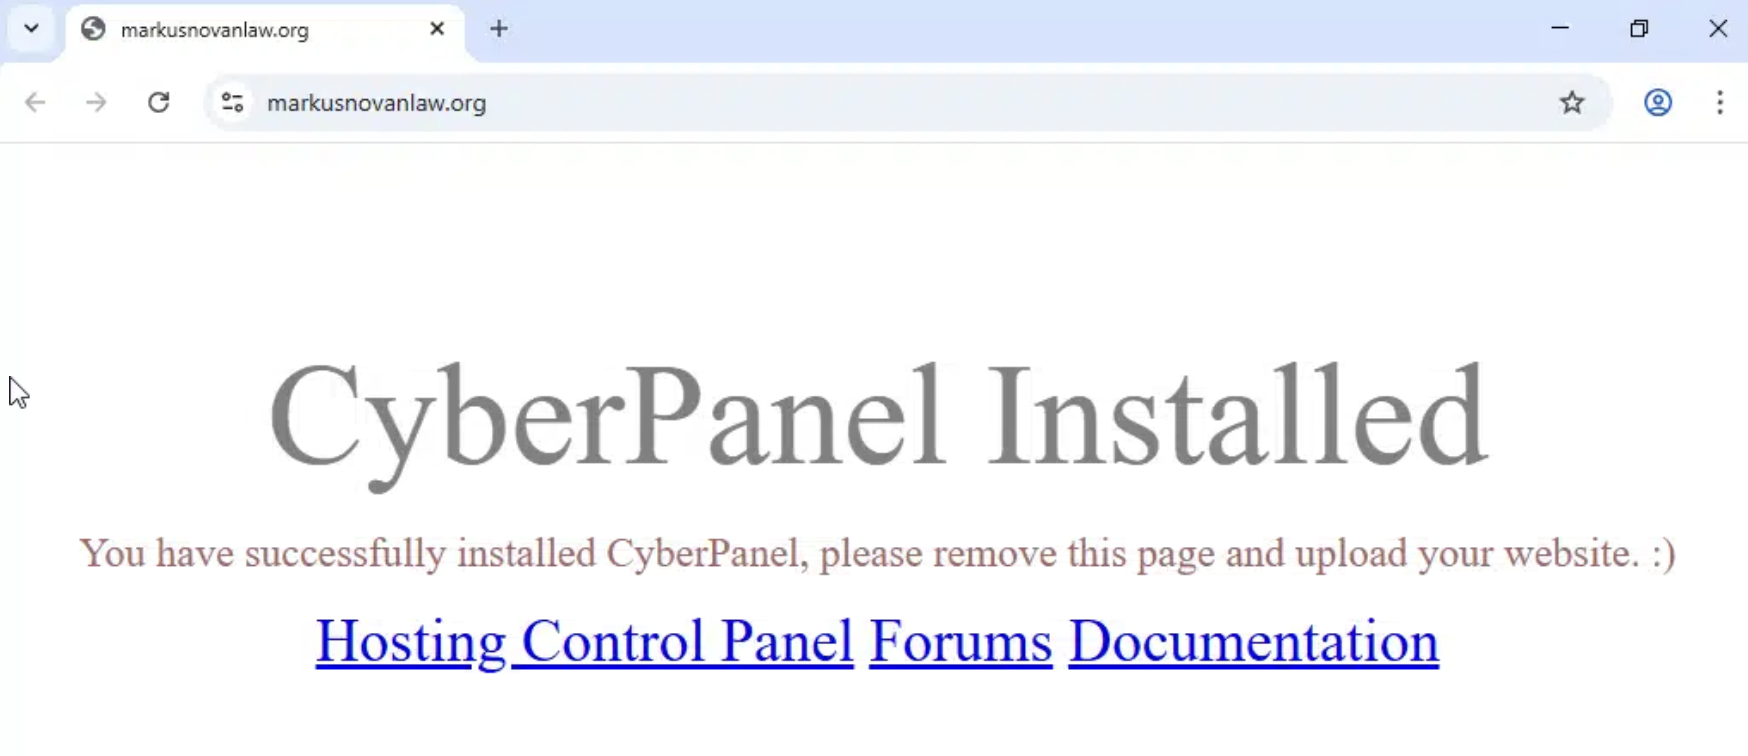
CyberPanel Installed
You have successfully installed CyberPanel, please remove this page and upload your website. :)
So the domain could authenticate mail, but the public site was just a default panel page. Not exactly a confidence builder!
The mail path also exposed an older server identity:
Received: from denpharmsltd.com (markusnovanlaw.org [...])
AbuseIPDB history tied that same SMTP identity to prior spam reports. VirusTotal passive DNS also showed denpharmsltd.com in the same mail-hosting neighborhood before markusnovanlaw.org appeared.
The reply-to domain
The Reply-To domain, saipoveldar.com, did not present as Saipov Eldar, law, or anything resembling the sender. It was pharma instead.
It served a site branded as:
KOVDACK PHARMA
The same content also appeared through kovdackpharmltd.com. A related domain, noozkackpharmaltd.com, used the same site structure, same hero text, same product categories, same Cyprus location story, and the same overall visual template.
The shared hero copy:
When it comes to pharmaceuticals,
patients come first.
The repeated business framing:
Kovdack Pharmaceuticals LTD
Noozkack Pharmaceuticals LTD
Movzen Pharmaceuticals LTD
Dooxweck Pharmaceuticals LTD
The source comment
The best artifact was sitting in the page source:
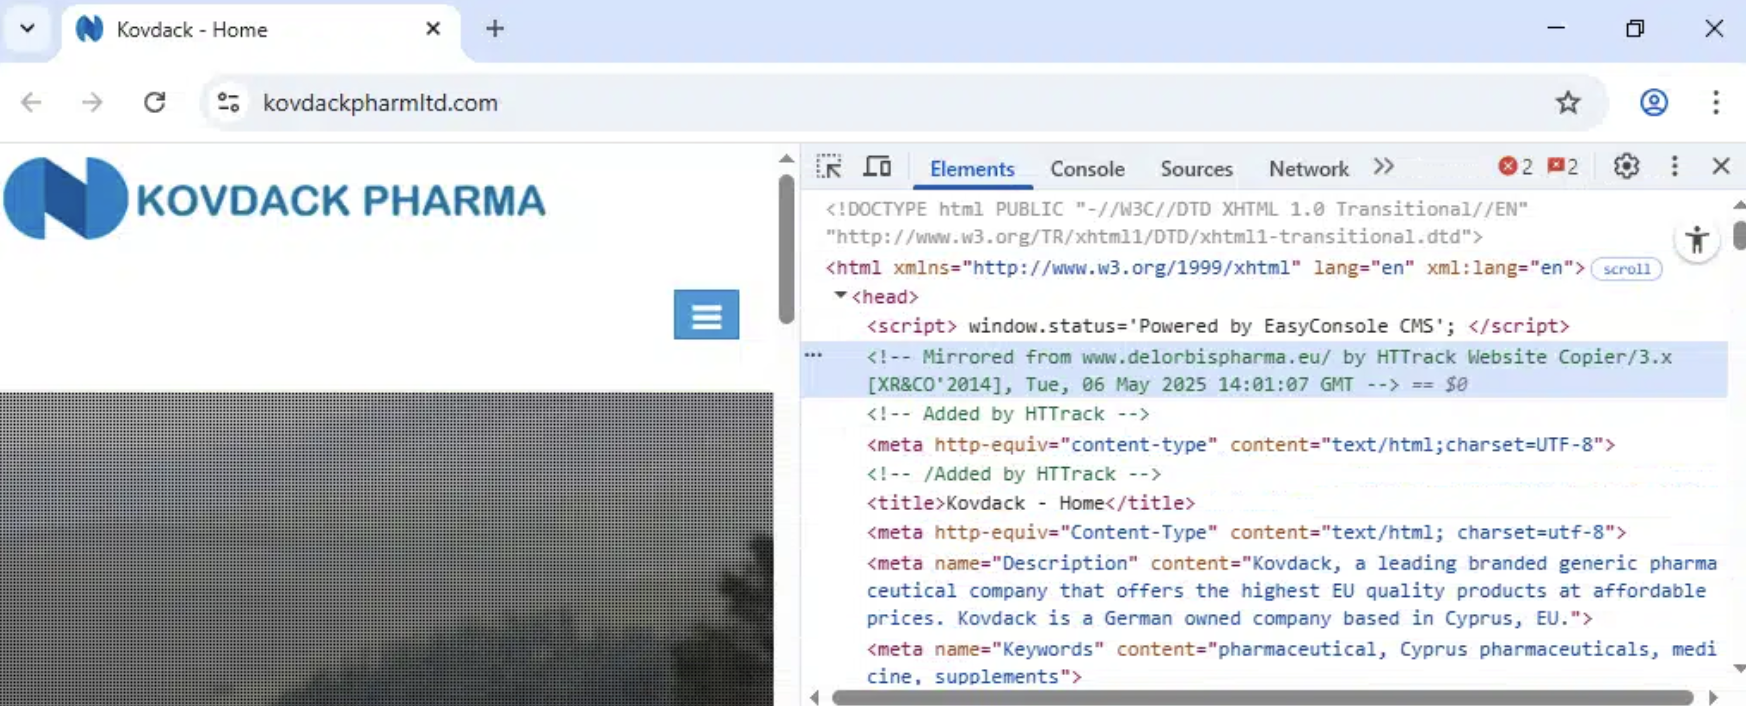
<!-- Mirrored from www.delorbispharma.eu/ by HTTrack Website Copier/3.x
[XR&CO'2014], Tue, 06 May 2025 14:01:07 GMT -->
The copied pages also retained:
window.status='Powered by EasyConsole CMS';
So the fake pharma fronts were not lovingly handcrafted. They appear to be HTTrack mirrors of www.delorbispharma.eu, with brand names, emails, street numbers, and phone numbers swapped.
More clone brands surfaced
Search and certificate pivots expanded the cluster:
kovdackpharmltd.com
noozkackpharmaltd.com
movzenpharmltd.com
dooxweckpharmaltd.com
saipoveldar.com
The phone and persona reuse made the cluster easier to see:
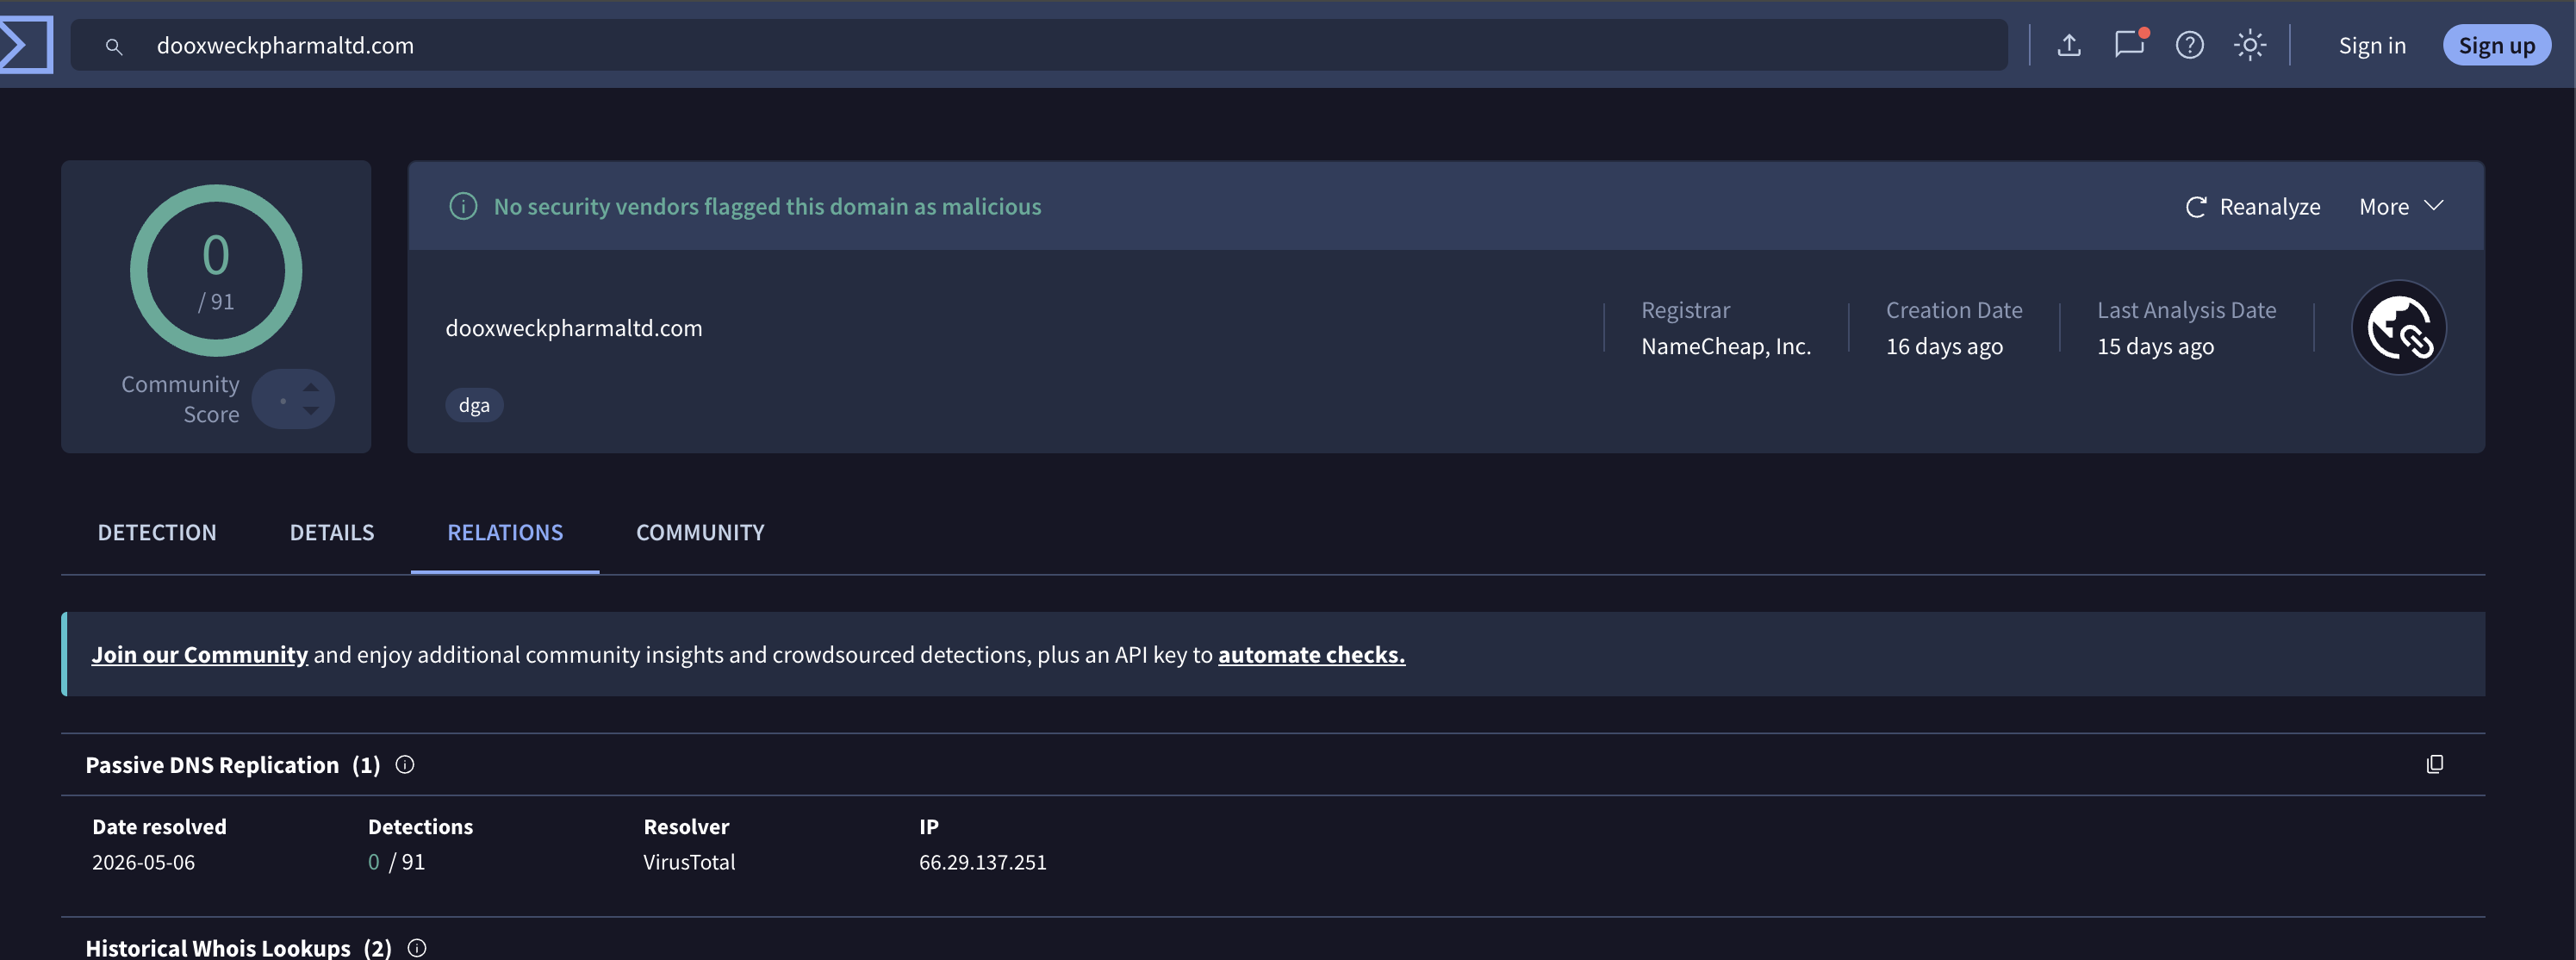
The original email used the rozentalaleksandr persona. The fake pharma layer reused that name on dooxweckpharmaltd.com.
Search results for dooxweckpharmaltd.com showed the same cloned pharma shape:
Certificate SANs exposed the staging pattern
Certificate pivots connect the fake pharma fronts. One certificate for the Kovdack/Noozkack/Saipoveldar cluster included:
*.kovdackpharmltd.com
*.noozkackpharmaltd.com
*.saipoveldar.com
kovdackpharmltd.com
noozkackpharmaltd.com
saipoveldar.com
www.kovdackpharmltd.com.saipoveldar.com
www.noozkackpharmaltd.com.saipoveldar.com
And, weirdly:
*.com.saipoveldar.com
That last one looked like a generated or sloppy namespace artifact rather than an active wildcard. Random names under that pattern did not resolve when I checked, but the named nested hosts were live and served the cloned pharma pages.
Another cluster branch used:
movzenpharmltd.com.cndlogisticsid.com
www.movzenpharmltd.com.cndlogisticsid.com
Those were also live. They served the Movzen pharma clone under a domain that otherwise presented as an Indonesian logistics company. Sure. Why should one fake business vertical have all the fun?
ViewDNS had more of the same under cndlogisticsid.com:
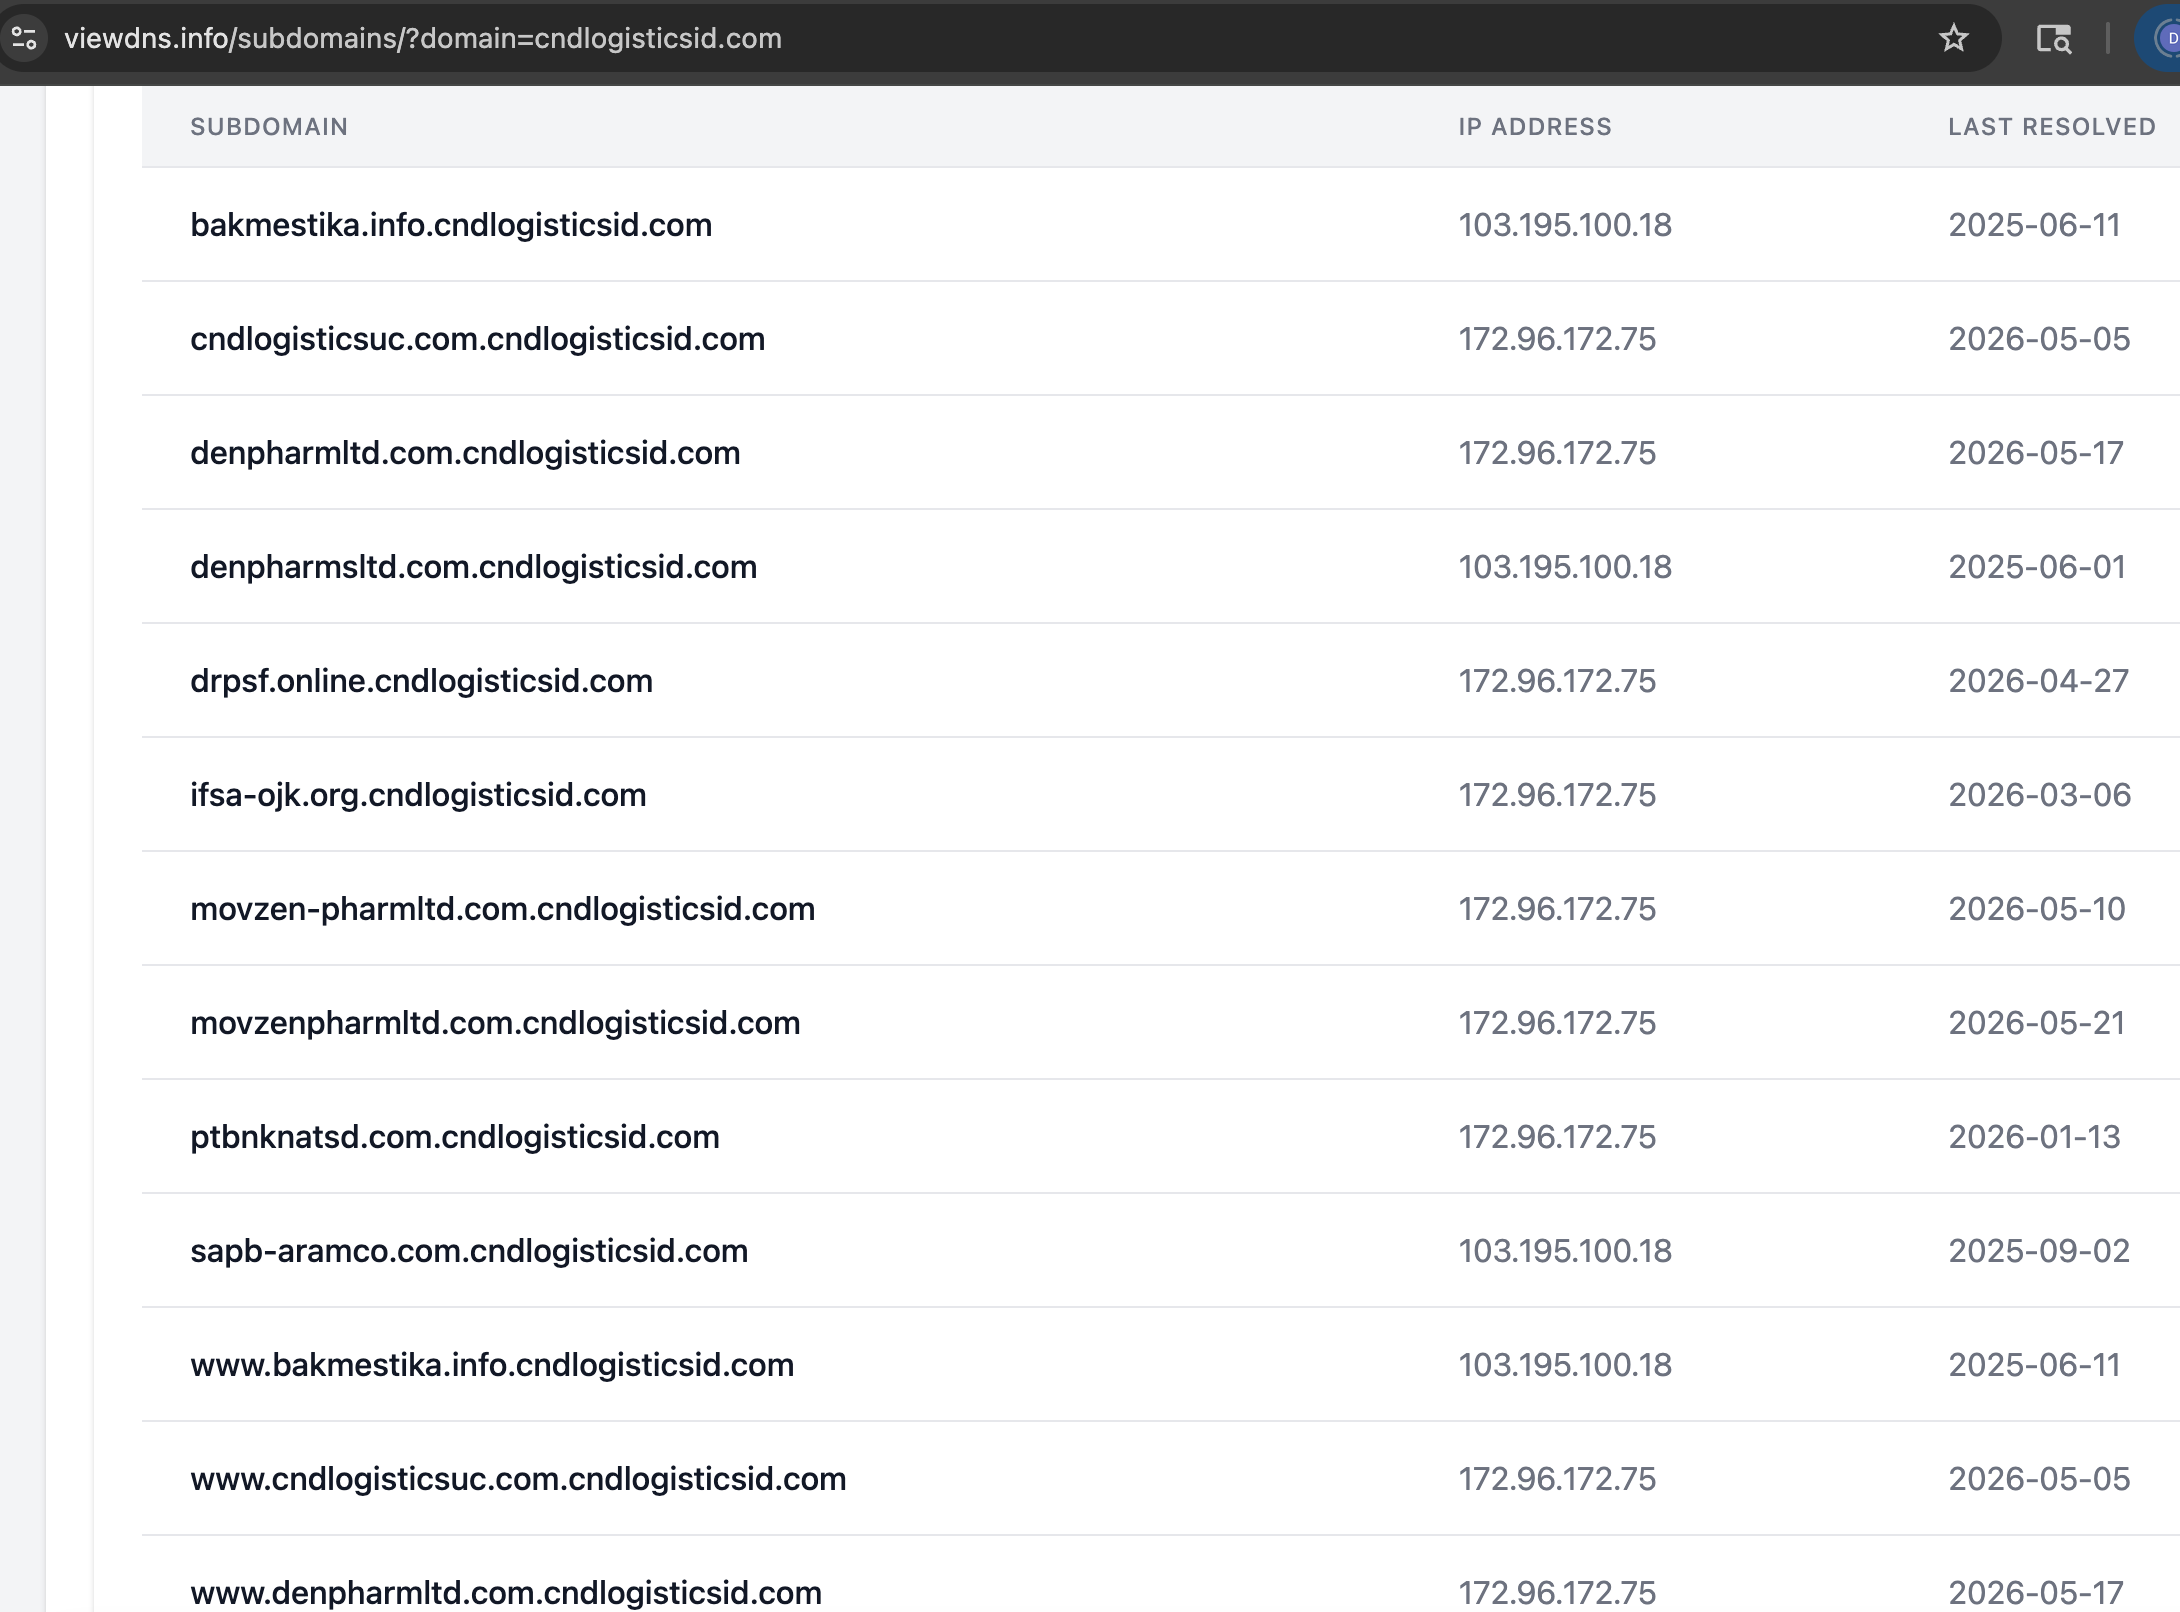
Some of these were just nested hostnames, some were live sites:
denpharmltd.com.cndlogisticsid.com
drpsf.online.cndlogisticsid.com
movzen-pharmltd.com.cndlogisticsid.com
cndlogisticsuc.com.cndlogisticsid.com
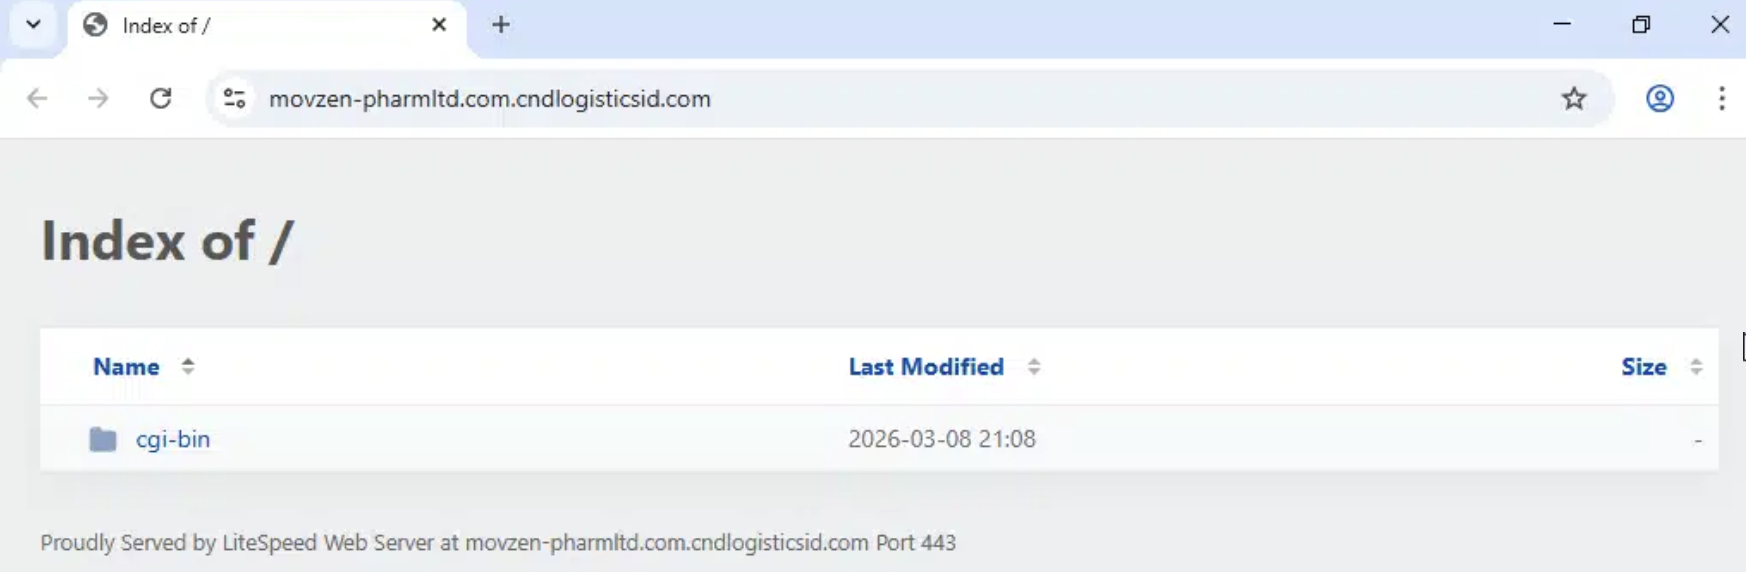
movzen-pharmltd.com.cndlogisticsid.com did not show the polished pharma clone when I loaded it. It showed a directory index with only cgi-bin:
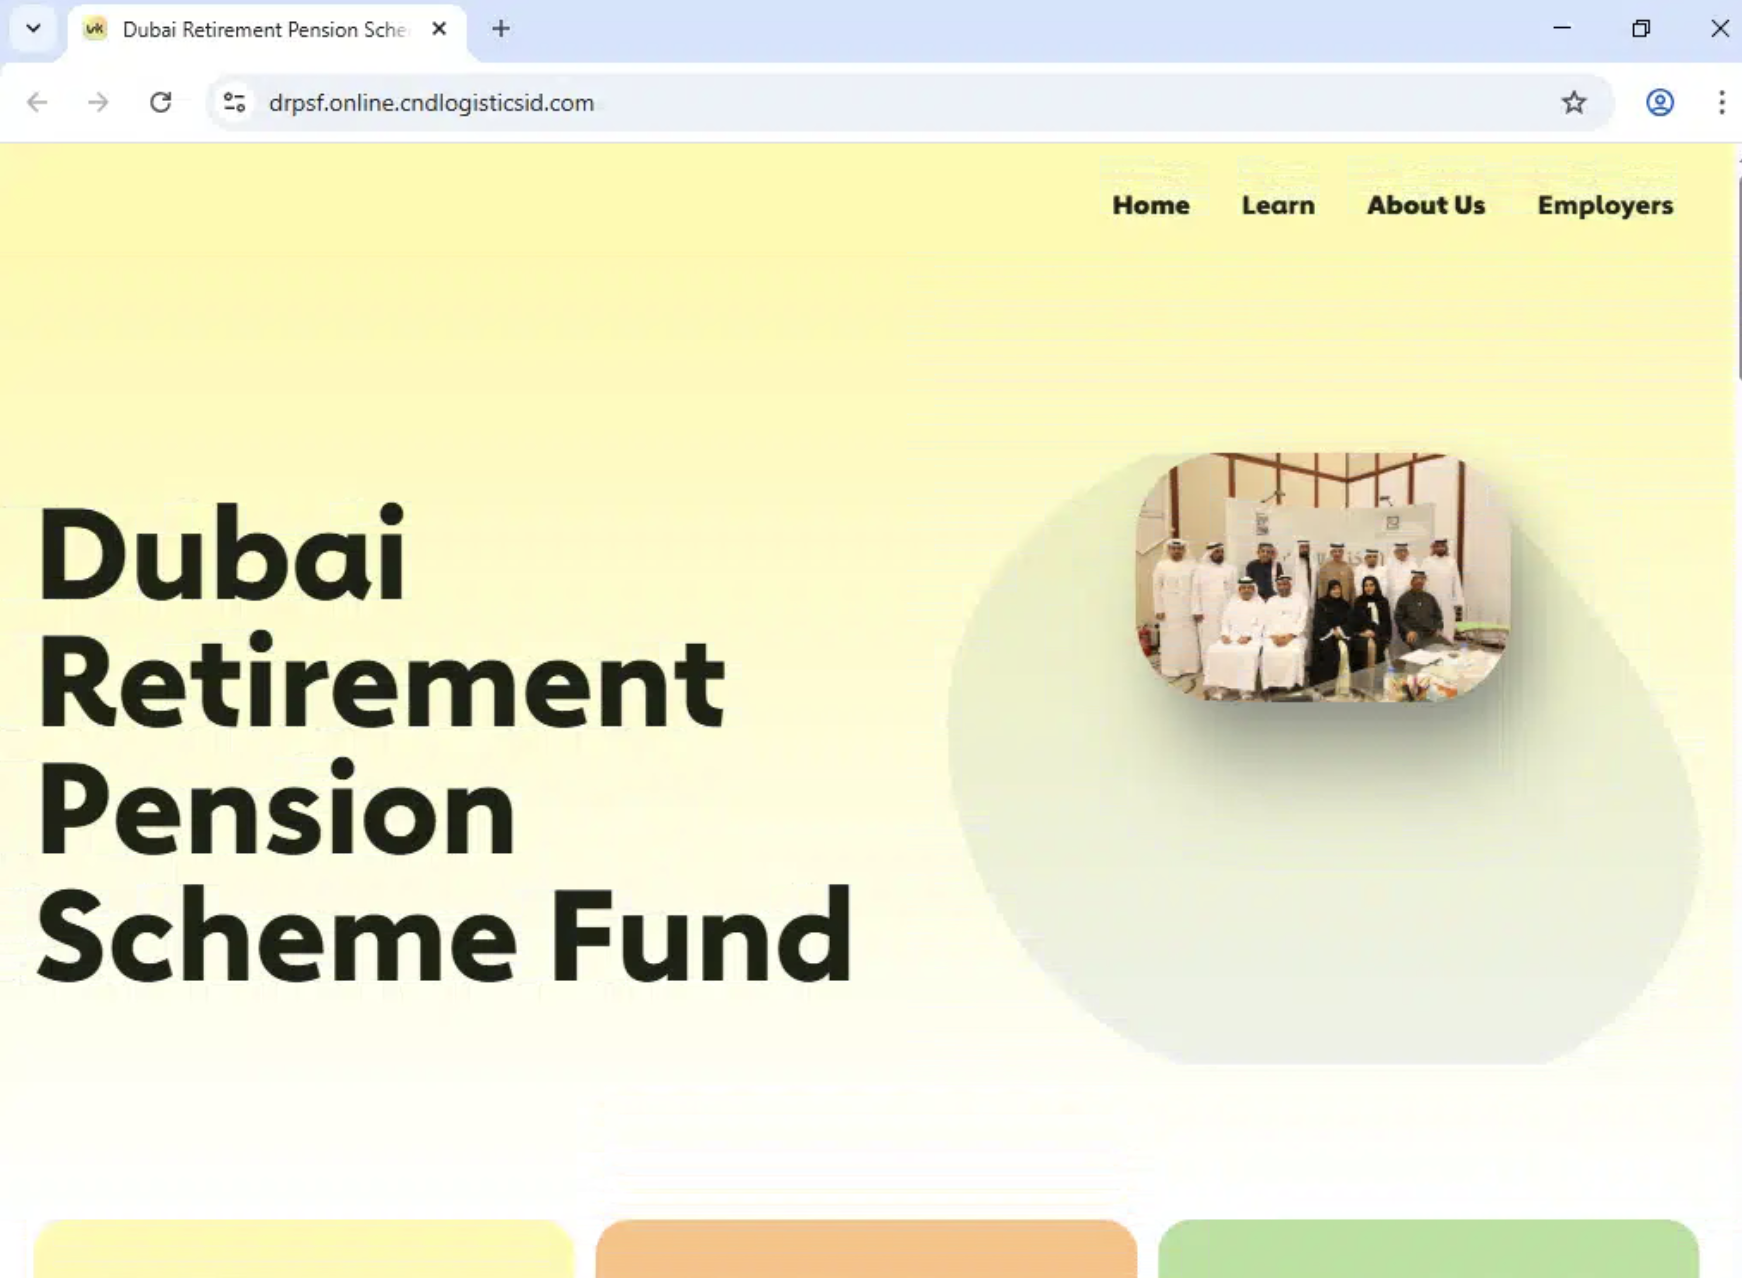
drpsf.online.cndlogisticsid.com served a "Dubai Retirement Pension Scheme Fund" site:
The footer claimed:
Email: [email protected]
Phone: +971 52 276 0126
(Shoutout to our prior finding of drpsf.site!)
And the source had another HTTrack receipt:
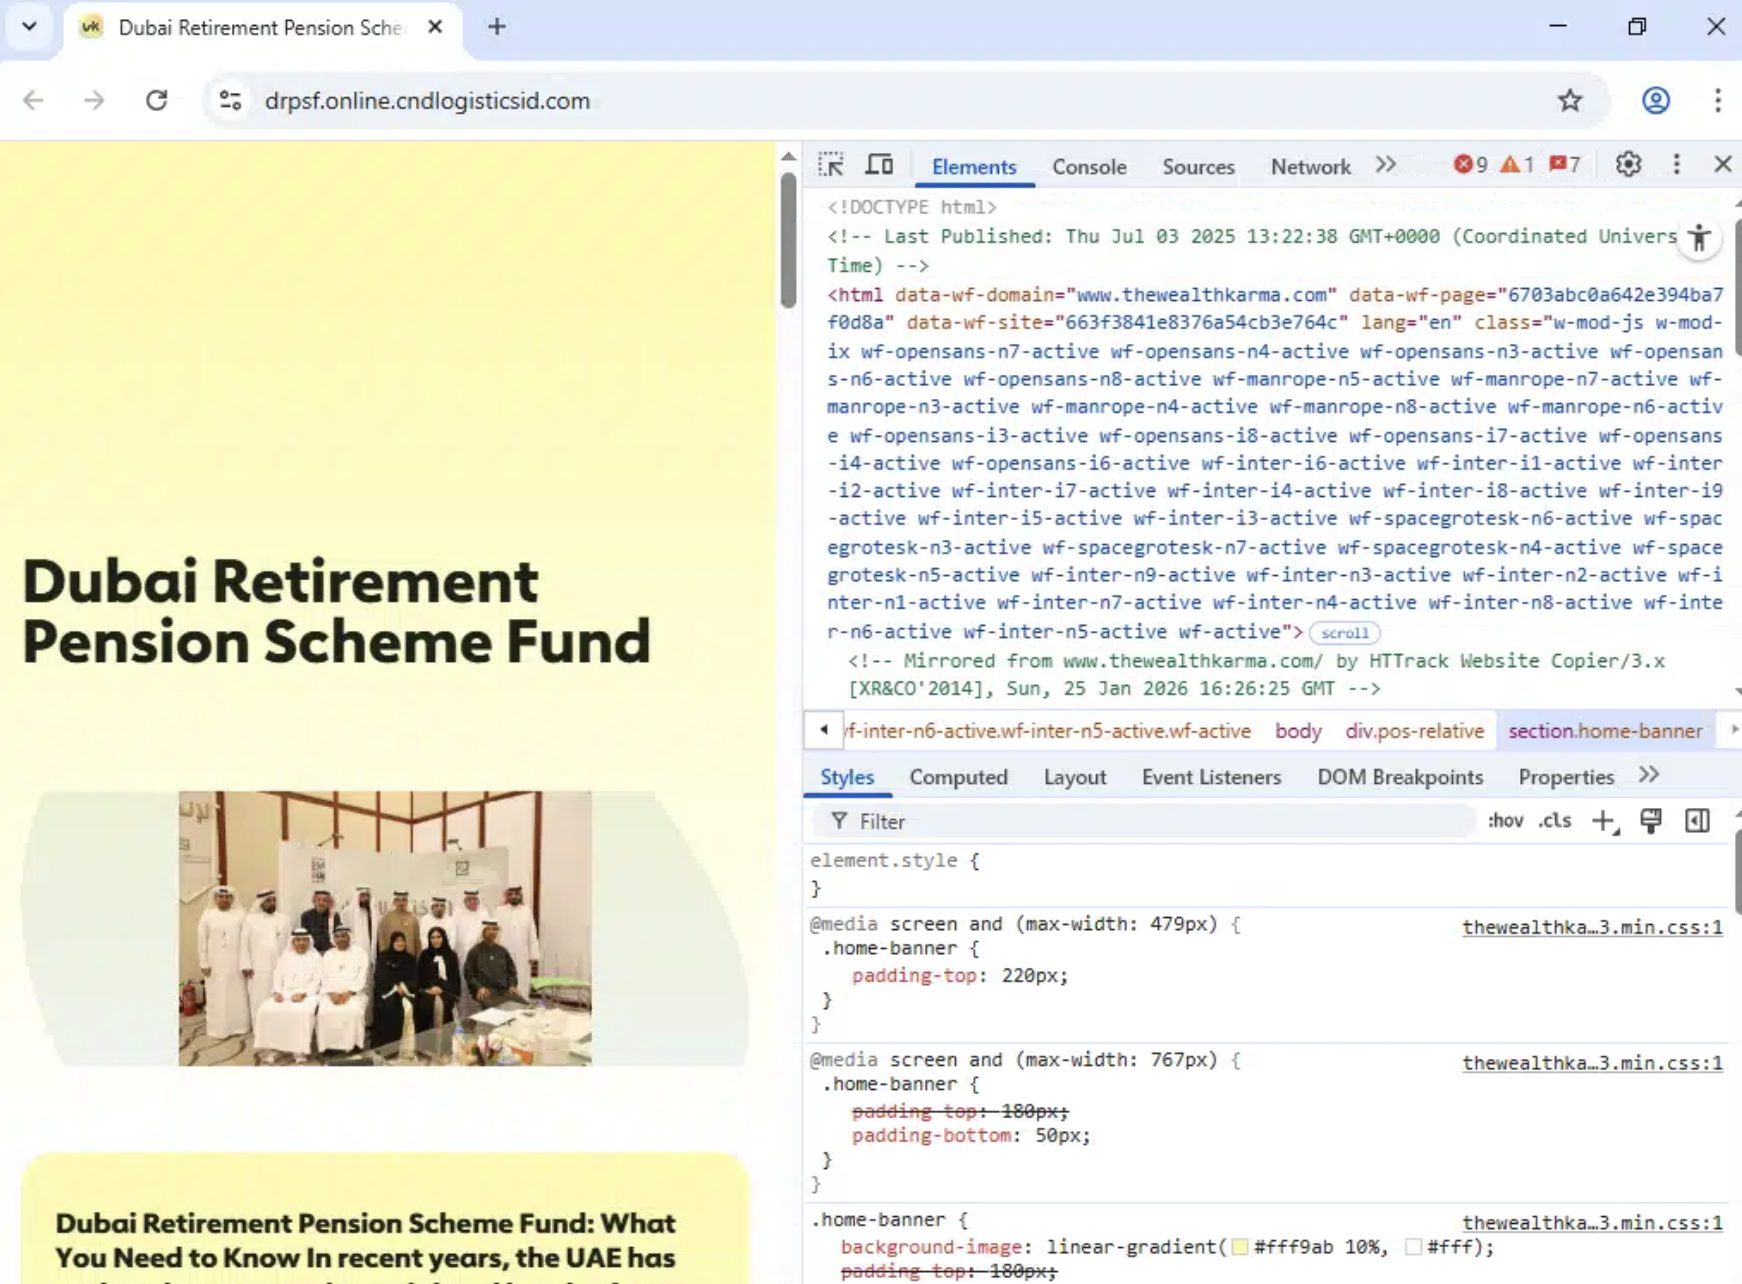
<!-- Mirrored from www.thewealthkarma.com/ by HTTrack Website Copier/3.x
[XR&CO'2014], Sun, 25 Jan 2026 16:26:25 GMT -->
So the cloning pattern was not limited to pharma. It also included a fake pension/finance front copied from a different source site.
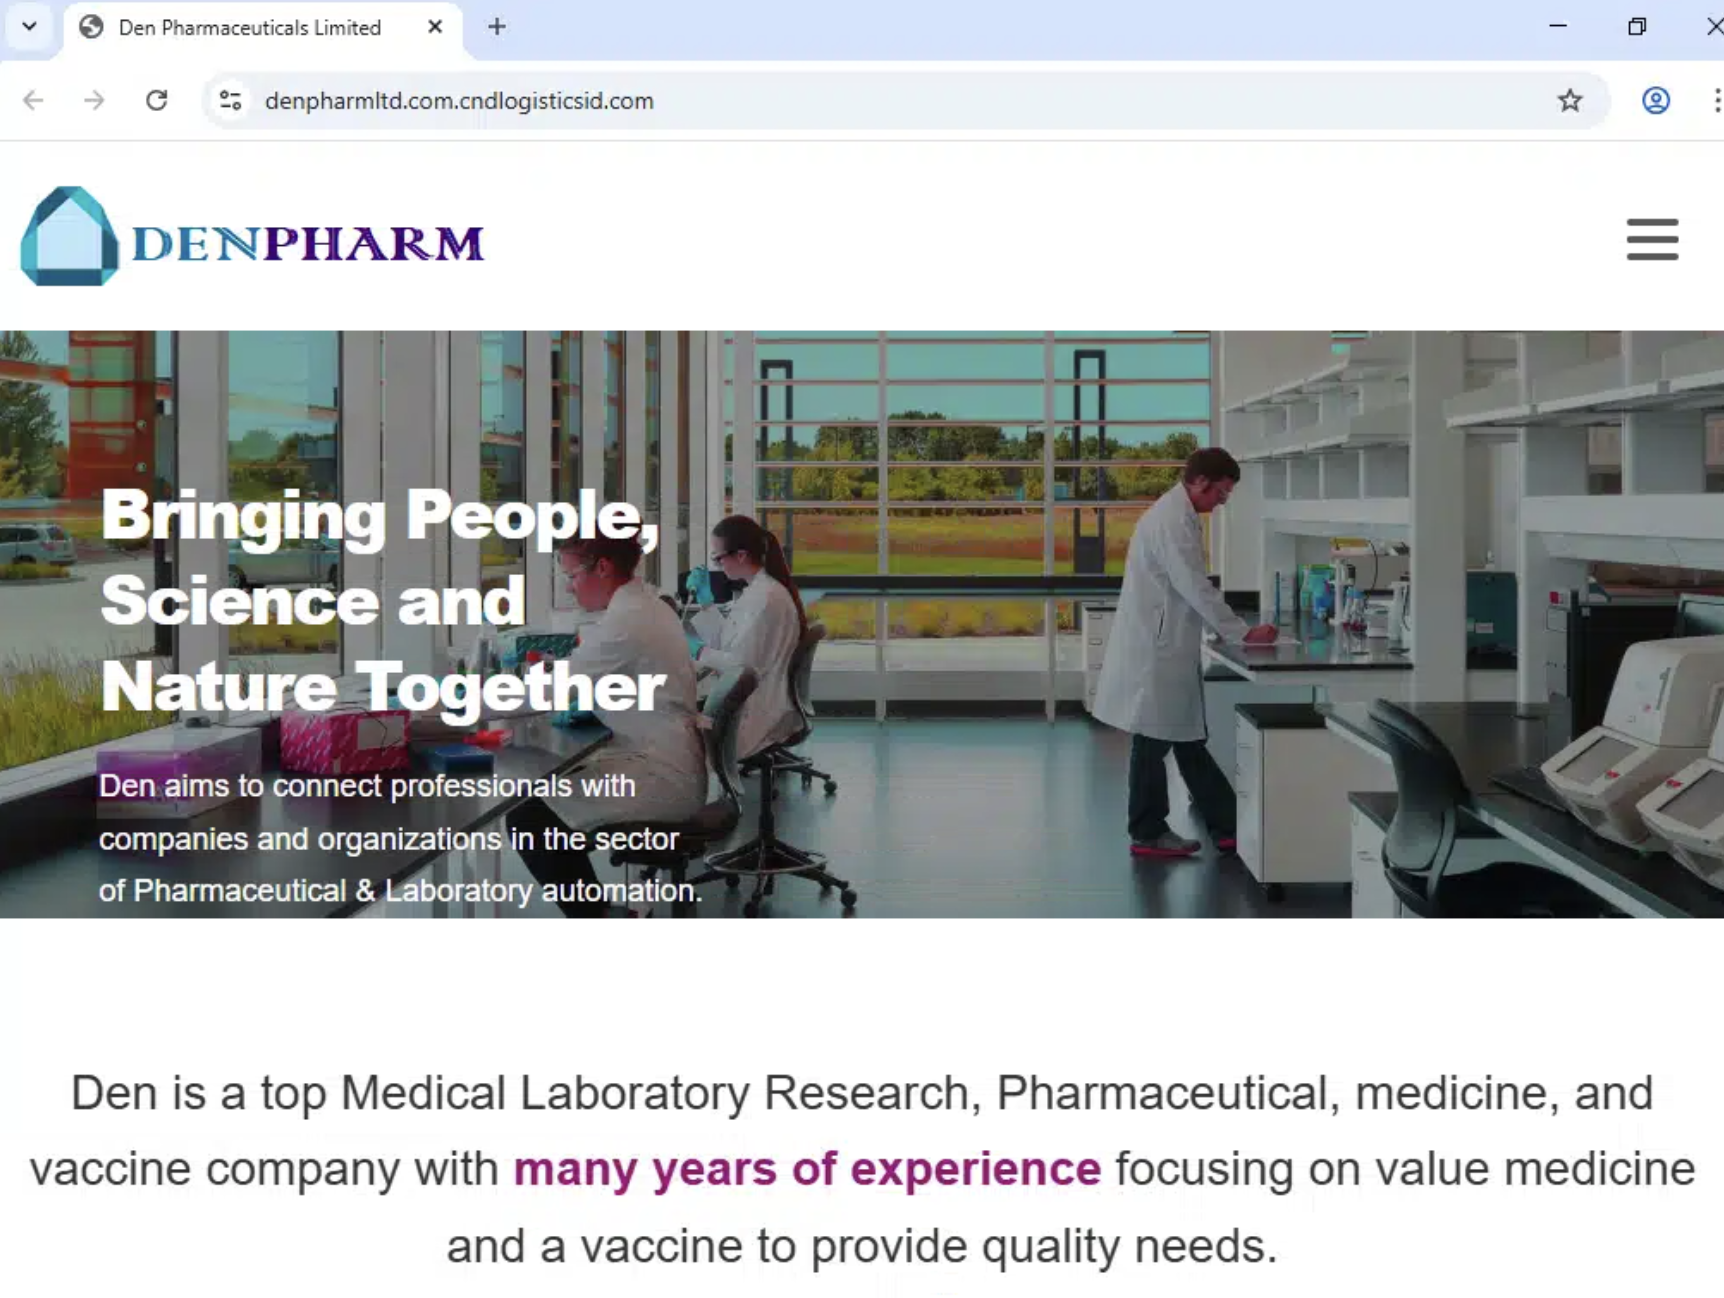
denpharmltd.com.cndlogisticsid.com served a Denpharm-branded pharma/lab automation page:
And, again, the source gave away the copy job:
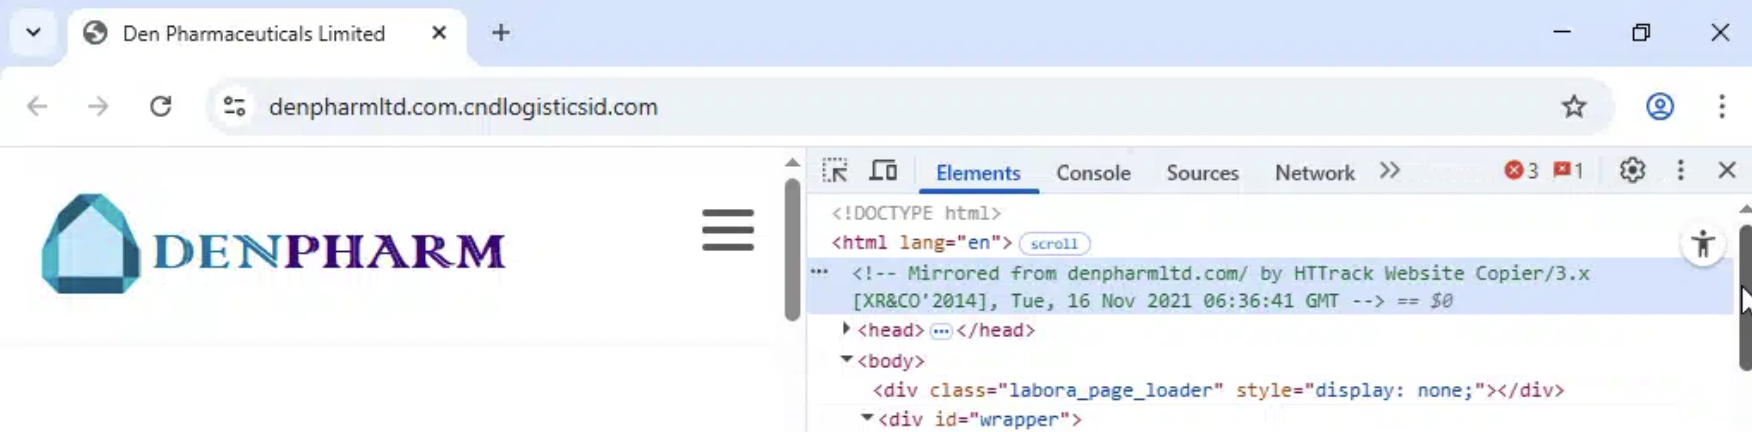
<!-- Mirrored from denpharmltd.com/ by HTTrack Website Copier/3.x
[XR&CO'2014], Tue, 16 Nov 2021 06:36:41 GMT -->
Denpharm is not new
The Denpharm branch has history outside this cluster.
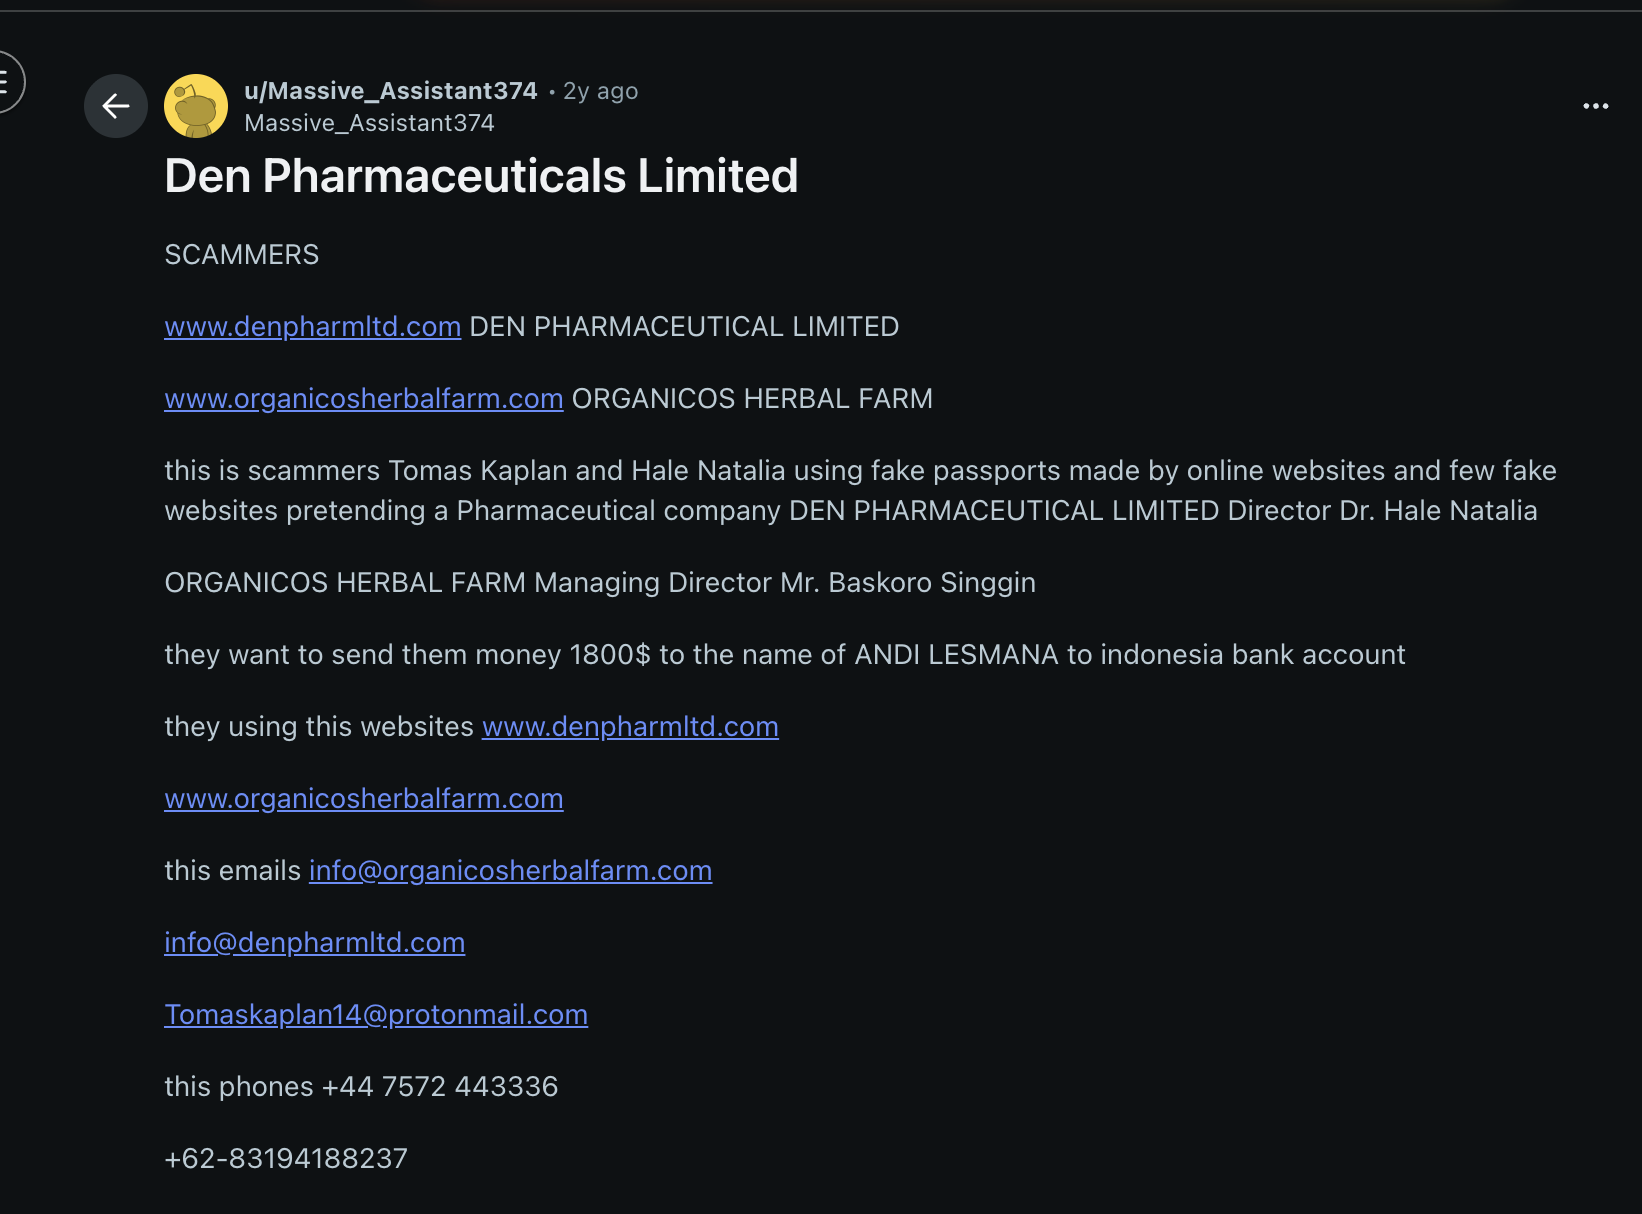
A public Reddit warning from 2024 called out denpharmltd.com alongside organicosherbalfarm.com and described the setup as a procurement scam using fake pharmaceutical and herbal-supplier personas. The post named [email protected], [email protected], and [email protected], plus the same sort of "director / managing director" cosplay that showed up in the cloned sites.
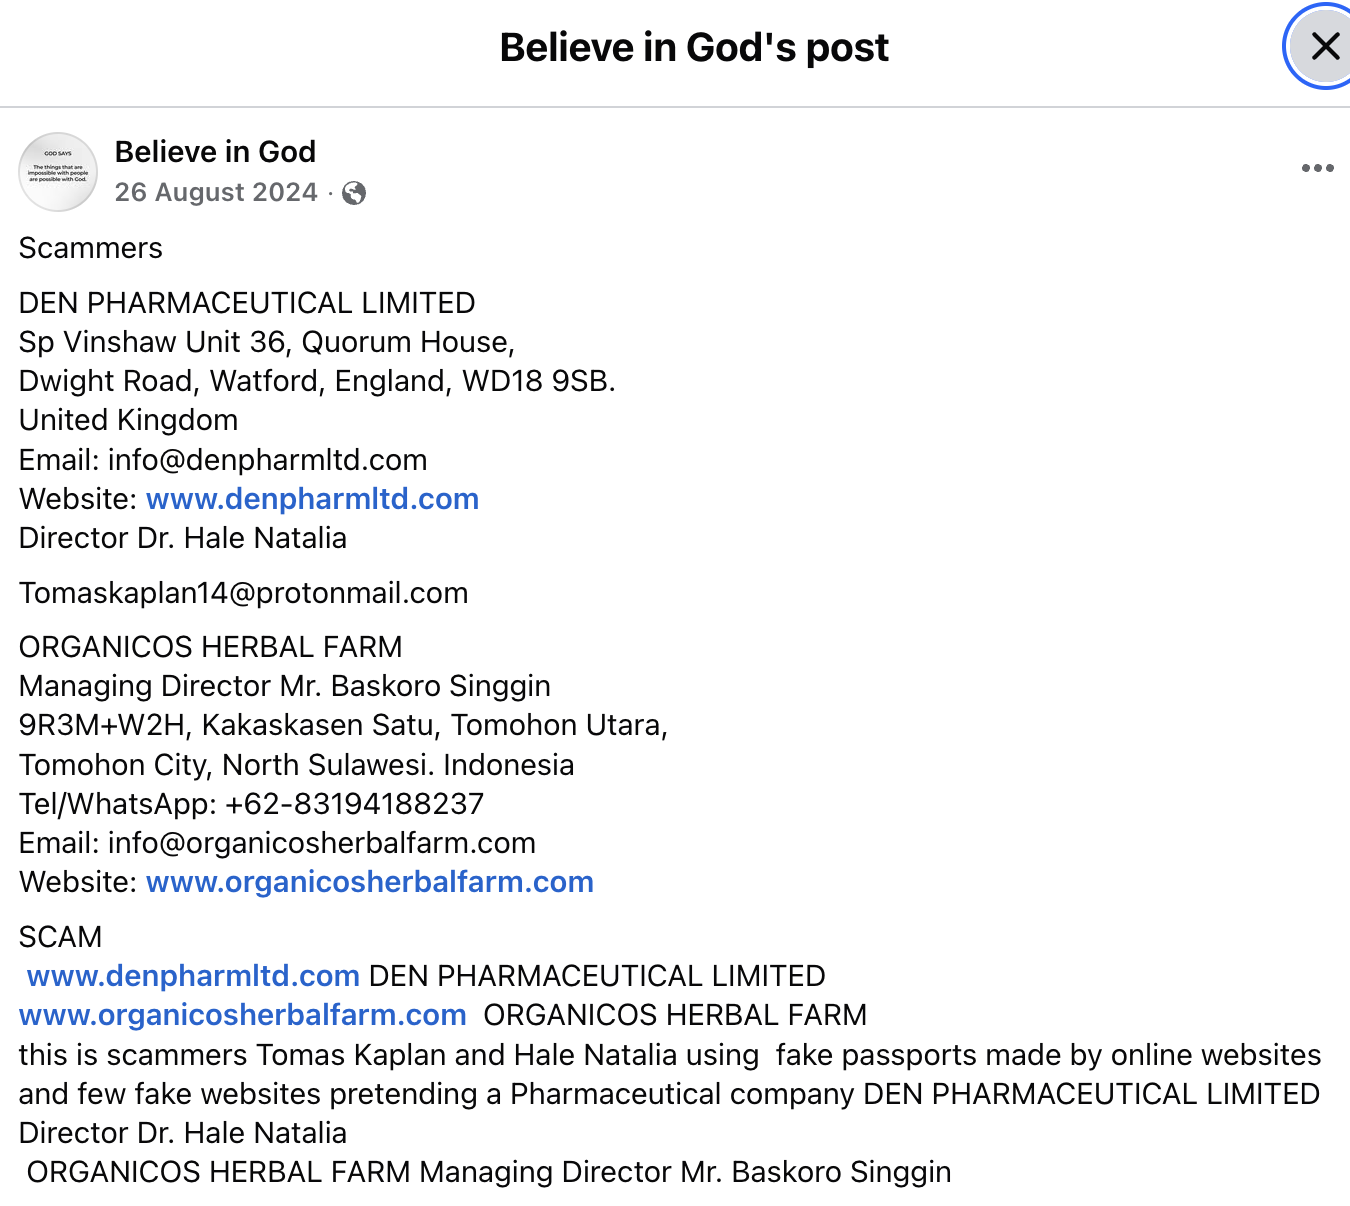
There was also a Facebook post with a longer version of the script. The pitch was classic advance-fee/procurement bait: a pharma buyer needs a herbal oil extract supplier, asks the victim to act as the local dealer, then talks through big per-barrel profit margins.
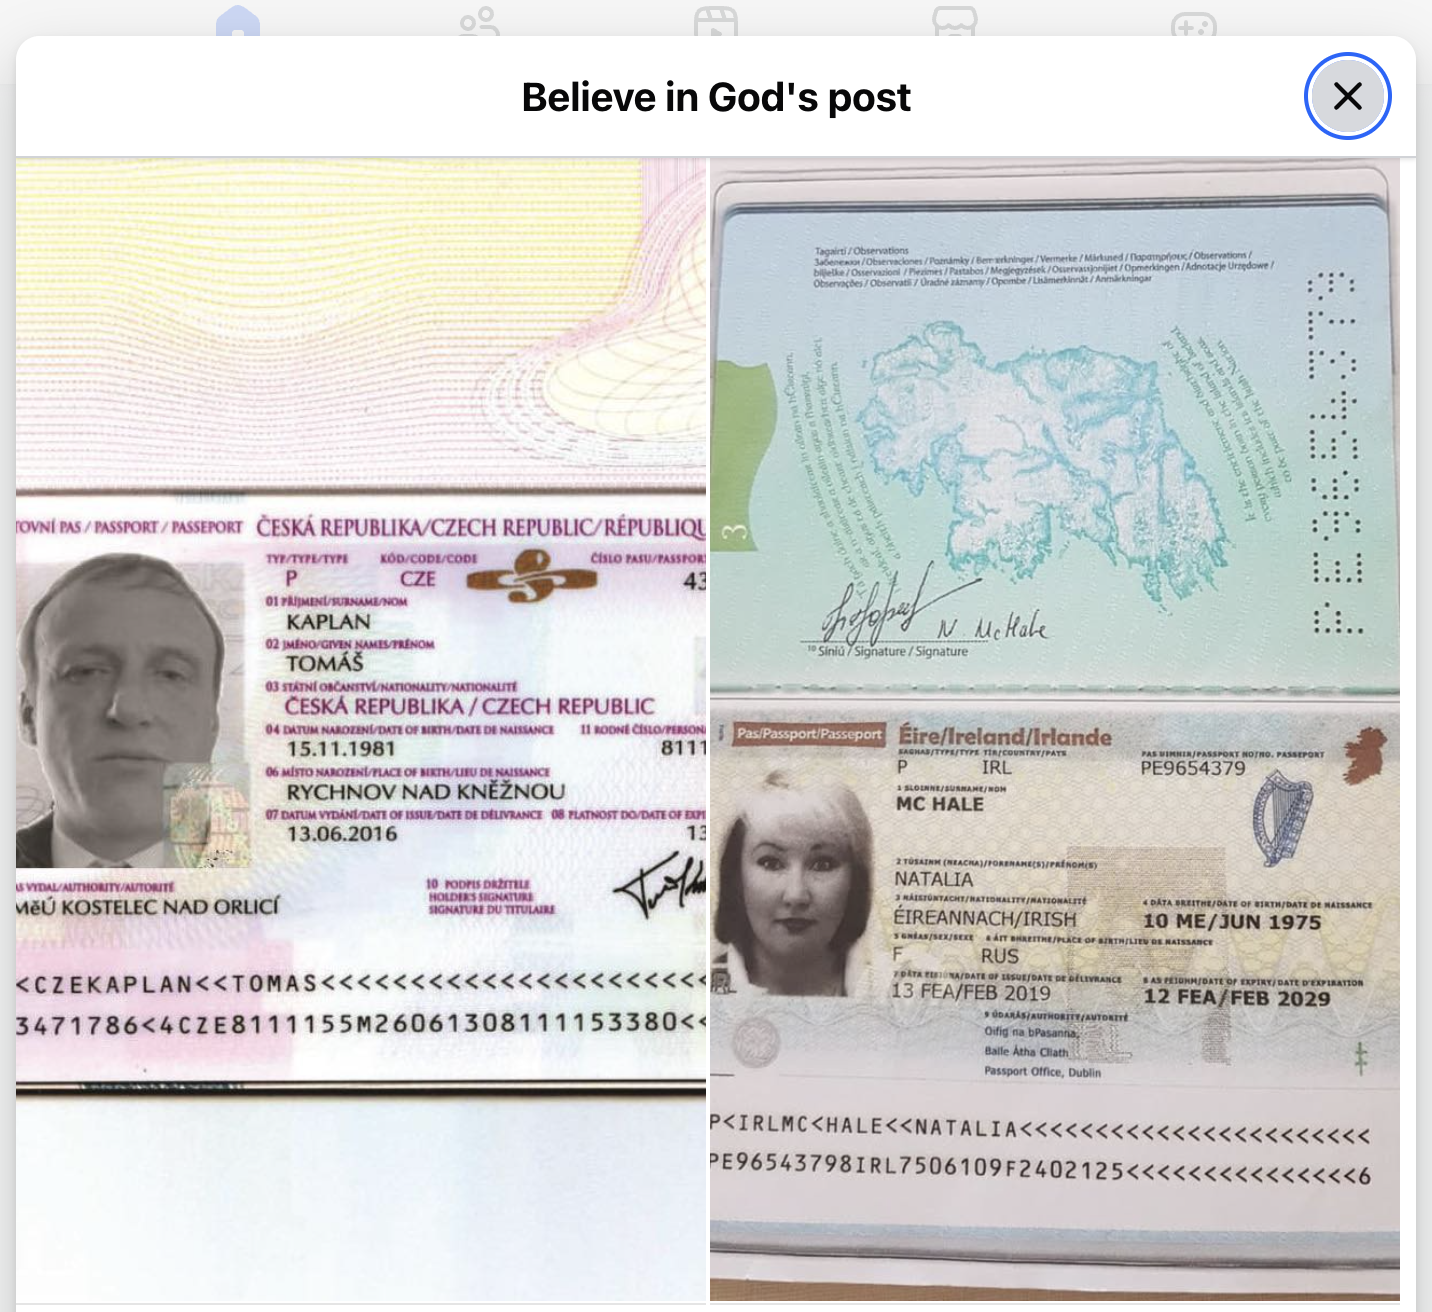
The same public warning included alleged fake passport images for the Tomas Kaplan and Hale Natalia personas:
A separate Betrugsalarm report from September 2024 pointed at organicosherbalfarm.com, [email protected], the Andi Lesmana Jakarta name, and the same Indonesian phone number family:
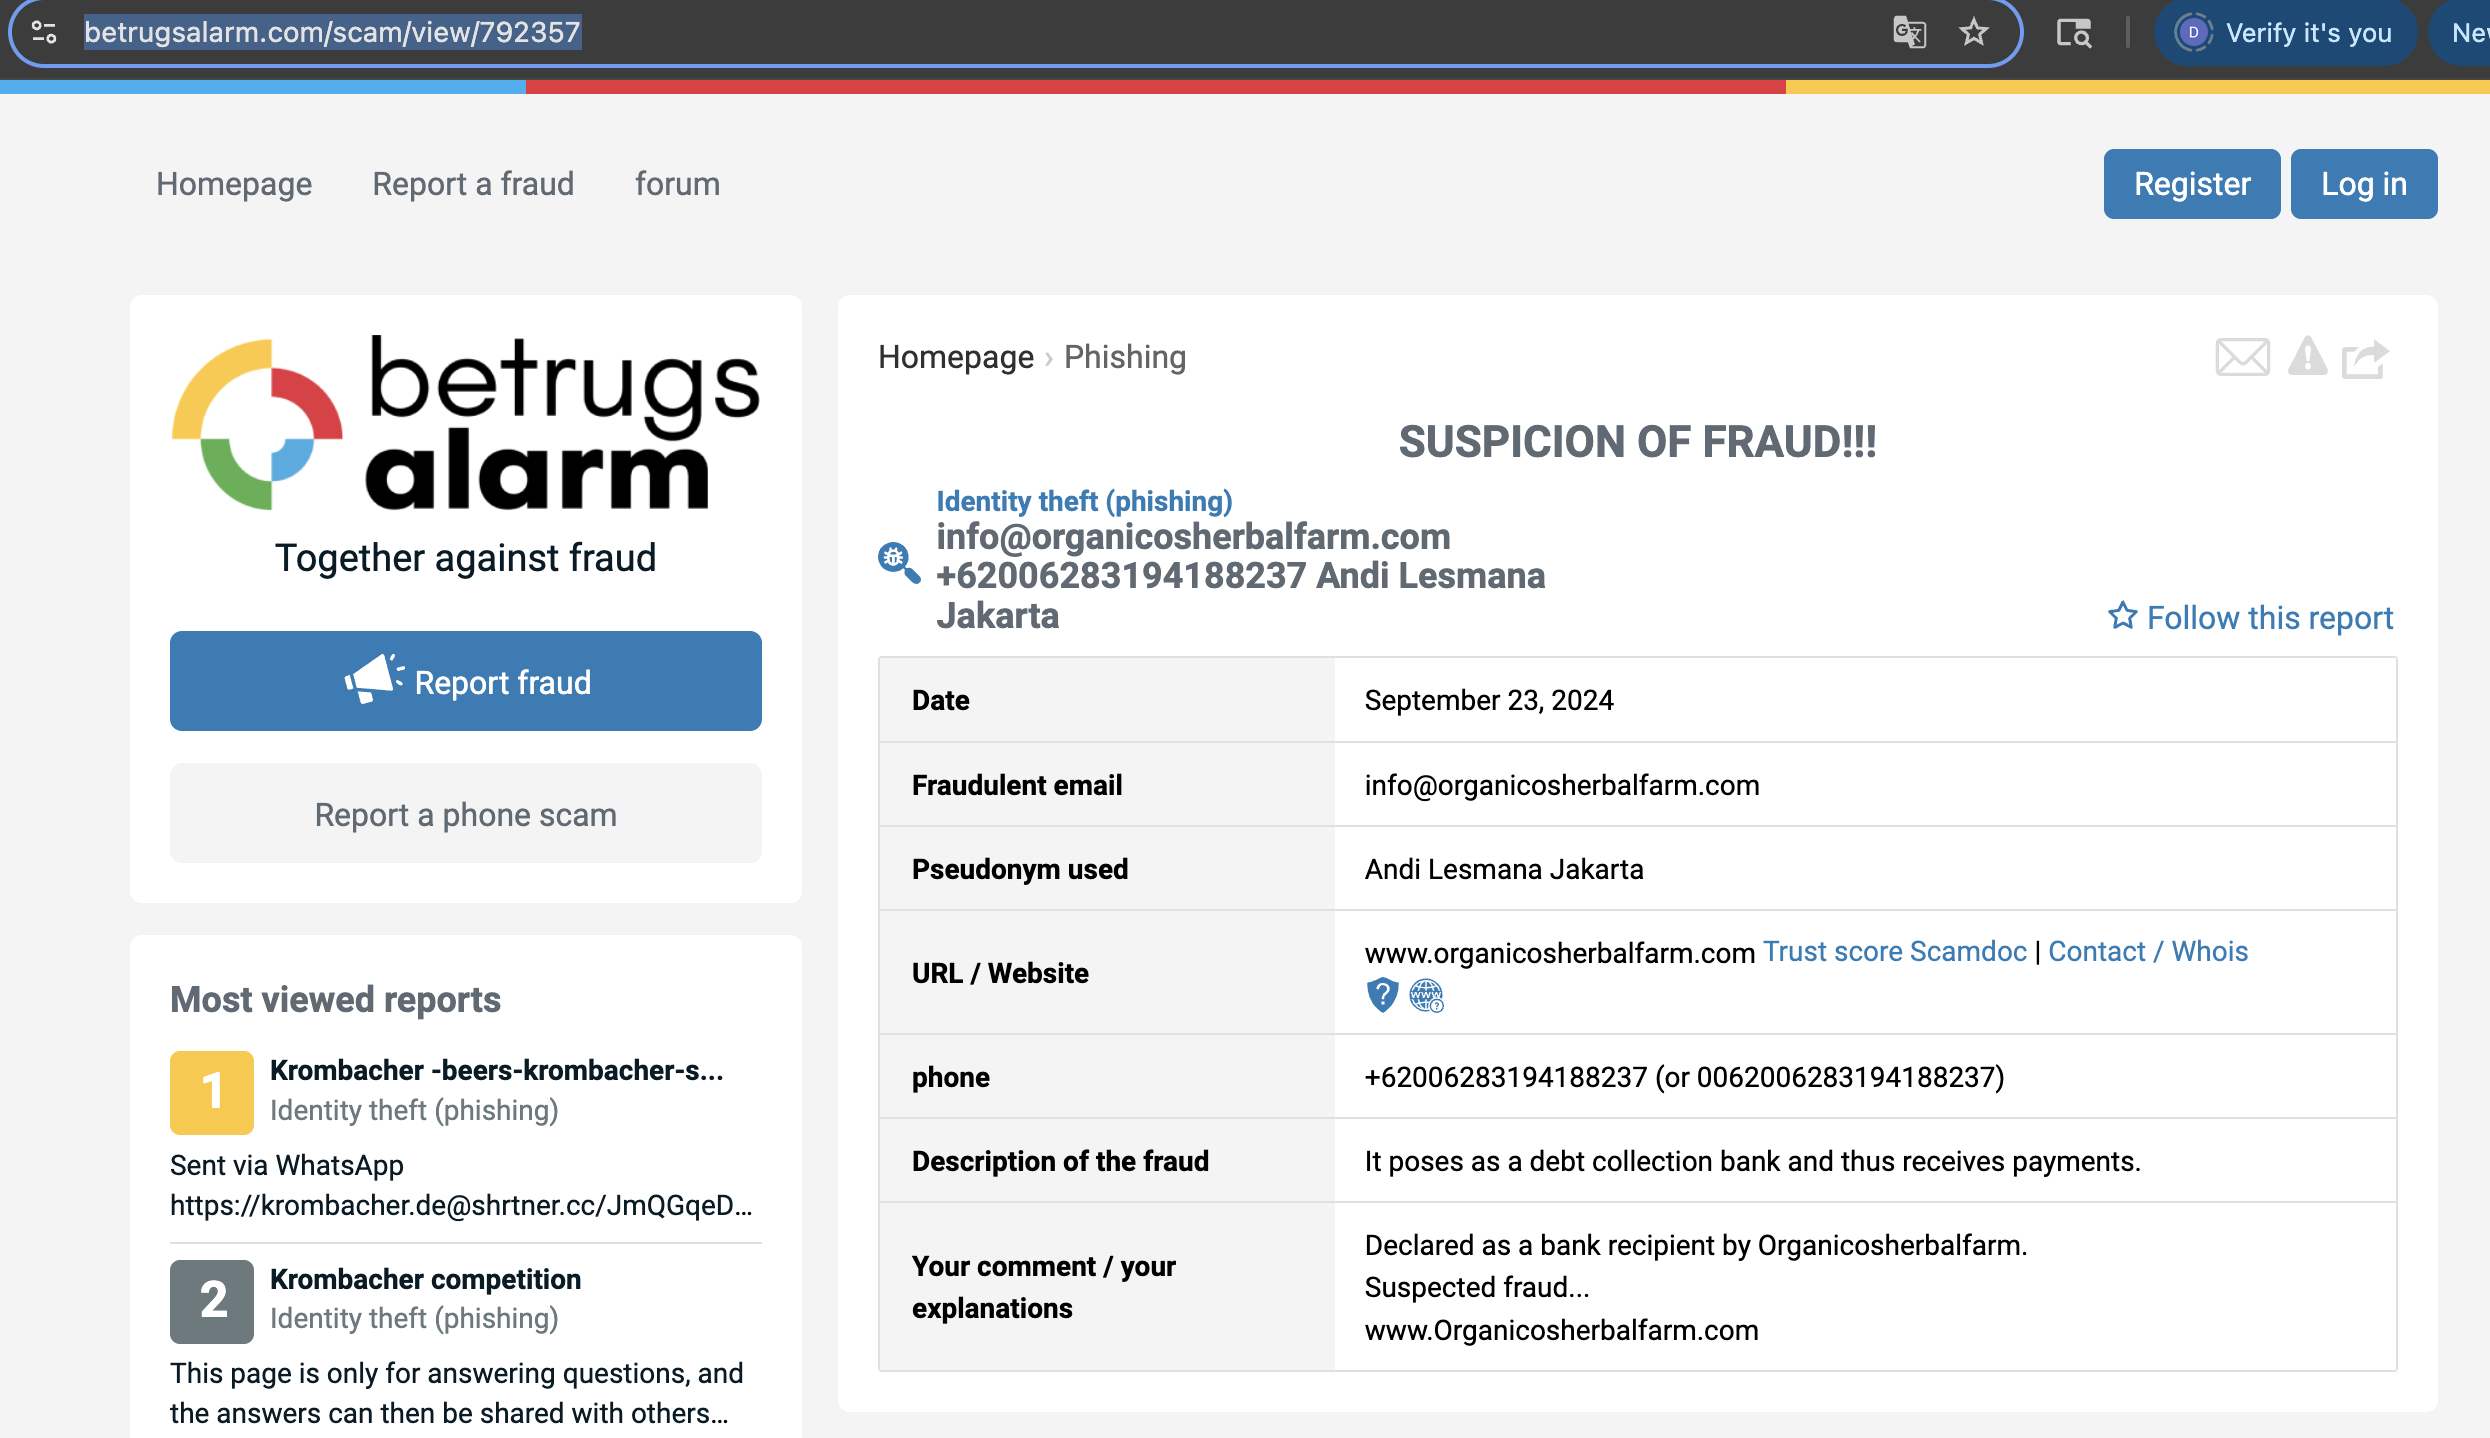
Fraudulent email: [email protected]
Pseudonym used:   Andi Lesmana Jakarta
Website:          www.organicosherbalfarm.com
Phone:            +62006283194188237
That makes denpharmltd.com more than a random clone found under cndlogisticsid.com. It appears to be an older front that had already been reported in public scam warnings, then later showed up again in the same nested-hostname style as the current cluster.
The Organicos side had its own clone residue:
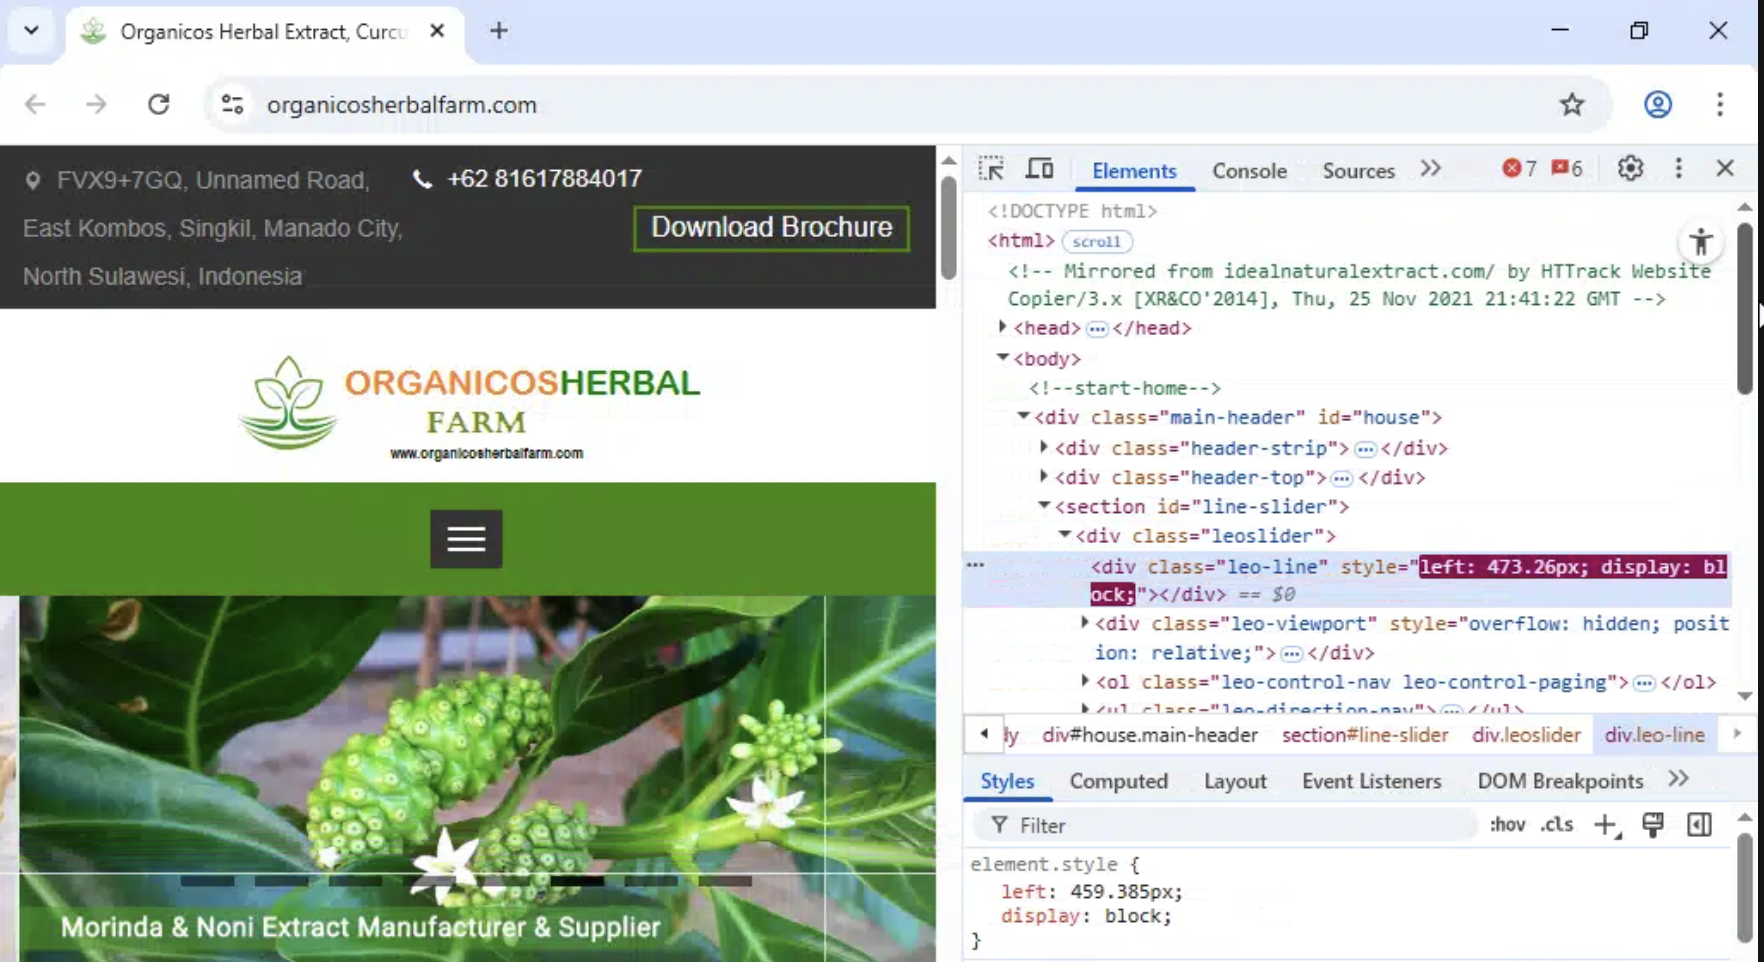
<!-- Mirrored from idealnaturalextract.com/ by HTTrack Website Copier/3.x
[XR&CO'2014], Thu, 25 Nov 2021 21:41:22 GMT -->
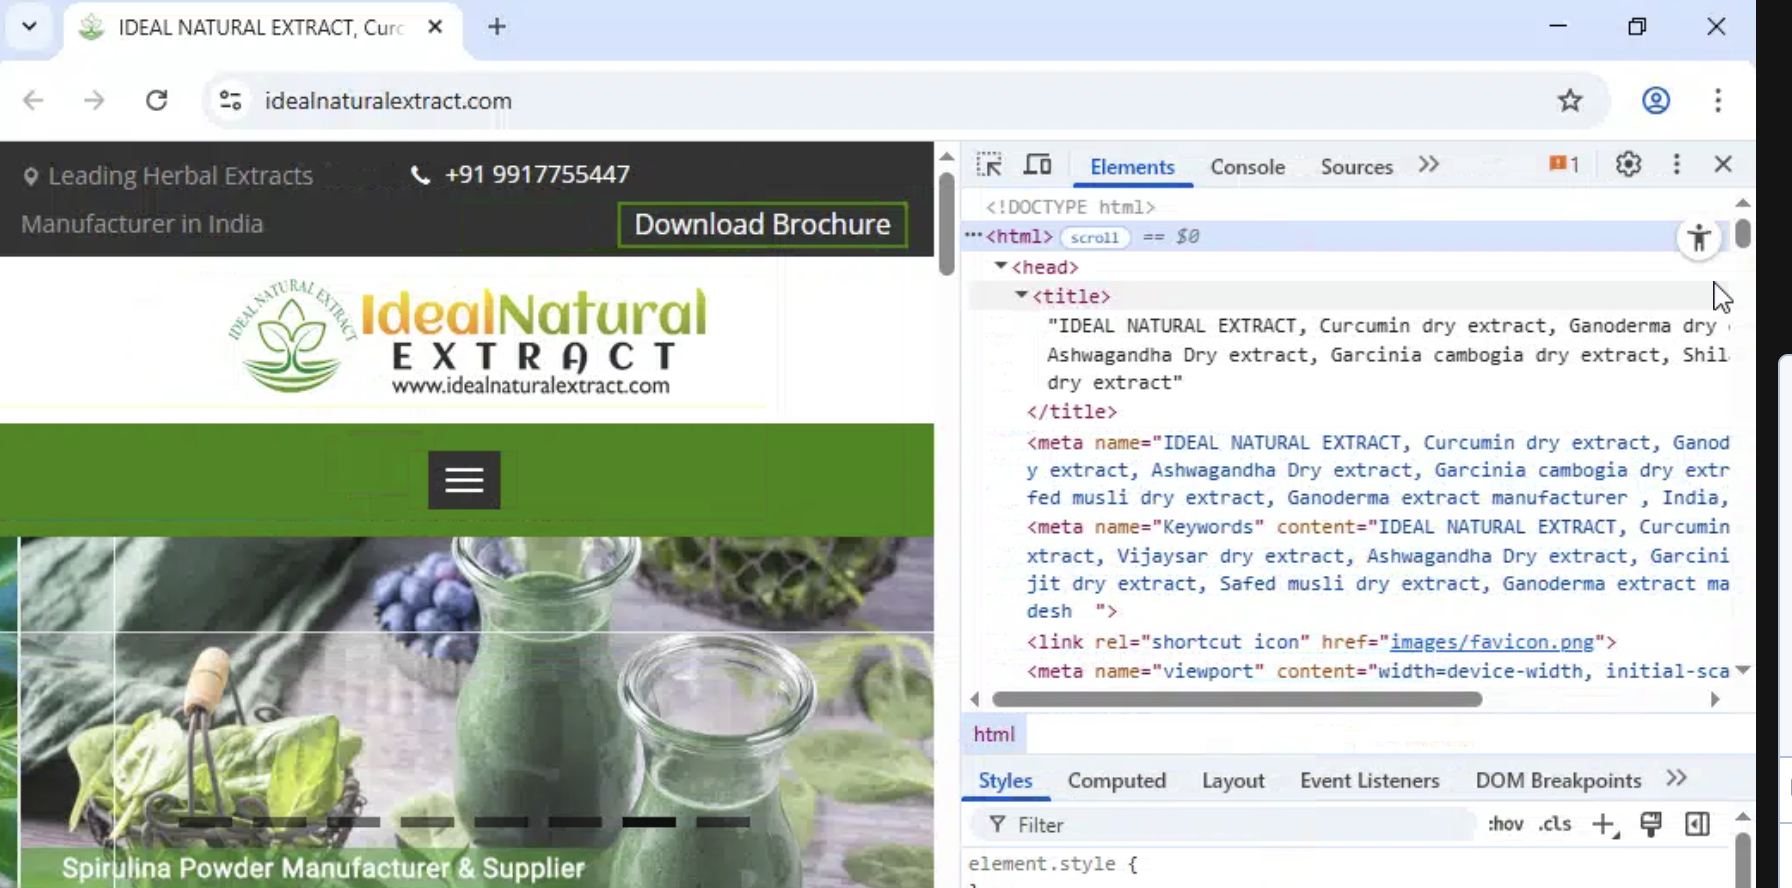
The live-looking source site, idealnaturalextract.com, still showed the same herbal-extract theme and product language:
The certificate history for organicosherbalfarm.com also had a familiar little nested-domain tell:
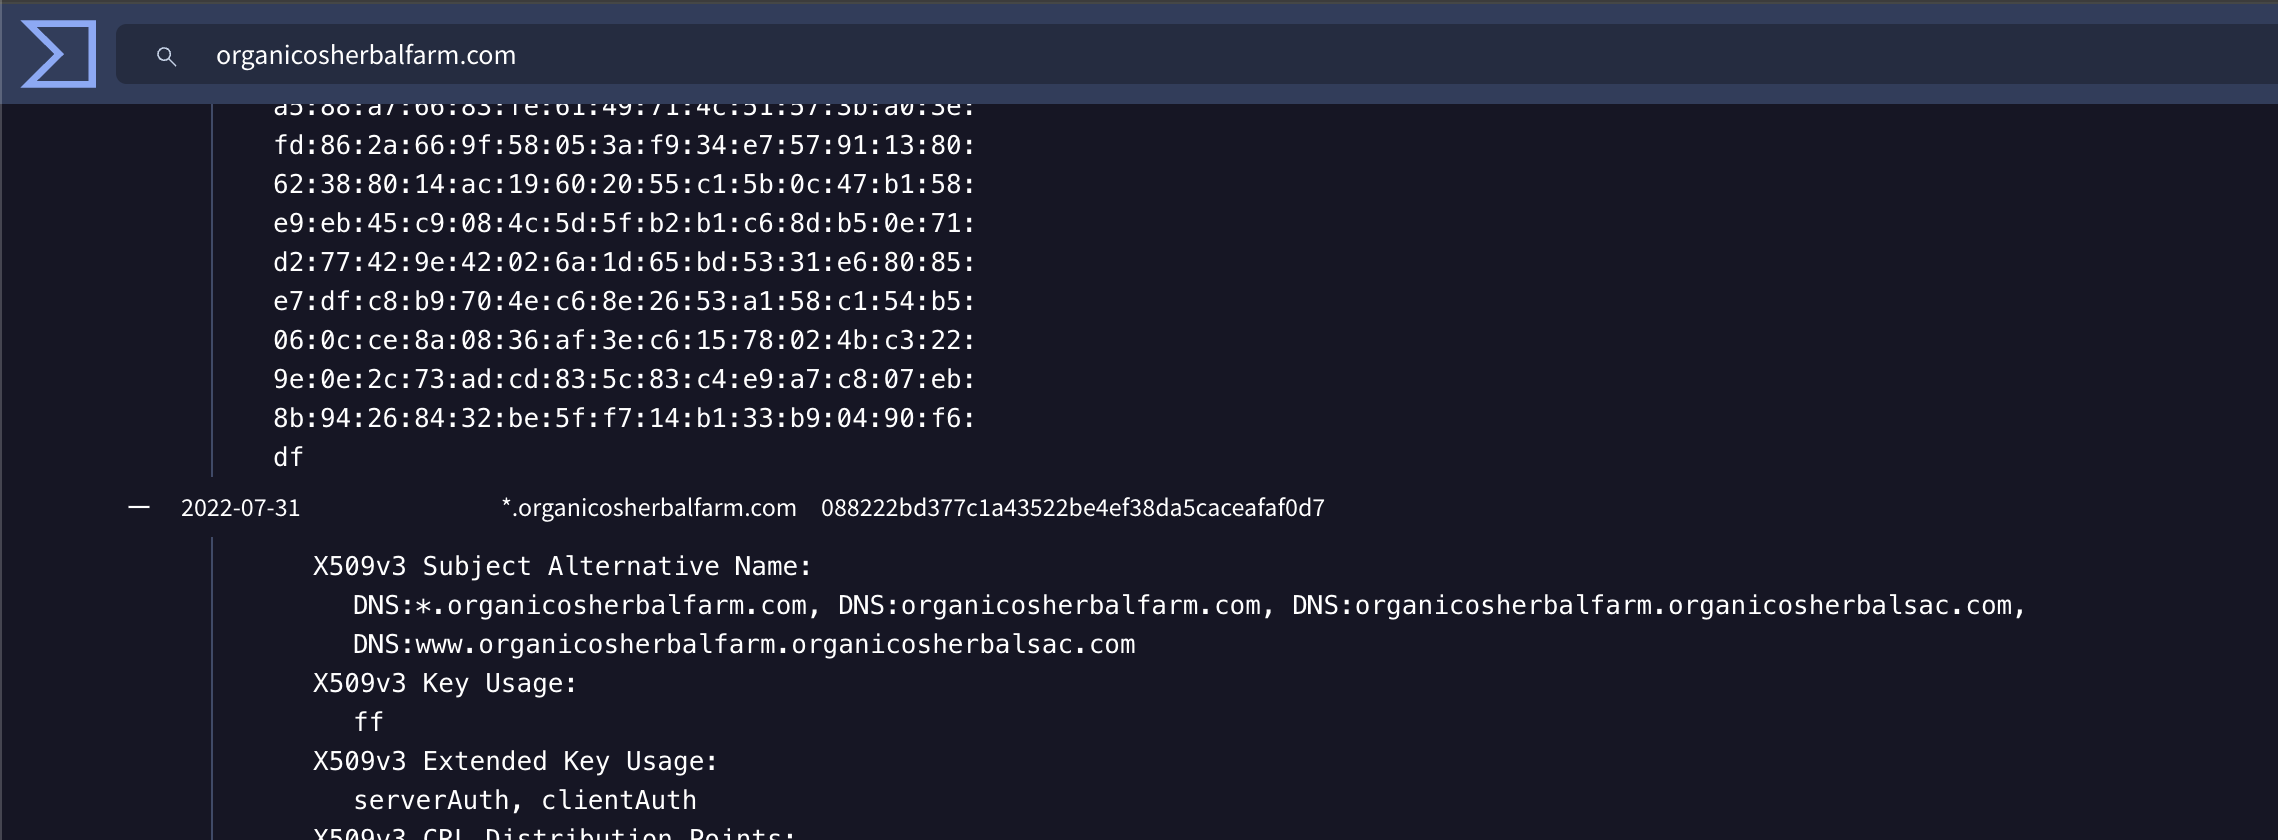
*.organicosherbalfarm.com
organicosherbalfarm.com
organicosherbalfarm.organicosherbalsac.com
www.organicosherbalfarm.organicosherbalsac.com
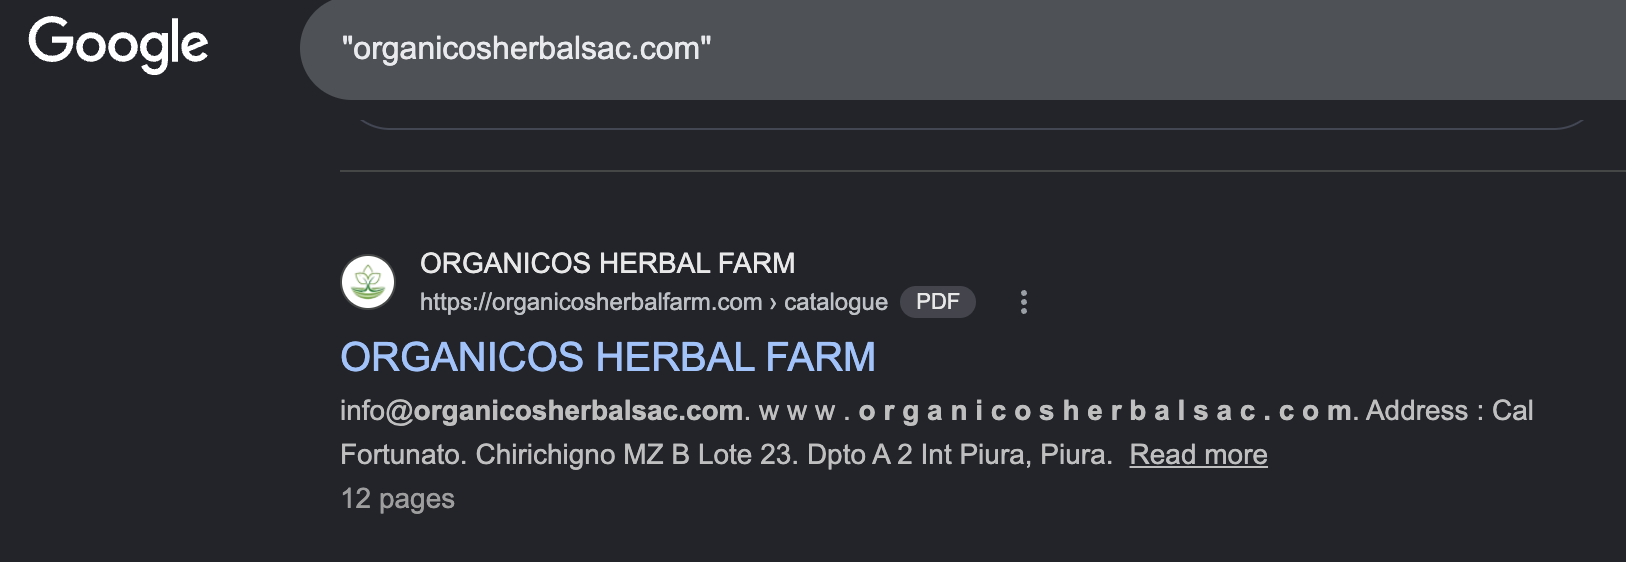
And Google still had organicosherbalsac.com indexed from the catalogue:
Subdomain discovery for organicosherbalsac.com added one more Denpharm bridge and a couple of names worth later checking:
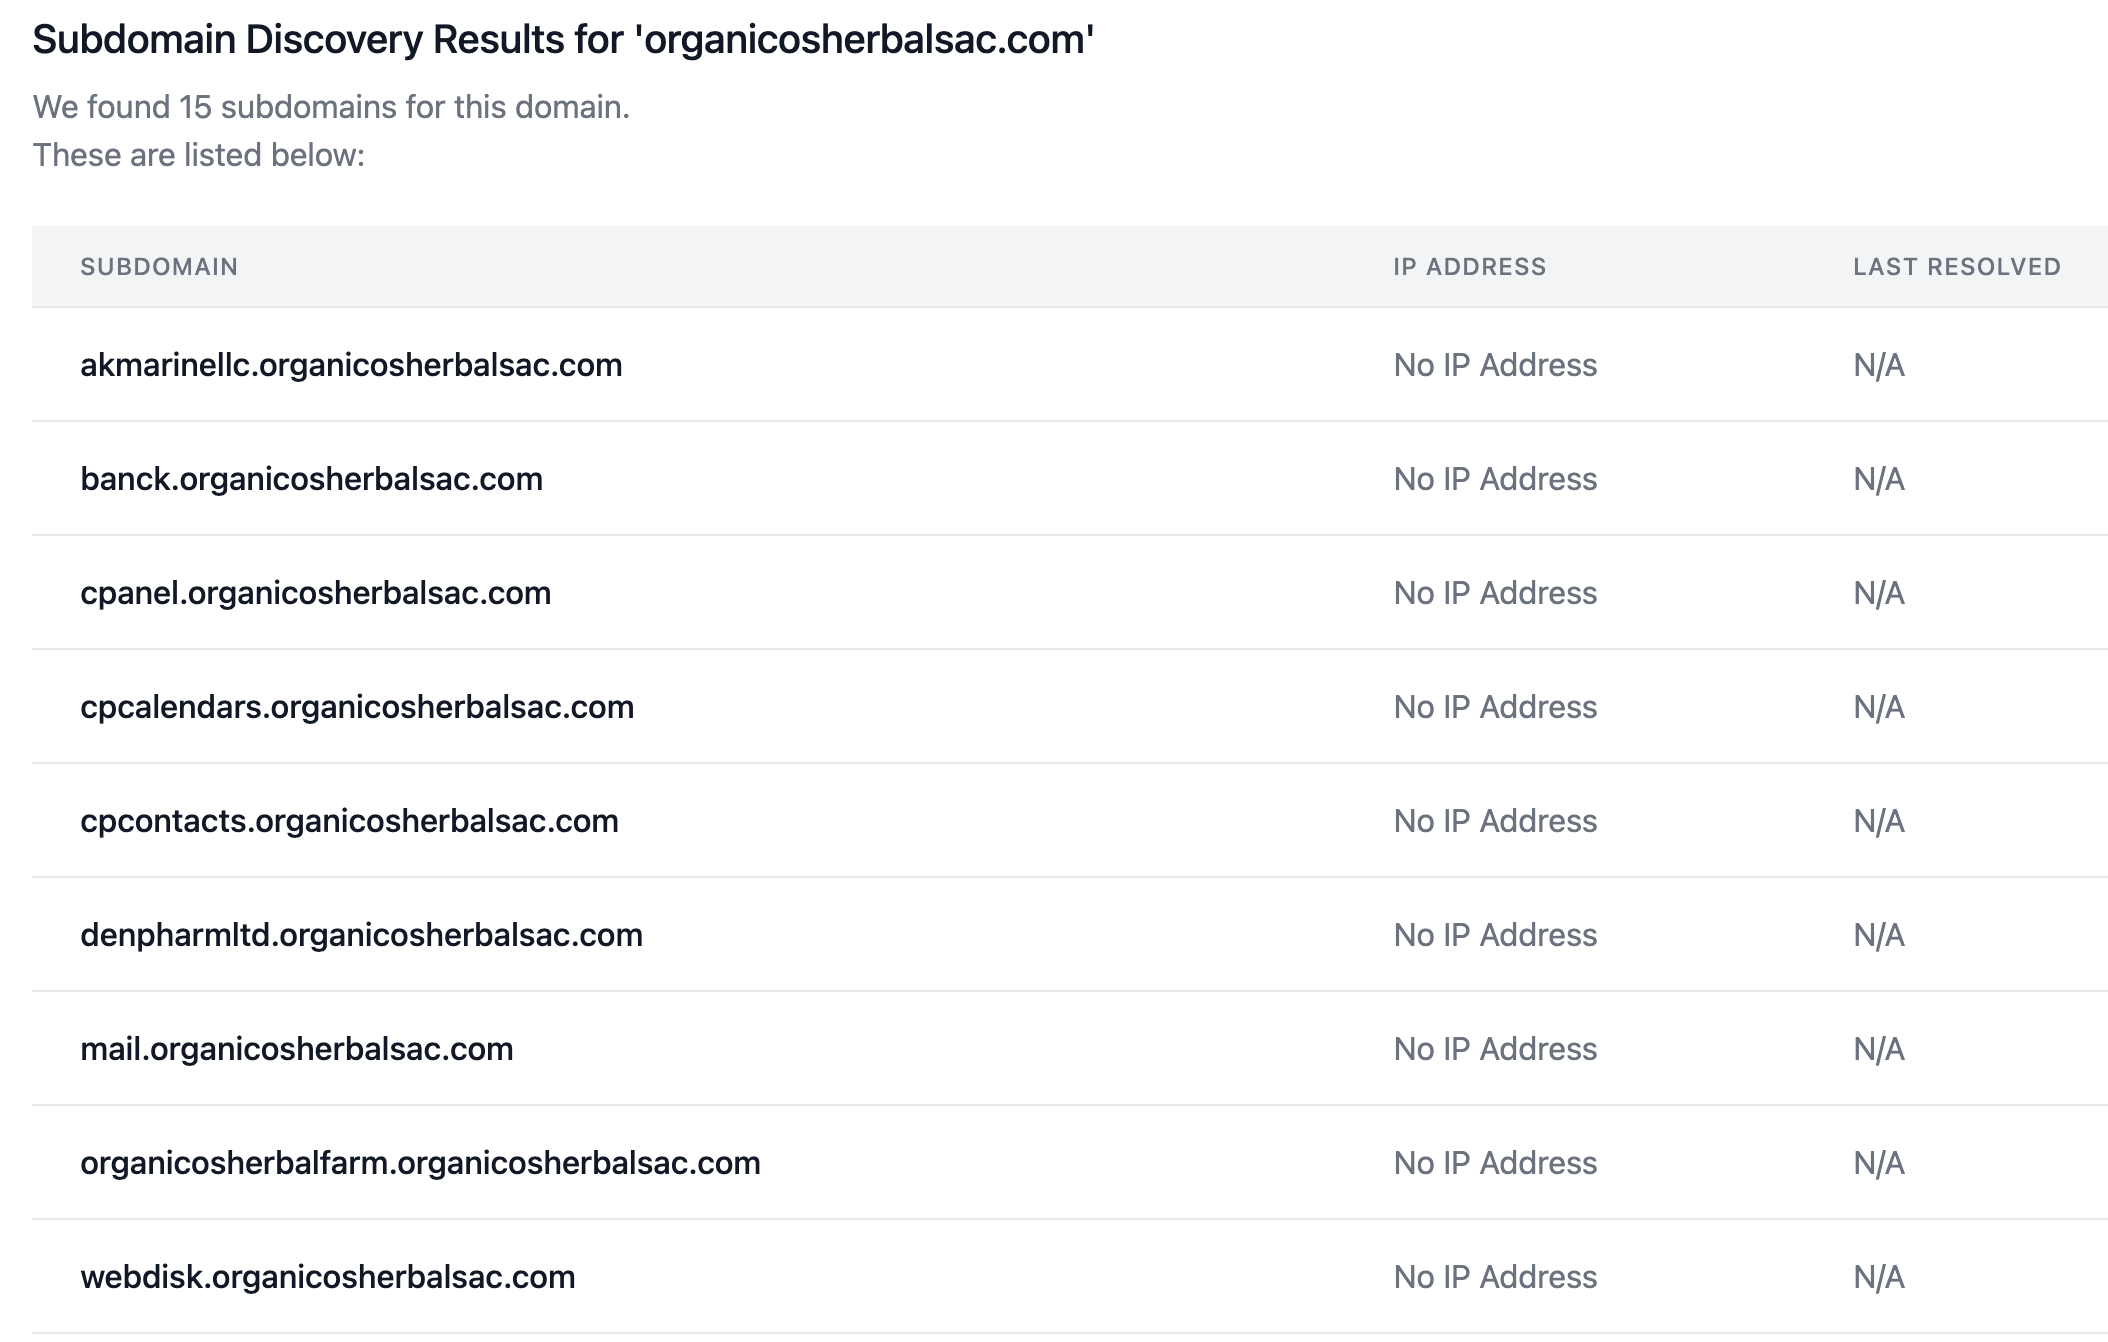
denpharmltd.organicosherbalsac.com
organicosherbalfarm.organicosherbalsac.com
akmarinellc.organicosherbalsac.com
banck.organicosherbalsac.com
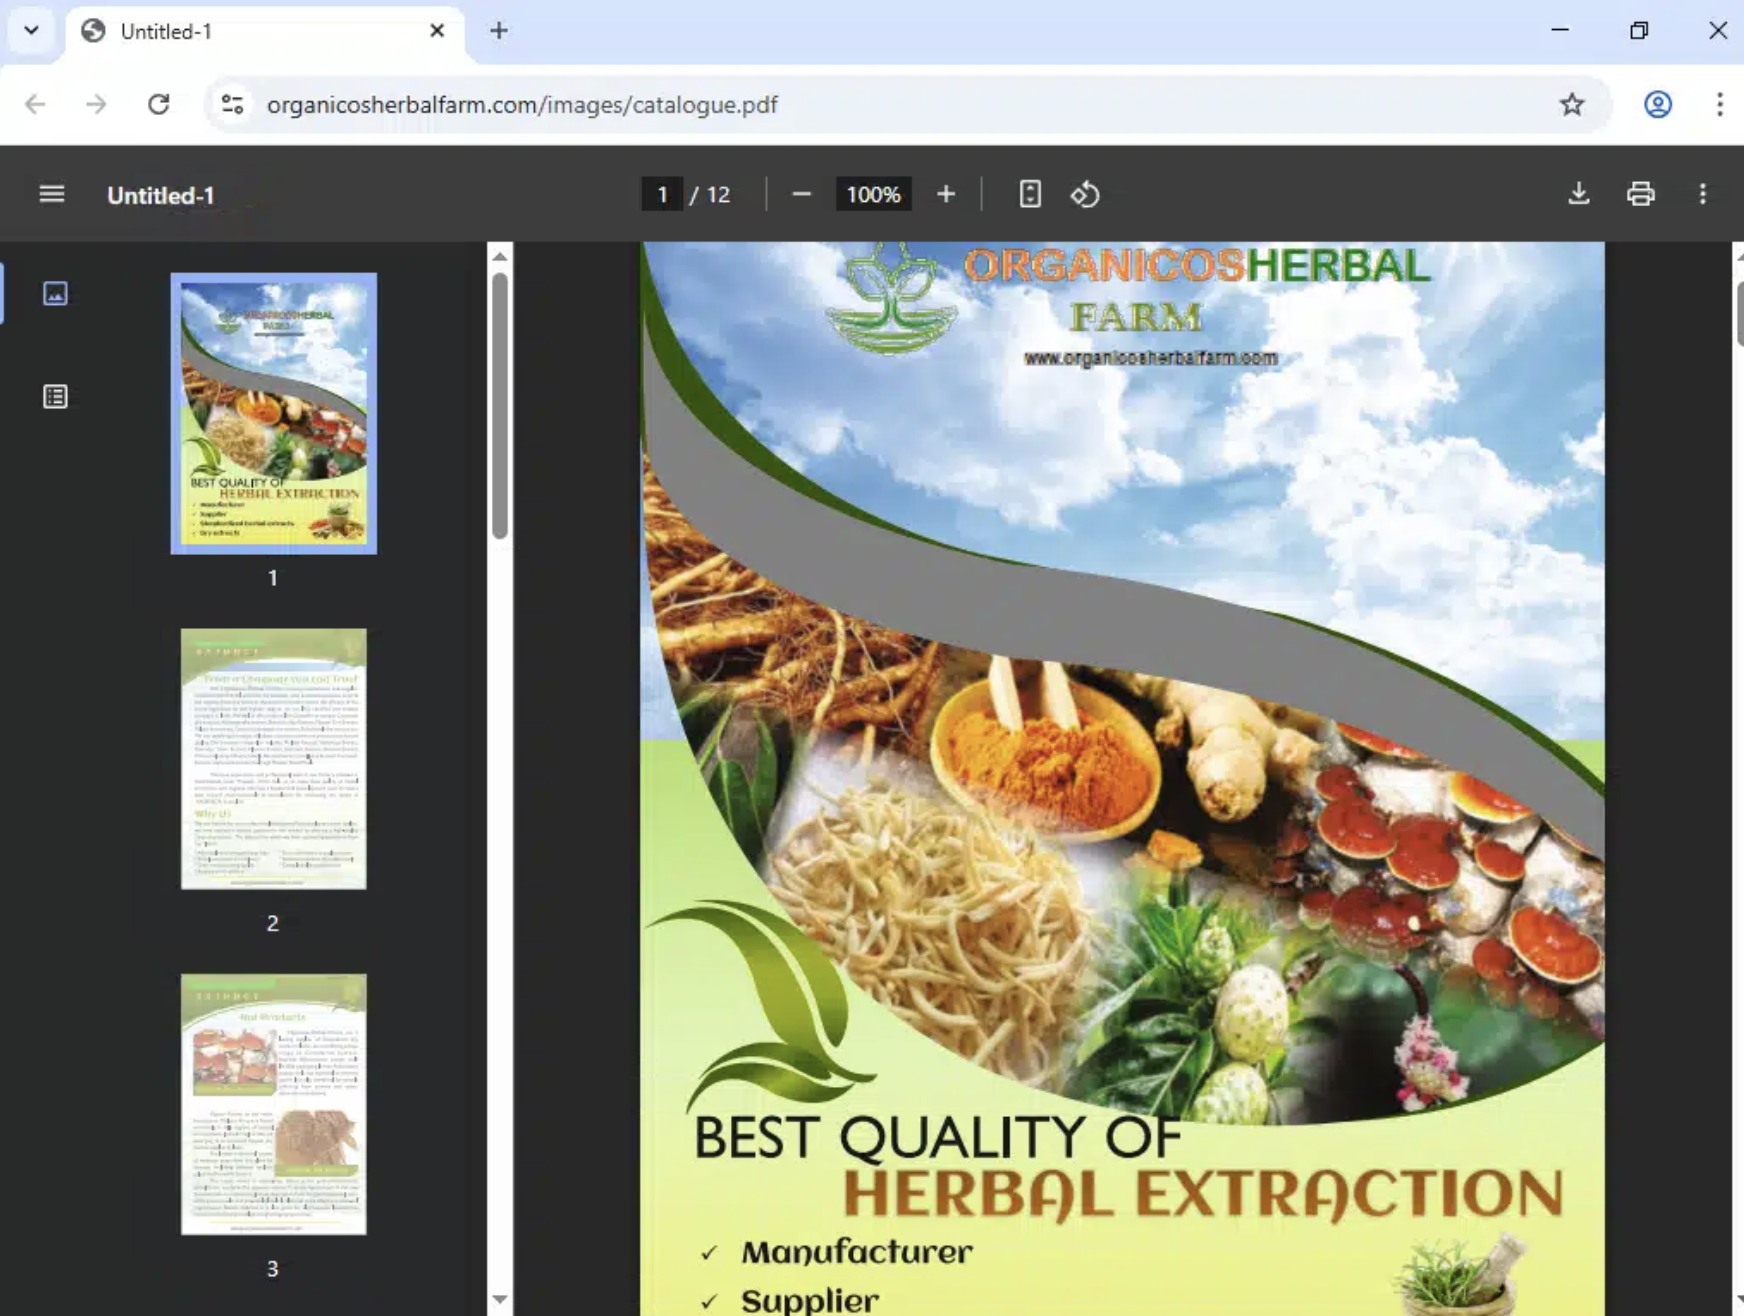
The last page carried the contact details:
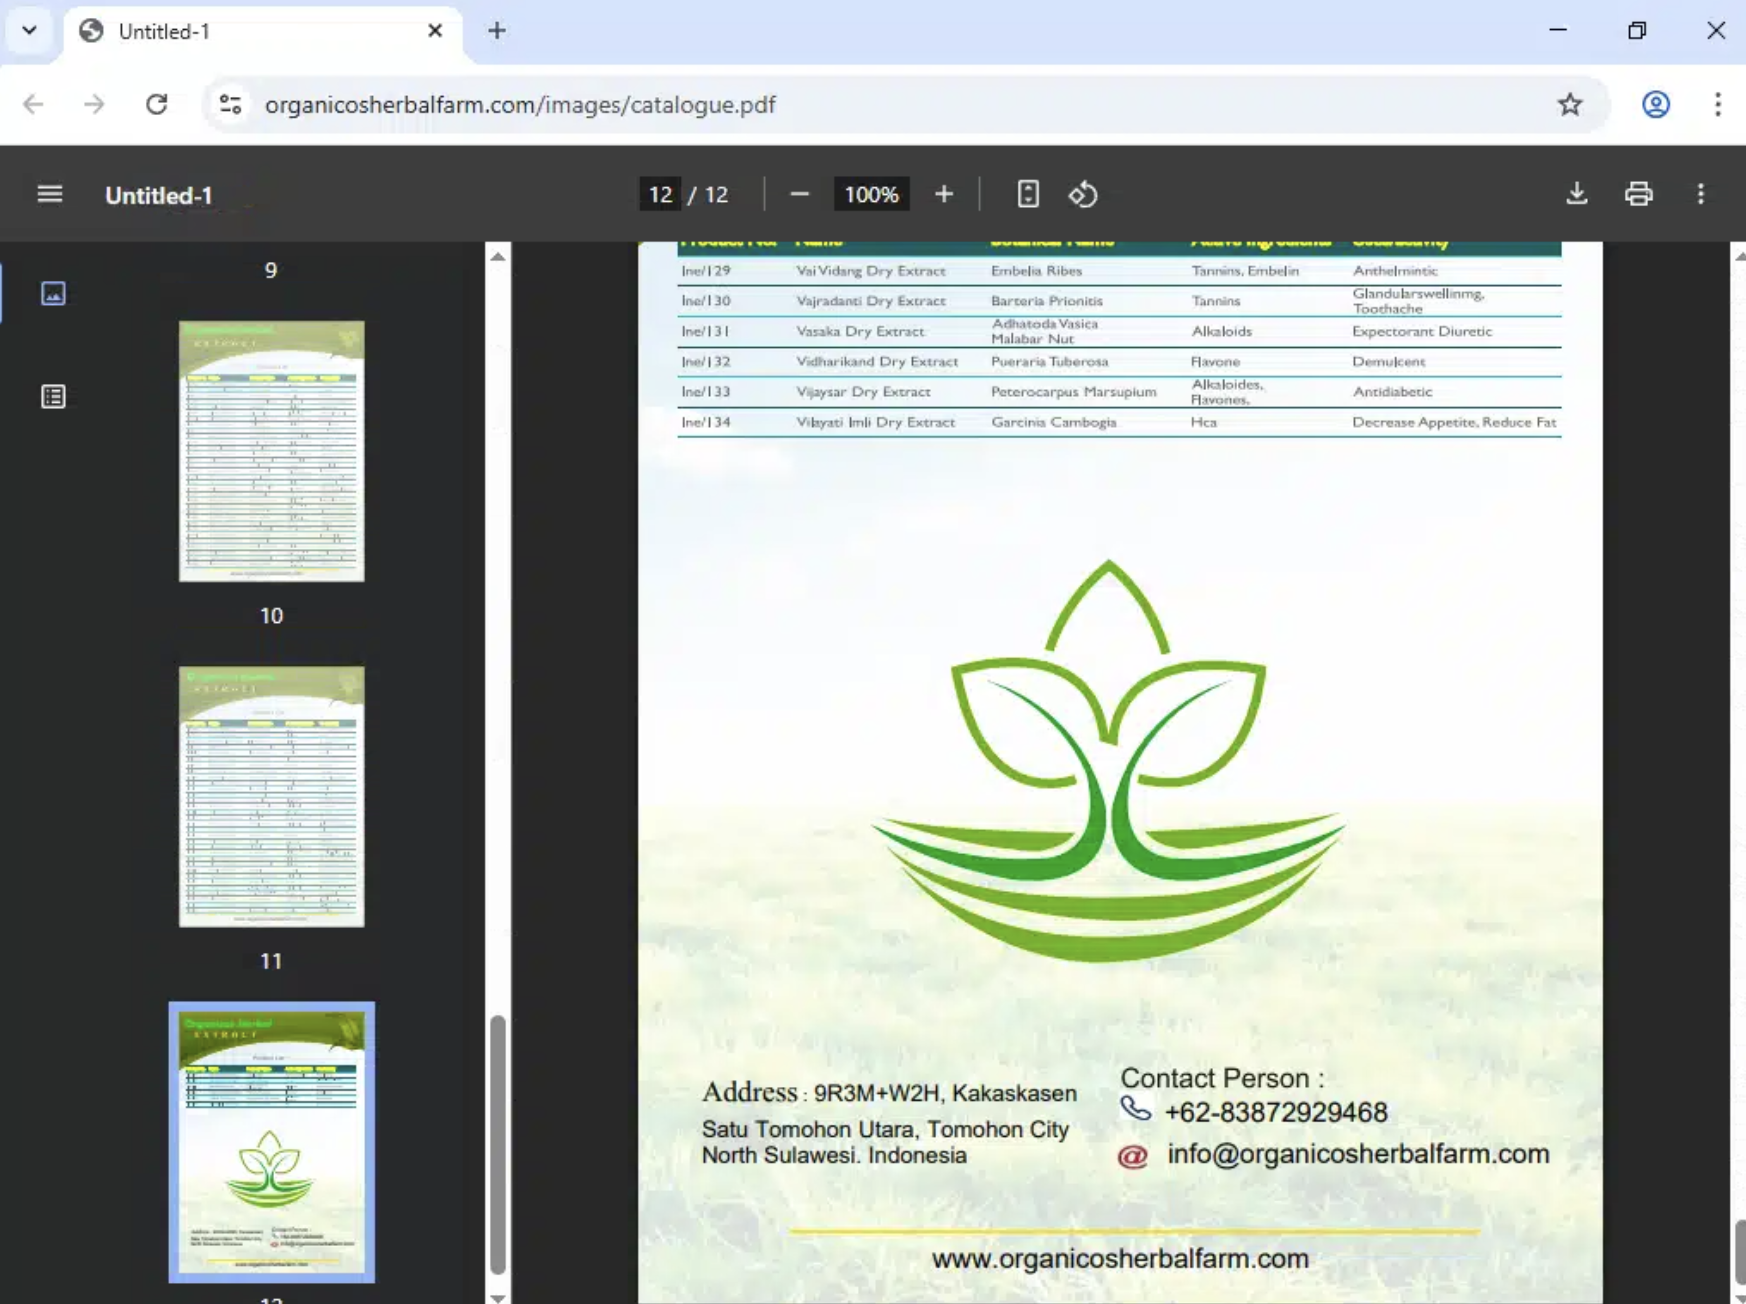
+62-83872929468
And because this cluster is sloppy, /images/ listed the site assets directly:
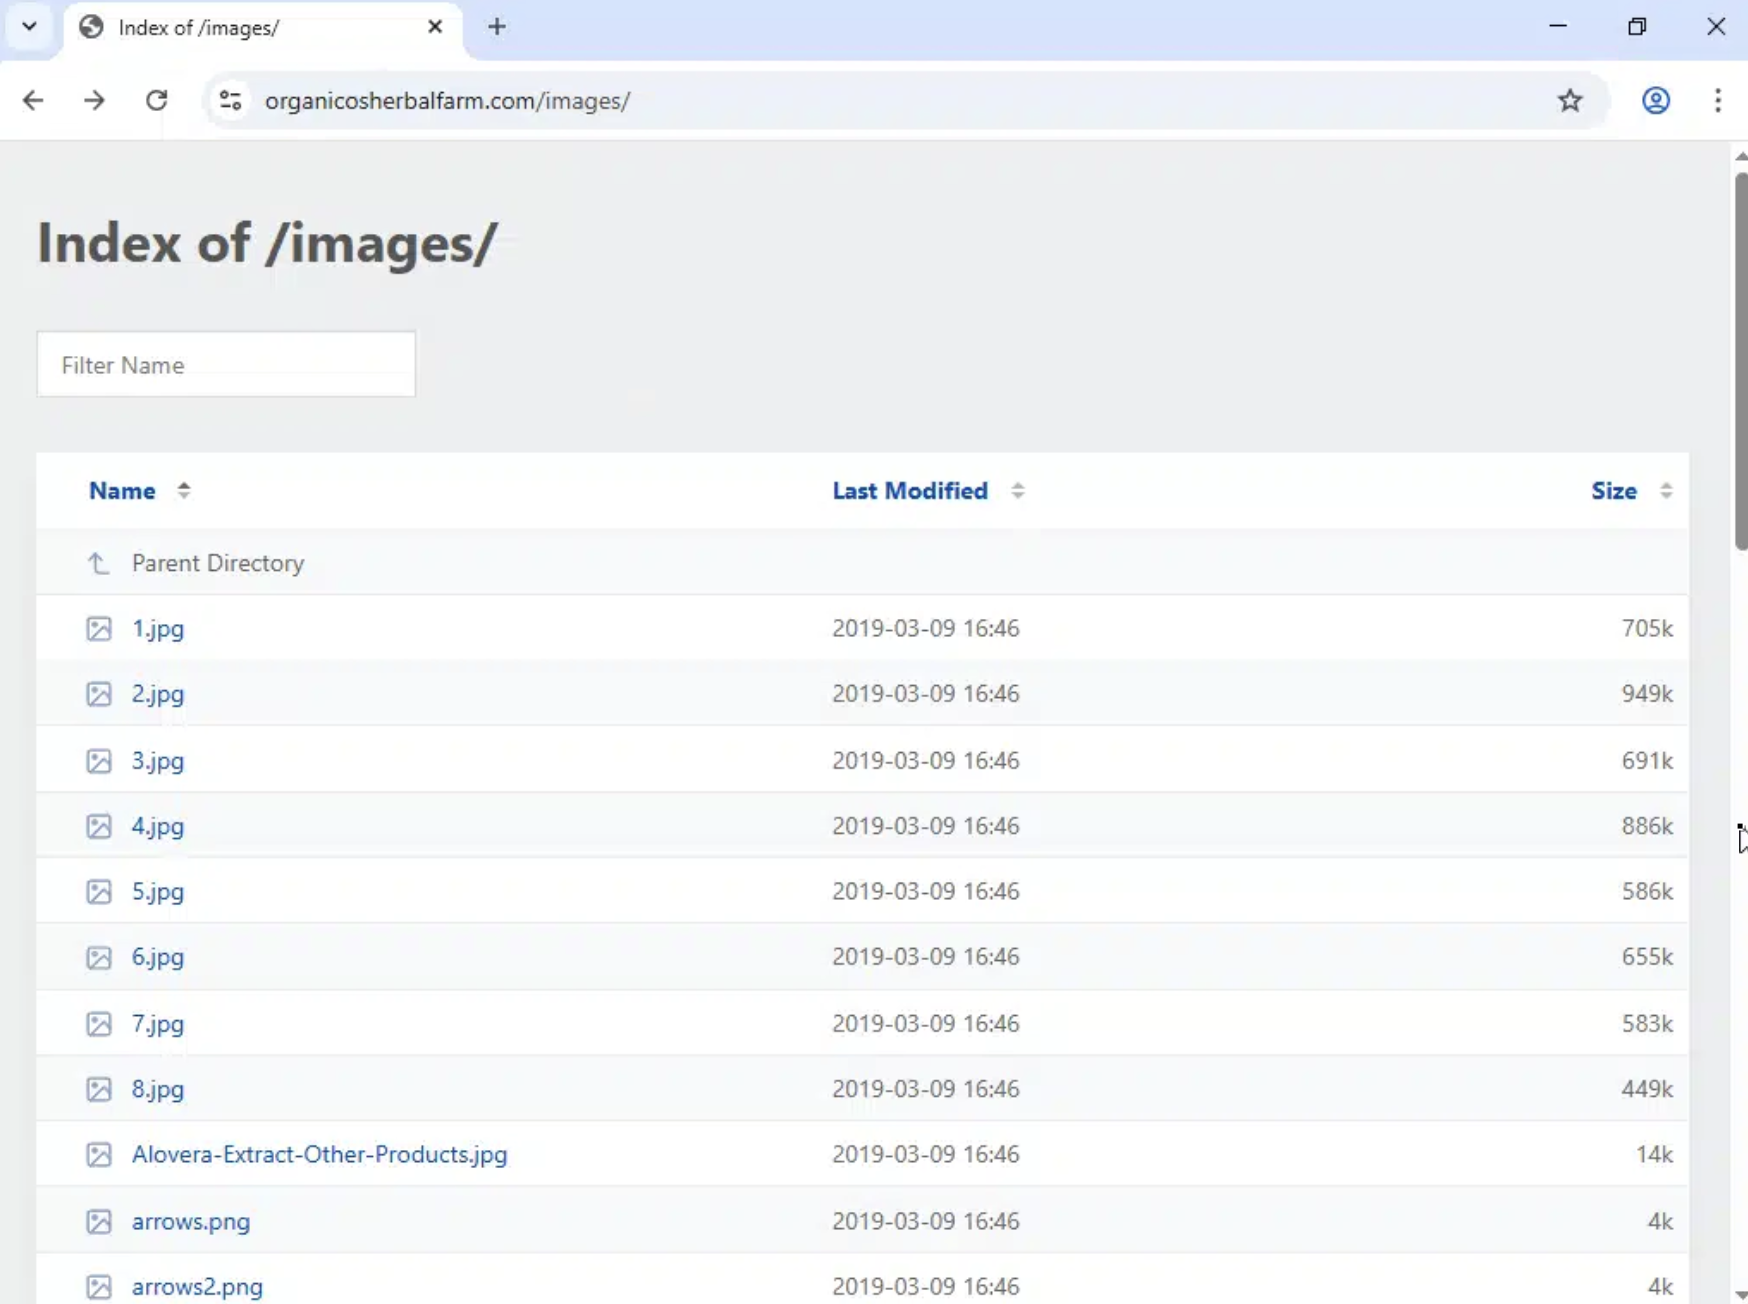
So the Denpharm/Organicos piece looks like an older procurement-scam branch: public warnings, cloned company sites, fake identity material, a product catalogue, and another nested-domain/certificate breadcrumb.
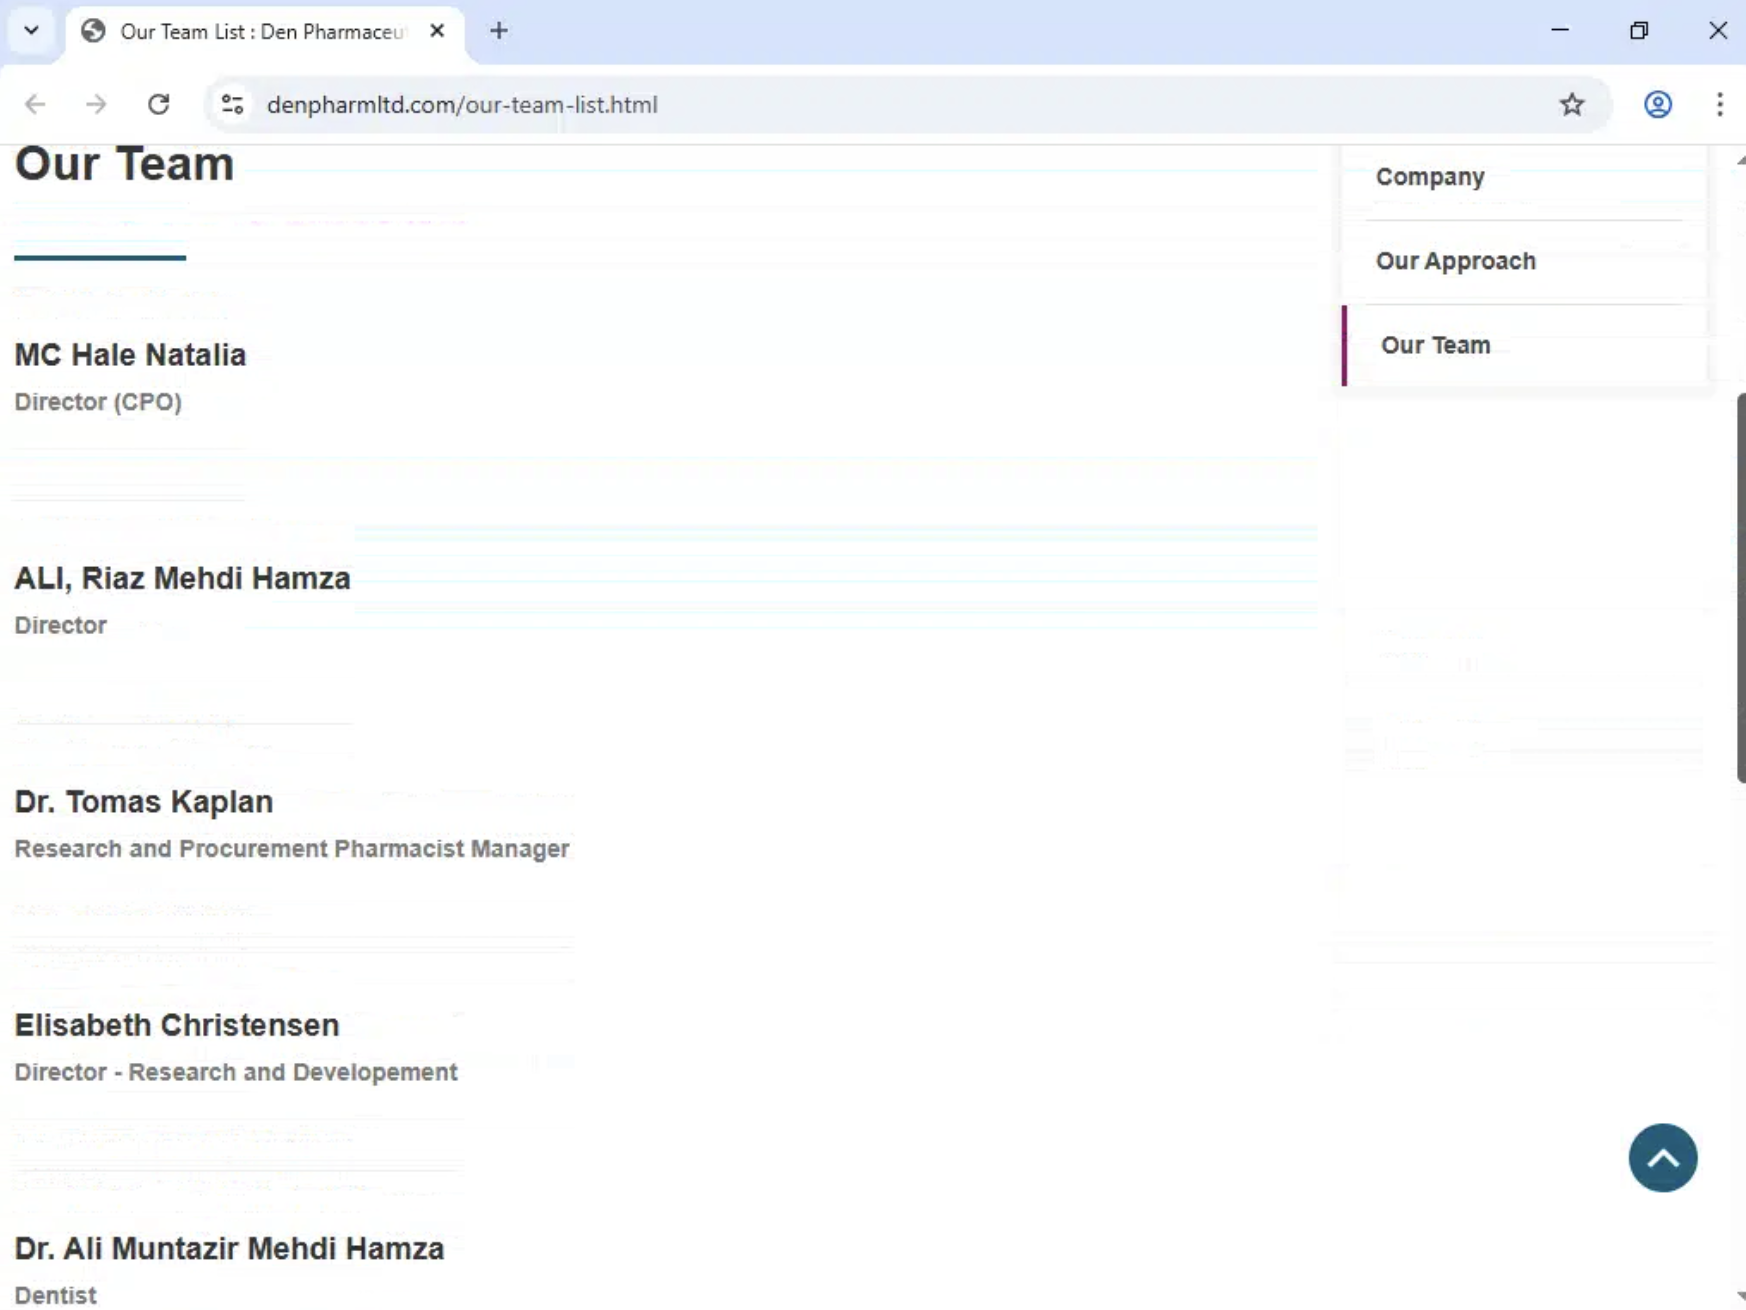
The Denpharm site itself still had a few helpful pages exposed. The team page included MC Hale Natalia and Dr. Tomas Kaplan, matching the names from the public warnings:
The contact page added more UK phone numbers:
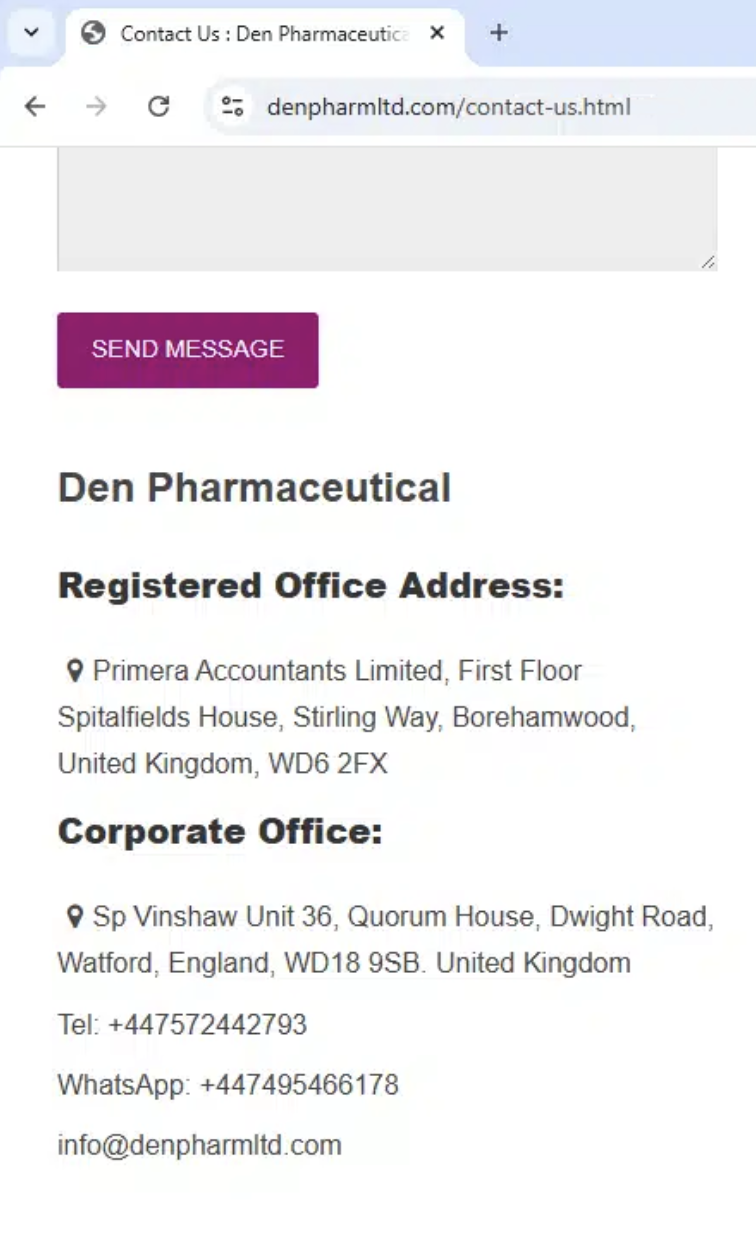
Tel:      +447572442793
WhatsApp: +447495466178
Email:    [email protected]
And index-2.html still carried the HTTrack timestamp:
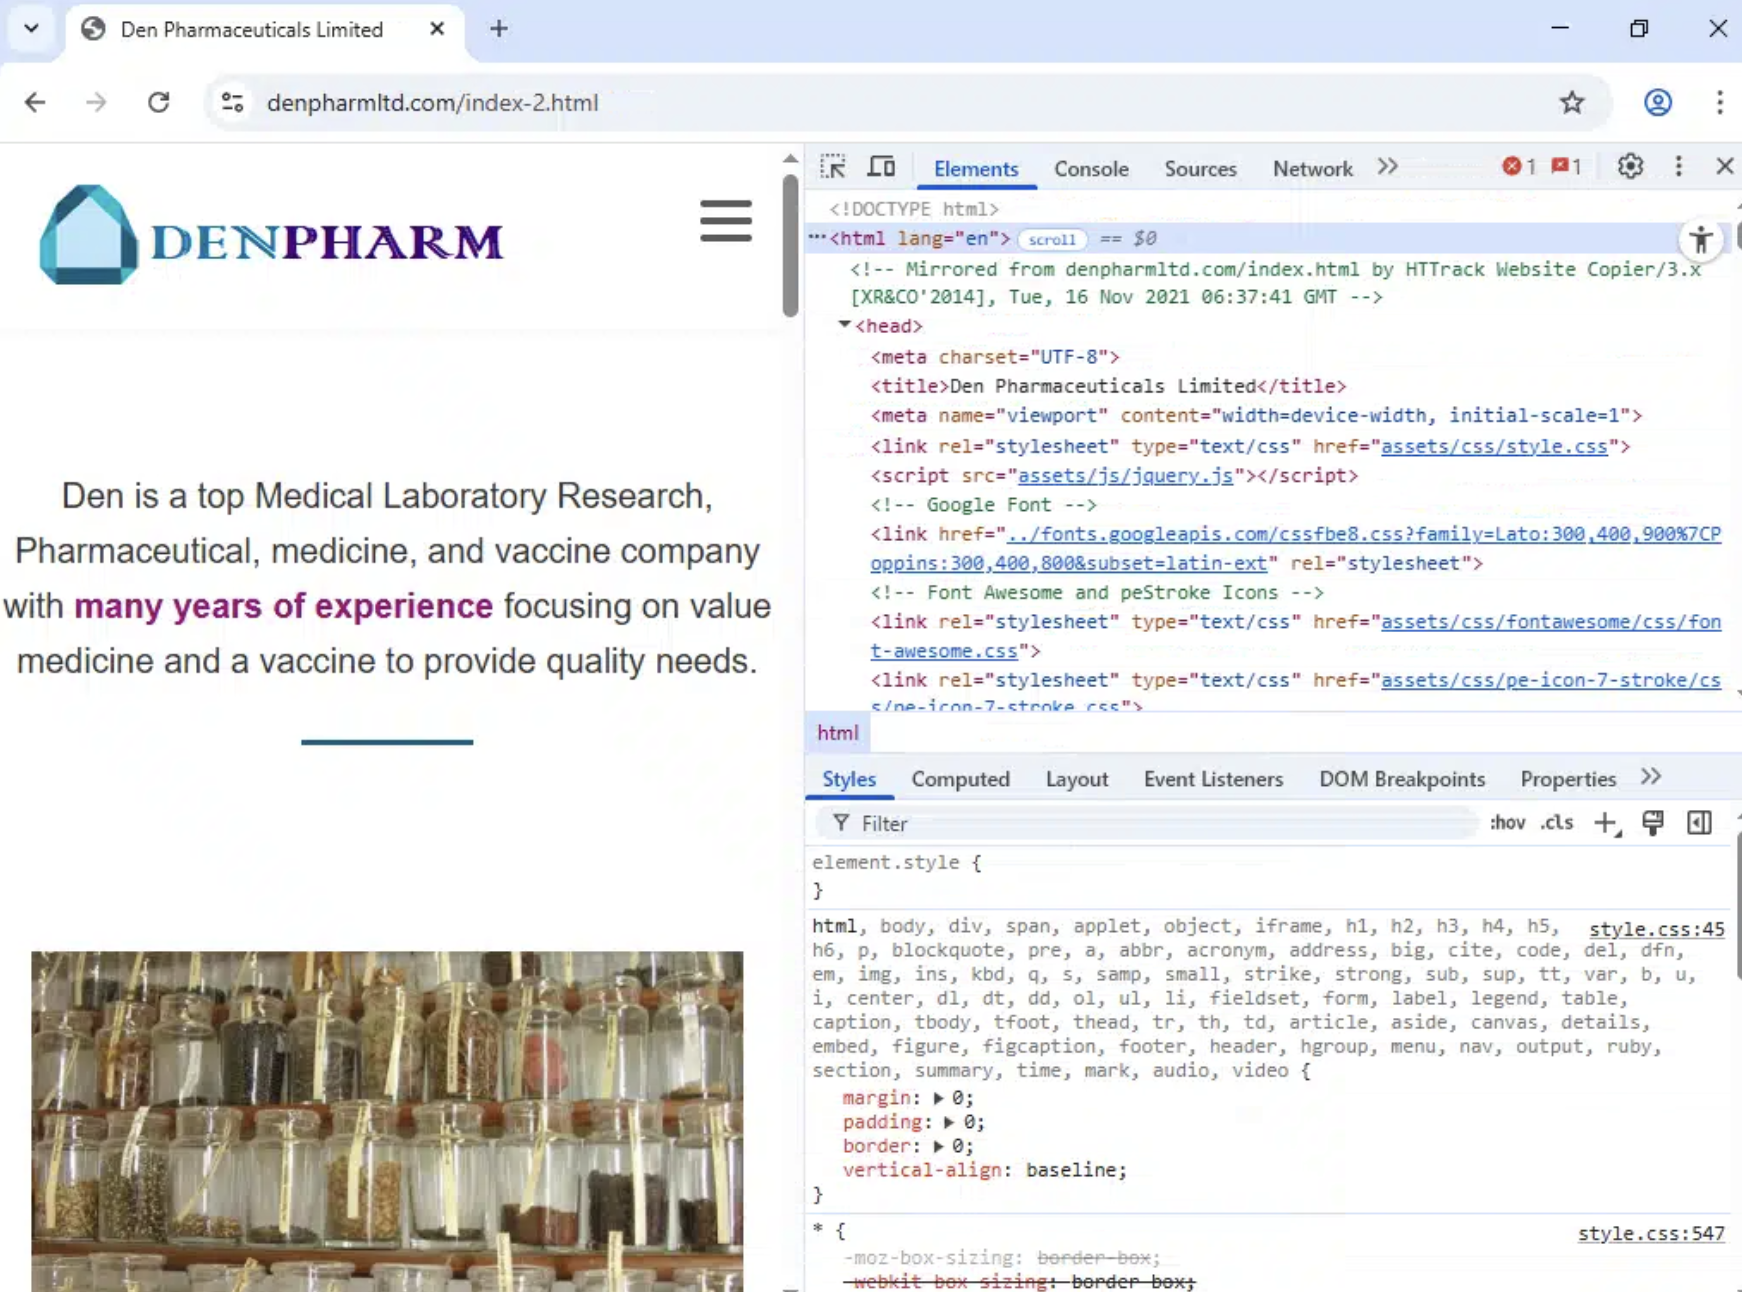
<!-- Mirrored from denpharmltd.com/index.html by HTTrack Website Copier/3.x
[XR&CO'2014], Tue, 16 Nov 2021 06:37:41 GMT -->
The "CND Logistics" theme also had a sibling-looking site:
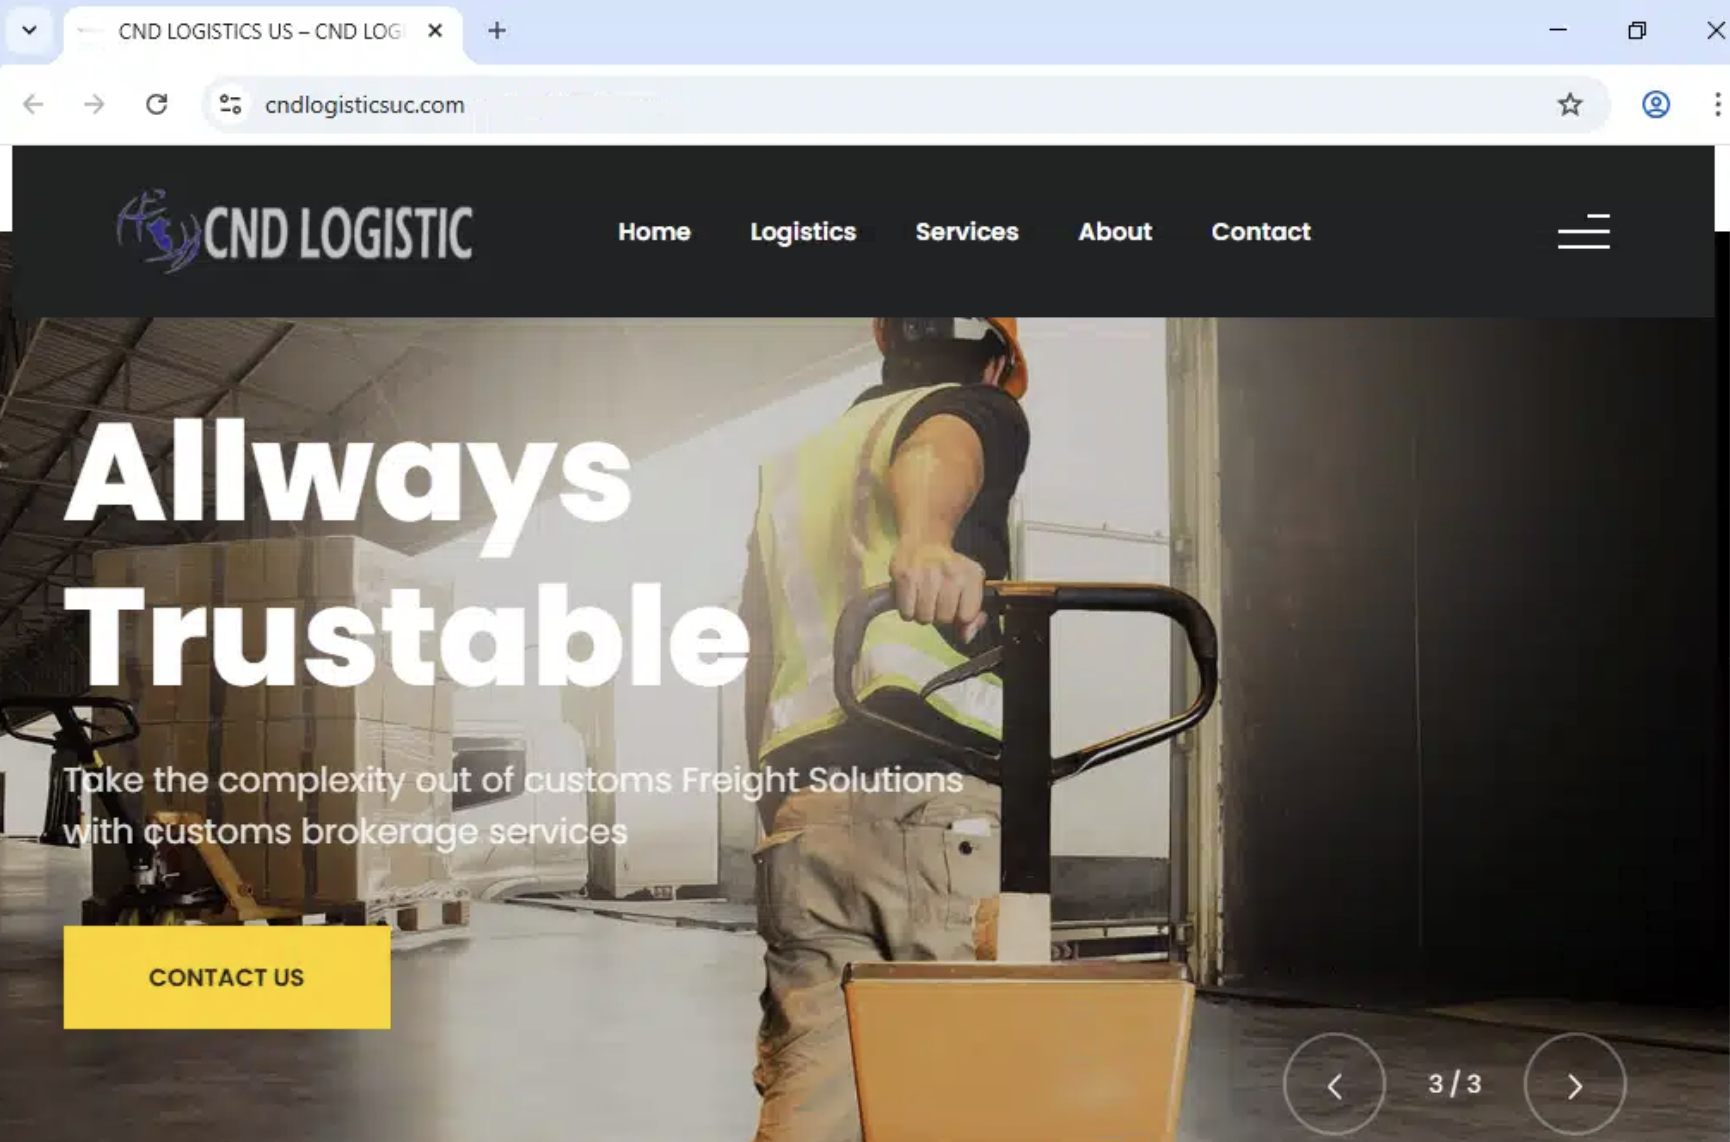
cndlogisticsuc.com
cndlogisticsuc.com.cndlogisticsid.com
Mail hosting surfaces
The fake pharma domains exposed the usual hosted-mail and control-panel elements:
autoconfig.kovdackpharmltd.com
autodiscover.kovdackpharmltd.com
cpanel.kovdackpharmltd.com
webmail.kovdackpharmltd.com
whm.kovdackpharmltd.com
mail.kovdackpharmltd.com
The autoconfig endpoint returned a Thunderbird-style XML profile:
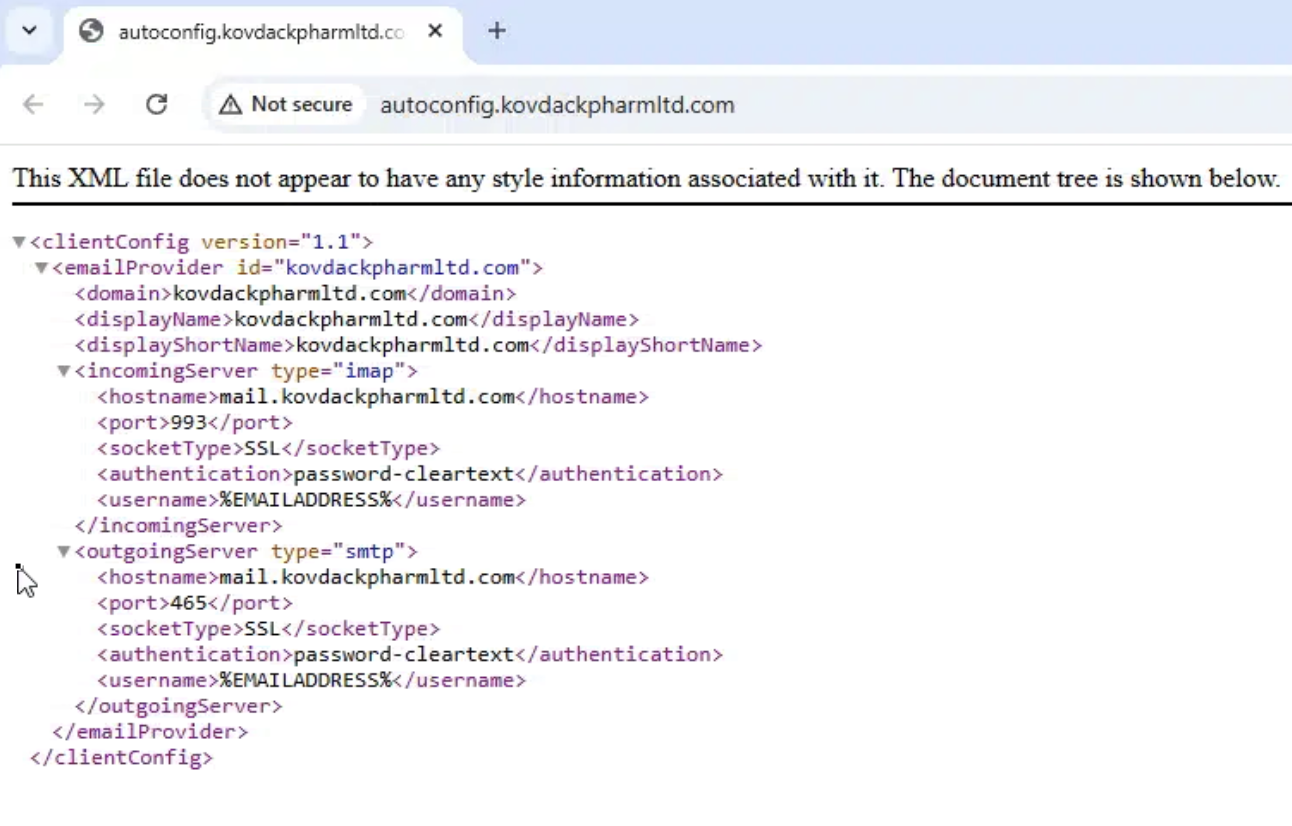
<emailProvider id="kovdackpharmltd.com">
  <domain>kovdackpharmltd.com</domain>
  <incomingServer type="imap">
    <hostname>mail.kovdackpharmltd.com</hostname>
    <port>993</port>
    <socketType>SSL</socketType>
    <authentication>password-cleartext</authentication>
  </incomingServer>
  <outgoingServer type="smtp">
    <hostname>mail.kovdackpharmltd.com</hostname>
    <port>465</port>
    <socketType>SSL</socketType>
    <authentication>password-cleartext</authentication>
  </outgoingServer>
</emailProvider>
noozkackpharmaltd.com (and others) exposed the same kind of autoconfig profile for its own mail host.
The mail-service pivot
movzenpharmltd.com used a shared mail exchanger at one point in the investigation. VirusTotal confirms the mail service touched by this cluster has suspicious community context:
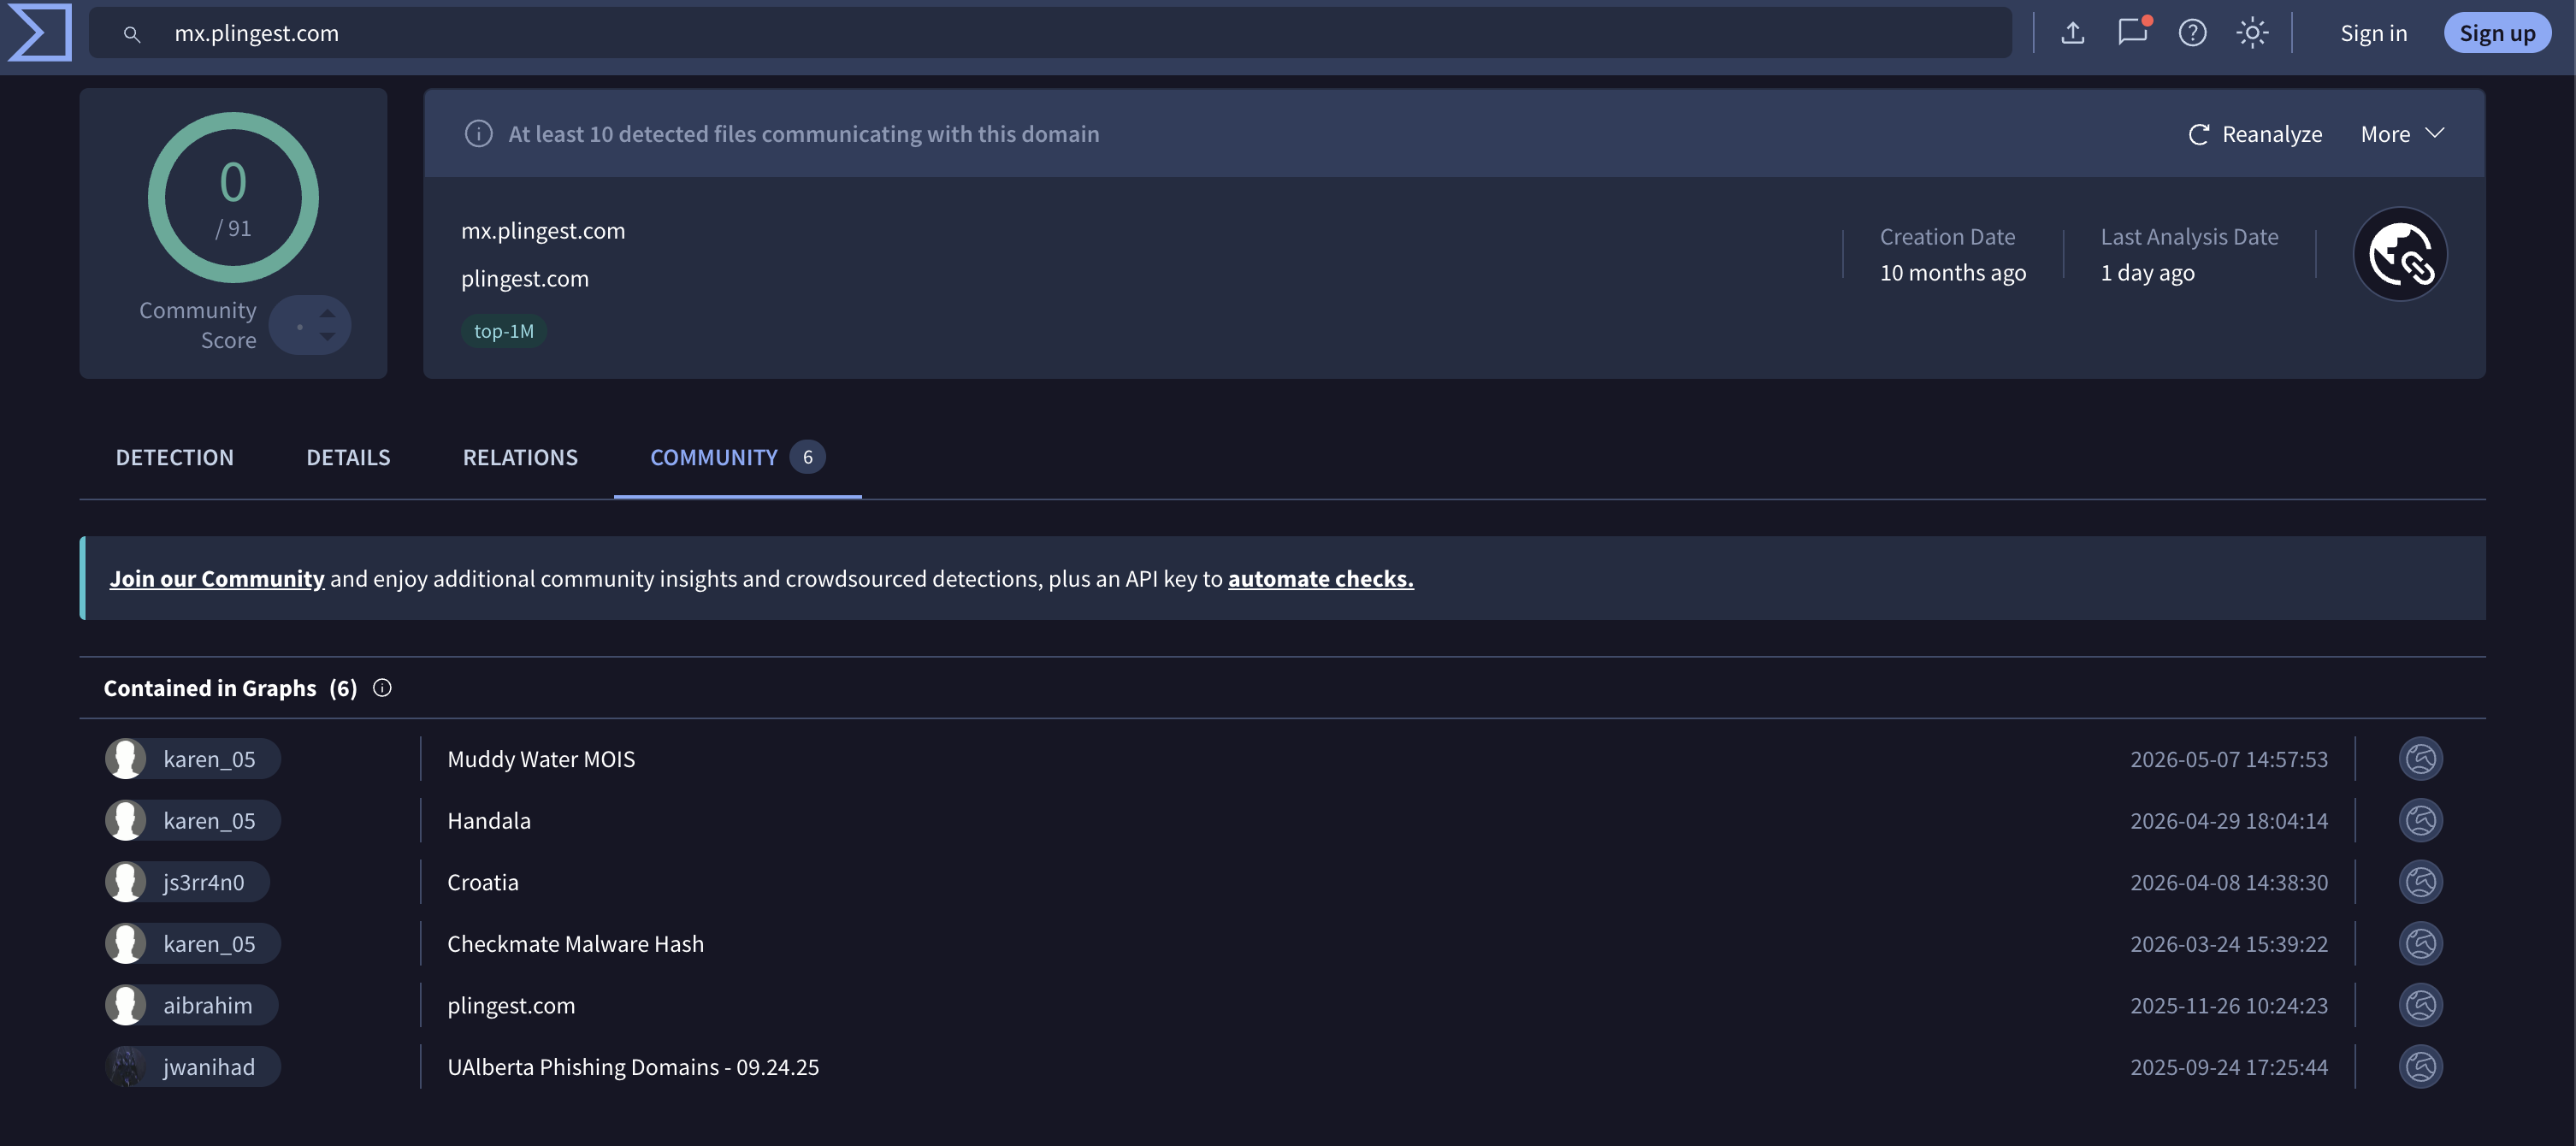
At least 10 detected files communicating with this domain

Contained in graphs:
- Muddy Water MOIS
- Handala
- Croatia
- Checkmate Malware Hash
- plingest.com
- UAlberta Phishing Domains - 09.24.25
Also, reverse-MX data showed a huge number of domains using that mail server. So, for IOC purposes, I am treating it as shared hosting/mail context rather than campaign-specific infrastructure.
IOCs
Email identities
Names and pseudonyms
DR. ROZENTAL ALEKSANDR
Tomas Kaplan
MC Hale Natalia
Andi Lesmana Jakarta
Baskoro Singgin
Domains and hostnames
markusnovanlaw.org
denpharmsltd.com
saipoveldar.com
kovdackpharmltd.com
noozkackpharmaltd.com
movzenpharmltd.com
dooxweckpharmaltd.com
cndlogisticsid.com
cndlogisticsuc.com
drpsf.site
drpsf.online
denpharmltd.com
organicosherbalfarm.com
organicosherbalsac.com
Nested hostnames
movzenpharmltd.com.cndlogisticsid.com
www.movzenpharmltd.com.cndlogisticsid.com
movzen-pharmltd.com.cndlogisticsid.com
www.movzen-pharmltd.com.cndlogisticsid.com
denpharmltd.com.cndlogisticsid.com
www.denpharmltd.com.cndlogisticsid.com
drpsf.online.cndlogisticsid.com
www.drpsf.online.cndlogisticsid.com
cndlogisticsuc.com.cndlogisticsid.com
www.cndlogisticsuc.com.cndlogisticsid.com
kovdackpharmltd.com.saipoveldar.com
www.kovdackpharmltd.com.saipoveldar.com
noozkackpharmaltd.com.saipoveldar.com
www.noozkackpharmaltd.com.saipoveldar.com
organicosherbalfarm.organicosherbalsac.com
www.organicosherbalfarm.organicosherbalsac.com
denpharmltd.organicosherbalsac.com
Exposed service hostnames
autoconfig.kovdackpharmltd.com
autodiscover.kovdackpharmltd.com
cpanel.kovdackpharmltd.com
webmail.kovdackpharmltd.com
whm.kovdackpharmltd.com
mail.kovdackpharmltd.com

autoconfig.noozkackpharmaltd.com
autodiscover.noozkackpharmaltd.com
ftp.noozkackpharmaltd.com
mail.noozkackpharmaltd.com
Reused visible contact values
+357 96 692 221
+357 95 550 432
+357 95 550 454
+357 96 910 893
+971 52 276 0126
+44 7572 443336
+62 83194188237
+62 83872929468
+62006283194188237
+44 7572 442793
+44 7495 466178
Detection Logic
IF
email authentication passes
AND the visible sender domain differs from the Reply-To domain
THEN
reply-chain fraud or BEC-style conversation starter likely
Observations & Conclusions
- SPF, DKIM, and DMARC passed, but authentication only proved control of the sending domain.
- The sender domain had a default CyberPanel page, not a credible law or doctor-related public site. (or even fake website prose).
- The
Reply-Todomain led into the fake pharma cluster. - The pharma sites retained HTTrack comments naming
www.delorbispharma.euas the mirrored source. - Kovdack, Noozkack, Movzen, and Dooxweck reused the same copied site structure with lightly edited names and contact details.
- Certificate and subdomain pivots exposed nested hostnames under
saipoveldar.comandcndlogisticsid.com, several of which were live and serving cloned business pages. - Mail autoconfig, webmail, cPanel, and WHM endpoints showed these domains were set up for operational mail.
- Public scam warnings tied
denpharmltd.comto an older procurement-scam script and paired it withorganicosherbalfarm.com. - The Organicos branch had the same clone residue: HTTrack comments, a copied herbal-extract source site, indexed catalogue material, and nested certificate names.
Very normal. Very business. Please acknowledge the proposal I allegedly sent yesterday.