Spam Tales: DocuSign Homoglyph Attack

Overview
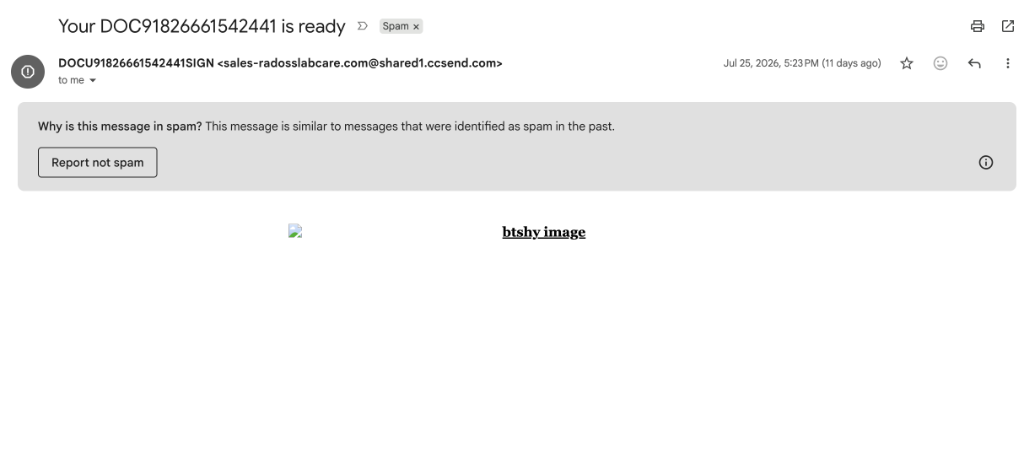
A sneaky brand impersonation attack hit my inbox disguised as an urgent DocuSign notification (Your DОϹU91826661542441 is ready).
This campaign used a combination of:
- homoglyph character substitution,
- email service provider (ESP) abuse,
- and open redirectors on compromised WordPress sites
Methodology
For this type of email lure, I like to preserve a few layers separately:
- Capture the rendered email and inbox spam warnings before interacting with links.
- Review the sender, recipient, timestamps, homoglyphs, and ESP authentication results.
- Inspect the raw HTML for hidden text, tracking, encoding tricks, and benign filler templates.
- Trace link redirects using sandbox analysis and isolated browser tools.
- Inspect the jump host environment, TLS certificate issuance history, and final landing page behavior.
- Extract reusable IOCs and construct detection logic.
Tools used
- Email source view for MIME structure, DKIM signatures, and homoglyph decoding
- Message authentication summary for SPF, DKIM, and DMARC results
- urlscan.io, urlquery, etc. sandbox for link expansion, TLS cert analysis, and HTTP redirect tracing
- Isolated browser inspection for domain, cPanel 404, and certificate details
Investigation
Email authentication
Raw Email Headers
Delivered-To: [email protected]
Received: by 2002:a05:6000:2981:20b0:470:1989:2b with SMTP id gl1-n2csp382087wrb; Sat, 25 Jul 2026 13:23:13 -0700 (PDT)
X-Received: by 2002:a05:622a:5b8b:b0:51c:11b4:6b24 with SMTP id d75a77b69052e-529a839eaf9mr30388281cf.3.1785010993037; Sat, 25 Jul 2026 13:23:13 -0700 (PDT)
ARC-Seal: i=1; a=rsa-sha256; t=1785010993; cv=none; d=google.com; s=arc-20260327; b=jc2U3u3oriGdaW3zKhRYbGj1CEYlYmguRS38AGYWbm8gveX7B86yYUiO0s0M7iBbF2 oVDANLiIYuaaZQGLDR0reqgBwZ8FaapypyN+eIFQQz13zOY69Kl91hlnt6APsmrCAEHz sq0bNJ+peR+l8qiavAjPF2K5scMRiVfpMmbRRmfX2oPTgZ1dZulB3VJCPiIRG3SE0UgA IdHcvE/1RTizvnx90LUIZreYH0JuUkw7/NWyH12XmRUgpHlddjT1Q62SLZC40bC1RbVo IxK/+z1OEzVDa0Zb3lExn0fV0gWFDHAWSa0tW8rLXR8b/7vr46YzjAEp8StEqQvWTrVG IM1g==
ARC-Message-Signature: i=1; a=rsa-sha256; c=relaxed/relaxed; d=google.com; s=arc-20260327; h=list-unsubscribe-post:list-unsubscribe:mime-version:subject:to :reply-to:from:date:message-id:dkim-signature:dkim-signature; bh=rEOILjV78ogHqX9MMMMGWZeCQ79y6ZHG/KxudsG5+H0=; fh=XM/DofkuIl8YxShyFh70zFRSv5HB1tzZL88CBxycvV0=; b=LQlyyeXe/82+ggZ+ecguRc8Bje5rKaICVaN8WfK5VGyNFWTtyCOZzIU+CSm26mtsoX aNt9hp0qgqo9fn3Rw+eL0dko0WoNQqiczHBcZSMvSG3csckaZQm6u4JF80aP0lH6AIBD 6FDNtr6KqPcT6INOkyjqb4SxVfDqrw1qPf90MqqP/2n1br3LQvOUx8bXrgZAAXu2lpVJ 34jLj4tWdHVd/IC/kNSaNad4jEb7qOgTZ8woyPaOq1Q7xZ6WZoM6LhkbzP/jM/9f9d/D 5ON5Vdpt+1LGYflnucMF849tTvHOtj4S45LwJ8gELIH1LEUJ1eiudFDXF+aS6/+cXbeF S8KQ==; dara=google.com
ARC-Authentication-Results: i=1; mx.google.com; dkim=pass [email protected] header.s=12042023 header.b=GhADEAp8; dkim=pass [email protected] header.s=1000073432 header.b=BQKKmA2h; spf=pass (google.com: domain of avmjokt7ttosjvgioqix2pq==_1142334191866_tcsumohmefg6vqjccjiaaw==@in.constantcontact.com designates 208.75.123.235 as permitted sender) smtp.mailfrom="AvMjokt7tTOSJVgiOqIX2PQ==_1142334191866_TCSUMohmEfG6vQJCCjIAAw==@in.constantcontact.com"; dmarc=pass (p=REJECT sp=REJECT dis=NONE) header.from=ccsend.com
Return-Path: <AvMjokt7tTOSJVgiOqIX2PQ==_1142334191866_TCSUMohmEfG6vQJCCjIAAw==@in.constantcontact.com>
Received: from ccm235.constantcontact.com (ccm235.constantcontact.com. [208.75.123.235]) by mx.google.com with ESMTPS id d75a77b69052e-529a2b0c0f6si37975291cf.265.2026.07.25.13.23.12 for <[email protected]> (version=TLS1_3 cipher=TLS_AES_256_GCM_SHA384 bits=256/256); Sat, 25 Jul 2026 13:23:13 -0700 (PDT)
Received-SPF: pass (google.com: domain of avmjokt7ttosjvgioqix2pq==_1142334191866_tcsumohmefg6vqjccjiaaw==@in.constantcontact.com designates 208.75.123.235 as permitted sender) client-ip=208.75.123.235;
Authentication-Results: mx.google.com; dkim=pass [email protected] header.s=12042023 header.b=GhADEAp8; dkim=pass [email protected] header.s=1000073432 header.b=BQKKmA2h; spf=pass (google.com: domain of avmjokt7ttosjvgioqix2pq==_1142334191866_tcsumohmefg6vqjccjiaaw==@in.constantcontact.com designates 208.75.123.235 as permitted sender) smtp.mailfrom="AvMjokt7tTOSJVgiOqIX2PQ==_1142334191866_TCSUMohmEfG6vQJCCjIAAw==@in.constantcontact.com"; dmarc=pass (p=REJECT sp=REJECT dis=NONE) header.from=ccsend.com
DKIM-Signature: v=1; q=dns/txt; a=rsa-sha256; c=relaxed/relaxed; s=12042023; d=shared1.ccsend.com; h=date:mime-version:subject:X-Feedback-ID:X-250ok-CID:message-id:from:reply-to:list-unsubscribe:list-unsubscribe-post:to; bh=rEOILjV78ogHqX9MMMMGWZeCQ79y6ZHG/KxudsG5+H0=; b=GhADEAp8Hl9mtinYMtmO7cWOCCfkJyHS3LNc2GWRAtNuJWkNoGaHi/9Mn5AC0R2x9gCnUJFU7NBOSCUkOpKM4jh7X9HwBKw/oJVofst4COXz82o/q9PG0ttDxYEjJnZRNnGjO4llhMuHa83FUIopPb9YhHcdS2ylLTsTmApBftJNwQpSi4vBJArC827YX/CW9PMDYCegUeRKUtiZJDhuMYVLLHF2LJxnYzqGoXW5Xoh89J8txf05xq9DXOiZtF//rulJJX5JvVb9cBjSPEGgm1n01mXrLLzGjX5y4f3yfpIpHT8yEFl6cERimZTUiR13jrd/q3TNqfA2fJr7RQ4IWw==
DKIM-Signature: v=1; q=dns/txt; a=rsa-sha256; c=relaxed/relaxed; s=1000073432; d=auth.ccsend.com; h=date:mime-version:subject:X-Feedback-ID:X-250ok-CID:message-id:from:reply-to:list-unsubscribe:list-unsubscribe-post:to; bh=rEOILjV78ogHqX9MMMMGWZeCQ79y6ZHG/KxudsG5+H0=; b=BQKKmA2hm8ll5kaH7Ta9cQdLtzW8O7KwoNkUV8ZpGduqEjcTTy2kyV3dyXK3iNE97k60jRjTTxISdFivzZh51sT8dzwirbvnsZiy6kcjRJemEYQWj6Eu05Ao4xROp38tMCeUnoDVyG2E+nGKpsPIztEjqgrOBgcDnL9H7gA7wsg=
Message-ID: <1142334703227.1142334191866.1072553232.0.291622JL.2002@synd.ccsend.com>
Date: Sat, 25 Jul 2026 16:23:12 -0400 (EDT)
From: =?utf-8?Q?D=D0=9E=CF=B9U91826661542441=D0=85=D0=86G=CE=9D?= <[email protected]>
Reply-To: [email protected]
To: [email protected]
Subject: =?utf-8?Q?Your_D=D0=9E=CF=B991826661542441_is_ready?=
MIME-Version: 1.0
Content-Type: multipart/alternative; boundary="----=_Part_275054477_708520069.1785010992844"
List-Unsubscribe: <https://visitor.constantcontact.com/do?p=un&m=001st0JLJ3BRgXpr0CayrEO5A%3D%3D&se=001cBN8W11zlBDfFajHrVJgTw%3D%3D&t=001EkZLEx15CcE%3D&llr=9h5yg7hbb>
List-Unsubscribe-Post: List-Unsubscribe=One-Click
X-Campaign-Activity-ID: bcc8e892-deed-4ce4-8956-088ea885f63d
X-250ok-CID: bcc8e892-deed-4ce4-8956-088ea885f63d
X-Channel-ID: 4c249432-8866-11f1-babd-02420a320003
X-Return-Path-Hint: AvMjokt7tTOSJVgiOqIX2PQ==_1142334191866_TCSUMohmEfG6vQJCCjIAAw==@in.constantcontact.com
X-Roving-Campaignid: 1142334703227
X-Roving-Id: 1142334191866.1072553232
X-Feedback-ID: 4c249432-8866-11f1-babd-02420a320003:bcc8e892-deed-4ce4-8956-088ea885f63d:1142334191866:CTCT
X-CTCT-ID: 4c14f3f6-8866-11f1-babd-02420a320003
The message presented itself as:
From: DОϹU91826661542441ЅЅGΝ <[email protected]>
Reply-To: [email protected]
Subject: Your DОϹU91826661542441 is ready
Date: Sat, 25 Jul 2026 16:23:12 -0400
Observed authentication results:
SPF:   PASS (google.com: domain of constantcontact.com designates 208.75.123.235 as permitted sender)
DKIM:  PASS (shared1.ccsend.com and auth.ccsend.com)
DMARC: PASS (p=REJECT header.from=ccsend.com)
Because Constant Contact (ccm235.constantcontact.com / 208.75.123.235) is a legitimate bulk email marketing platform, the message passed all standard email authentication checks.
To evade automated Natural Language Processing (NLP) anti-phishing rules that flag words like DocuSign, the attacker replaced standard Latin characters with visually identical Cyrillic and Greek Unicode characters:
- Subject String:
DОϹU91826661542441О→ Cyrillic Capital Letter O (U+041E)Ϲ→ Greek Lunate Sigma Symbol (U+03F2)
- Sender Display Name:
DОϹU91826661542441ЅЅGΝЅ→ Cyrillic Capital Letter Dze (U+0405)Ν→ Greek Capital Letter Nu (U+039N)
HTML filler
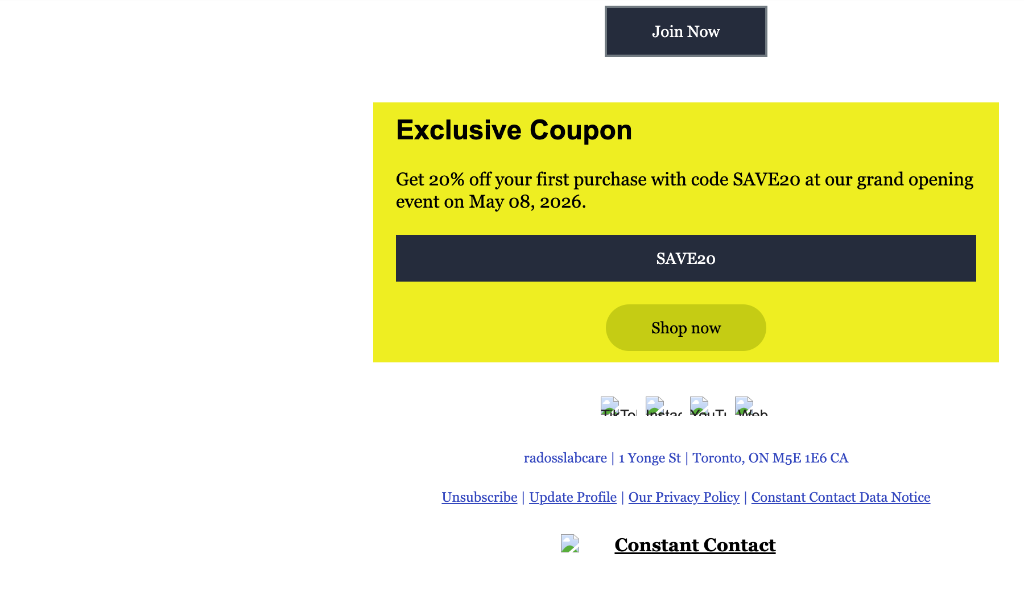
The HTML and plain text bodies contained a complete template for a business (radosslabcare) with a discount code (SAVE20).
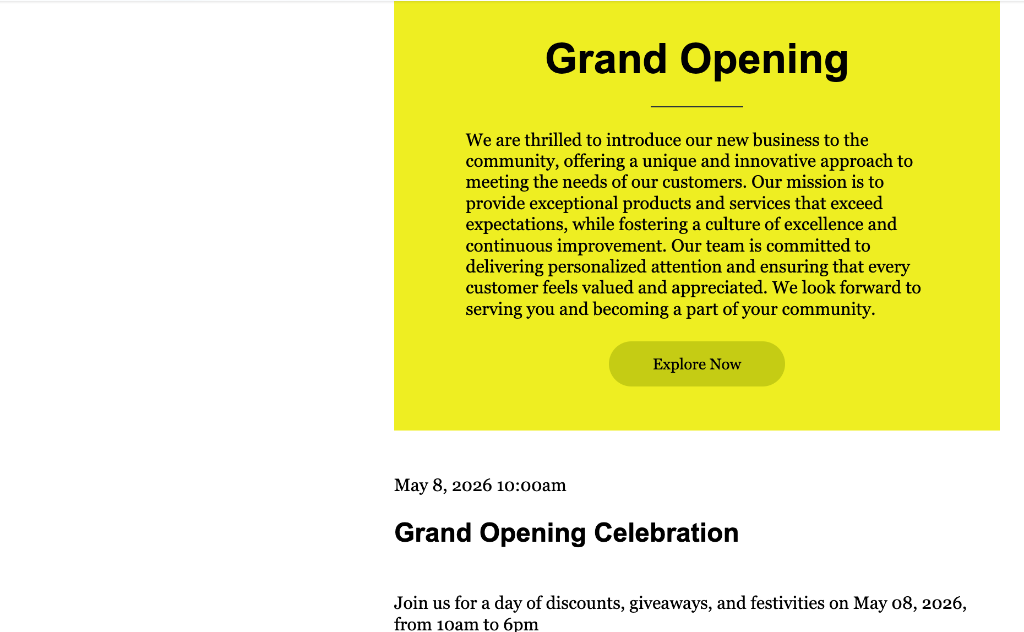
Inserting benign commercial text serves a dual purpose:
- Classifier Confusion: Spam filters scoring content intent classify the body as a standard commercial promotional message.
- Hidden Links: The actual visual link is tied to a large transparent overlay image pointing to the attacker's infrastructure.
Original links
The primary link embedded in the message was wrapped via Constant Contact's tracking service:
https://9h5yg7hbb.cc.rs6.net/tn.jsp?f=001_jBSTymjOra5YfUT2qw9hXuChXdeMd26MdFnOw_DbLc1sErBjhURTLTMTGY1qUhLe-CFnbKIXq--vZW5n-j2kJY3Ppl89Kbs5dsCembTC1ceSa8NM80a0Sj8U1OOYU5GfqnHWCBbUfIr8gOQSqNt3YSq9_e4B0uJ
Which resolved to the first-stage jump host:
https://mcguiganflooring.com/mcguiganflooring/
Unsubscribe behavior
The message included standard Constant Contact unsubscribe headers and footer links:
List-Unsubscribe: <https://visitor.constantcontact.com/do?p=un&m=001st0JLJ3BRgXpr0CayrEO5A%3D%3D...>
List-Unsubscribe-Post: List-Unsubscribe=One-Click
Because legitimate ESP headers were used, mail clients recognized one-click unsubscribe functionality, further helping the message bypass initial email filters.
Redirect script
The jump host (mcguiganflooring.com/mcguiganflooring/) performed an HTTP 302 redirect directly to the second-stage domain:
HTTP/1.1 302 Found
Location: https://singdoctoyou.com/docsing/
Resulting redirect
The destination of the redirect chain was:
https://singdoctoyou.com/docsing/
- Target Domain:
singdoctoyou.com(possible typosquatting/anagram spoofing DocuSign). - Path:
/docsing/(doc-sing). - Domain Registration Date: July 21, 2026 (Registered just 4 days before the email was sent).
- Hosted On: Cloudflare (
188.114.96.3).
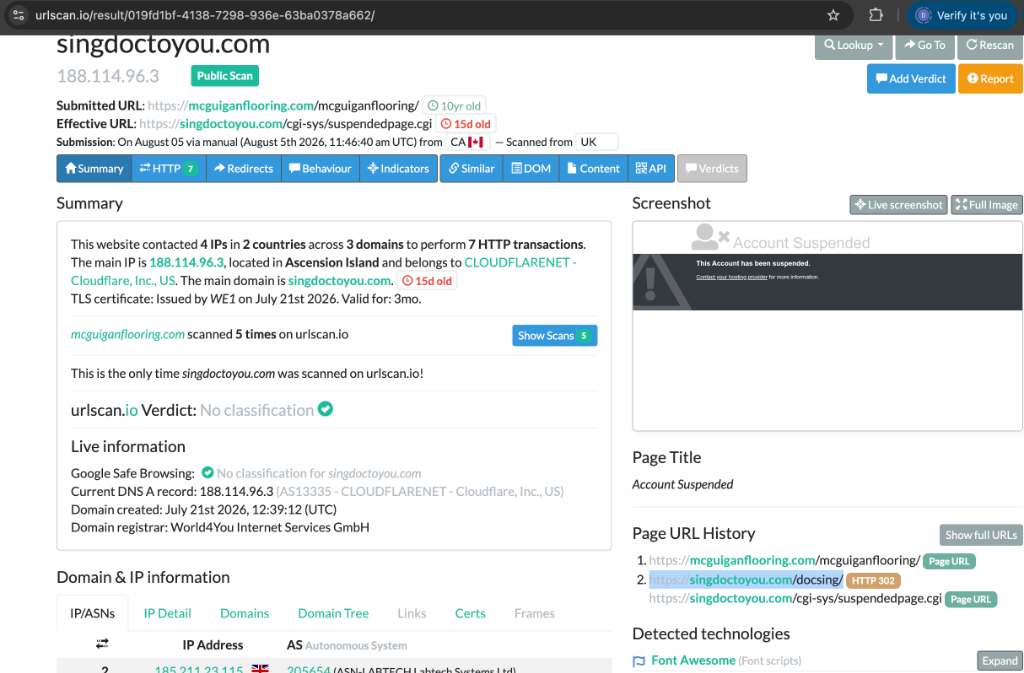
By the time of inspection, the host and domain were suspended (/cgi-sys/suspendedpage.cgi), and Cloudflare WAF was blocking incoming connections.
I was too late, bummer!
Redirect host cover page and certificate
Examining the jump host (mcguiganflooring.com):
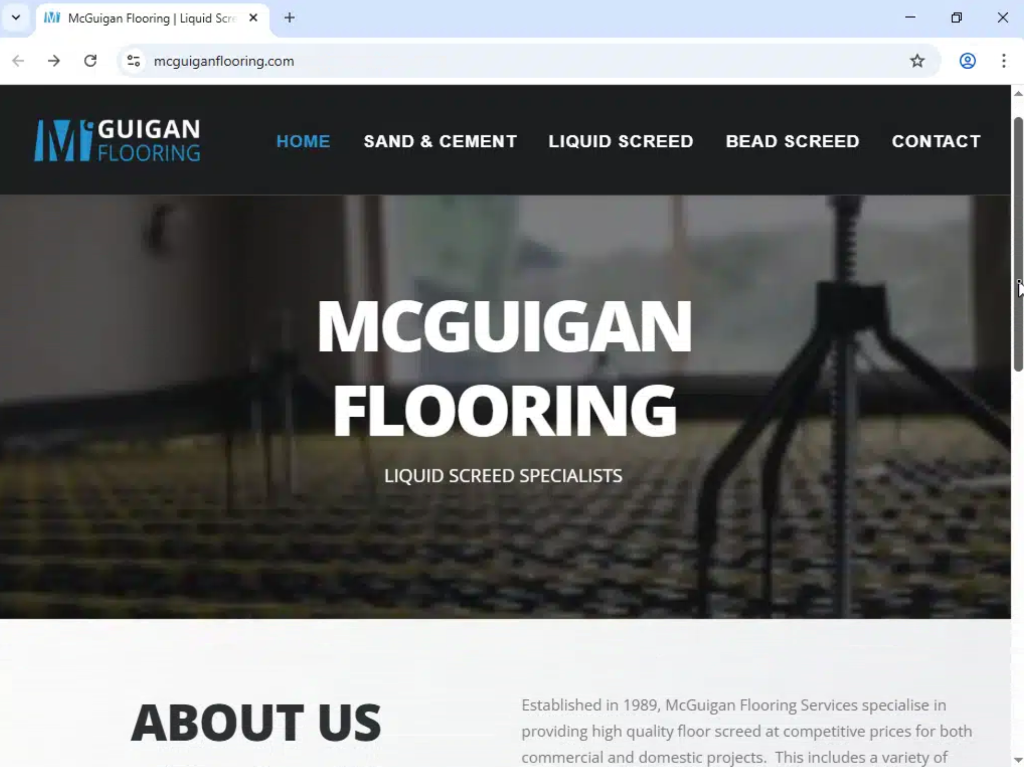
- The initial link points to a UK flooring business website (
mcguiganflooring.com).
- cPanel Compromise Timeline Correlation: Inspecting the SSL certificate for
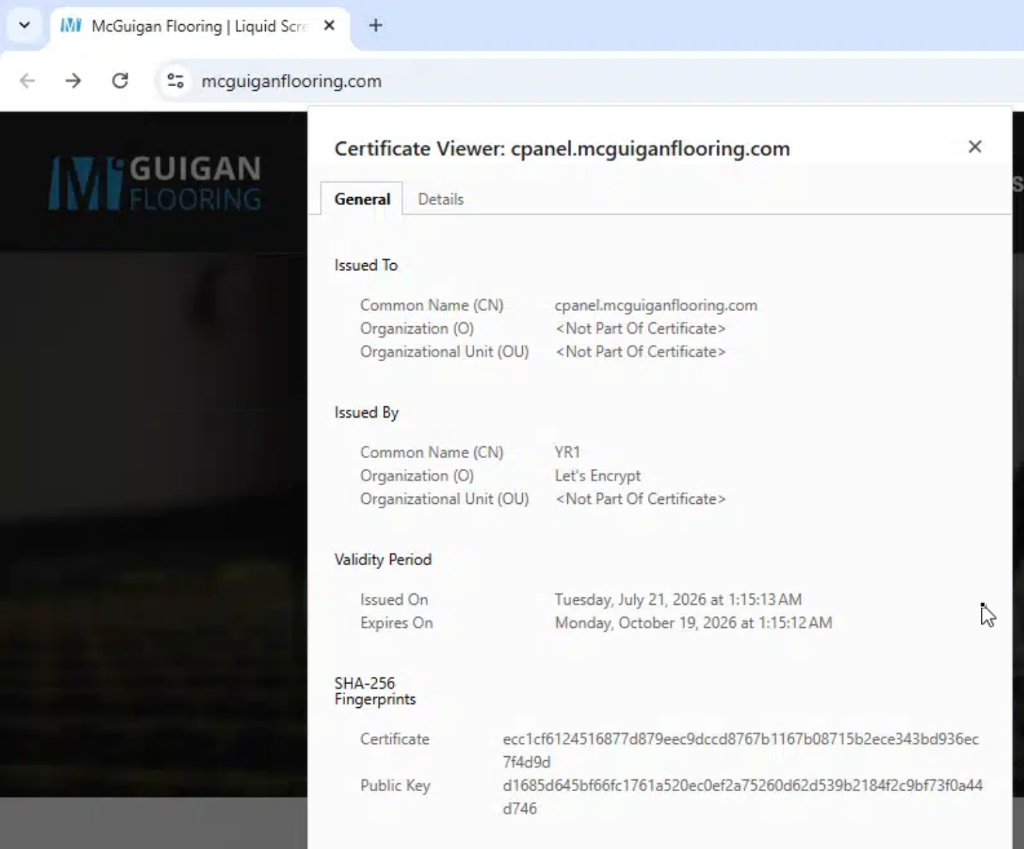
cpanel.mcguiganflooring.comreveals a Let's Encrypt TLS certificate issued on July 21, 2026 at 01:15 AM UTC — just 11 hours before the attacker registered the phishing targetsingdoctoyou.com(July 21 at 12:39 PM UTC)!
- Server Environment: Visiting missing subpaths (e.g.
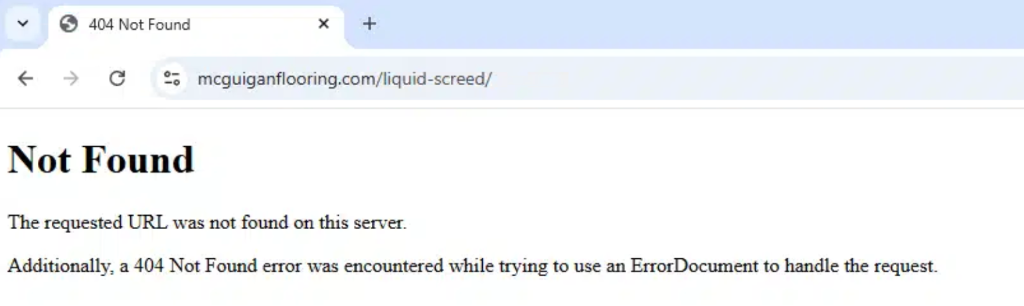
/liquid-screed/) returns a standard cPanel / Apache 404 error (The requested URL was not found on this server. Additionally, a 404 Not Found error...), indicating an underlying cPanel hosting account.
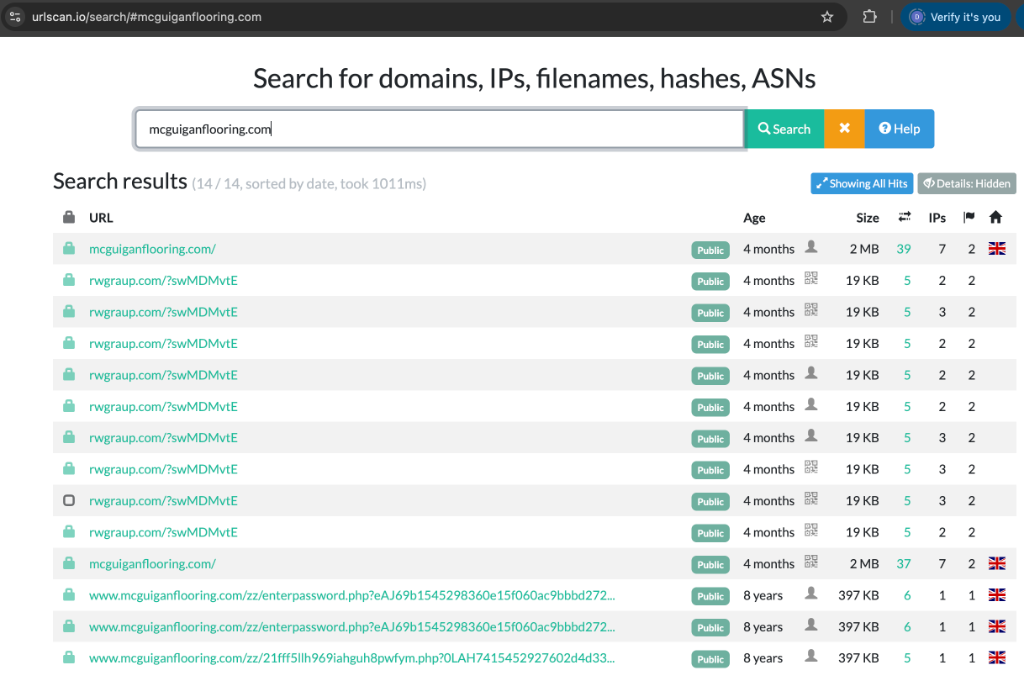
- Historical scans reveal this host was previously compromised to host probable credential theft scripts (e.g.,
/zz/enterpassword.php).
IOCs
| Indicator Type | Value | Description |
|---|---|---|
| Phishing Domain | singdoctoyou.com | Typosquatted DocuSign Phishing Host |
| Phishing Path | /docsing/ | Phishing credential harvester endpoint |
| Compromised Host | mcguiganflooring.com | Open Redirector / Compromised CMS |
Detection Logic
IF
Subject or Display Name contains non-ASCII homoglyphs resembling brand names (DocuSign)
AND Email originates from legitimate ESP infrastructure (Constant Contact / ccsend.com)
THEN
Homoglyph ESP abuse phishing attempt likely
Observations & Conclusions
- The attacker abused a legitimate Email Service Provider (Constant Contact) to obtain clean SPF, DKIM, and DMARC pass results.
- Homoglyph character substitution (Cyrillic and Greek Unicode characters) was used in both the Subject and Display Name to bypass string-matching security rules.
- The email body was stuffed with benign commercial promotional text to confuse content-based classification engines.
- The initial link leveraged a compromised UK flooring company (
mcguiganflooring.com), whose cPanel SSL certificate was re-issued just 11 hours before the phishing target domain was registered on July 21, 2026. - The final target (
singdoctoyou.com/docsing/) was suspended shortly after the campaign launched.